
ADenum
 secuproject/adenum
AD Enum is a pentesting tool that allows to find misconfiguration through the the protocol LDAP and exploit some of those weaknesses with kerberos.
misconfigurationpassword-crackingpenetration-testing
secuproject/adenumAD Enum is a pentesting tool that allows to find misconfiguration through the the protocol LDAP and exploit some of those weaknesses with kerberos.
 noxurge/cve-2025-65900
DifuseHQ Kalmia CMS version 0.2.0 contains an Incorrect Access Control vulnerability in the /kal-api/auth/users API endpoint. Due to insufficient…
 jenderal92/wp-def
Wordpress Default Password
 leekenghwa/cve-2023-37756-cwe-521-lead-to-malicious-plugin-upload-in-the-i-doit-pro-25-and-below
Proof-of-concept for CVE-2023-37756: weak password requirements in i-doit Pro admin-center enabling brute-force login and malicious plugin upload…
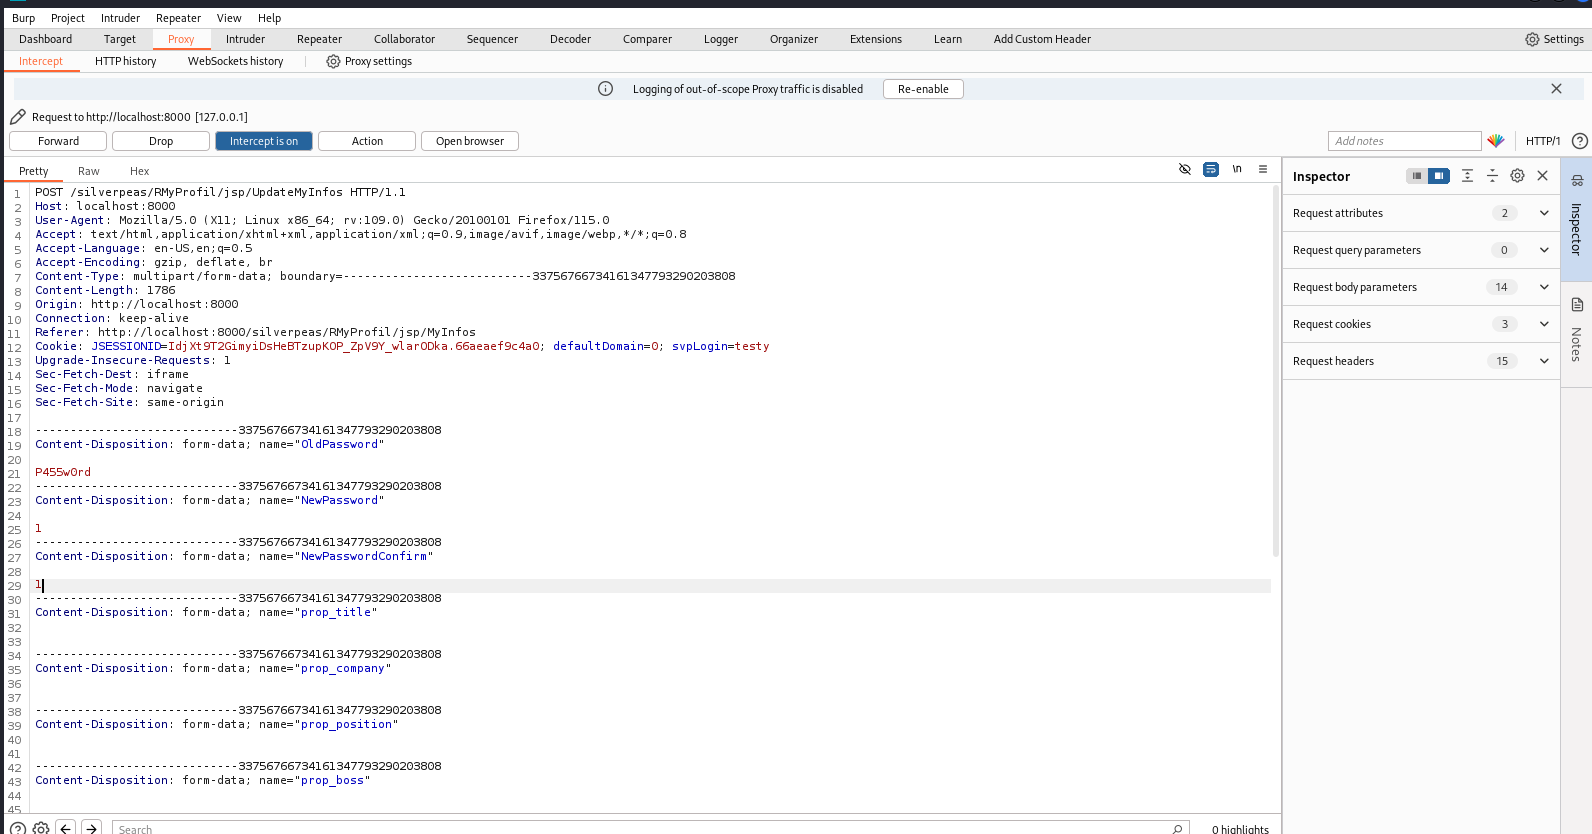 njmbb8/cve-2024-42850
An issue in Silverpeas v6.4.2 and lower allows for the bypassing of password complexity requirements.
 gh-ost00/cve-2024-28987-poc
Web Help Desk Hardcoded Credential Vulnerability (CVE-2024-28987)
 unix13/metasploitable2
PHP-CGI-REMOTE_CVE-2012-1823, UnrealIRCd, MySQL, PostgreSQL and SSH bruteforce, VSFTPD2.3.4, samba CVE-2007-2447, JAVA RMI Server, distcc daemon,…
 soy-oreocato/cve-2022-42176
Proof-of-concept for CVE-2022-42176: hard-coded credentials in PCSecure configuration file allow local privilege escalation to admin panel and…
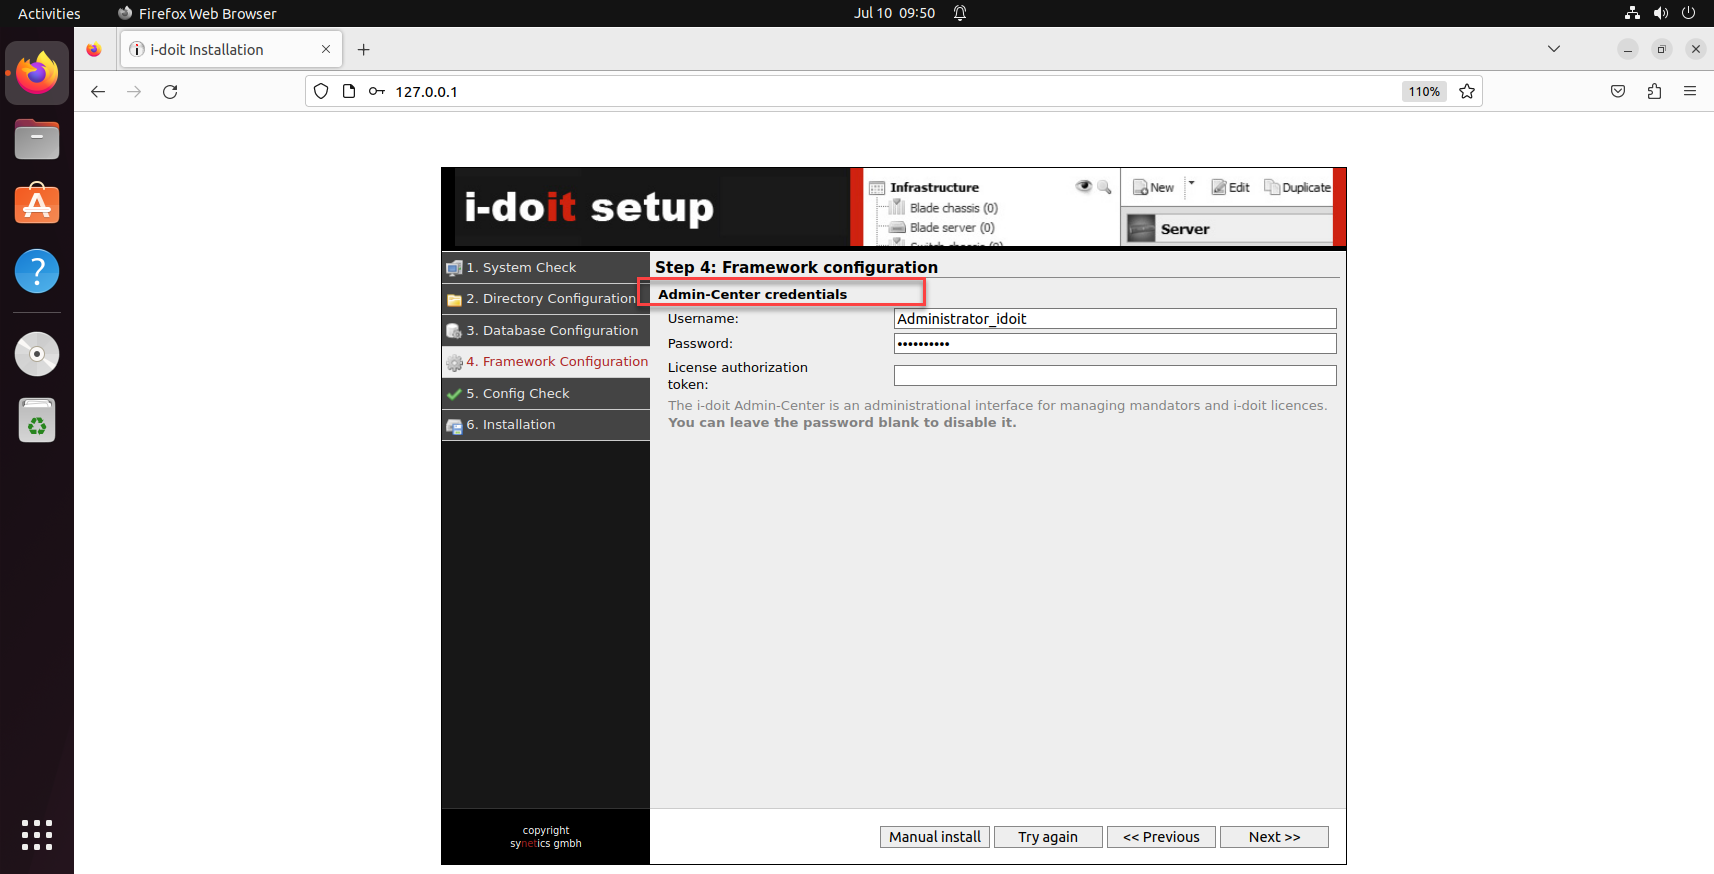 leekenghwa/cve-2023-37755---hardcoded-admin-credential-in-i-doit-pro-25-and-below
Proof-of-concept for CVE-2023-37755: hardcoded admin credentials (admin/admin) in i-doit Pro 25 and below, enabling unauthorized admin login via the…