
aura-inspector
 google/aura-inspector
Automated security testing tool for Salesforce Experience Cloud that discovers misconfigured Aura applications, accessible records, and unauthorized…
api-security-testingcloud-securityinformation-gathering+3
109
google/aura-inspectorAutomated security testing tool for Salesforce Experience Cloud that discovers misconfigured Aura applications, accessible records, and unauthorized…
 santandersecurityresearch/corsair_scan
Automated CORS misconfiguration scanner that tests Origin header injection, wildcard reflection, and credential leakage across web applications and…
 rodhnin/argus-wp-watcher
WordPress security scanner with AI-powered analysis, ethical compliance framework, and professional reporting.
 hac01/owasp-top-10-k8s-2025
Hands-on capture-the-flag lab for the OWASP Kubernetes Top 10 (2025). Exploit 11 real-world cluster weaknesses, capture flags, then apply fixes and…
 ovotech/domain-protect
Automated detection of vulnerable domain configurations and subdomain takeover risks across cloud environments, with continuous monitoring and…
 coreruleset/coreruleset
Generic attack detection rule set for web application firewalls, protecting against OWASP Top Ten and common vulnerabilities with minimal false…
 owasp/owasp-subtractive-hardening-top-10
The OWASP Subtractive Security Top 10 Project is an initiative to identify, document, and promote the highest-impact opportunities for reducing cyber…
 shoucheng3/esapi__esapi-java-legacy_cve-2022-24891_2-2-3-1
OWASP Enterprise Security API library providing security controls for Java web applications, including authentication, access control, input…
 foxvr-sudo/bug-bounty-arsenal-v.3
Full-stack platform for authorized web application security scanning with a detector-based engine, async Celery workers, and a React dashboard for…
 perufitlife/directus-security
Keyless active-probe security auditor for Directus CMS. Proves public-role data exposure, user enumeration, unauthenticated version/schema leaks,…
 sobri3195/pegasus-pentest-arsenal
A comprehensive web application security testing toolkit that combines 10 powerful penetration testing features into one tool.
 amnnrth/cve-2025-34291_cors_security_scanner
A lightweight Python-based security assessment tool for detecting dangerous Cross-Origin Resource Sharing (CORS) misconfigurations - CVE-2025-34291.
 havoc10-sw/detect_polyfill_cve-2024-38537-
Here's a Python script that checks if the polyfill.io domain is present in the Content Security Policy (CSP) header of a given web application.
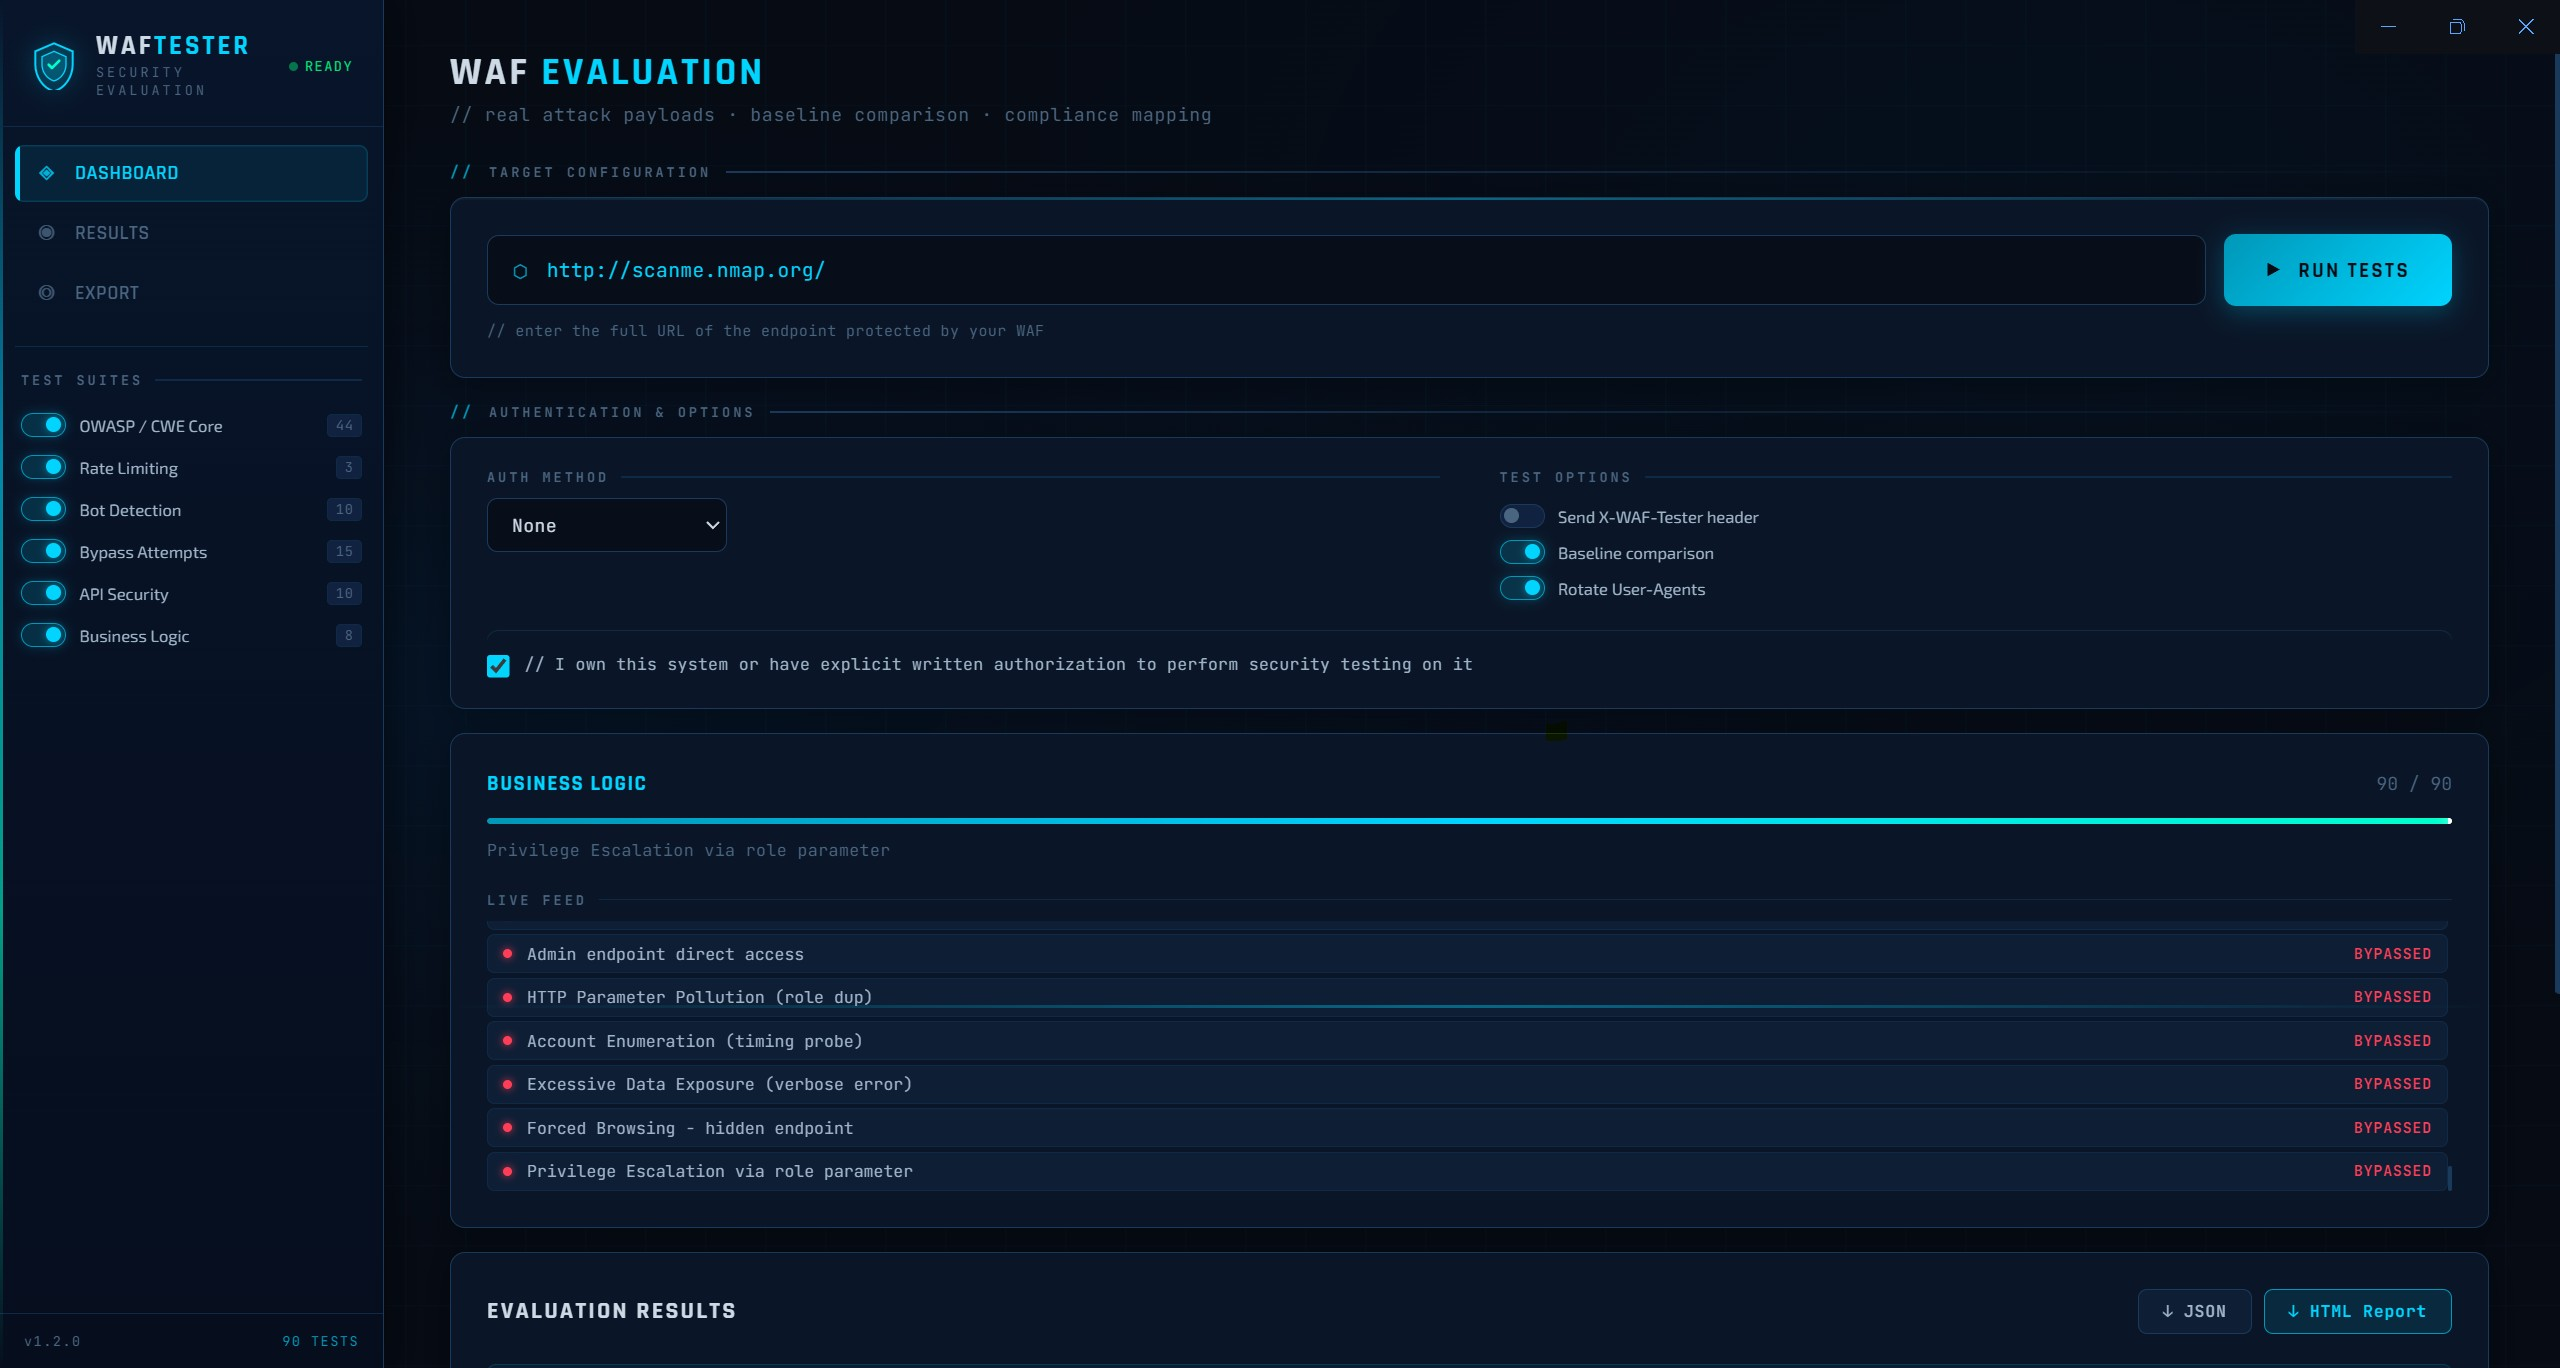 kpomin57/waf-tester
A program for testing WAF functionality
 ridhinva/langflow-cors-scanner
Scanner: CVE-2025-34291 Langflow Origin Validation Error / CORS Misconfiguration — Python checker (CISA KEV)
 csinexus/mcpshield
Drop-in fix for the unpatched MCP STDIO command-injection flaw (CVE-2026-30623 family)
 moniik/poc_salesforce_lightning
Academic purposes only. Attack against Salesforce lightning with guest privilege.
 mda2av/http11probe
An open testing platform that probes HTTP/1.1 servers against RFC 9110/9112 requirements, smuggling vectors, and malformed input handling. Add your…