
JShielder
 jsitech/jshielder
Hardening Script for Linux Servers/ Secure LAMP-LEMP Deployer/ CIS Benchmark
configuration-auditingdevsecopshardware-security+7
7817 years ago
jsitech/jshielderHardening Script for Linux Servers/ Secure LAMP-LEMP Deployer/ CIS Benchmark
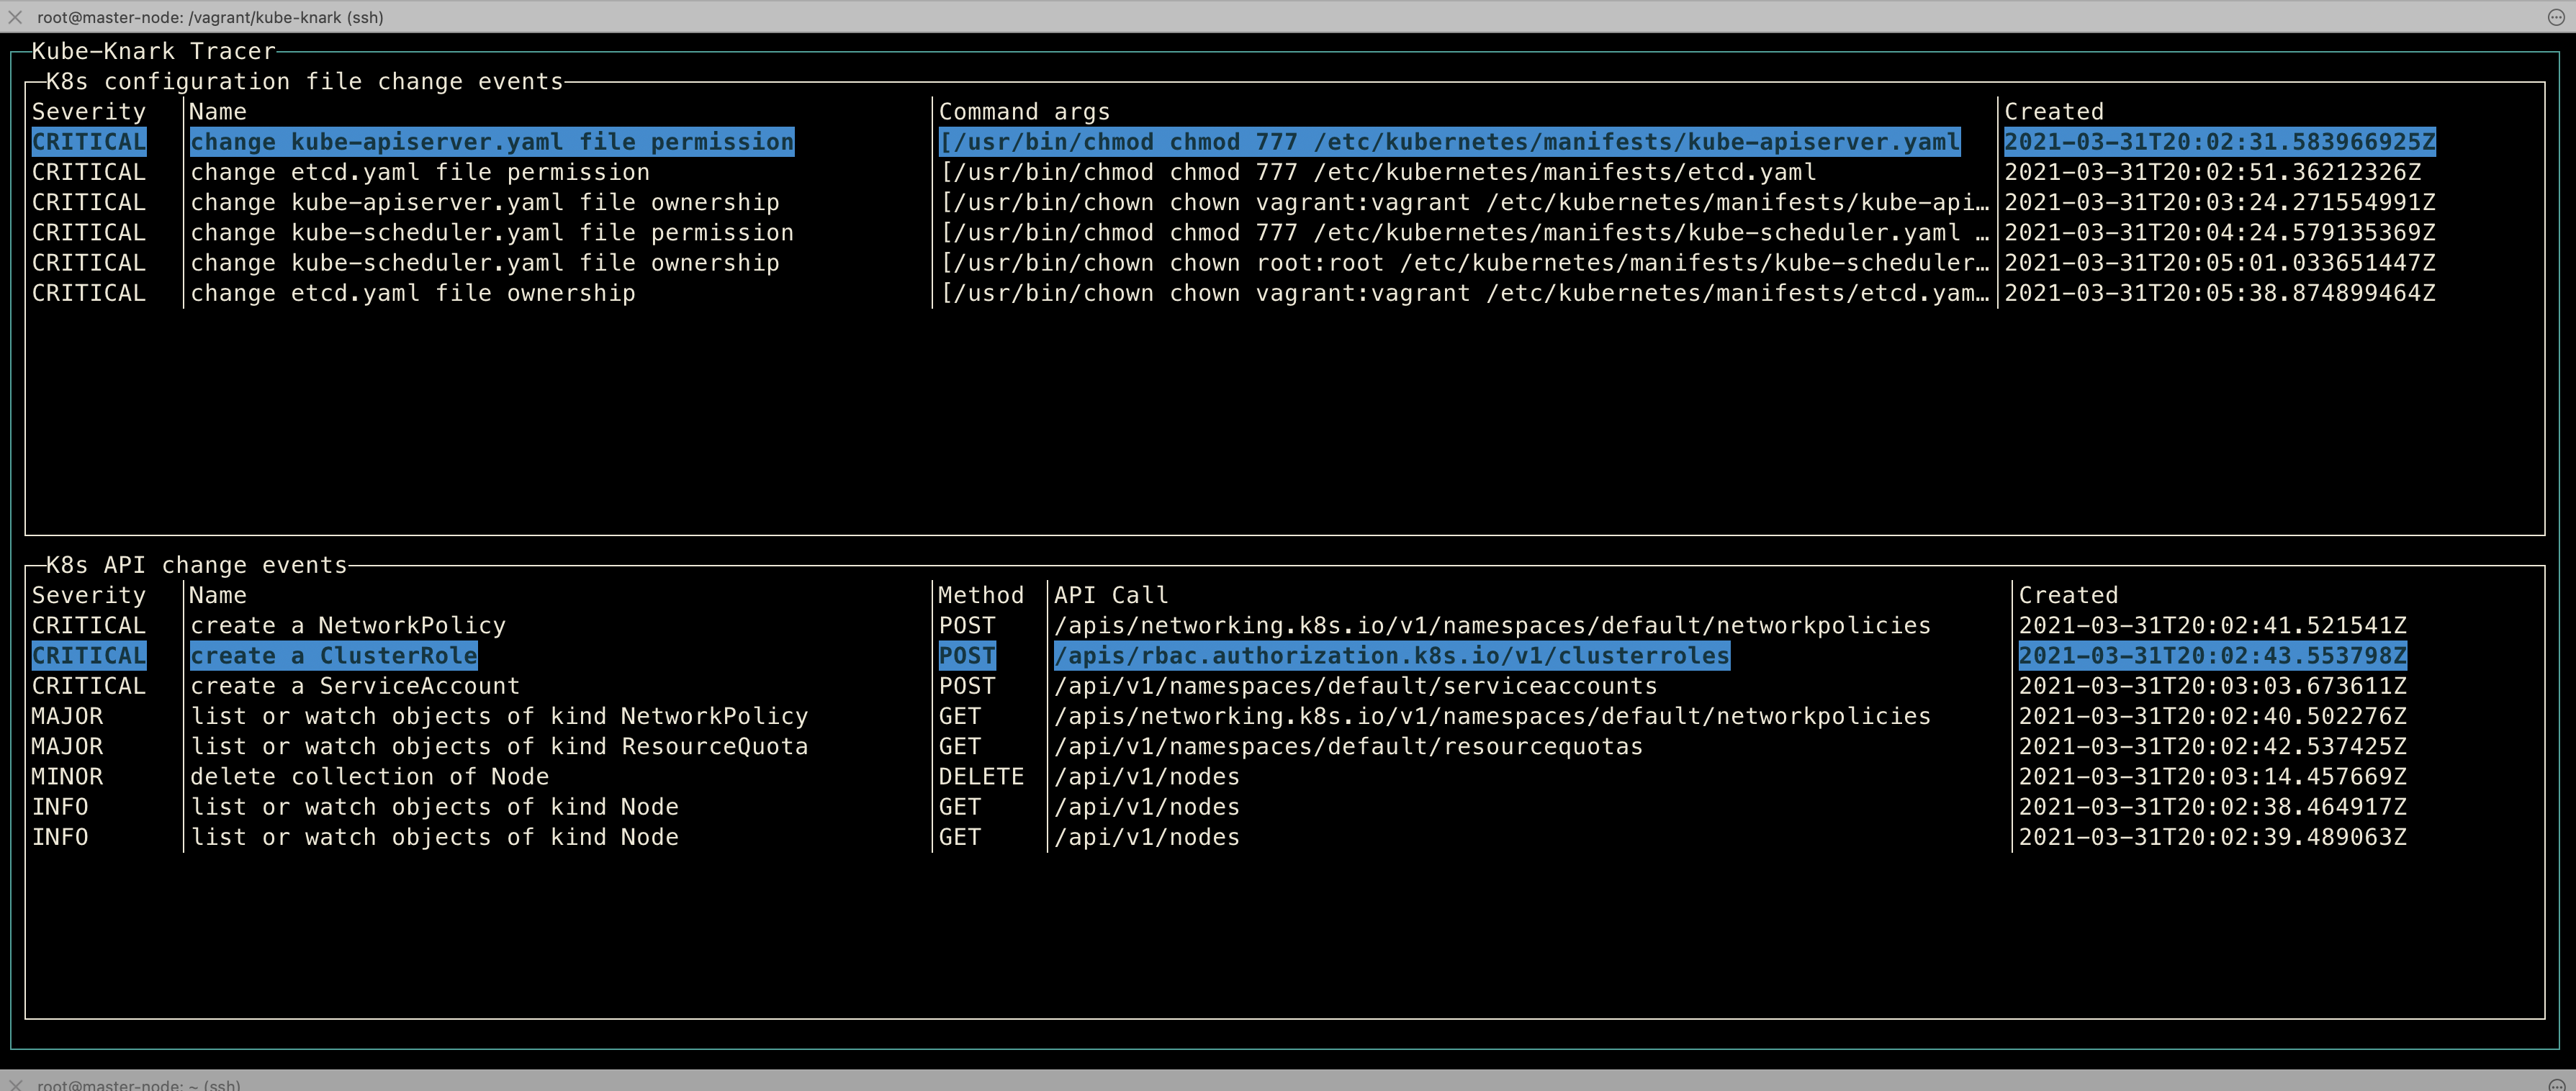 chen-keinan/kube-knark
Open Source runtime tool which help to detect malware code execution and run time mis-configuration change on a kubernetes cluster
 mondoohq/cnspec
An open source, cloud-native security to protect everything from build to runtime
 shiftleftsecurity/sast-scan
Scan is a free & Open Source DevSecOps tool for performing static analysis based security testing of your applications and its dependencies. CI and…
 bunkerity/bunkerweb
🛡️ Open-source and cloud-native Web Application Firewall (WAF)
 gensecaihq/cve-2024-3094-vulnerability-checker-fixer
Shell script and Ansible playbook to detect and remediate CVE-2024-3094 in xz-utils by checking package versions, upgrading or downgrading to a…
 cisofy/lynis
Agentless security auditing tool for Linux, macOS, and UNIX systems. Performs in-depth scans for vulnerabilities, configuration issues, and…
 dev-sec/ansible-collection-hardening
This Ansible collection provides battle tested hardening for Linux, SSH, nginx, MySQL
 jp1337/easywall
Web interface for the nftables firewall on Linux, written in Go. The apply undoes itself after 120 seconds unless you confirm it — you cannot lock…
 complianceascode/content
Generates SCAP, Ansible, Bash, and CEL security content for compliance evaluation and automated hardening across Linux hosts, containers, and…
 sleventyeleven/linuxprivchecker
Local Linux enumeration script that identifies privilege escalation vectors including misconfigurations, world-writable files, clear-text passwords,…
 alessandroz/beroot
Privilege Escalation Project - Windows / Linux / Mac
 sharma01672/traveller-htb
Traveller is an Easy Linux machine featuring a Joomla 4.2.7 travel booking website vulnerable to CVE-2023-23752, an unauthenticated REST API…
 galacticquest/cve-2024-3094-detect
Bash script to detect vulnerable XZ Utils versions (CVE-2024-3094) and downgrade to a safe release, supporting multiple Linux distributions and…
 visaicyber/cve-2025-27591-below-
Local Privilege Escalation vai `below` (CVE-2025-27591) - PoC Exploit
 rhinosecuritylabs/cloudgoat
CloudGoat is Rhino Security Labs' "Vulnerable by Design" AWS deployment tool
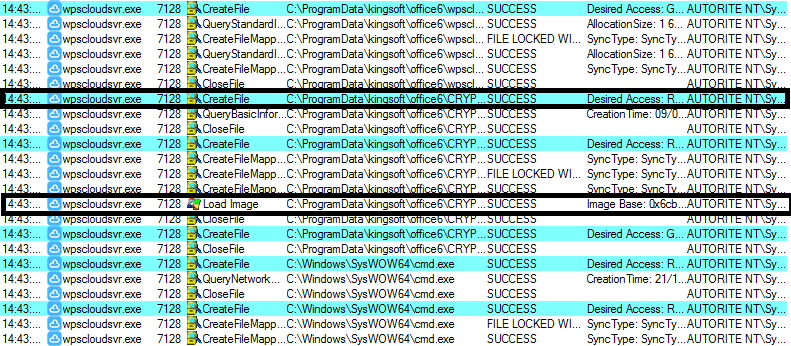 hadimed/kingsoft-wps-office-lpe
CVE-2022-25943
 machine1337/hackguard
FAST WEB APPLICATION VULNERABILITY SCANNER written in python3