CVE-2026-37069
Proof-of-concept for absolute path disclosure in Veno File Manager 4.4.9 via an unauthenticated GET request to a debug script, revealing the server's…

Proof-of-concept for absolute path disclosure in Veno File Manager 4.4.9 via an unauthenticated GET request to a debug script, revealing the server's…

Detection and remediation for CVE-2021-3438 with Powershell

Created after the disclosure of CVE-2022-22965 and CVE-2022-22963. Bash script that detects Spring Framework occurrences in your projects and…

Scans exported Azure domain dumps for plaintext passwords, connection strings, storage keys, and other secrets; generates redacted CSV/HTML reports…

Security Advisory: Insufficient Access Controls Allow for Unauthorized File Downloads (Let's Chat)

Mitigate CVE-2018-6389 WordPress load-scripts / load-styles attacks

Exploit for CVE-2021-44667 targeting Alibaba Nacos 2.0.3, enabling unauthenticated remote code execution via a crafted request to the Derby database…

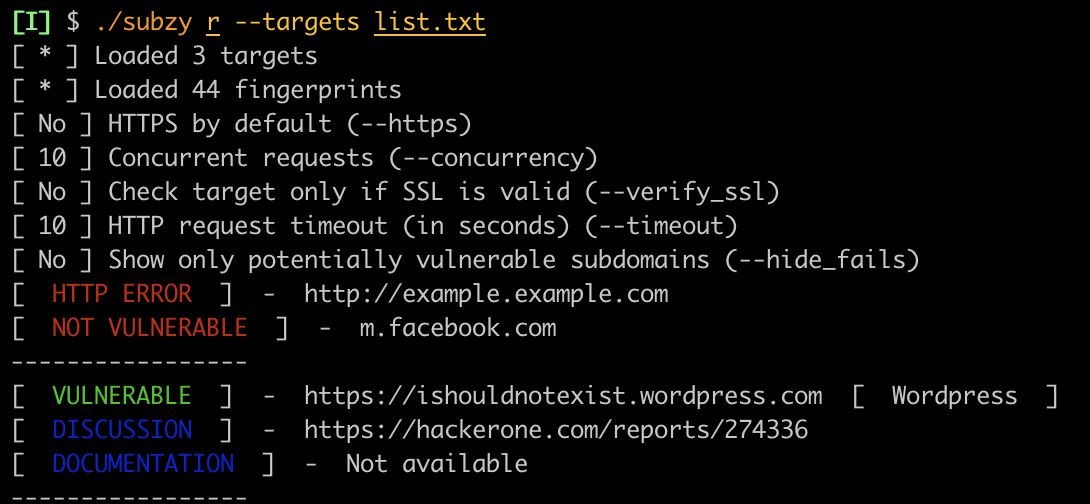
Subdomain takeover vulnerability checker

An open testing platform that probes HTTP/1.1 servers against RFC 9110/9112 requirements, smuggling vectors, and malformed input handling. Add your…

Use Exposed KongAPI to act like a proxy and get metadata urls or internal urls

Enemies Of Symfony - Debug mode Symfony looter

Arbitary Code Execution in Unsecured Apache Spark Cluster

Drupal CVE-2024-45440

TOTOLINK-A702R-V1.0.0-B20161227.1023 Directory Indexing Vulnerability