
CVE-2022-42176
 soy-oreocato/cve-2022-42176
Proof-of-concept for CVE-2022-42176: hard-coded credentials in PCSecure configuration file allow local privilege escalation to admin panel and…
authenticationexploitationmisconfiguration+3
1
soy-oreocato/cve-2022-42176Proof-of-concept for CVE-2022-42176: hard-coded credentials in PCSecure configuration file allow local privilege escalation to admin panel and…
 hadimed/dsl-2750u-full-chain
CVE-2021-3707 , CVE-2021-3708
 s1lkys/cve-2020-11107
Detailed writeup and step-by-step proof-of-concept for CVE-2020-11107, a Windows XAMPP privilege escalation vulnerability allowing arbitrary command…
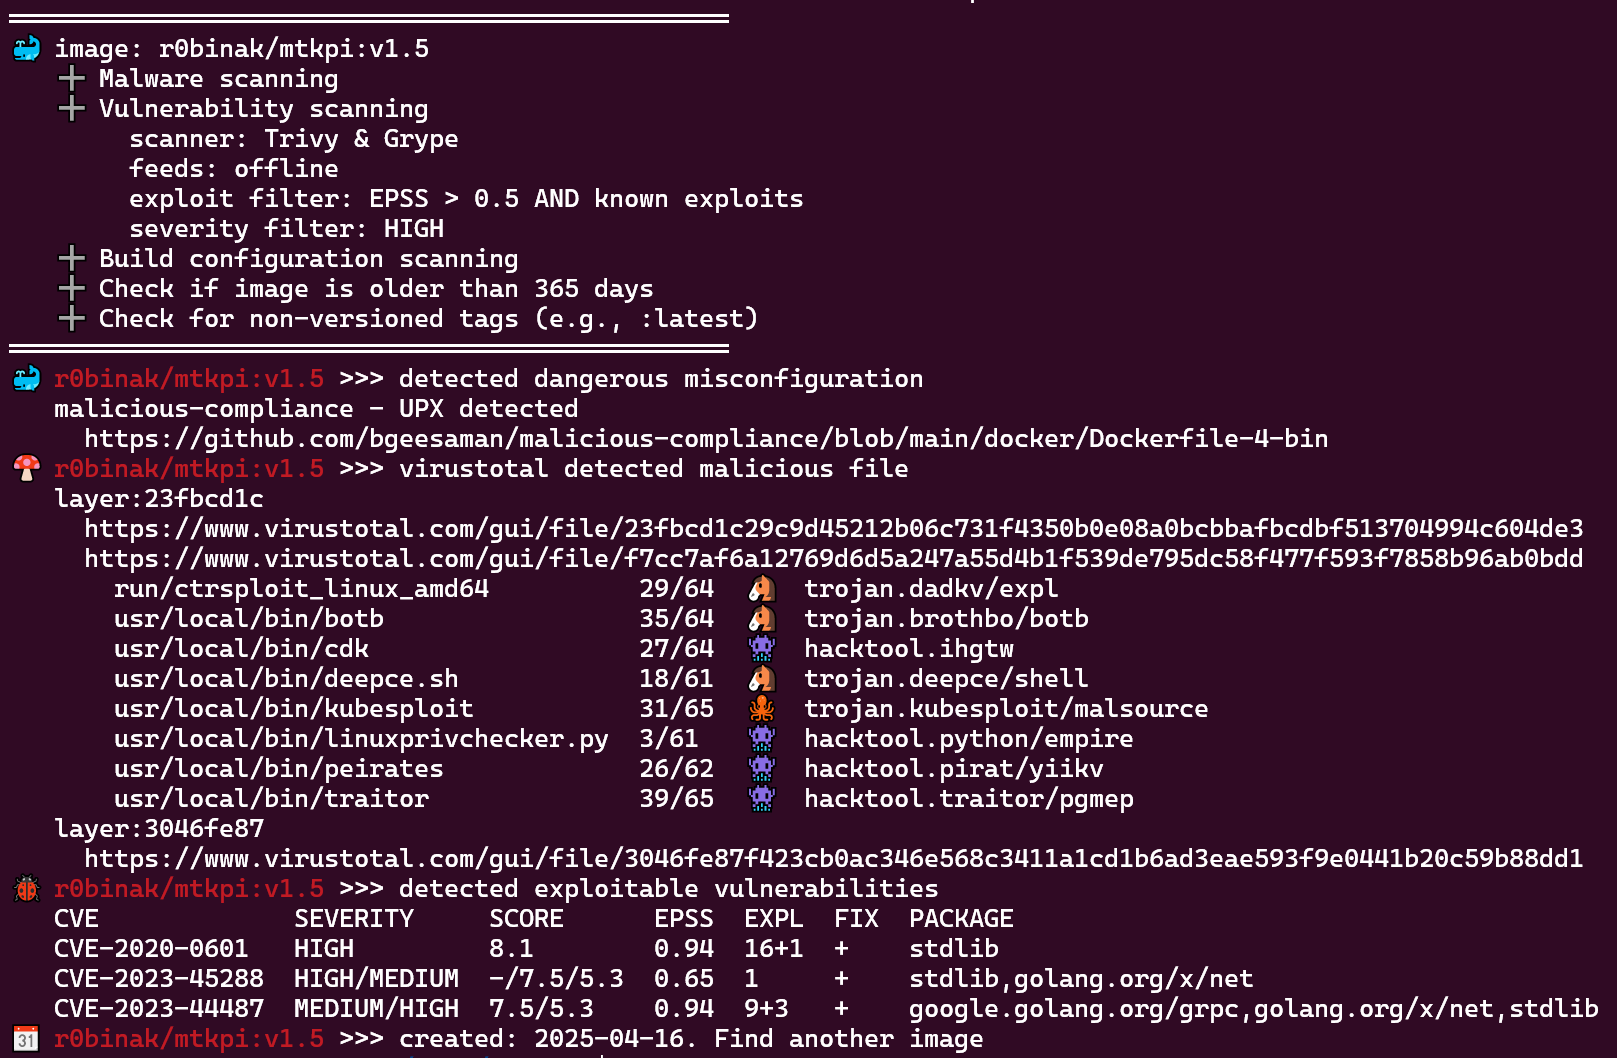 ecomtech-oss/pisc
Public OCI-Image (docker image) Security Checker
 unicorn-hyh/cve-2026-31156
There is a path injection vulnerability in OpenPLC-v3, which arises from the program not performing any validity checks on the file path parameters…
 th3xace/sudo_killer
A tool designed to exploit a privilege escalation vulnerability in the sudo program on Unix-like systems. It takes advantage of a specific…
 summitroute/aws_exposable_resources
Curated catalog of AWS resource types that can be publicly exposed, with CLI commands for creating and auditing public access configurations across…
 dumbmachine/cloud-doctor
One command grades your whole cloud account — misconfigurations, missing observability, and security posture.
 waleedadam360-web/syncshield
SyncShield - Browser Extension to Detect Unsafe Rsync Commands (CVE-2018-5764)
 hunt-benito/bring-your-own-key-cve-2026-73678-unauthenticated-rce-in-mindsdb-cowork
PoC exploit for CVE-2026-73678: unauthenticated RCE in MindsDB Cowork via attacker-supplied LLM key and unsandboxed scratchpad exec to run OS…
 mtaha-sec/bash-apocalypse
Recreating Shellshock (CVE-2014-6271) - the bash vulnerability that endangered millions of servers. Automated exploitation toolkit + Burp Suite…
 j4ck3lsyn-gen2/cve-2026-13768
Azure IoT Hub where exposure of an owner-level Shared Access Key enables unauthenticated remote code execution (RCE) against connected IoT devices.…
 win3zz/cve-2023-43261
CVE-2023-43261 - Credential Leakage Through Unprotected System Logs and Weak Password Encryption
 csinexus/mcpshield
Drop-in fix for the unpatched MCP STDIO command-injection flaw (CVE-2026-30623 family)
 cappricio-securities/behat-config-leaks
BeHat Configuration file leaking
 cappricio-securities/appspec-yaml-leaks
Appspec YML and YAML leaks
 cappricio-securities/phpinfo-files-leaks
This tool is used to find php info page
 cappricio-securities/cgi-printenv
CGI Print ENV leaking