

Pegasus-Pentest-Arsenal
 sobri3195/pegasus-pentest-arsenal
A comprehensive web application security testing toolkit that combines 10 powerful penetration testing features into one tool.
api-security-testingctfeducation+9
61
sobri3195/pegasus-pentest-arsenalA comprehensive web application security testing toolkit that combines 10 powerful penetration testing features into one tool.
 machine1337/hackguard
FAST WEB APPLICATION VULNERABILITY SCANNER written in python3
 corazawaf/coraza
Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
 foxvr-sudo/bug-bounty-arsenal-v.3
Full-stack platform for authorized web application security scanning with a detector-based engine, async Celery workers, and a React dashboard for…
 havoc10-sw/detect_polyfill_cve-2024-38537-
Here's a Python script that checks if the polyfill.io domain is present in the Content Security Policy (CSP) header of a given web application.
 yousseflahouifi/dbdtct
Python-based scanner that detects debug mode misconfigurations in web applications using multiple HTTP methods and fingerprinting techniques to…
 lb0x/cve-2020-24572
Proof-of-concept exploit for CVE-2020-24572 targeting authenticated remote command execution via a misconfigured web console in RaspAP 2.5.
 balajih4kr/cve-2025-29927
CVE-2025-29927 is a critical vulnerability in Next.js, a popular React-based web framework. The flaw exists in how the middleware feature handles…
 immunit/cve-2018-11759
Proof-of-concept exploit for CVE-2018-11759 demonstrating Apache mod_jk access bypass via specially crafted requests to bypass reverse proxy…
 trackflaw/cve-2023-25202
CVE-2023-25202: Insecure file upload mechanism
 12nio/cve-2025-68428_poc
CVE-2025-68428 Proof of Concept
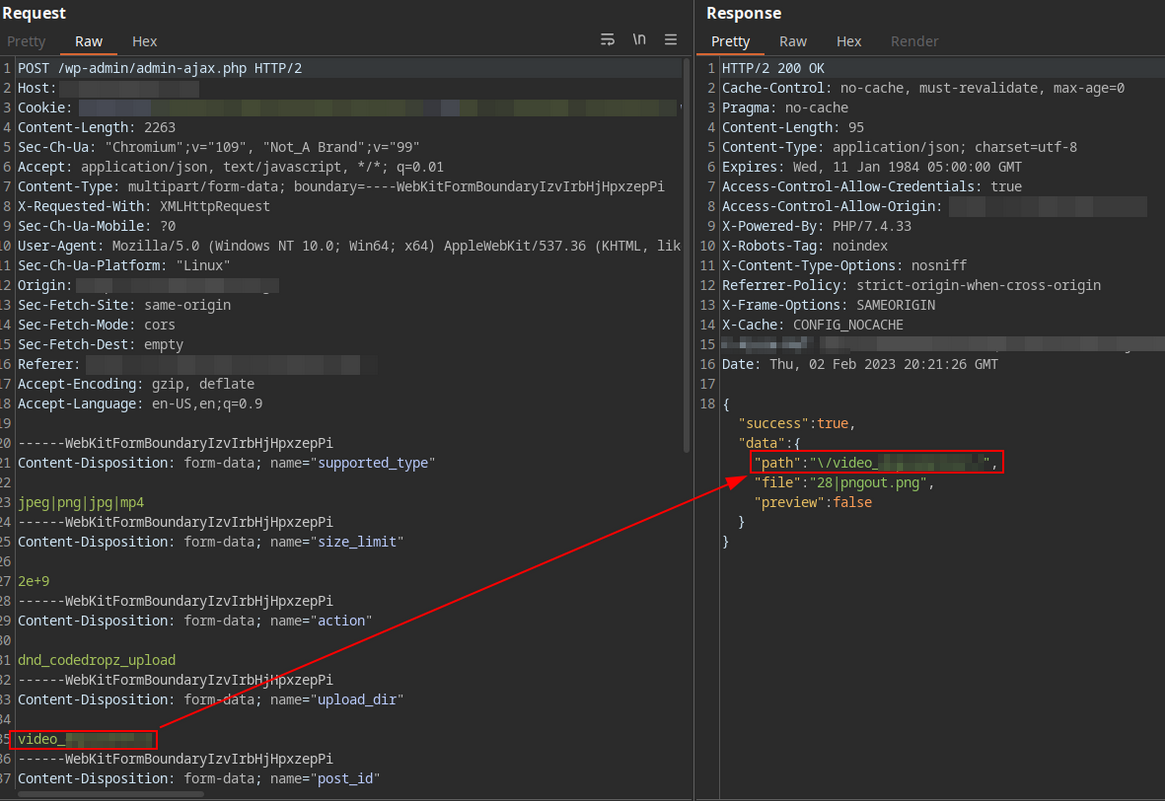 nickguitar/drag-and-drop-multiple-file-uploader-pro-path-traversal
Drag and Drop Multiple File Uploader PRO - Contact Form 7 v5.0.6.1 Path Traversal (CVE-2023-1112)
 ademking/cve-2025-29927
Next.js Middleware Authorization Bypass
 gregk4sec/cve-2025-31651-o
Proof-of-concept exploit for CVE-2025-31651, demonstrating bypass of security-enforcing rewrite rules via specially crafted requests in affected…
 randomrobbiebf/cve-2024-13800
Popup Plugin For WordPress - ConvertPlus <= 3.5.30 - Missing Authorization to Authenticated (Subscriber+) Limited Options Update
 vulnmachines/confluence-cve-2023-22515
Confluence Broken Access Control
 polosss/by-poloss..-..cve-2026-12432-poc
WP Full Stripe Free <= 8.4.3 - Missing Authorization
 whitej3rry/cve-2022-40490
Tiny File Manager v2.4.7 and below are vulnerable to Cross Site Scripting