EntraFalcon
A lightweight PowerShell tool for assessing the security posture of Microsoft Entra ID environments. It helps identify privileged objects, risky…

A lightweight PowerShell tool for assessing the security posture of Microsoft Entra ID environments. It helps identify privileged objects, risky…

Cloud-native Kubernetes cluster inspection tool that detects application misconfigurations, unhealthy components, and node problems using custom OPA,…

Library and CLI tool for analysing CloudFormation templates and check them for security compliance.

Fast service fingerprinting CLI for 170+ protocols (TCP/UDP/SCTP) - built by Praetorian

Subdomain brute-forcing tool that enumerates existing subdomains and detects misconfigured cloud-hosted subdomains vulnerable to takeover across AWS,…

Detect and remediate misconfigurations and security risks across all your GitHub and GitLab assets

Find vulnerabilities in AD Group Policy, but do it better than Grouper2 did.

An open-source Secure Email Gateway (SEG) evaluation toolkit designed for red-teamers.

Powerful open-source CLI to audit security, costs, and best practices in AWS. 🩺 ☁️

HackBox is a powerful and comprehensive tool that combines a variety of techniques for web application and network security assessments, including…

Content hijacking proof-of-concept using Flash, PDF and Silverlight

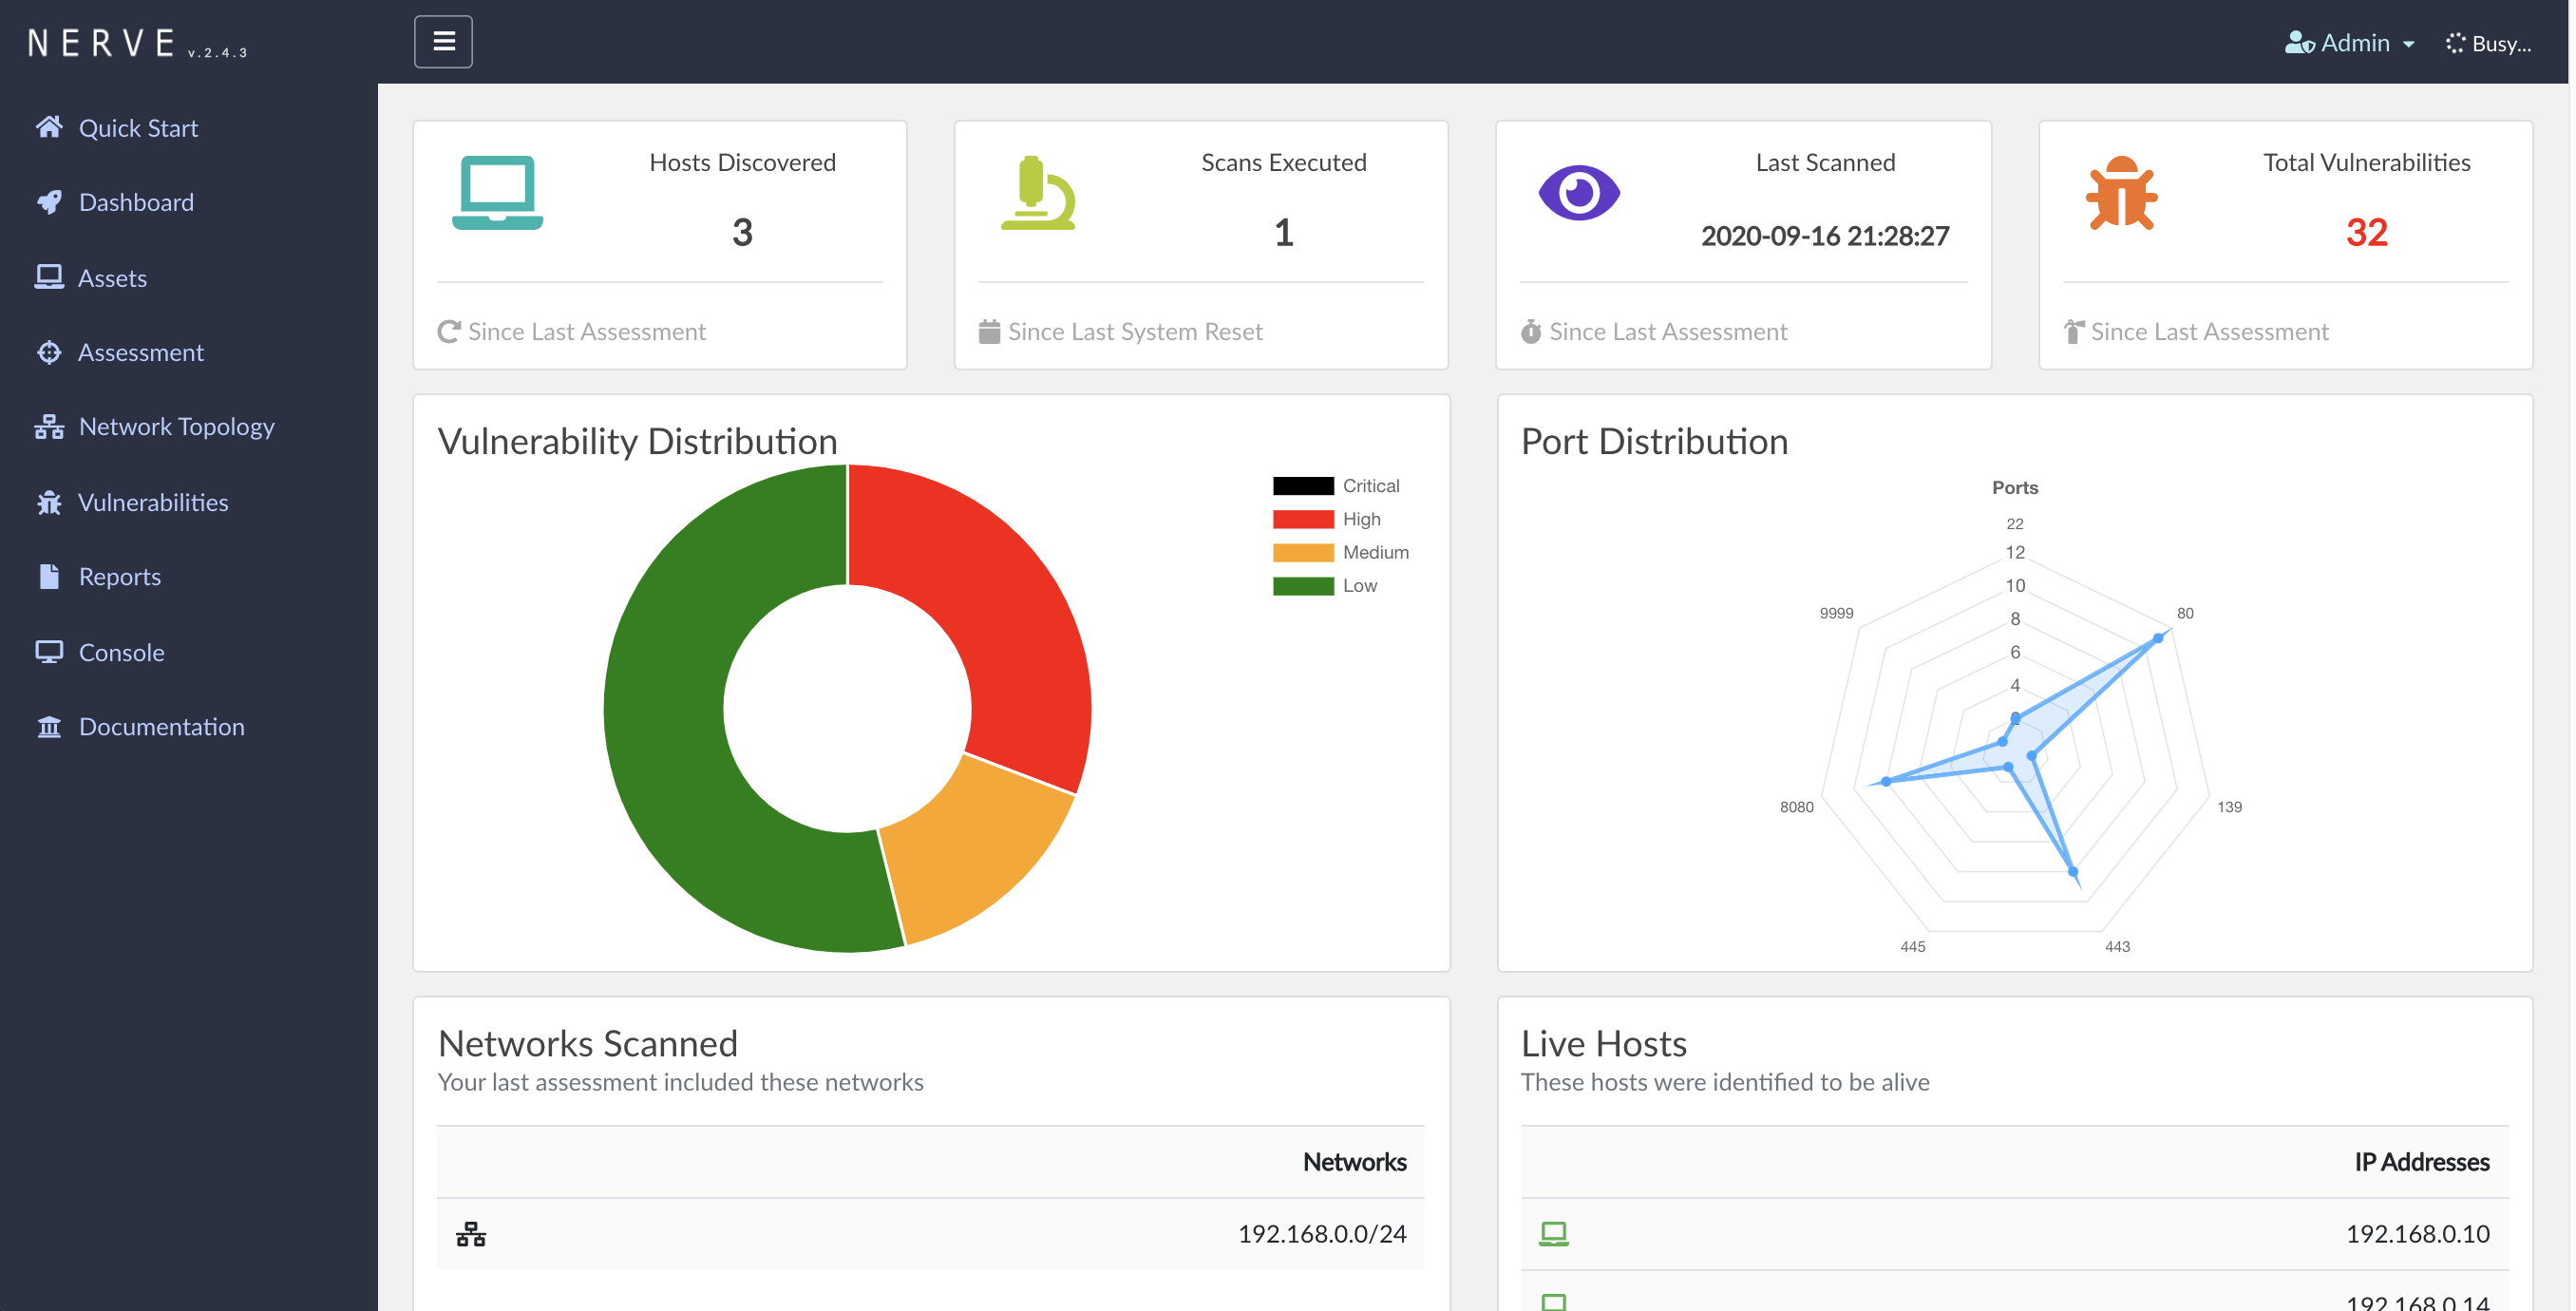
NERVE Continuous Vulnerability Scanner

SCCMSecrets.py aims at exploiting SCCM policies distribution for credentials harvesting, initial access and lateral movement.

Octoscan is a static vulnerability scanner for GitHub action workflows.

Automating the MITM attack on WSUS

Read-only AI agent that queries your cloud, code, and runtime infrastructure to surface misconfigurations, leaked secrets, and privilege escalation…

A fast universal code security scanner, written in Rust. Batteries included: supports 14 languages, TUI for triage, secrets, post-quantum audits,…

Enemies Of Symfony - Debug mode Symfony looter