
CVE-2026-55726
 michaeladamgroberman/cve-2026-55726
CVE-2026-55726: Publicly Listable Azure Blob Storage Container (device logs) - Gardyn (ICSA-26-183-03)
cloud-securityinformation-gatheringiot-security+3
michaeladamgroberman/cve-2026-55726CVE-2026-55726: Publicly Listable Azure Blob Storage Container (device logs) - Gardyn (ICSA-26-183-03)
 flyingllama87/p4wned
Perforce security research and tools - CVE-2026-6043
 sahiloj/cve-2023-37599
Issabel-pbx version 4.0.0-6 contains a Broken Access Control vulnerability that manifests as unauthenticated Directory Listing on the web interface.
 mdanzaruddin/cve-2021-33558.
Exploit code for CVE-2021-33558 targeting Boa/0.94.13 misconfigurations that expose sensitive information via backup, preview, log, and config files.
 allenenosh/cve-2021-40352
Proof-of-concept for CVE-2021-40352 in OpenEMR 6.0.0, demonstrating unauthorized access to patient messages via parameter manipulation in…
 f4rber/cve-2020-36287
The dashboard gadgets preference resource of the Atlassian gadgets plugin used in Jira Server and Jira Data Center before version 8.13.5, and from…
 huseyn0vs/cve-2026-16540-simplyscheduleappointments
CVE-2026-16540 — Simply Schedule Appointments < 1.6.12.6 Unauthenticated Appointment Data Disclosure and Mass Deletion
 dckento/cve-2021-40375
Broken Access Control in OpenEyes 3.5.1
 johenlastgen-jlg/cve-2026-11961
CVE-2026-11961 — UserRegistration: WordPress User Registration <= 5.2.2 Privilege Escalation. Misconfigured Membership Roles → Unauthenticated Admin…
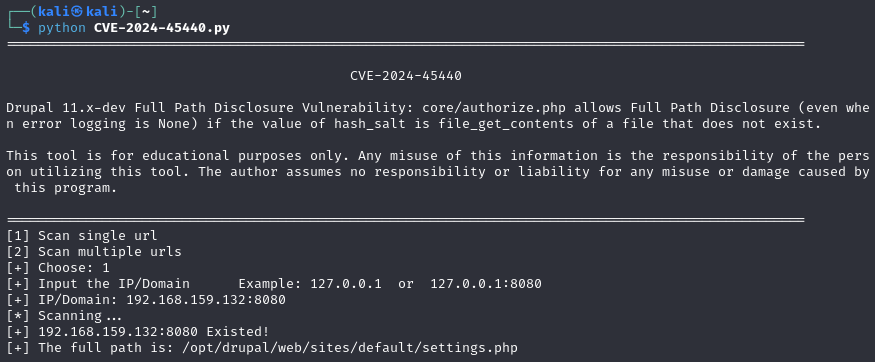 w0r1i0g1ht/cve-2024-45440
Drupal CVE-2024-45440
 jenderal92/git-dump
This script is a tool to recursively download the contents of the '.git' directory from a website. Using Python and libraries like 'requests' and…
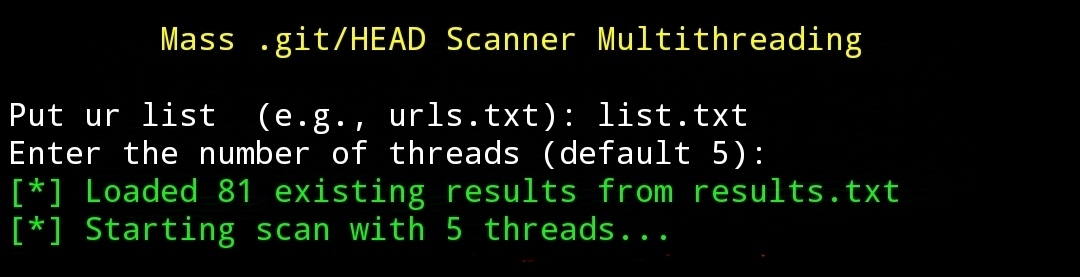 jenderal92/git-scan
This tool is designed to scan and identify whether a website has an exposed ".git" directory, which may contain sensitive information such as source…
 0xzerosec/cve-2025-69727
CVE-2025-69727
 rashidkhanpathan/cve-2022-41446
Privilege Escalation in Teachers Record Management System using CodeIgnitor
 lul/testrail-files.md5-iac-scanner
Python scanner for TestRail servers vulnerable to CVE-2021-40875
 michaeladamgroberman/cve-2026-32646
CVE-2026-32646: Missing Authentication on Admin Device Endpoint — Gardyn Home Kit (ICSA-26-055-03)
 jfs-jfs/cve-2026-37067
Incorrect access control in /vfm-admin/admin-panel/view/save-cvs.php in Veno File Manager Project 4.4.9 allows an unauthenticated attacker to extract…
 jfs-jfs/cve-2026-37069
Proof-of-concept for absolute path disclosure in Veno File Manager 4.4.9 via an unauthenticated GET request to a debug script, revealing the server's…