
Http11Probe
 mda2av/http11probe
An open testing platform that probes HTTP/1.1 servers against RFC 9110/9112 requirements, smuggling vectors, and malformed input handling. Add your…
api-security-testingfuzzingmisconfiguration+2
30
mda2av/http11probeAn open testing platform that probes HTTP/1.1 servers against RFC 9110/9112 requirements, smuggling vectors, and malformed input handling. Add your…
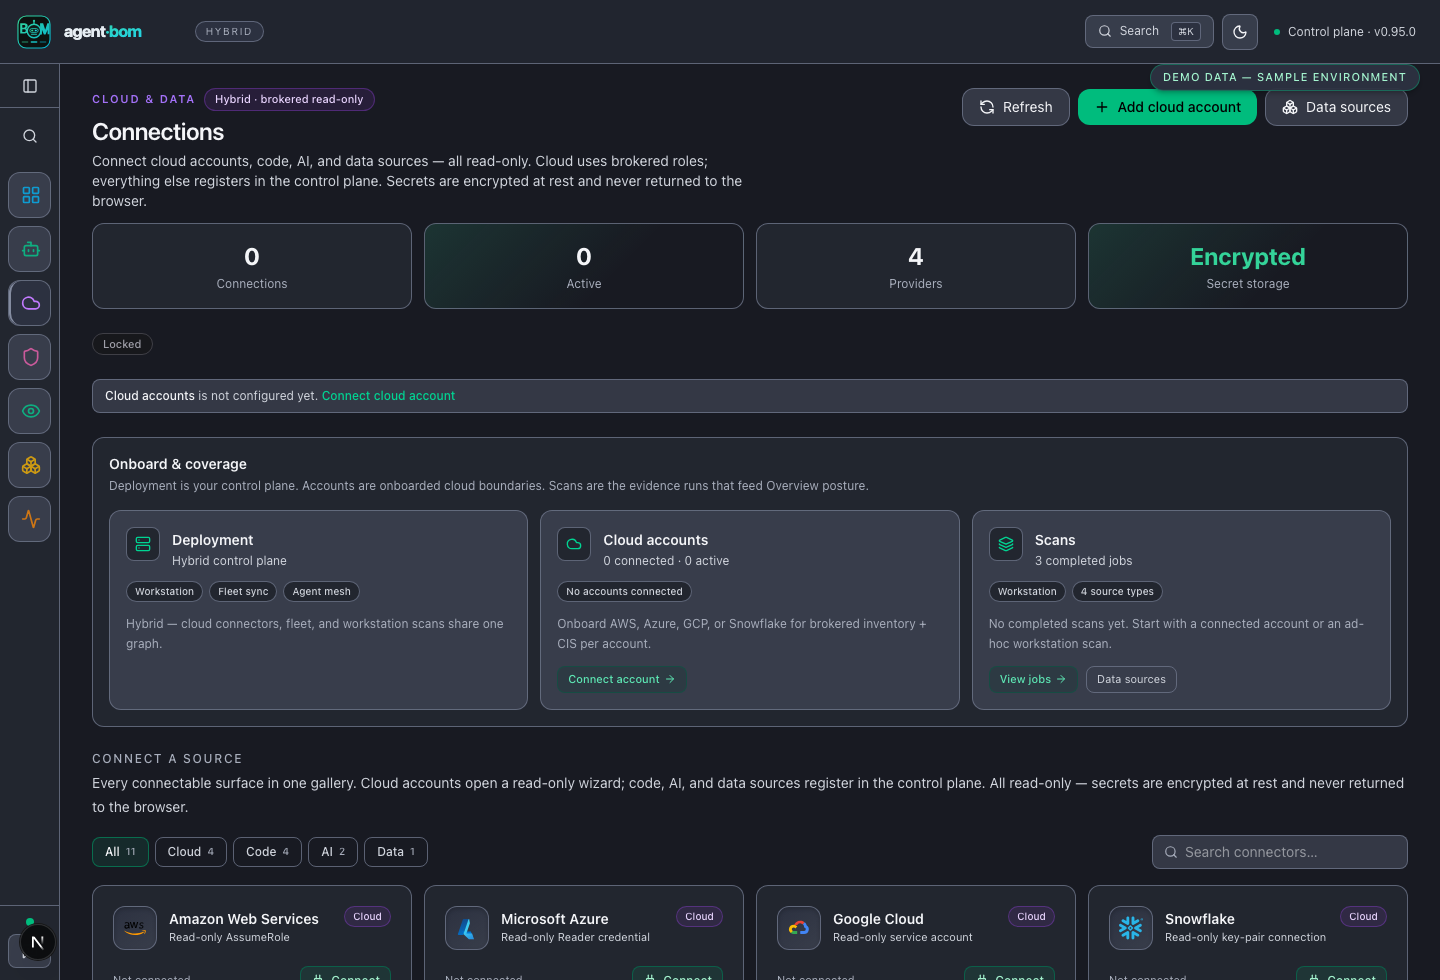 msaad00/agent-bom
Open security scanner and self-hosted control plane for AI, MCP, and cloud. One evidence model — run scans in your environment, centralize findings,…
 whitespots/fast-security-scanners
Security checks for your researches
 farenhytee/database-sentinel
Claude Skill that audits your projects for RLS misconfigurations, exposed keys, auth bypasses, and storage vulnerabilities. 27 anti-patterns sourced…
 synacktiv/kcmapper
KcMapper is a security auditing tool for Keycloak. It exports your Keycloak configuration (realms, clients, users, roles, etc.) into a Neo4j graph…
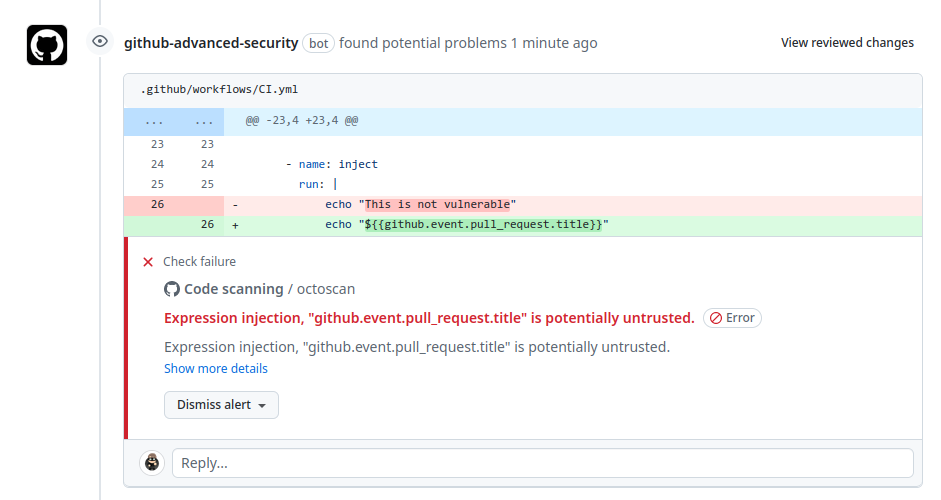 synacktiv/action-octoscan
📦 :octocat: A GitHub Action that performs a security scan of your GitHub Actions.
 heroku/heroku-cve-2013-0269
Inspect all of your Heroku apps for vulnerable versions of the JSON gem
 dumbmachine/cloud-doctor
One command grades your whole cloud account — misconfigurations, missing observability, and security posture.
 wadesweaponshed/check-point-trusted-access-review
Local web app for conducting a Check Point Trusted Access Review. This scanner is built specifically to look for configuration issues around…
 alash3al/wp-allowed-hosts
a plugin that protects your wp site from the CVE-2017-8295 vulnerability
 realityone/cve-2026-42945-scan
Scan your NGINX configuration to determine whether it is affected by CVE-2026-42945.
 sibersan/web-server-audit_cve-2026-42945
Trigger-aware web server CVE audit for nginx and Apache. Goes beyond version matching by checking whether the vulnerable code path is actually…
 mebibite/springhound
Created after the disclosure of CVE-2022-22965 and CVE-2022-22963. Bash script that detects Spring Framework occurrences in your projects and…
 piranhap/cve-2013-3900_remediation_powershell
Script to make changes on registry to fix CVE-2013-3900. It comes with an option to undo in case it breaks something on your environment.
 shopify/kubeaudit
kubeaudit helps you audit your Kubernetes clusters against common security controls
 maweil/bidi_char_detector
Checks your files for existence of Unicode BIDI characters which can be misused for supply chain attacks. See CVE-2021-42574
 open-policy-agent/opa
Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…
 vercel-labs/deepsec
Agent-powered vulnerability scanner for large-scale codebases. Uses LLMs to find hard-to-detect security issues via regex matchers and AI…