
Owasp-top-10-k8s-2025
 hac01/owasp-top-10-k8s-2025
Hands-on capture-the-flag lab for the OWASP Kubernetes Top 10 (2025). Exploit 11 real-world cluster weaknesses, capture flags, then apply fixes and…
cloud-securitycontainer-securityctf+8
49
hac01/owasp-top-10-k8s-2025Hands-on capture-the-flag lab for the OWASP Kubernetes Top 10 (2025). Exploit 11 real-world cluster weaknesses, capture flags, then apply fixes and…
 owasp/java-html-sanitizer
Takes third-party HTML and produces HTML that is safe to embed in your web application. Fast and easy to configure.
 owasp/openshield
Open source CSPM for Azure - scan for misconfigurations and quantum-unsafe cryptography, map findings to CIS/NIST/ISO27001/SOC2, and fix them with…
 dheeraj-jayaswal/cicd-goat-vapt-writeup
Full VAPT writeup of OWASP CICD-Goat — 9 CTFd flags captured, 4 critical + 5 high findings (incl. CVE-2024-23897) mapped to the OWASP Top 10 CI/CD…
 domain-protect/domain-protect
OWASP Domain Protect - prevent subdomain takeover
 voorivex/pentest-guide
Penetration tests guide based on OWASP including test cases, resources and examples.

 owasp/awscanner
Finds internet-exposed resources in an AWS account
 spiderlabs/owasp-modsecurity-crs
OWASP ModSecurity Core Rule Set (CRS) Project (Official Repository)
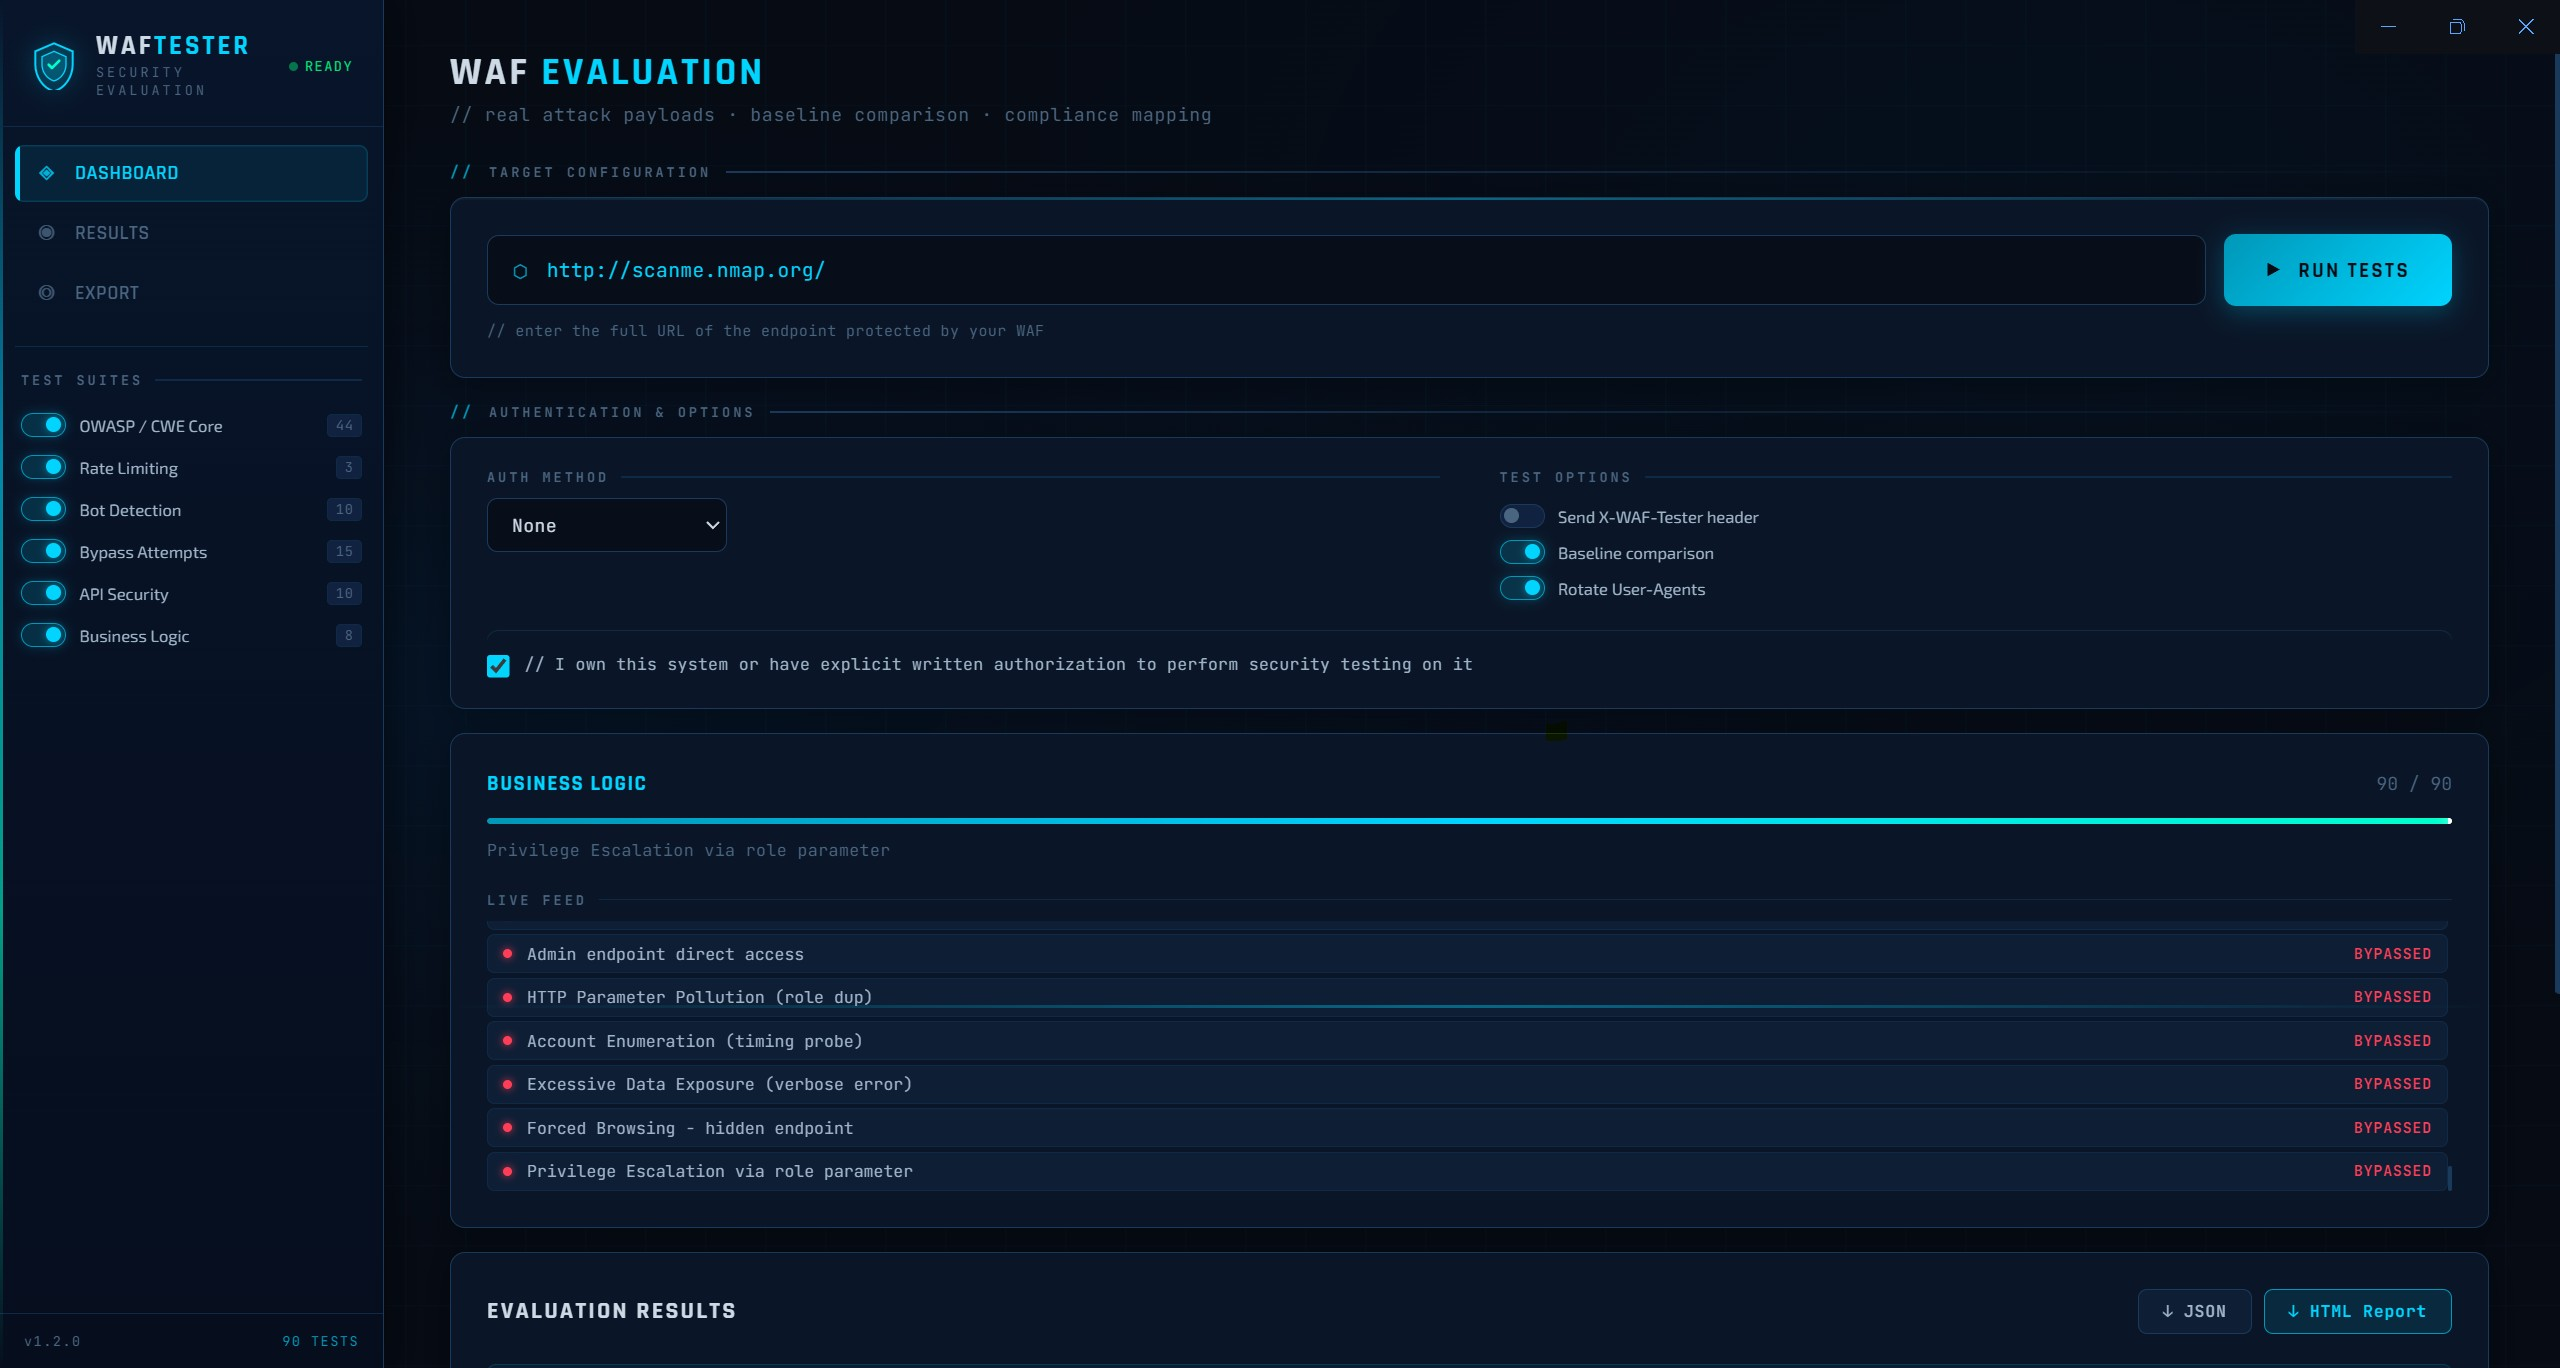 kpomin57/waf-tester
A program for testing WAF functionality
 ovotech/domain-protect
Automated detection of vulnerable domain configurations and subdomain takeover risks across cloud environments, with continuous monitoring and…
 coffinxp/google-api-key-scanner
Validates Google Maps API keys against 21 endpoints, revealing exposed services with PoC URLs, proxy support, and quiet mode for focused auditing.
 santandersecurityresearch/corsair_scan
Automated CORS misconfiguration scanner that tests Origin header injection, wildcard reflection, and credential leakage across web applications and…
 bishopfox/snowpick
find sensitive data leaking from ServiceNow instances.
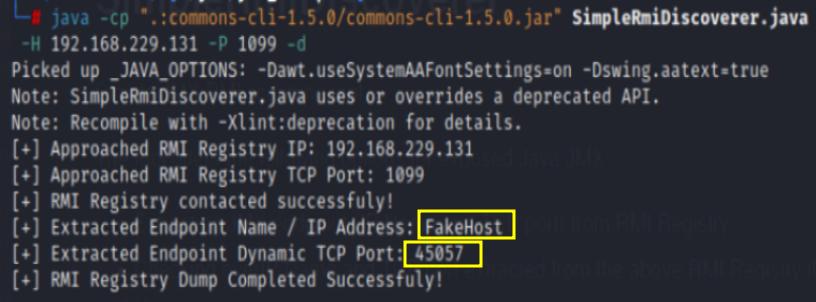 marcin-wolak/simplermidiscoverer
Simple JMX RMI scanning tool
 qianlijaingshan/milvus-auth-audit
Milvus 认证安全检测脚本:CVE-2025-64513 (sourceid后门) / CVE-2026-26190 (/expr弱token) / 内部端口53100
 ridhinva/langflow-cors-scanner
Scanner: CVE-2025-34291 Langflow Origin Validation Error / CORS Misconfiguration — Python checker (CISA KEV)
 perufitlife/directus-security
Keyless active-probe security auditor for Directus CMS. Proves public-role data exposure, user enumeration, unauthenticated version/schema leaks,…