

snuffleupagus
 jvoisin/snuffleupagus
Security module for php7 and php8 - Killing bugclasses and virtual-patching the rest!
code-analysisdefensive-toolsmisconfiguration+2
844
jvoisin/snuffleupagusSecurity module for php7 and php8 - Killing bugclasses and virtual-patching the rest!
 shiftleftsecurity/sast-scan
Scan is a free & Open Source DevSecOps tool for performing static analysis based security testing of your applications and its dependencies. CI and…
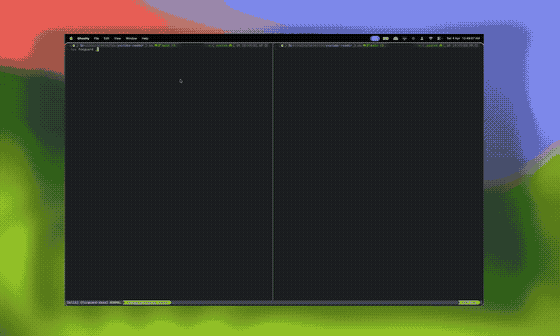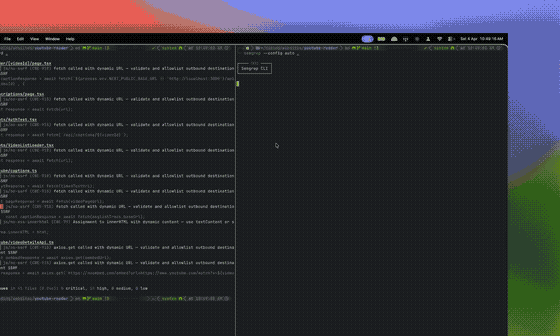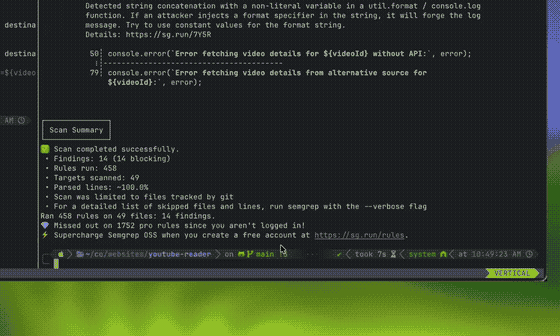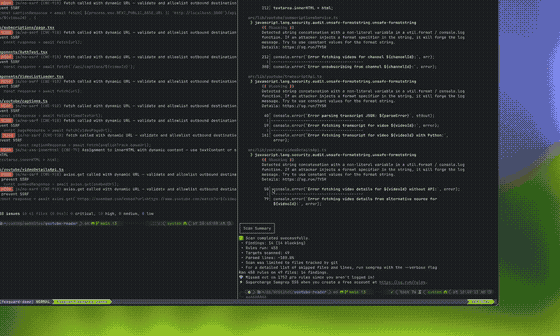 0sec-labs/foxguard
A fast universal code security scanner, written in Rust. Batteries included: supports 14 languages, TUI for triage, secrets, post-quantum audits,…
 praetorian-inc/trajan
A multi-platform CI/CD vulnerability detection and attack automation tool for identifying security weaknesses in pipeline configurations.
 preflightsh/preflight
Go-based CLI tool that scans codebases for launch readiness, detecting missing configuration, security hygiene issues, secret leaks, and integration…
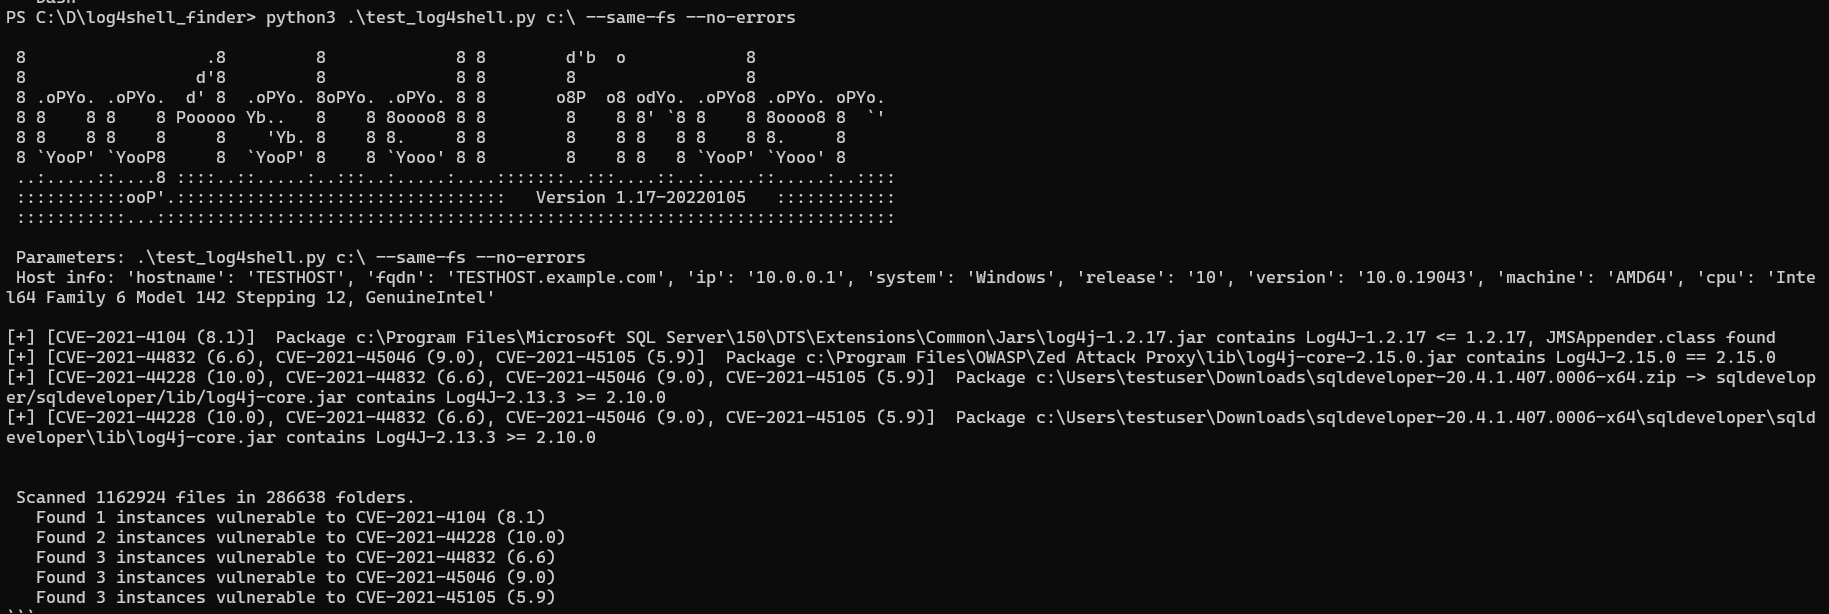 hynekpetrak/log4shell-finder
Fastest filesystem scanner for log4shell (CVE-2021-44228, CVE-2021-45046) and other vulnerable (CVE-2017-5645, CVE-2019-17571, CVE-2022-23305,…
 jvoisin/snuffleupagus
Security module for php7 and php8 - Killing bugclasses and virtual-patching the rest! https://snuffleupagus.rtfd.io
 arsbr/veritensor
The Anti-Virus for AI Artifacts & RAG Firewall. A static analysis tool scanning Models and Notebooks for RCE, Datasets and RAG docs for Data…
 mathiasreker/blmvuln
Major Security Vulnerability on PrestaShop Websites - CVE-2022-31101
 califio/ngxray
ngxray — nginx config security scanner
 nanitor/log4fix
Detect and fix log4j log4shell vulnerability (CVE-2021-44228)
 kulik-labs-development/ghost-cms-code-injection-audit-cve-2026-26980
Outdated Ghost CMS websites that have fallen become compromised from CVE-2026-26980 can suffer from spam code injection to pages. Use this to mass…
 razi-interactive/claude-project-scanner
Read-only safety scanner for Claude Code projects. Catches CVE-2025-59536, statusLine injection, prompt injection, and more.
 dillonkirsch/cve-2026-26720-twenty-rce
Proof-of-concept for authenticated remote code execution in Twenty CRM via unsandboxed serverless workflow functions, allowing arbitrary Node.js…
 nickops87/spring4shell-python-firewall-poc
Proof-of-Concept (POC) of a simple firewall in Python designed to mitigate the Spring4Shell (CVE-2022-22965) RCE attack by inspecting and blocking…
 yksivaihde/discourse-cve-2023-45806
Ruby script to fix quote attribution vulnerability (CVE-2023-45806) in Discourse forums by searching and patching malformed quote blocks with…
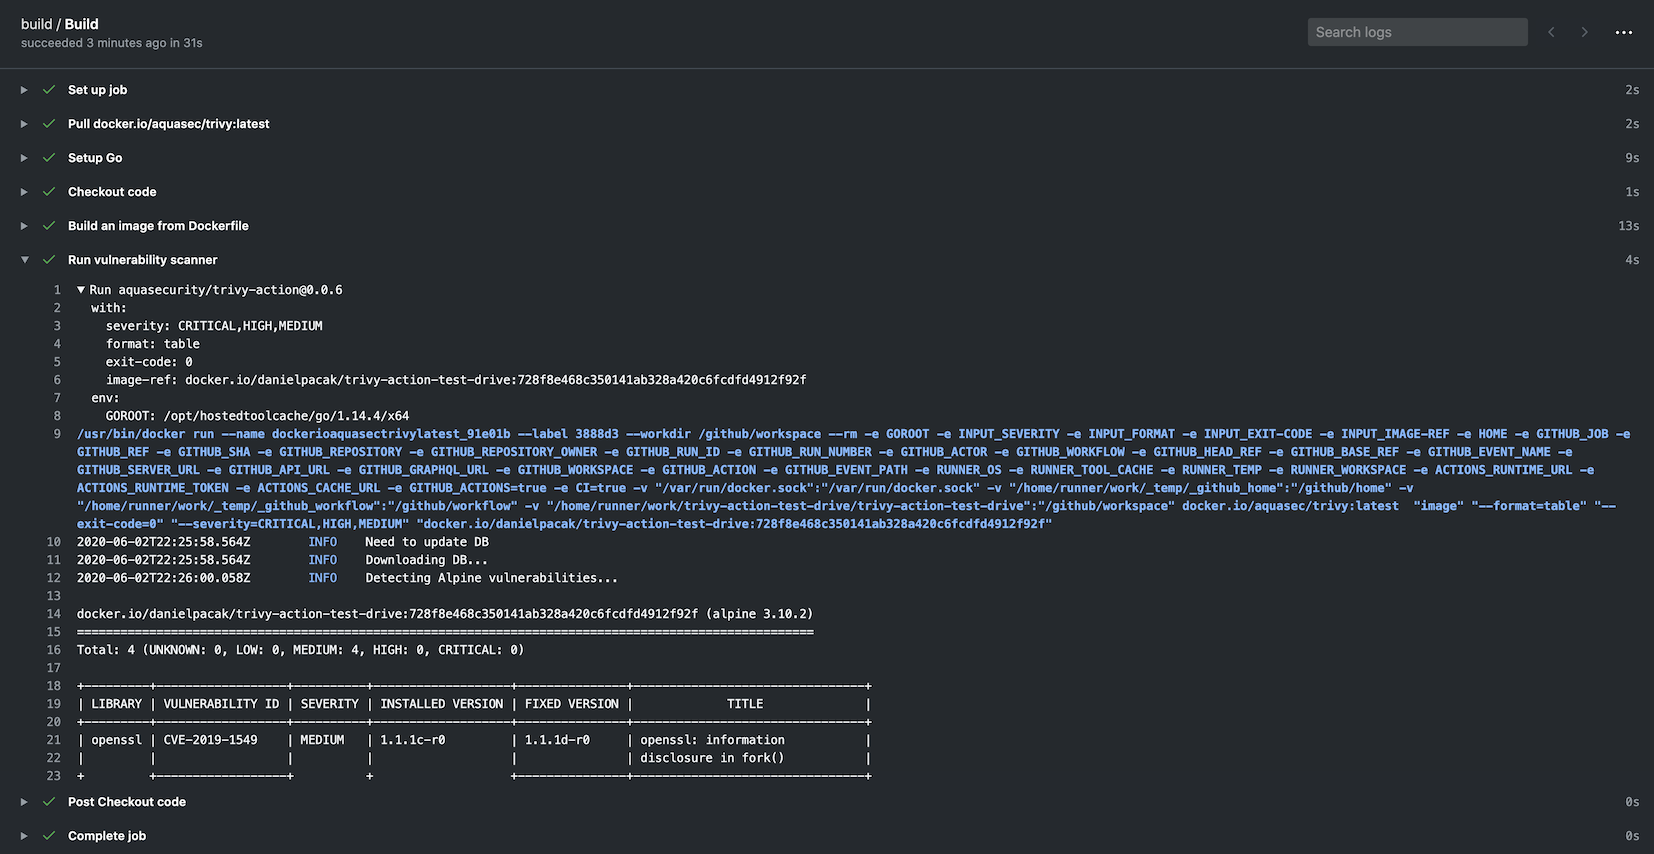 aquasecurity/trivy-action
Runs Trivy as GitHub action to scan your Docker container image for vulnerabilities
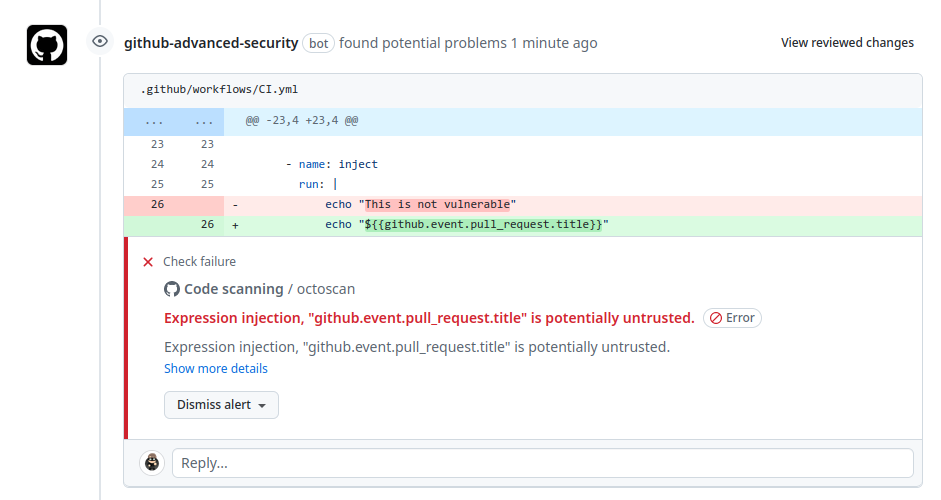 synacktiv/octoscan
Octoscan is a static vulnerability scanner for GitHub action workflows.