
nerva
 praetorian-inc/nerva
Fast service fingerprinting CLI for 170+ protocols (TCP/UDP/SCTP) - built by Praetorian
information-gatheringiot-securitymisconfiguration+4
3224 days ago
praetorian-inc/nervaFast service fingerprinting CLI for 170+ protocols (TCP/UDP/SCTP) - built by Praetorian
 abraxas/kafka-connect-filestream-win
Kafka Connect 4.3.1 - High - Windows FileStream classpath leftover - unauth file read/write
 vampsecure-labs/vamp-forticheck
VampSecure Labs: FortiOS CVE scanner (CVE-2018-13379, CVE-2022-40684, CVE-2023-27997, CVE-2024-21762)
 proviesec/google-dorks
Useful Google Dorks for WebSecurity and Bug Bounty
 abraxas/ats-jsonrpc-unrestricted
Apache Traffic Server 10.2.0 - High - Local - Privilege leftover - JSON-RPC unix socket unrestricted mode 0777
 pervinzahidli/cve-2026-104110
Unauthenticated disclosure of internal folder path, client email, and upload policy for FileRise Pro client portals via /api/pro/portals/get.php
 compasssecurity/entrafalcon
A lightweight PowerShell tool for assessing the security posture of Microsoft Entra ID environments. It helps identify privileged objects, risky…
 minhhk68/cve-2026-13736
Proof-of-concept exploit and technical advisory for an unauthenticated member PII disclosure in a WordPress REST API directory plugin, including…
 gopasteverything/gpewebdefender
Lightweight web-attack monitor. One Go binary + SQLite. Not OSSEC, not a WAF.
 johenlastgen-jlg/cve-2026-11961
CVE-2026-11961 — UserRegistration: WordPress User Registration <= 5.2.2 Privilege Escalation. Misconfigured Membership Roles → Unauthenticated Admin…
 redteambrasil/cve-2020-24029
Detailed disclosure of an unauthenticated password change vulnerability in ForLogic Qualiex v1 and v3, enabling remote privilege escalation and…
 huseyn0vs/cve-2026-16540-simplyscheduleappointments
CVE-2026-16540 — Simply Schedule Appointments < 1.6.12.6 Unauthenticated Appointment Data Disclosure and Mass Deletion
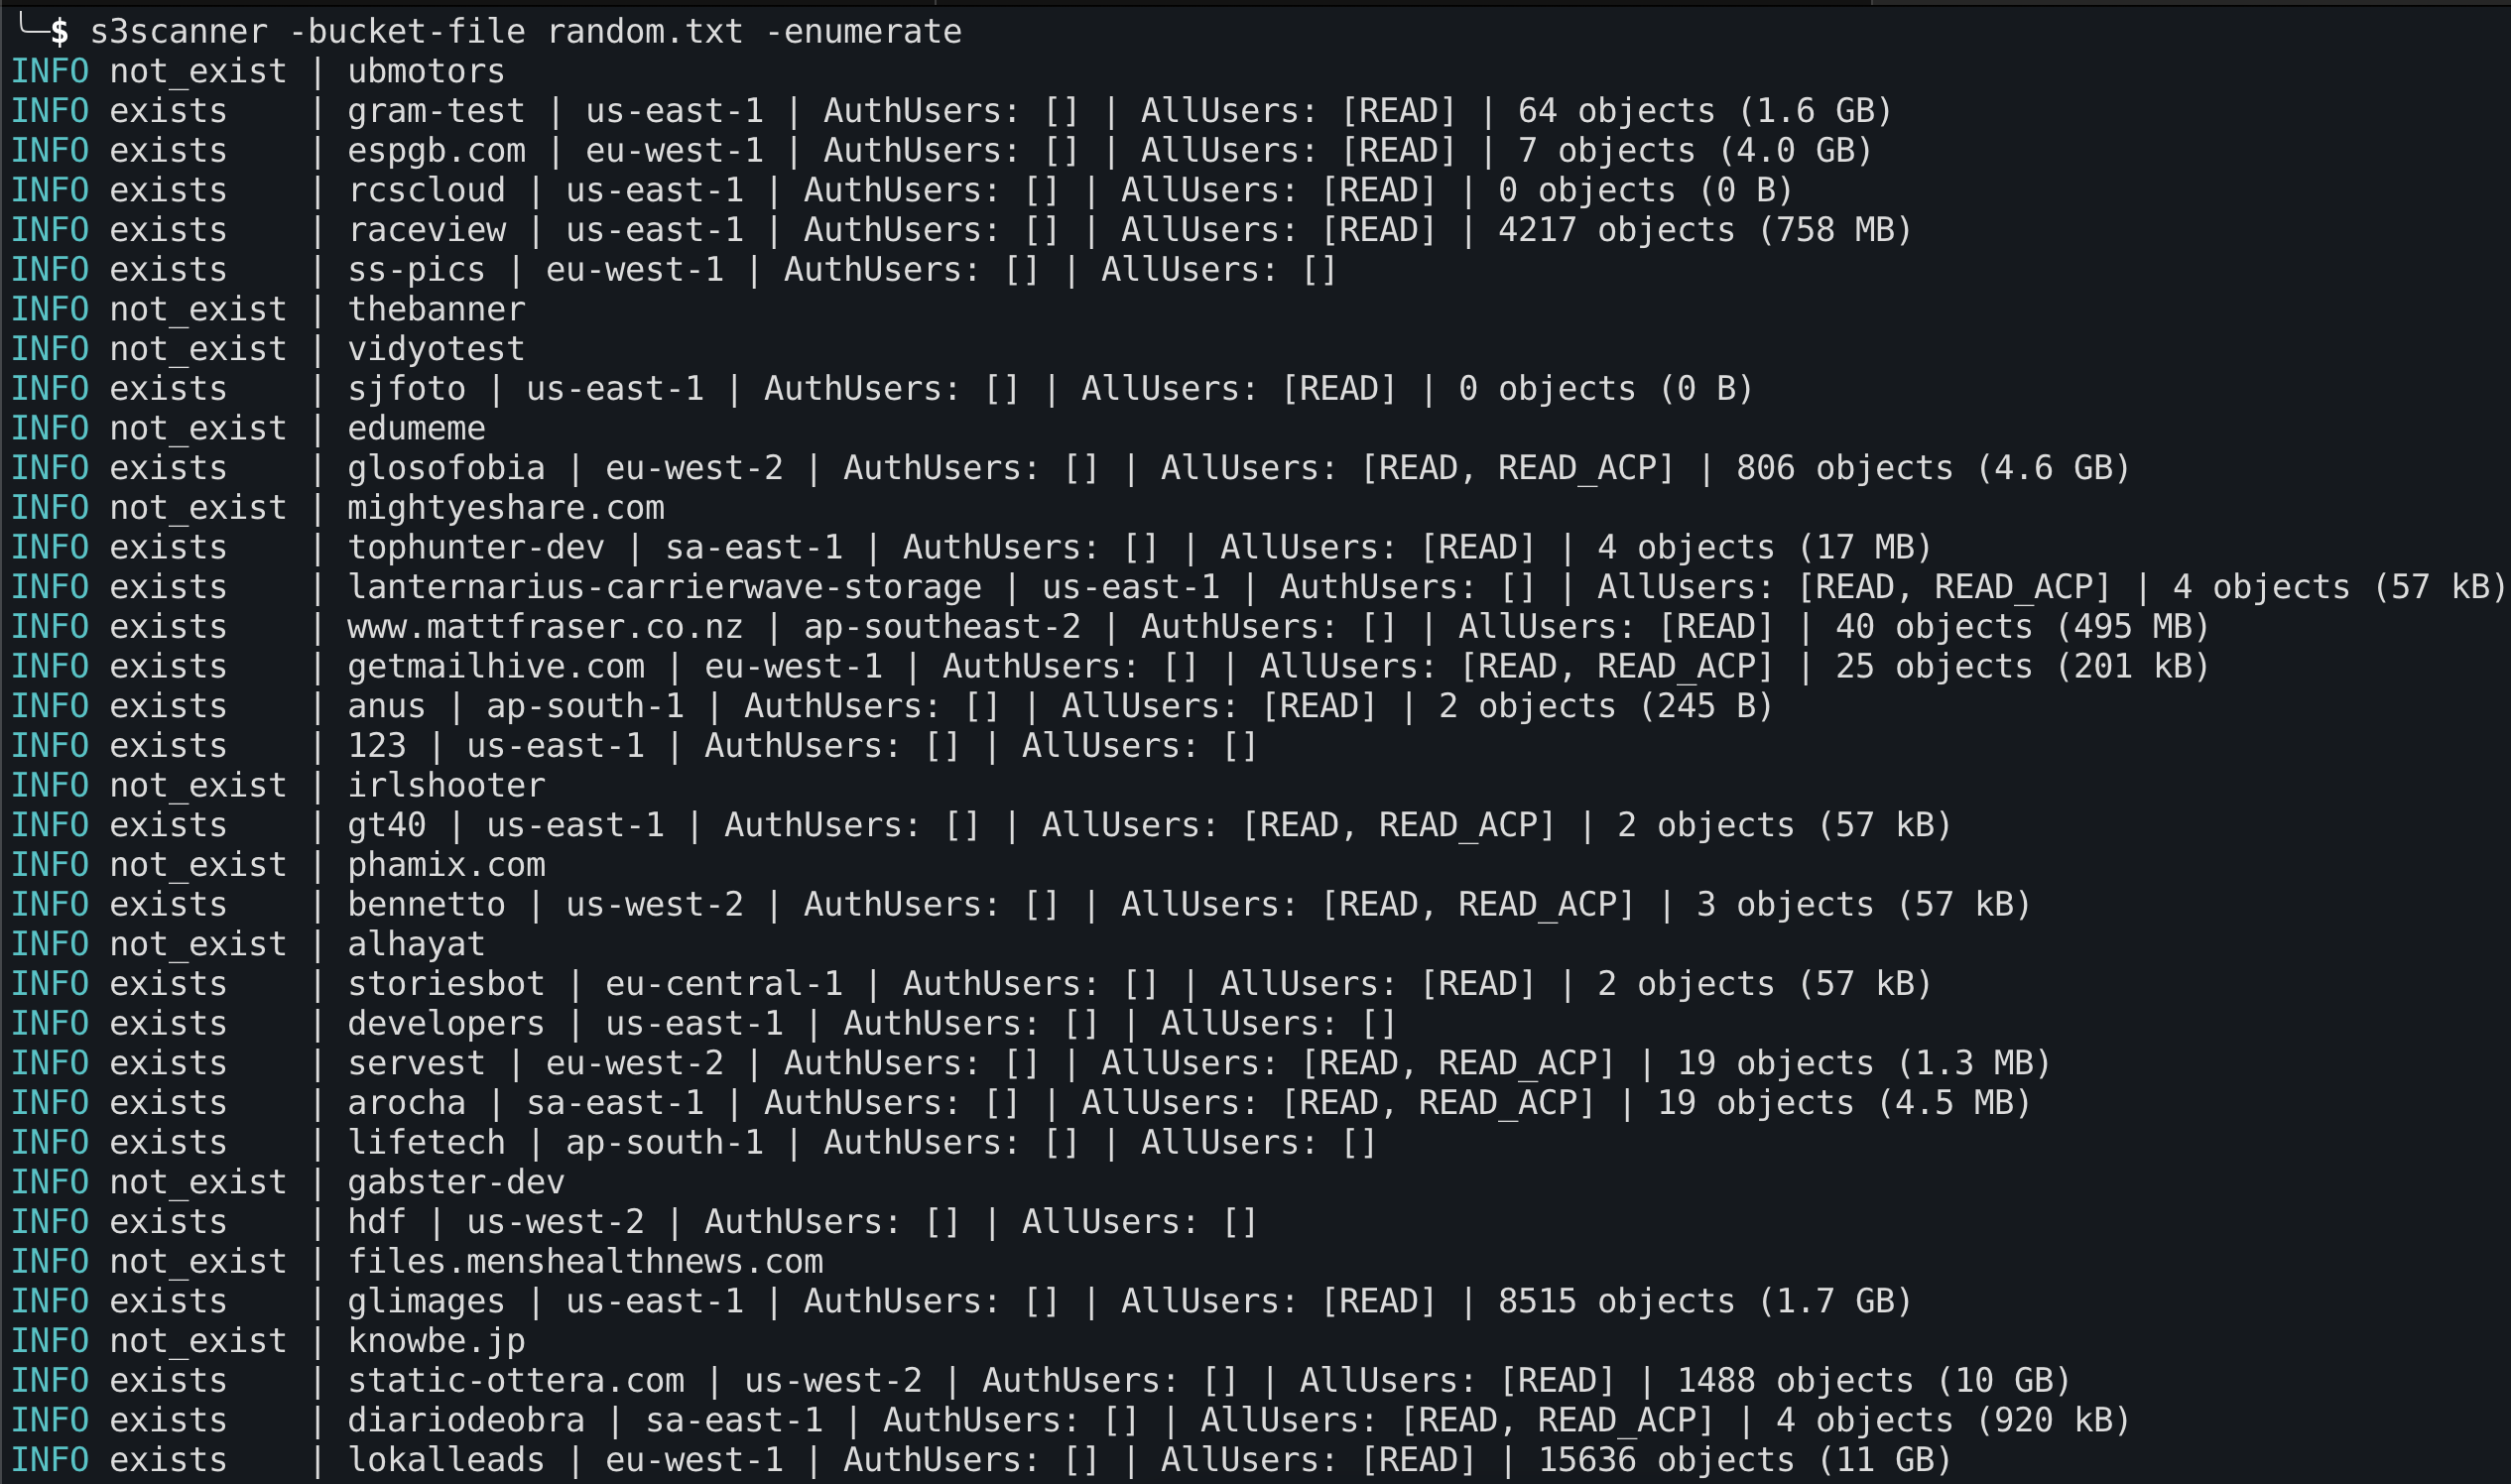 sa7mon/s3scanner
Scan for misconfigured S3 buckets across S3-compatible APIs!
 bountyyfi/azure-apim-cross-tenant-signup-bypass
Security advisory: Azure APIM Developer Portal allows cross-tenant account registration by bypassing UI signup restrictions. Reported to MSRC twice -…
 kh4sh3i/cve-2023-22515
CVE-2023-22515 - Broken Access Control Vulnerability in Confluence Data Center and Server
 michaeladamgroberman/cve-2026-55726
CVE-2026-55726: Publicly Listable Azure Blob Storage Container (device logs) - Gardyn (ICSA-26-183-03)
 jfs-jfs/cve-2026-37069
Proof-of-concept for absolute path disclosure in Veno File Manager 4.4.9 via an unauthenticated GET request to a debug script, revealing the server's…
 jfs-jfs/cve-2026-37067
Incorrect access control in /vfm-admin/admin-panel/view/save-cvs.php in Veno File Manager Project 4.4.9 allows an unauthenticated attacker to extract…