
cli
 snyk/cli
Snyk CLI scans and monitors your projects for security vulnerabilities.
cloud-infrastructure-securitycode-analysiscontainer-security+6
snyk/cliSnyk CLI scans and monitors your projects for security vulnerabilities.
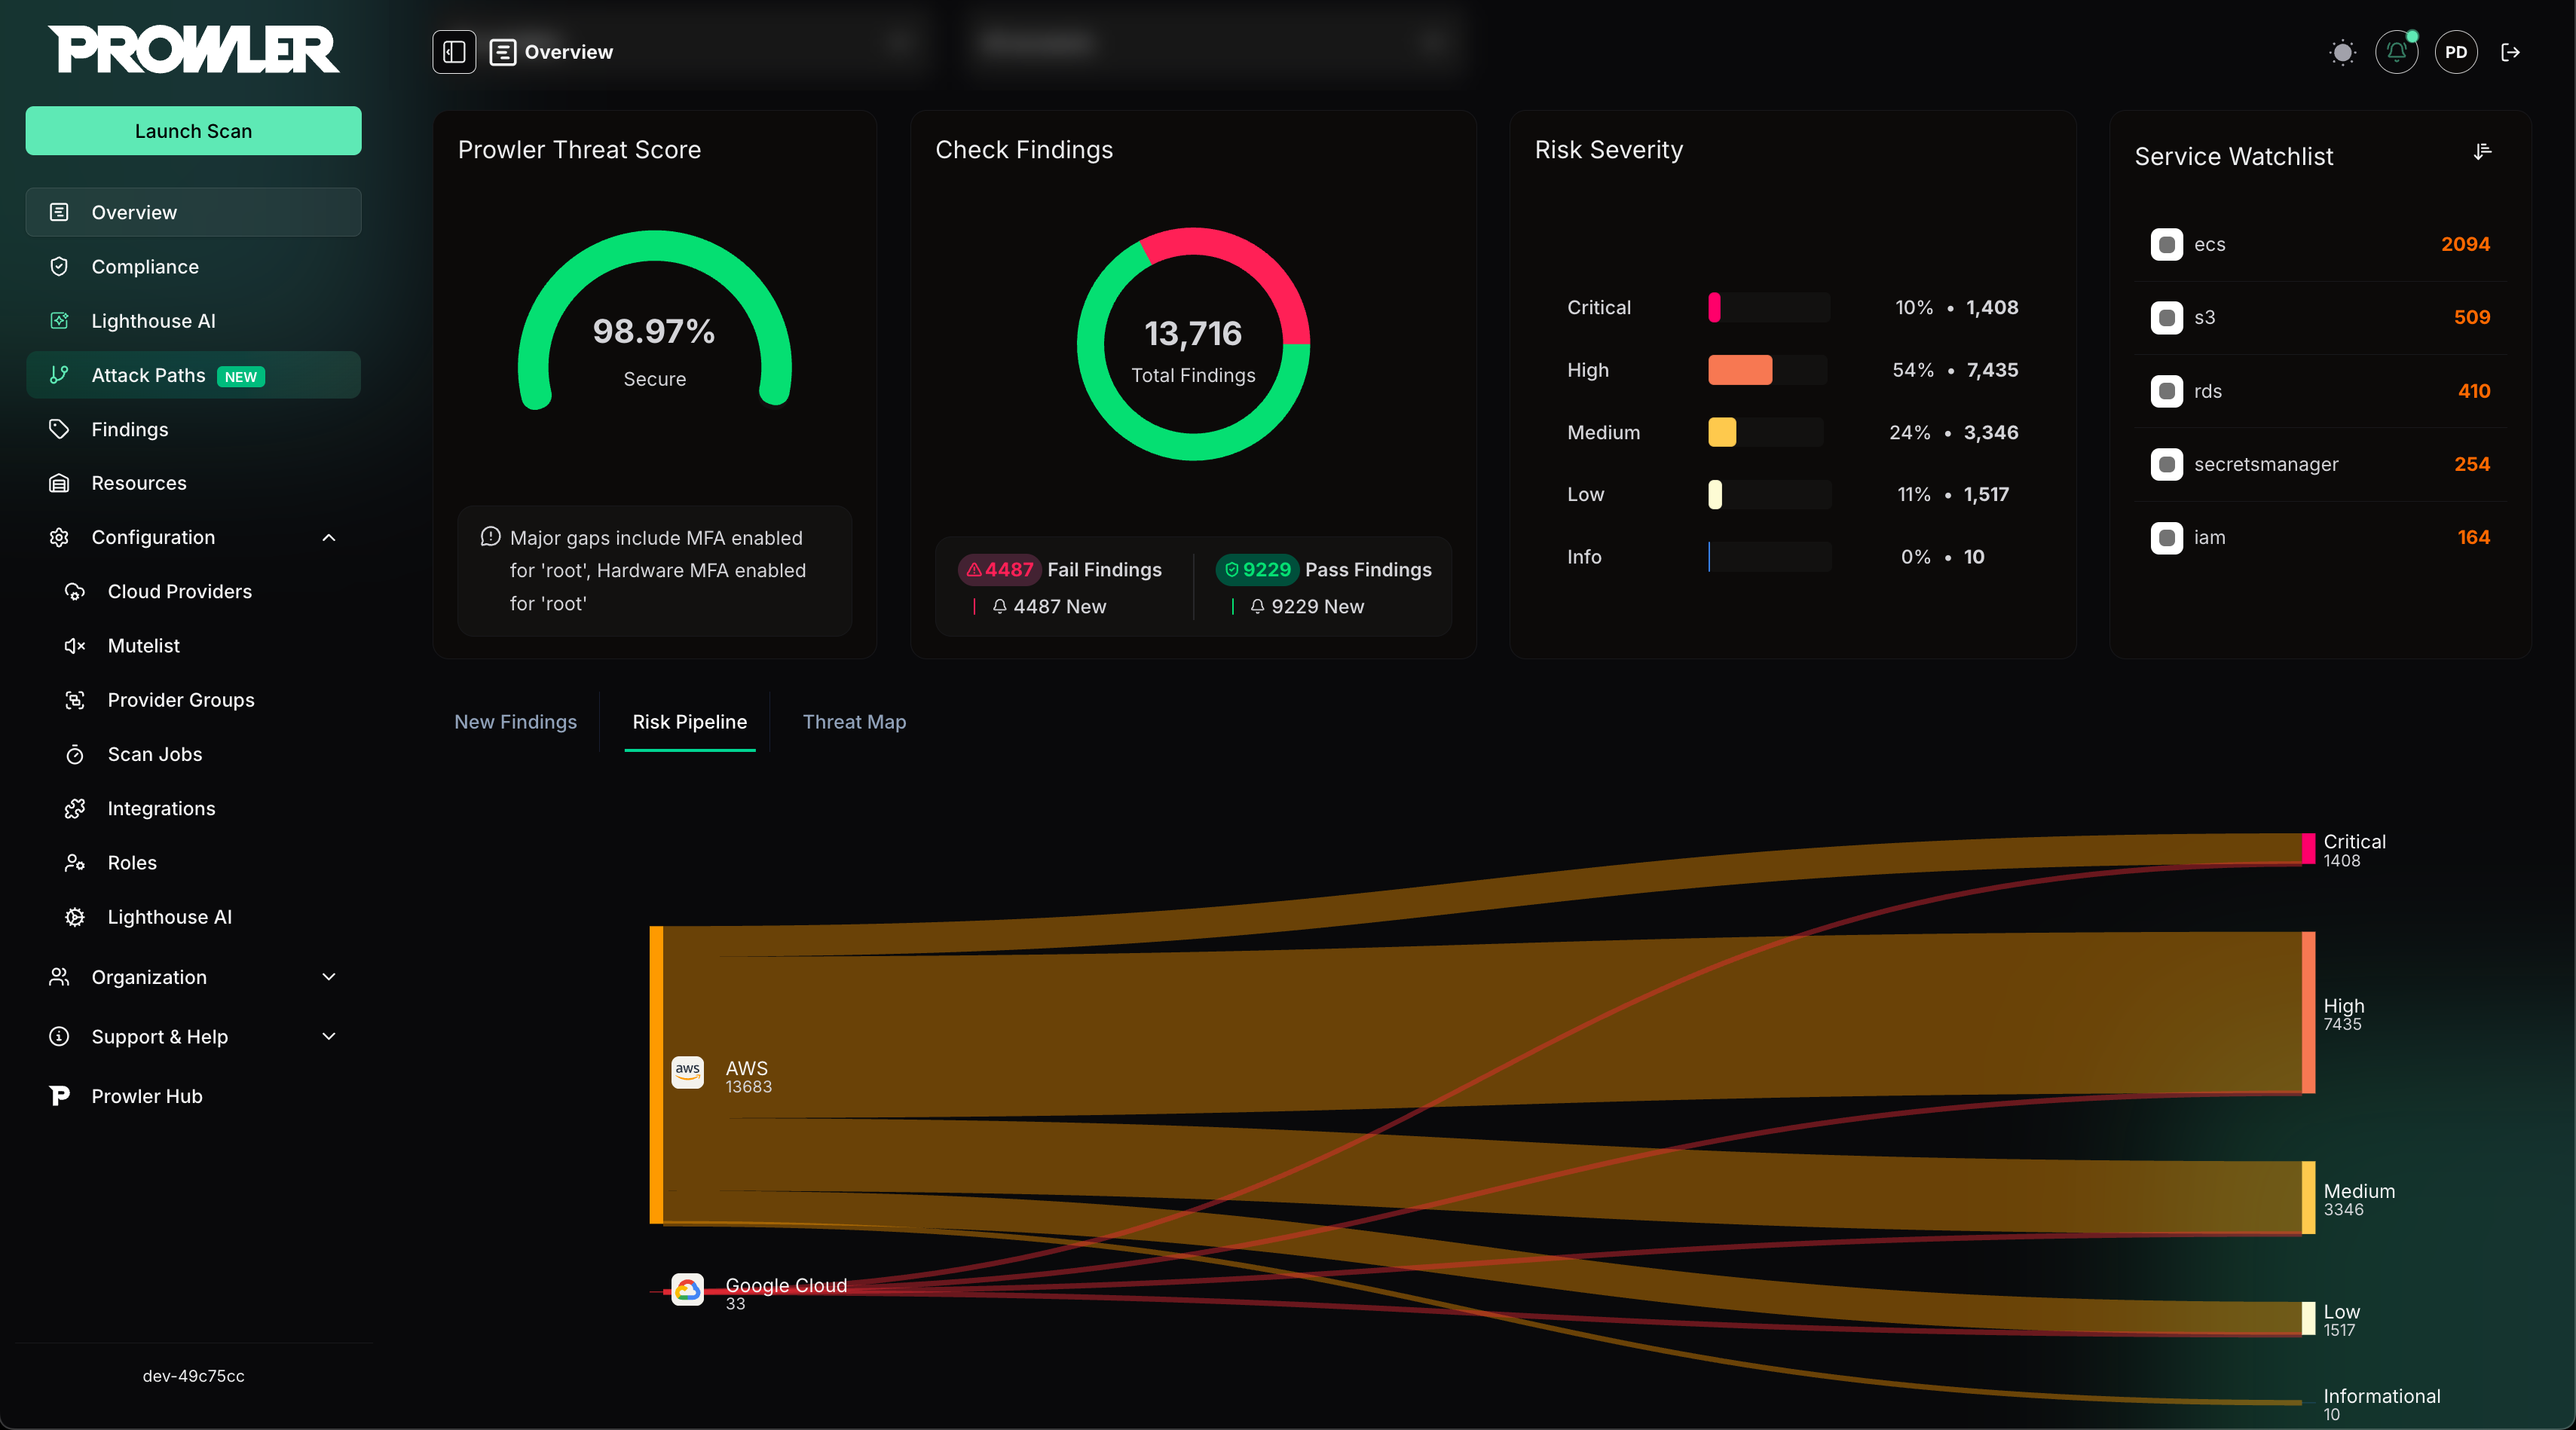 prowler-cloud/prowler
Prowler is the world’s most widely used open-source cloud security platform that automates security and compliance across any cloud environment.…
 open-policy-agent/opa
Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
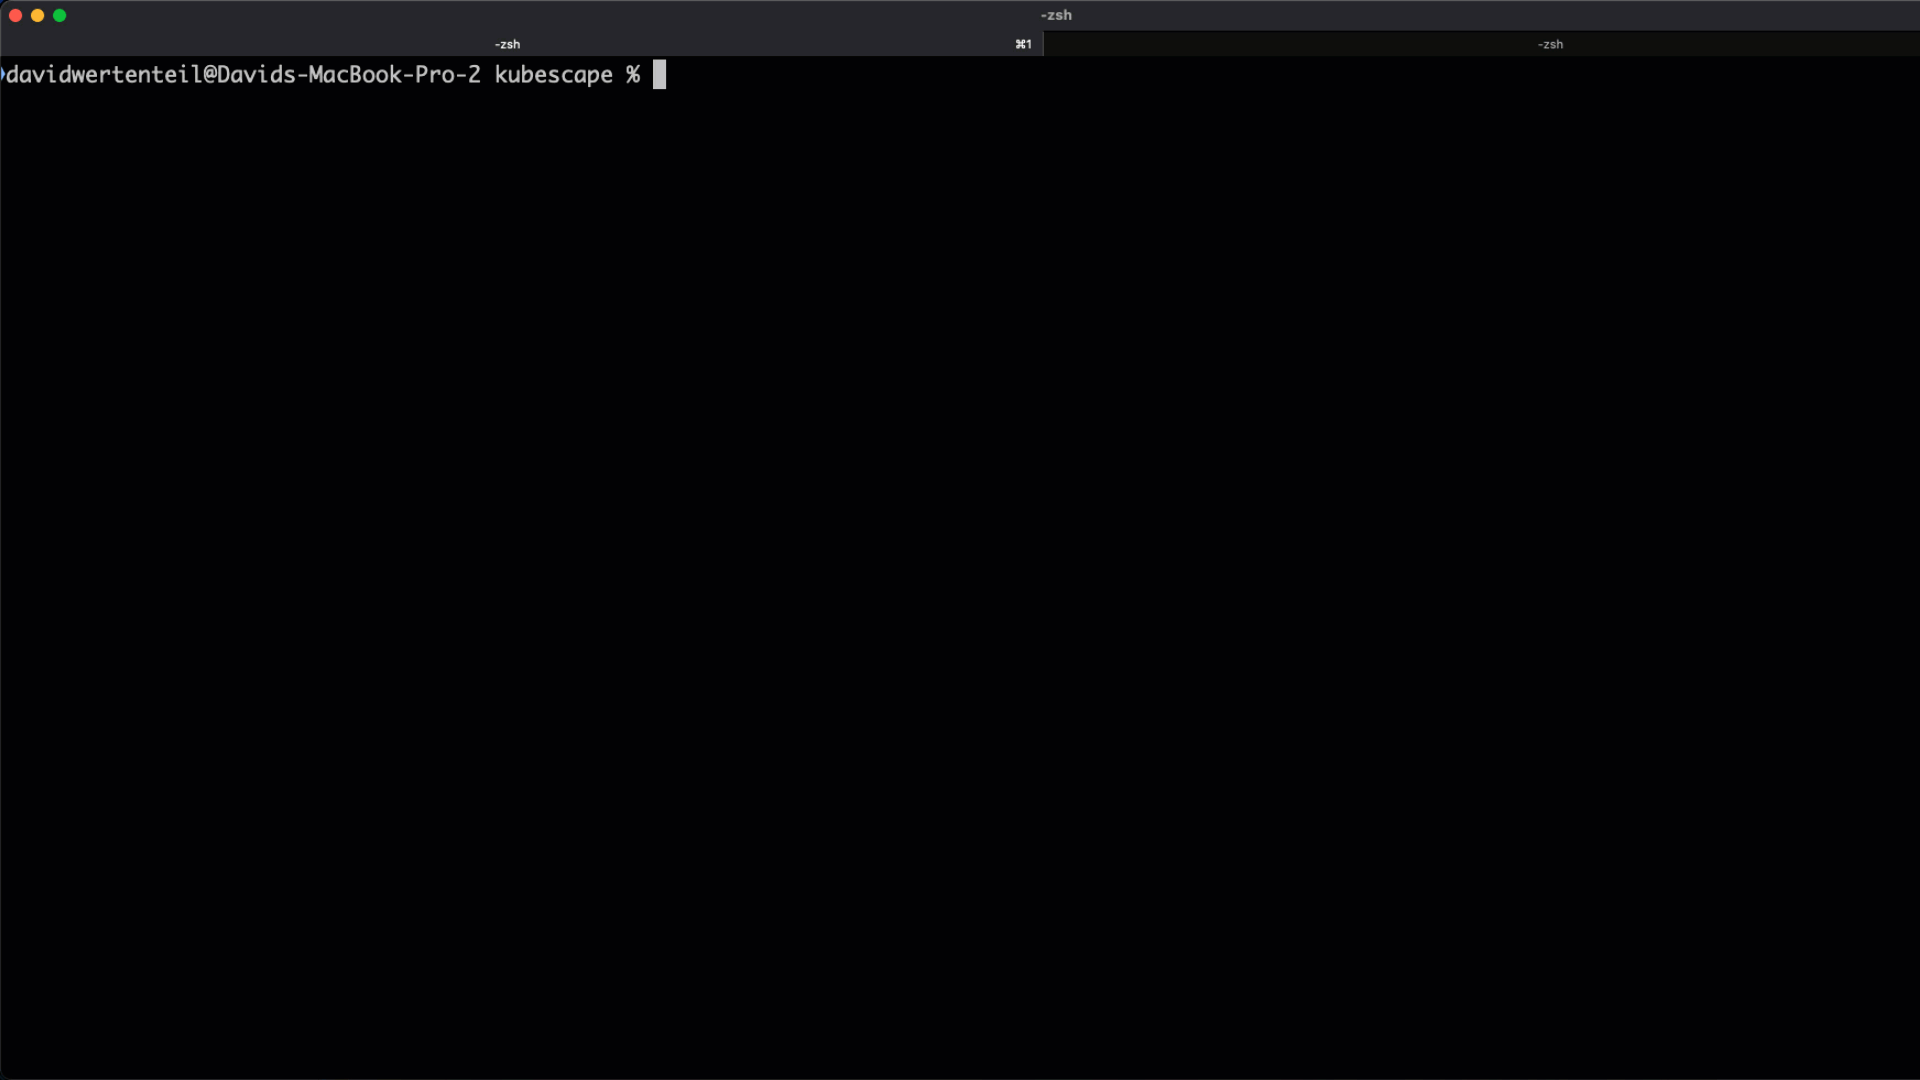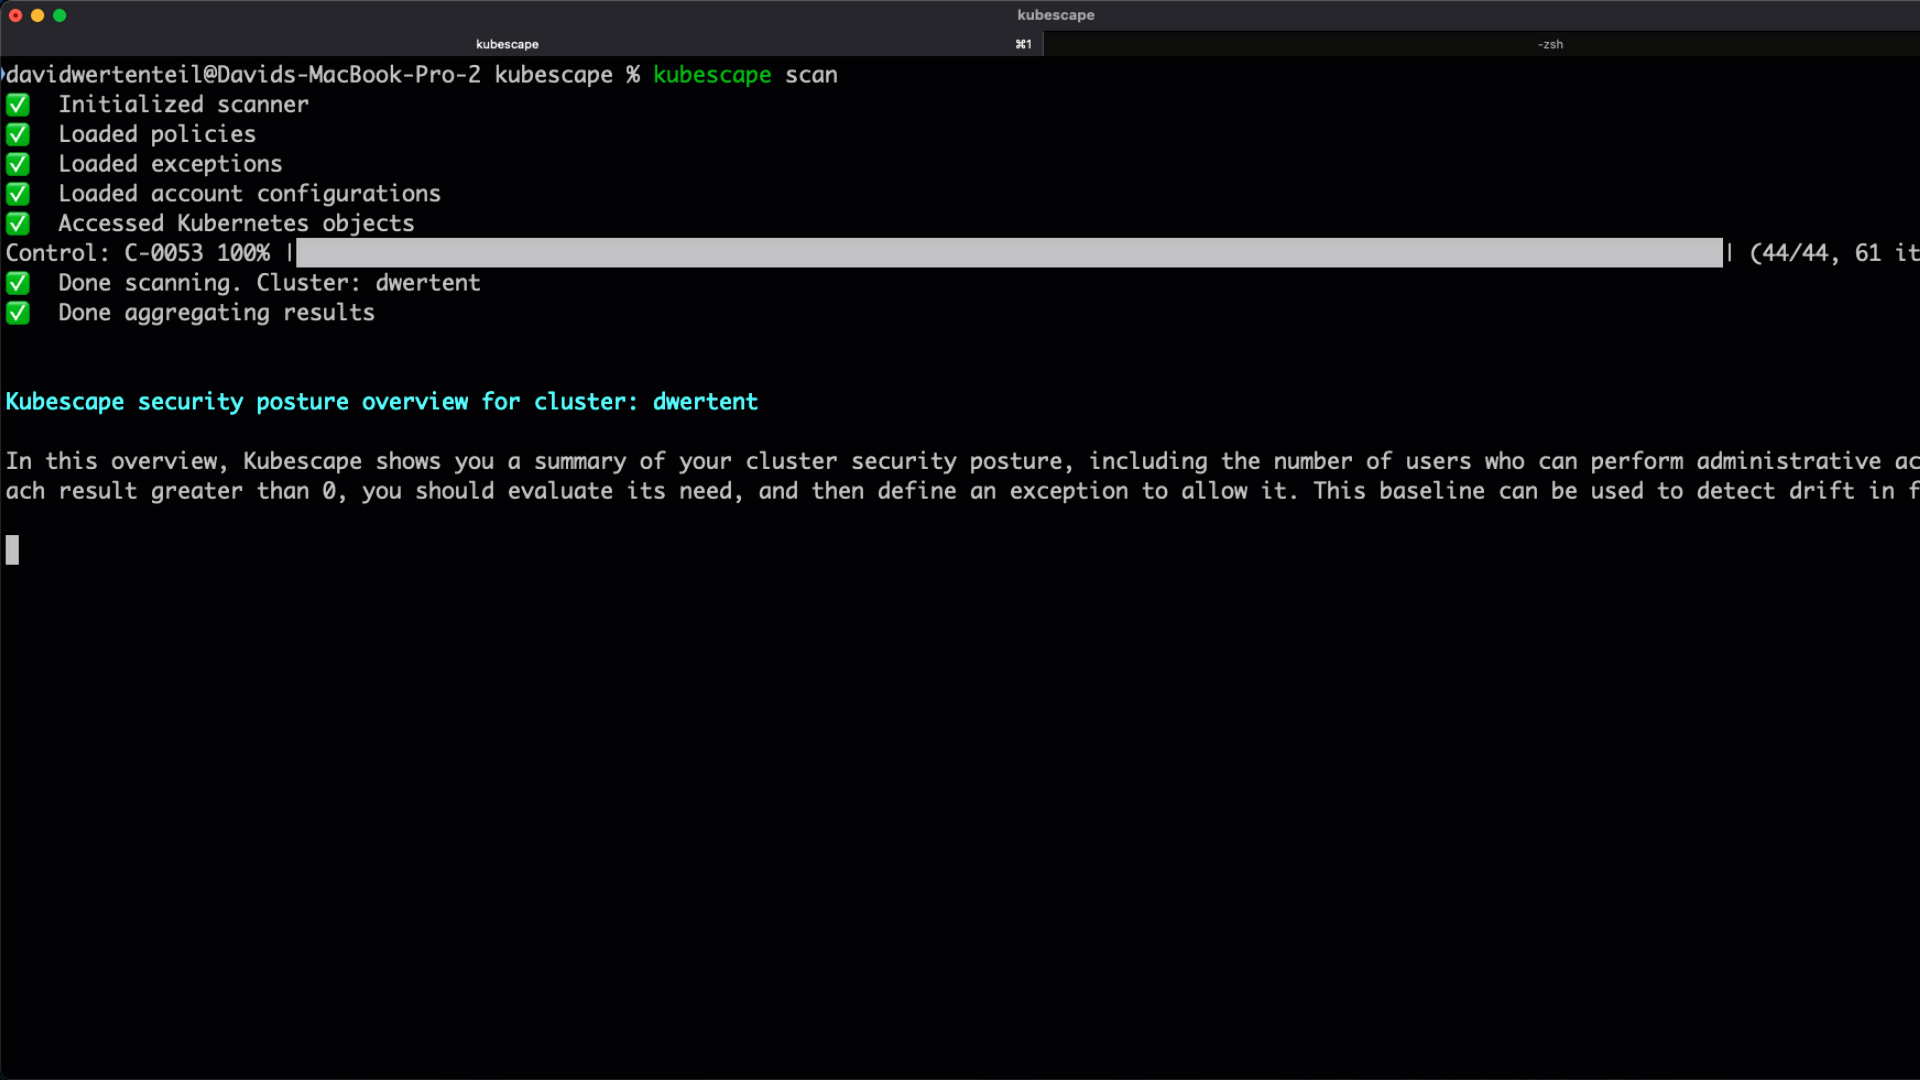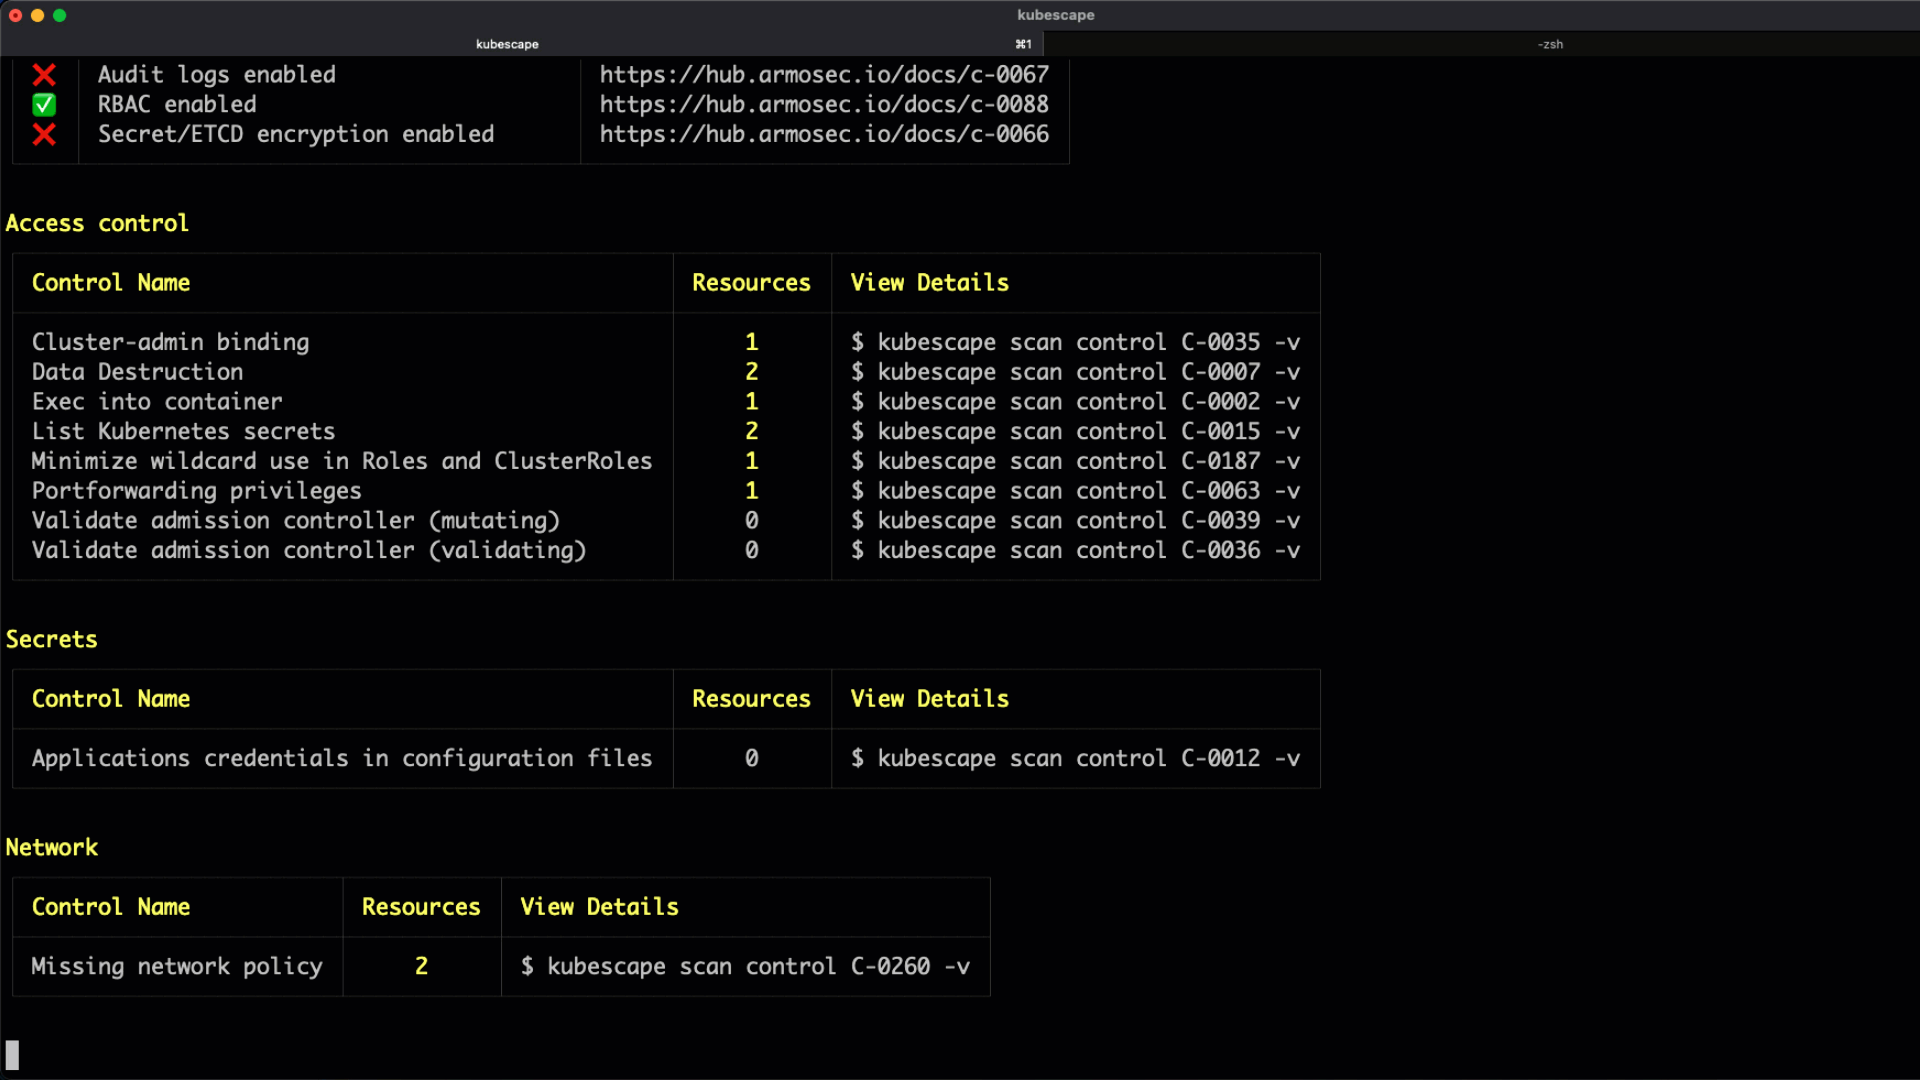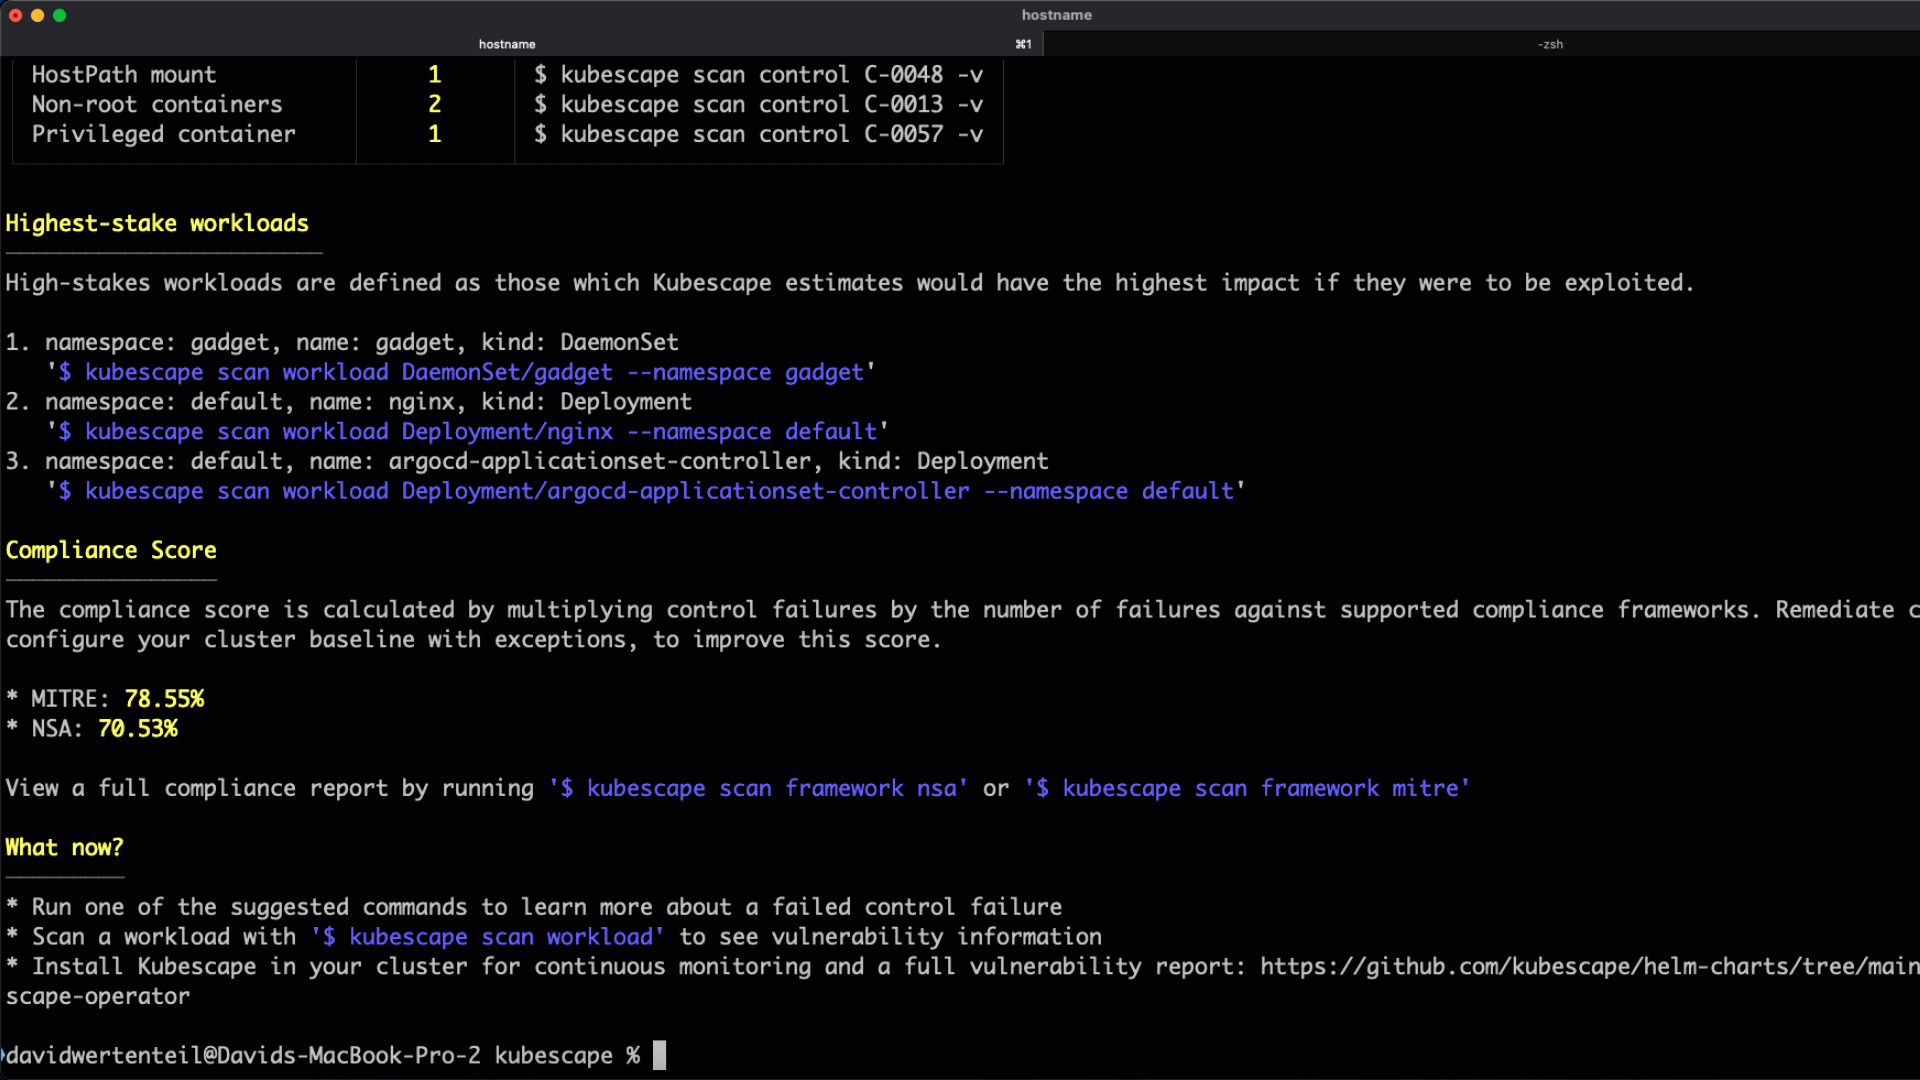 kubescape/kubescape
Open-source Kubernetes security platform scanning clusters, manifests, and images for misconfigurations, vulnerabilities, and compliance against NSA,…
 kyverno/kyverno
Enforce security and compliance on Kubernetes clusters via admission controls, resource mutation, background scans, and container image signature…
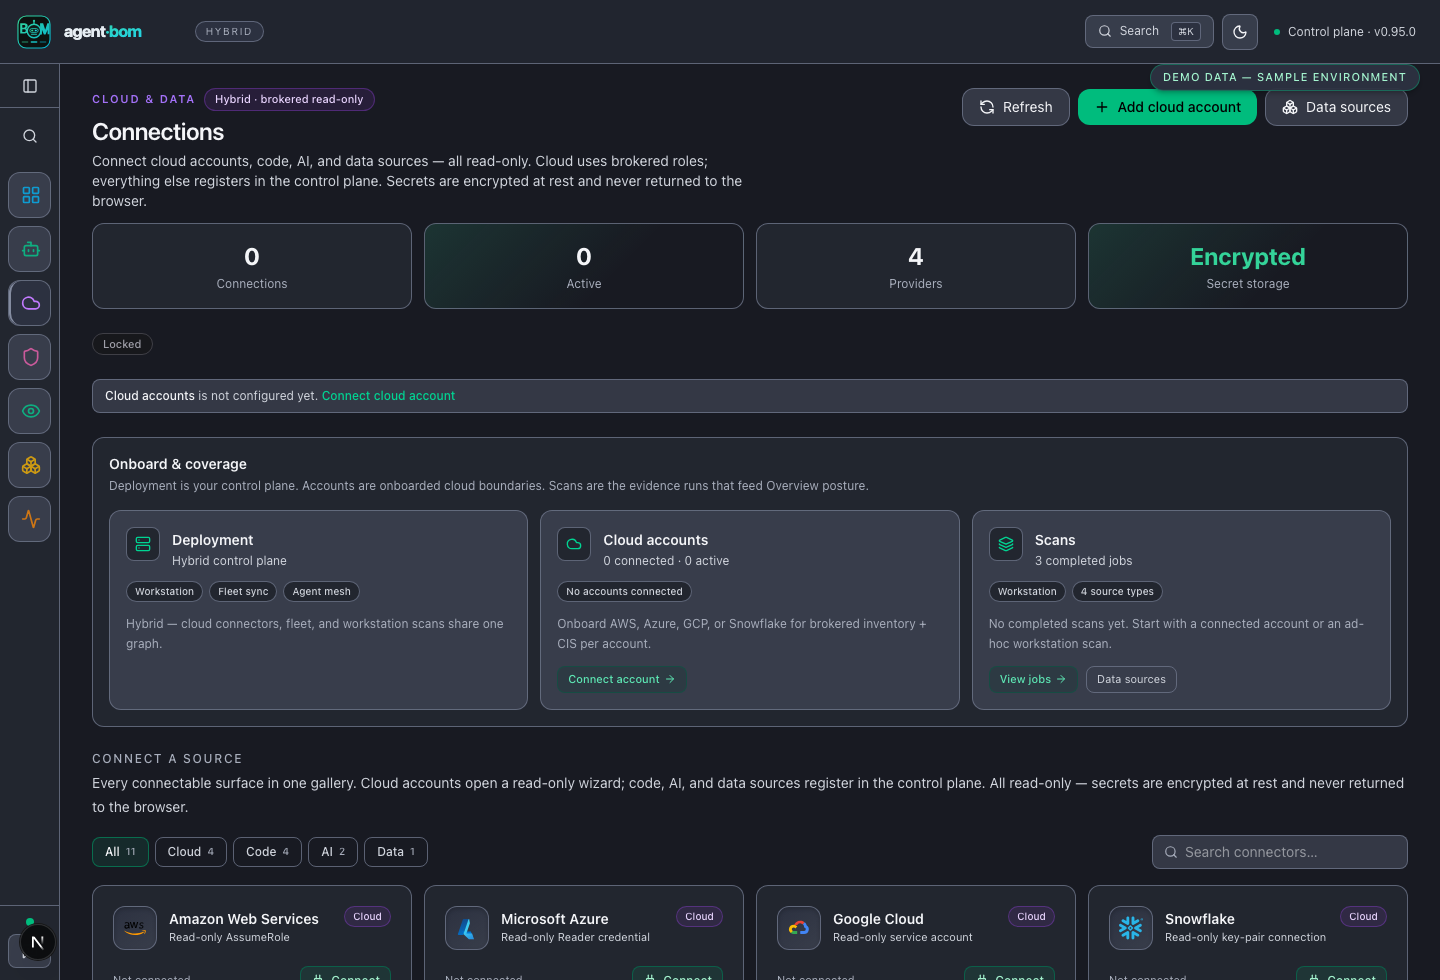 msaad00/agent-bom
Open security scanner and self-hosted control plane for AI, MCP, and cloud. One evidence model — run scans in your environment, centralize findings,…
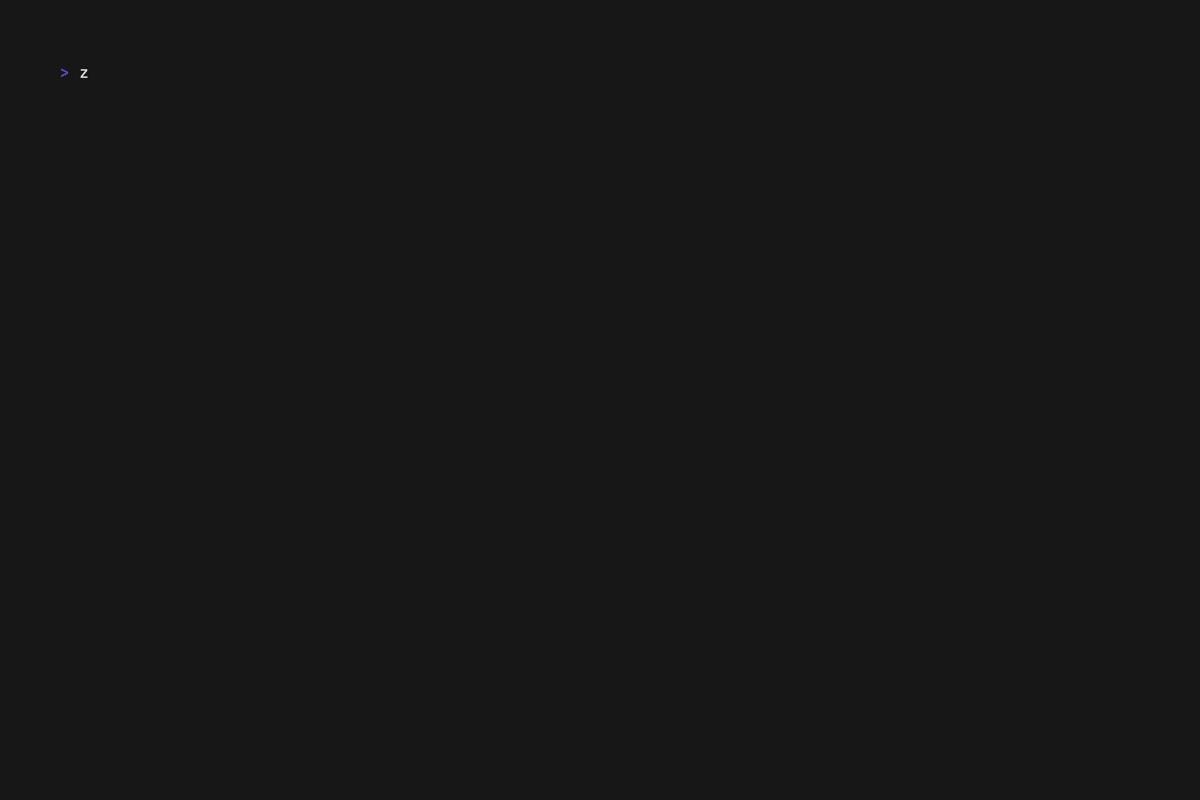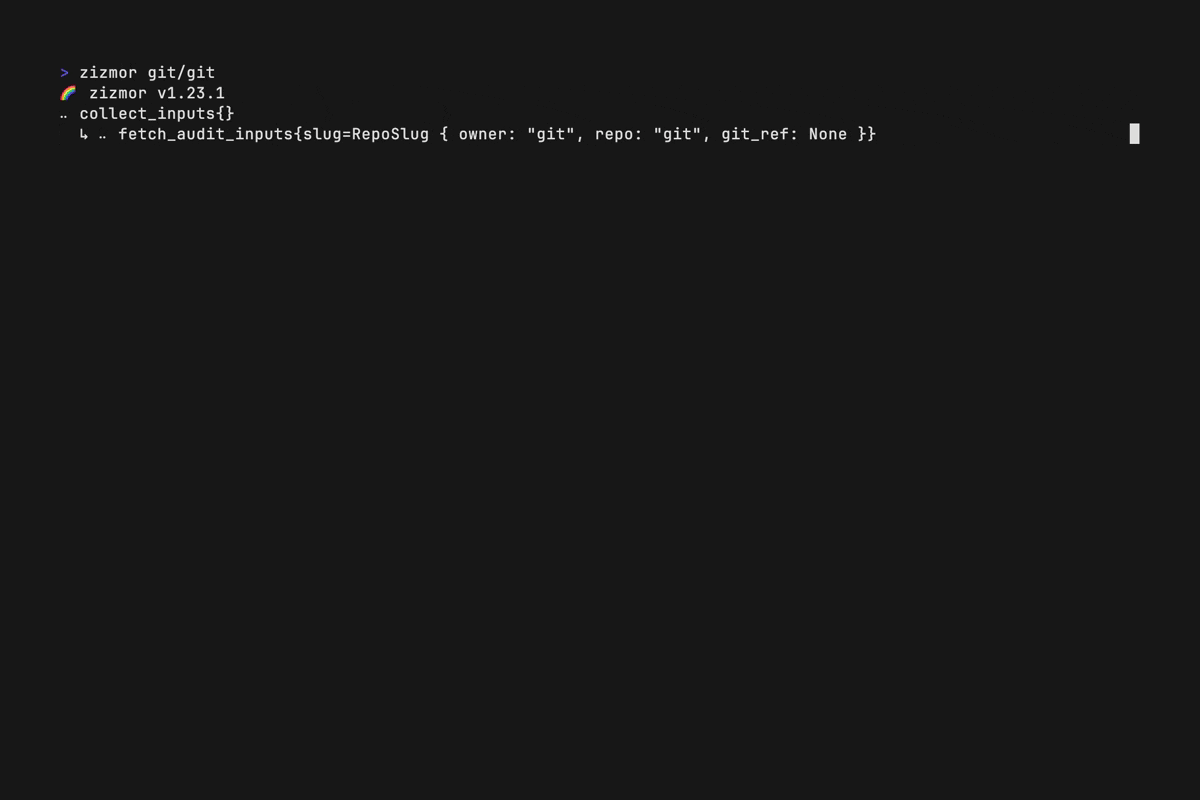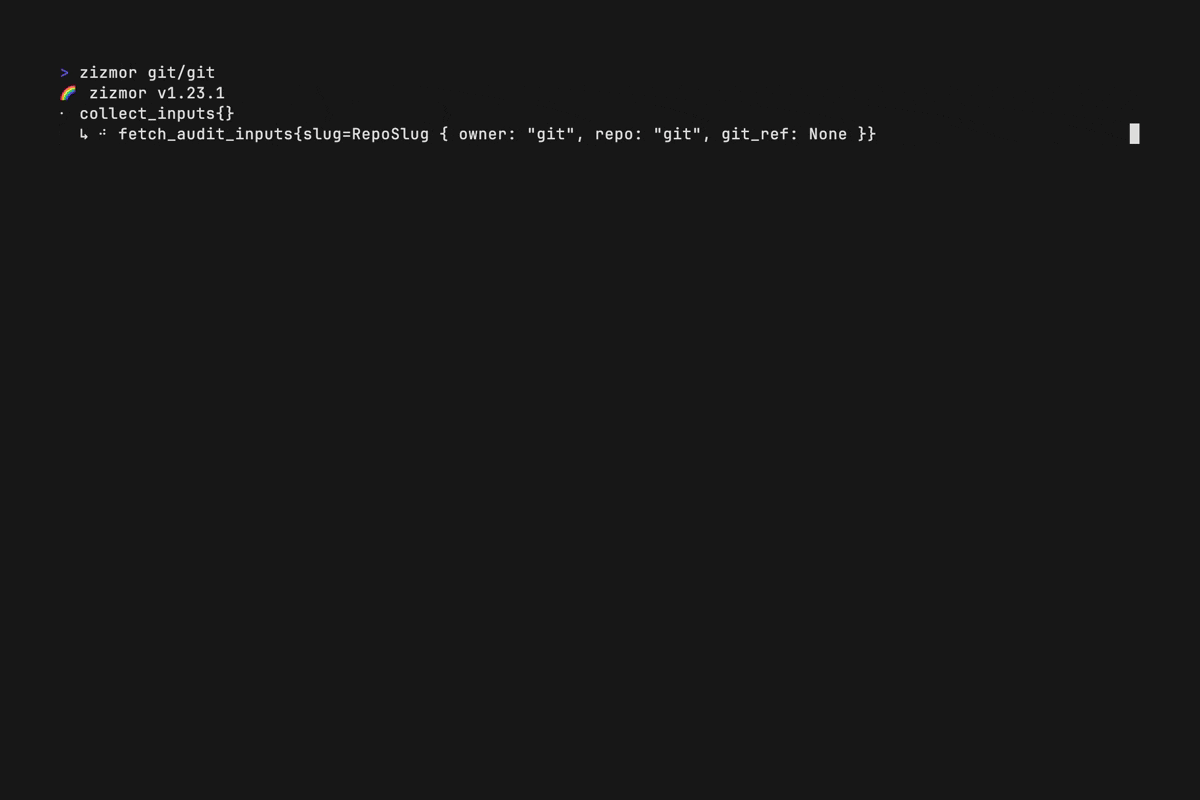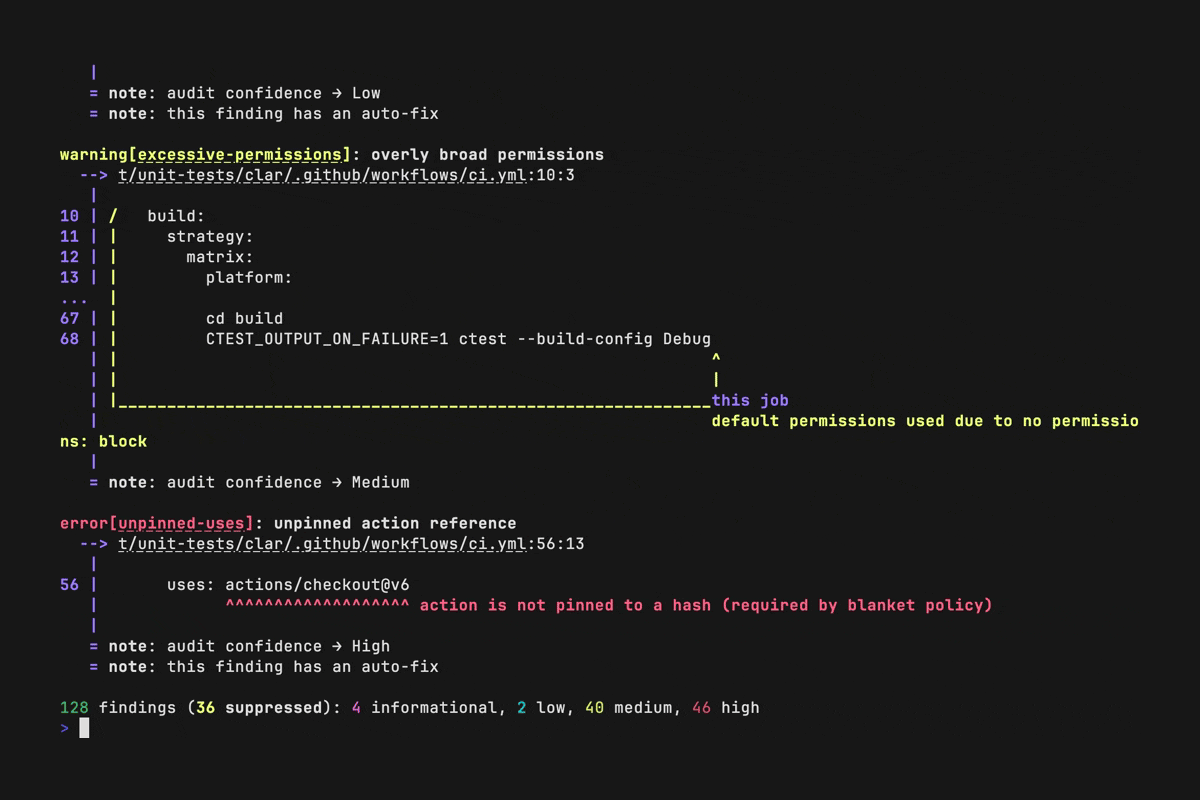 zizmorcore/zizmor
Static analysis tool for CI/CD systems that detects and fixes security issues in GitHub Actions, Dependabot, and pre-commit configurations, including…
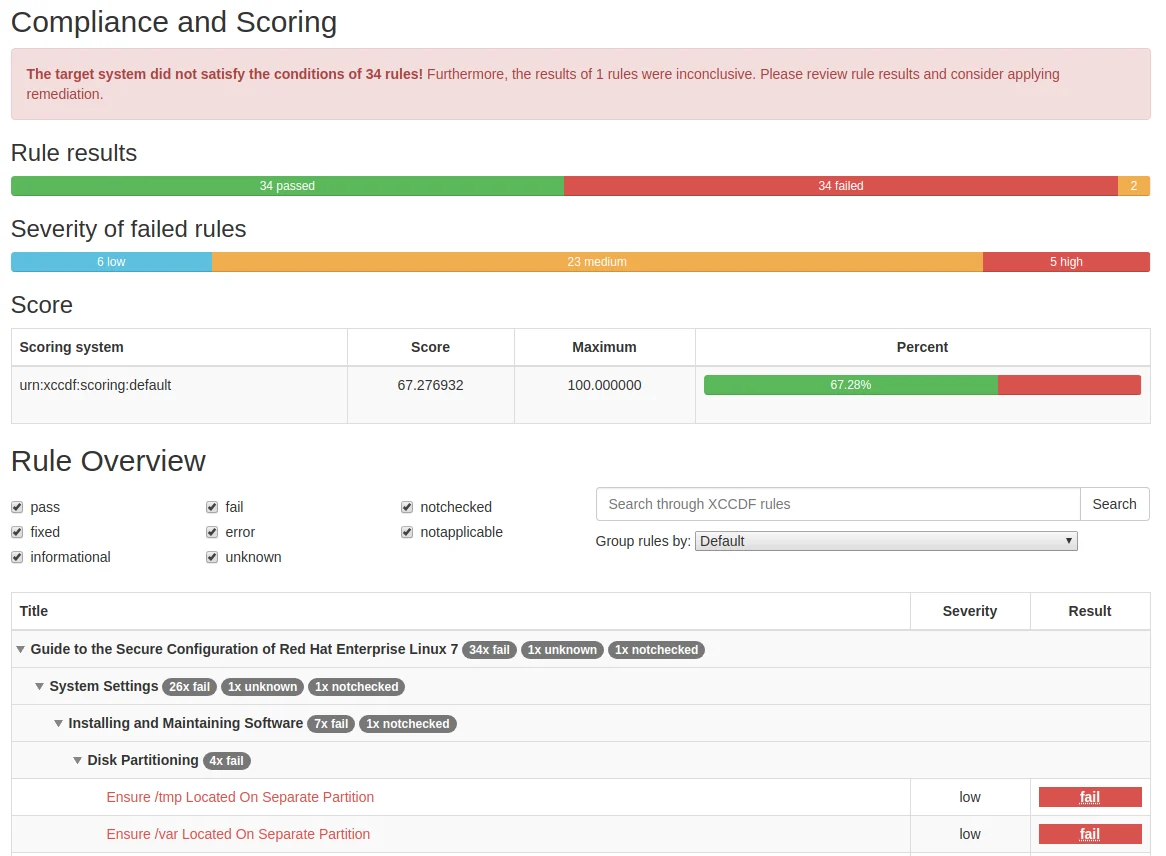 complianceascode/content
Generates SCAP, Ansible, Bash, and CEL security content for compliance evaluation and automated hardening across Linux hosts, containers, and…
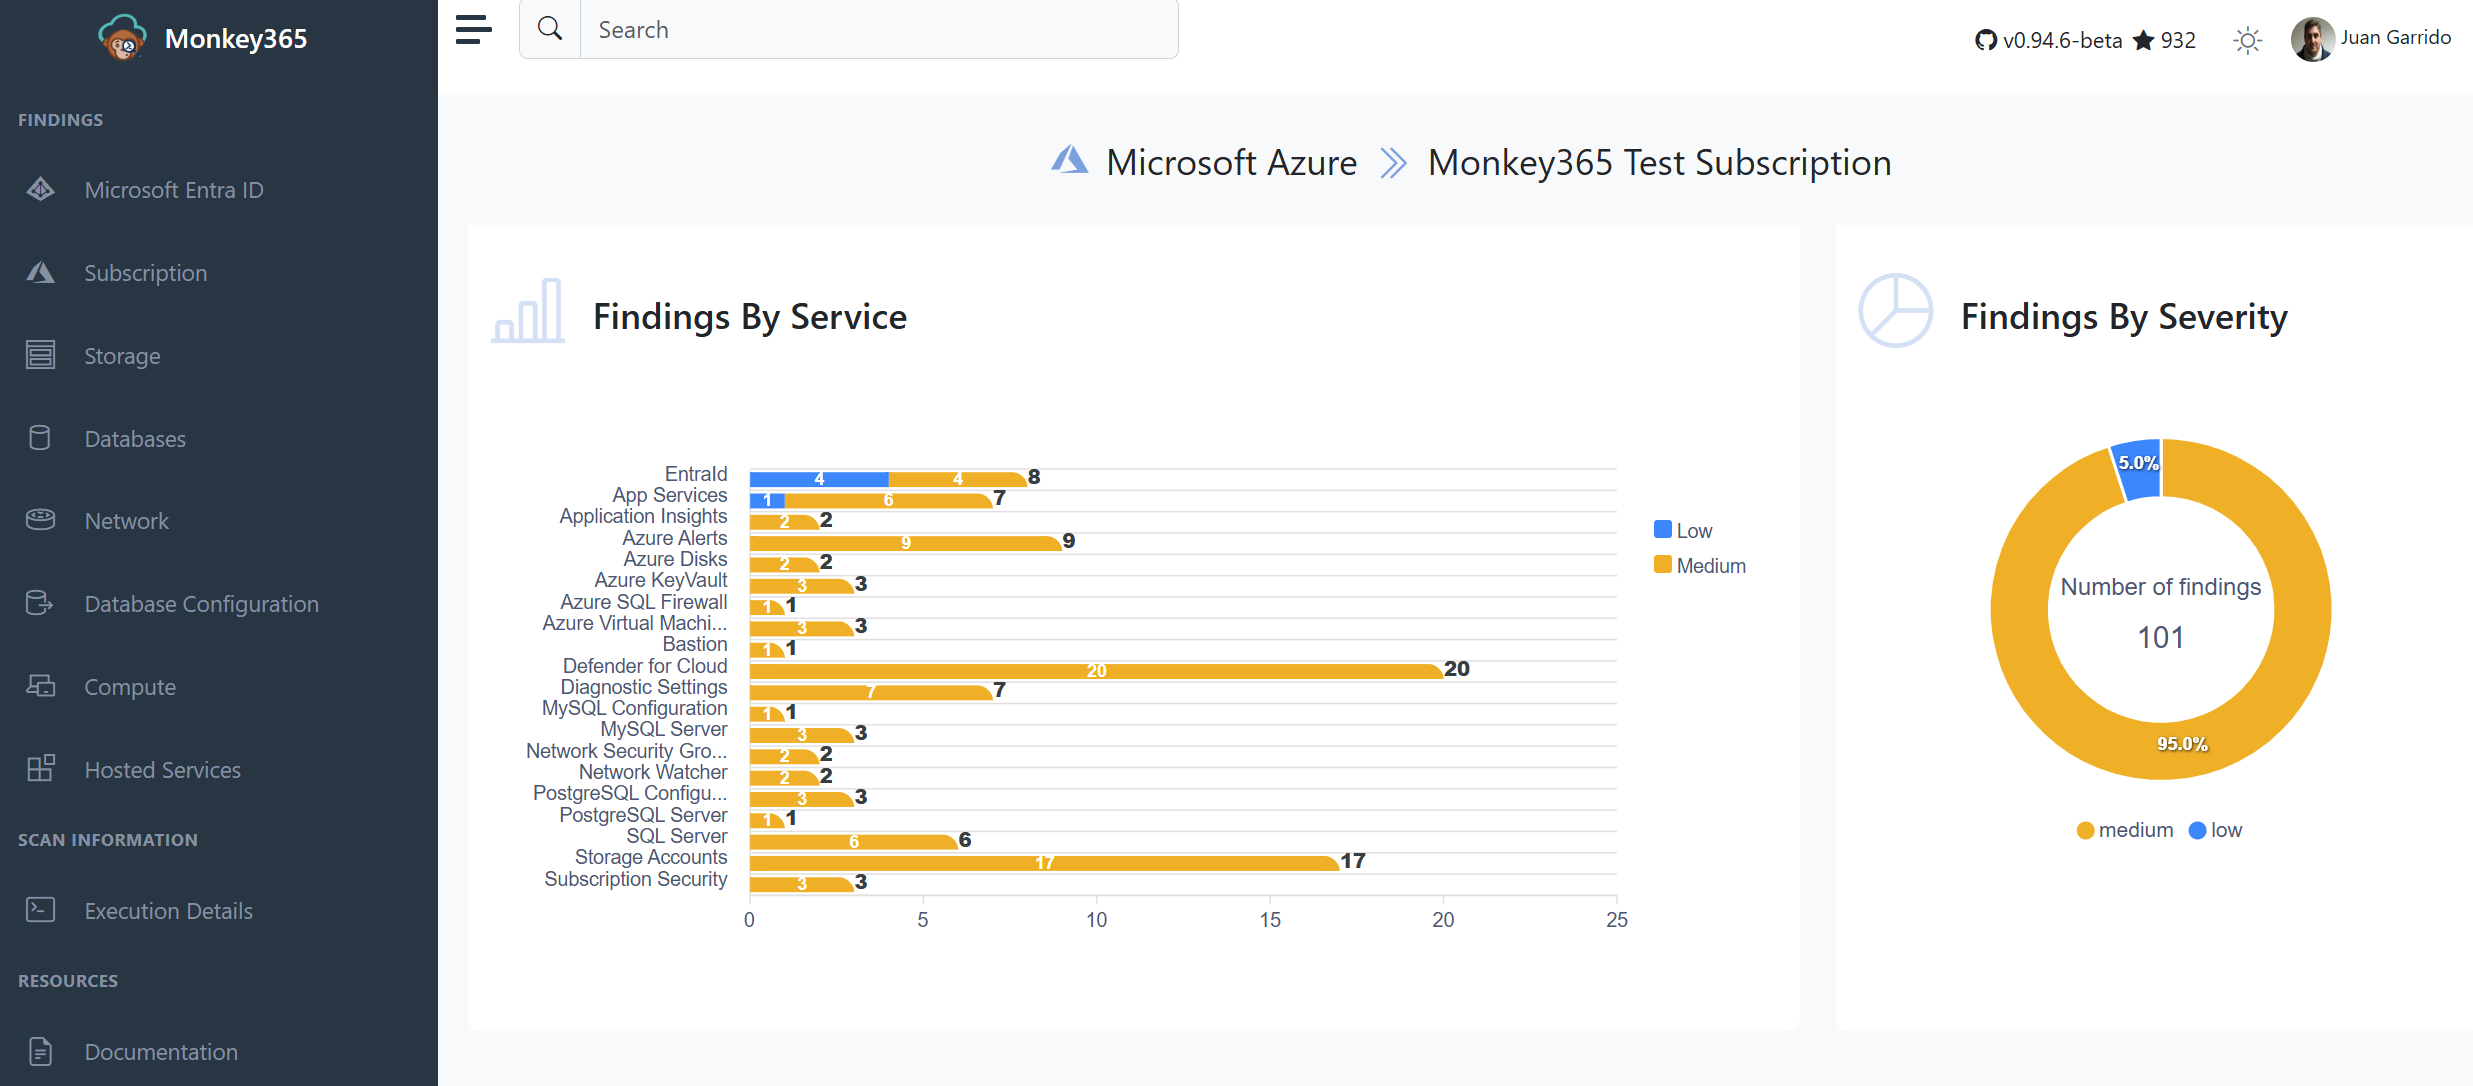 silverhack/monkey365
PowerShell-based security assessment framework for Microsoft 365, Azure, and Entra ID. Scans for misconfigurations, CIS benchmark compliance, and…
 cloud-custodian/cloud-custodian
Rules engine for cloud security, cost optimization, and governance, DSL in yaml for policies to query, filter, and take actions on resources
 stackrox/kube-linter
KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…
 jvoisin/snuffleupagus
Security module for php7 and php8 - Killing bugclasses and virtual-patching the rest!
 cynative/cynative
Read-only AI agent that queries your cloud, code, and runtime infrastructure to surface misconfigurations, leaked secrets, and privilege escalation…
 jp1337/easywall
Web interface for the nftables firewall on Linux, written in Go. The apply undoes itself after 120 seconds unless you confirm it — you cannot lock…
 coreruleset/coreruleset
Generic attack detection rule set for web application firewalls, protecting against OWASP Top Ten and common vulnerabilities with minimal false…
 vercel-labs/deepsec
Agent-powered vulnerability scanner for large-scale codebases. Uses LLMs to find hard-to-detect security issues via regex matchers and AI…
 dev-sec/ansible-collection-hardening
This Ansible collection provides battle tested hardening for Linux, SSH, nginx, MySQL