openclaw_vulnerabilities_and_solutions

> OpenClaw security audit and hardened deployment guide — known vulnerabilities (CVE-2026-25253, malicious skills, credential leakage), architectural…

> OpenClaw security audit and hardened deployment guide — known vulnerabilities (CVE-2026-25253, malicious skills, credential leakage), architectural…

PoC for CVE-2026-22015: malicious event injects environment variables into serverless functions, overwriting secrets and enabling privilege…

Proof-of-concept for Git LFS pointer poisoning, with Bash and Python scripts that create a malicious repository, simulate a rogue LFS server, and…

DJ-Classifieds Joomla Component Unauthenticated File Upload RCE. 3-string filter bypass via PHP short tags. CVSS 10.0 | CWE-434 | com_djclassifieds <…

There is a path injection vulnerability in OpenPLC-v3, which arises from the program not performing any validity checks on the file path parameters…

Java library for fast, configurable HTML sanitization from untrusted sources. Uses policy-driven scanning to remove malicious JavaScript and CSS,…

Proof-of-Concept (POC) of a simple firewall in Python designed to mitigate the Spring4Shell (CVE-2022-22965) RCE attack by inspecting and blocking…

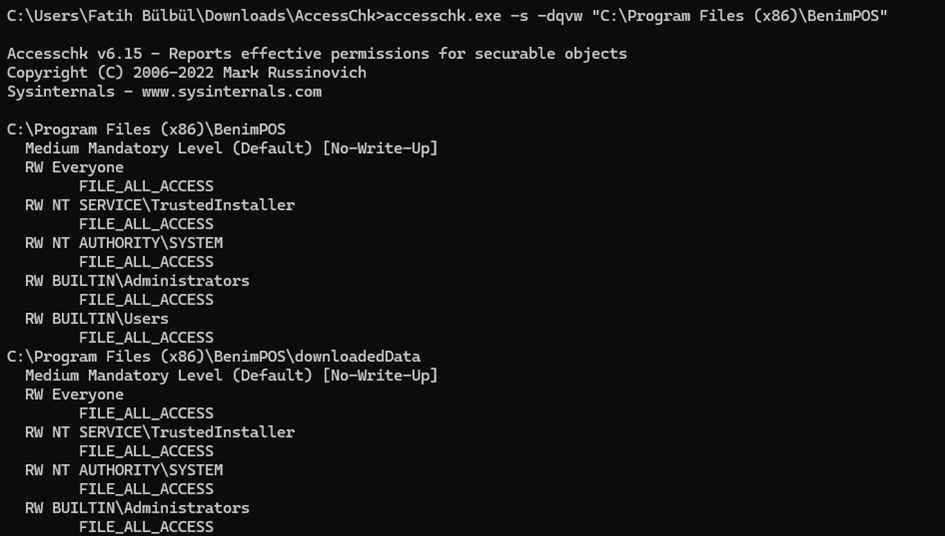
Proof-of-concept for CVE-2025-57392 demonstrating insecure default file permissions in BenimPOS Desktop V3.0, enabling privilege escalation via…

CVE-2024-10220 reveals a critical flaw in Kubernetes’ deprecated gitRepo volume type, allowing attackers to execute arbitrary commands via malicious…

A critical Remote Code Execution (RCE) vulnerability exists in Coolify's application deployment workflow. This flaw allows a low-privileged member to…

Fast, configurable HTML sanitization library for preventing XSS and malicious code injection from untrusted user input. Provides a policy-driven API…

CVE-2024-55963, allows unauthenticated remote code execution on Appsmith Enterprise platform due to a misconfigured PostgreSQL database included by…

Simple Dashboard <= 2.0 - Unauthenticated Privilege Escalation

teler-waf is a Go HTTP middleware that protects local web services from OWASP Top 10 threats, known vulnerabilities, malicious actors, botnets,…

MAL-011: Log4J Misconfiguration Allows Malicious JavaScript in Red Hat AMQ

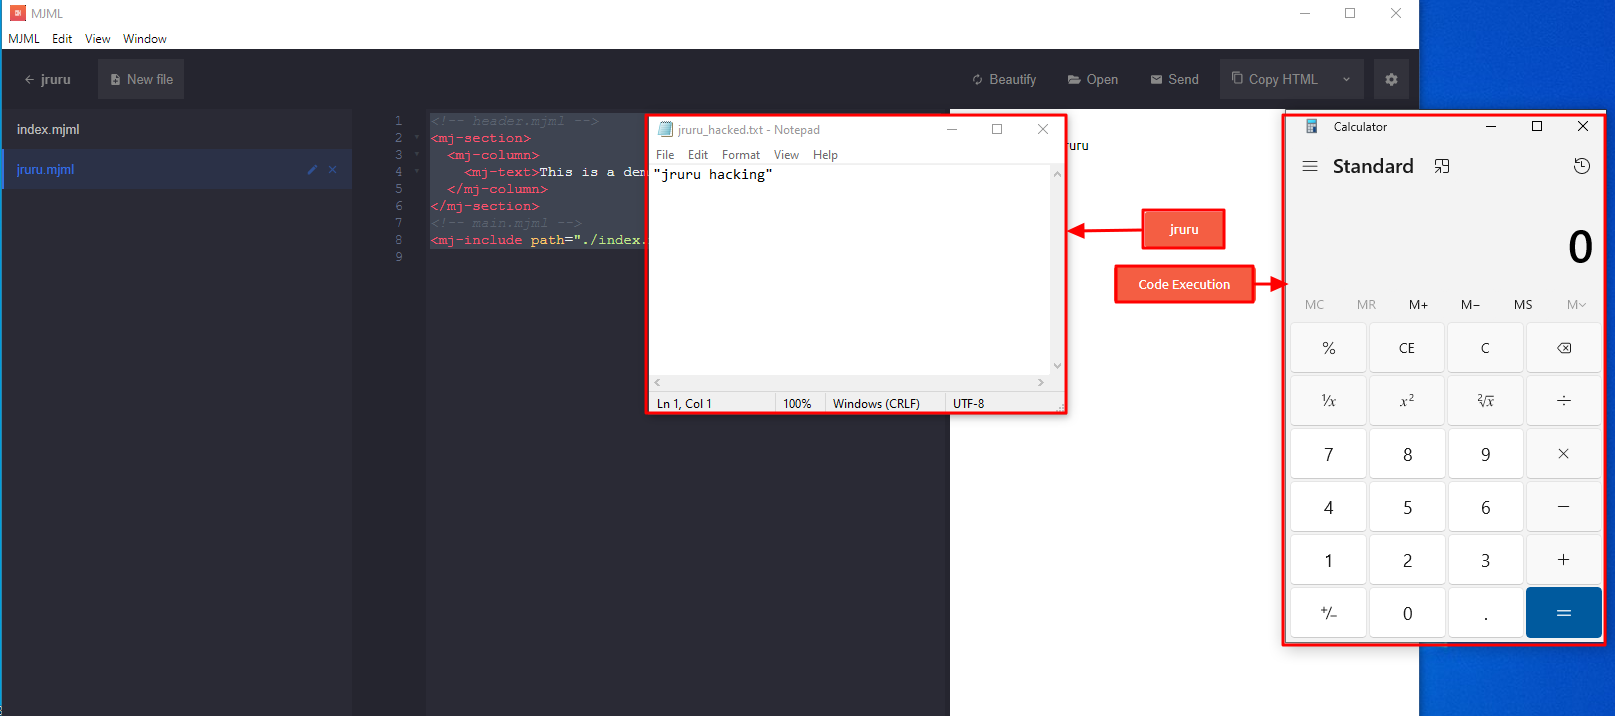
mjml-app v3.0.4 & 3.1.0-beta RCE exploit

K8S and Docker Vulnerability Check for CVE-2024-3094

Proof-of-concept for CVE-2023-37756: weak password requirements in i-doit Pro admin-center enabling brute-force login and malicious plugin upload…