
CSPBypass
 renniepak/cspbypass
CSPBypass.com, a tool designed to help ethical hackers bypass restrictive Content Security Policies (CSP) and exploit XSS (Cross-Site Scripting)…
configuration-auditingcurated-resourcesmisconfiguration+4
720
renniepak/cspbypassCSPBypass.com, a tool designed to help ethical hackers bypass restrictive Content Security Policies (CSP) and exploit XSS (Cross-Site Scripting)…
 firefart/stunner
Test and exploit STUN/TURN servers for misconfigurations, enabling internal network pivoting via SOCKS proxy, memory leak attacks, and internal port…
 stackrox/kube-linter
KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…
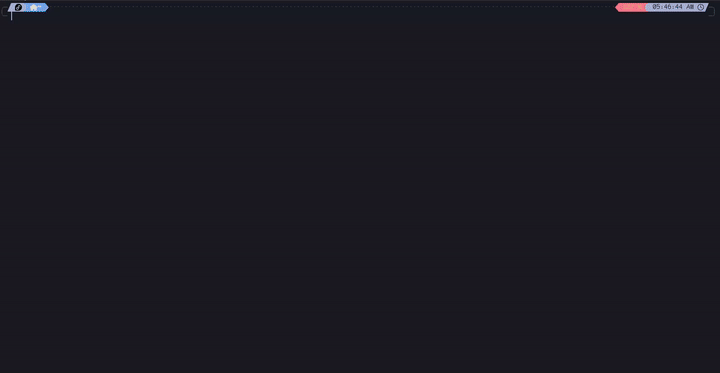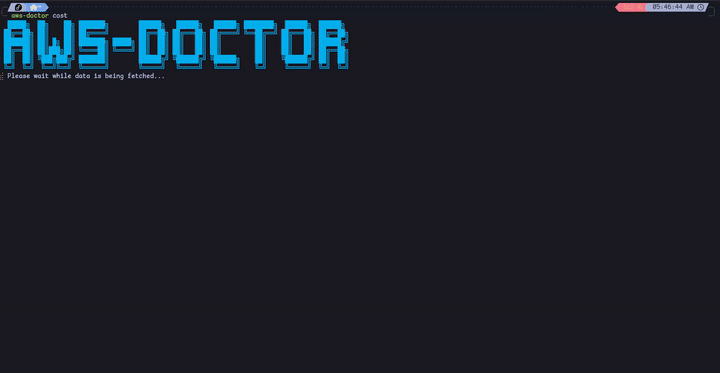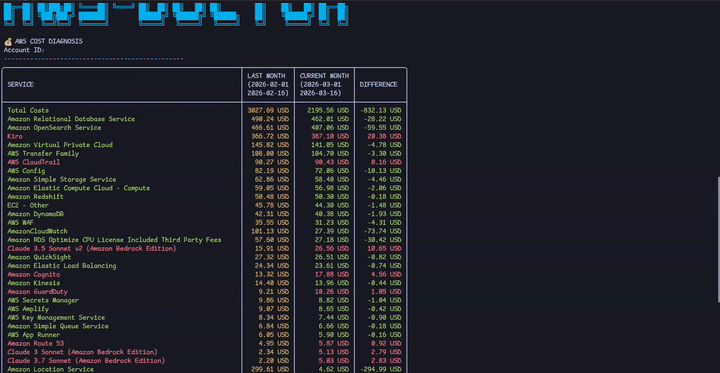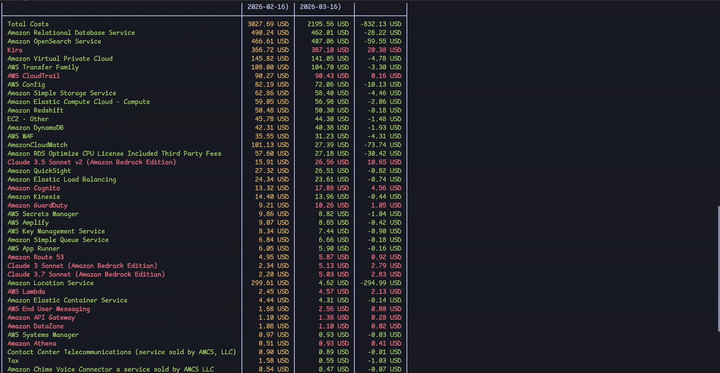 elc0mpa/aws-doctor
Powerful open-source CLI to audit security, costs, and best practices in AWS. 🩺 ☁️
 jakehildreth/locksmith
A small tool built to find and fix common misconfigurations in Active Directory Certificate Services.
 open-policy-agent/opa
Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…
 cisagov/scubagoggles
SCuBA Secure Configuration Baselines and assessment tool for Google Workspace
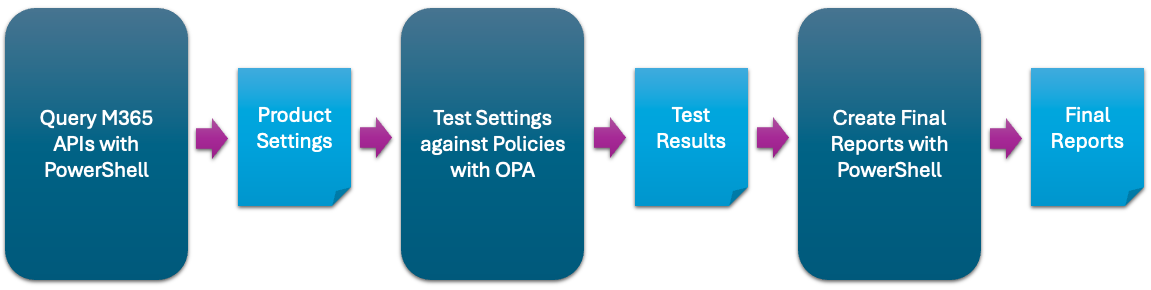 cisagov/scubagear
Automation to assess the state of your M365 tenant against CISA's baselines
 praetorian-inc/trajan
A multi-platform CI/CD vulnerability detection and attack automation tool for identifying security weaknesses in pipeline configurations.
 doyensec/electronegativity
Electronegativity is a tool to identify misconfigurations and security anti-patterns in Electron applications.
 cogiceo/gpohound
Offensive GPO dumping and analysis tool that leverages and enriches BloodHound data
 ekitji/siem
Curated SIEM queries and techniques for offensive discovery of Windows privilege escalation, misconfigured ACLs, services, scheduled tasks, and…
 megamansec/gixy-next
Gixy-Next: NGINX Configuration Security Scanner & Performance Checker
 aquasecurity/kube-bench
Checks whether Kubernetes is deployed according to security best practices as defined in the CIS Kubernetes Benchmark
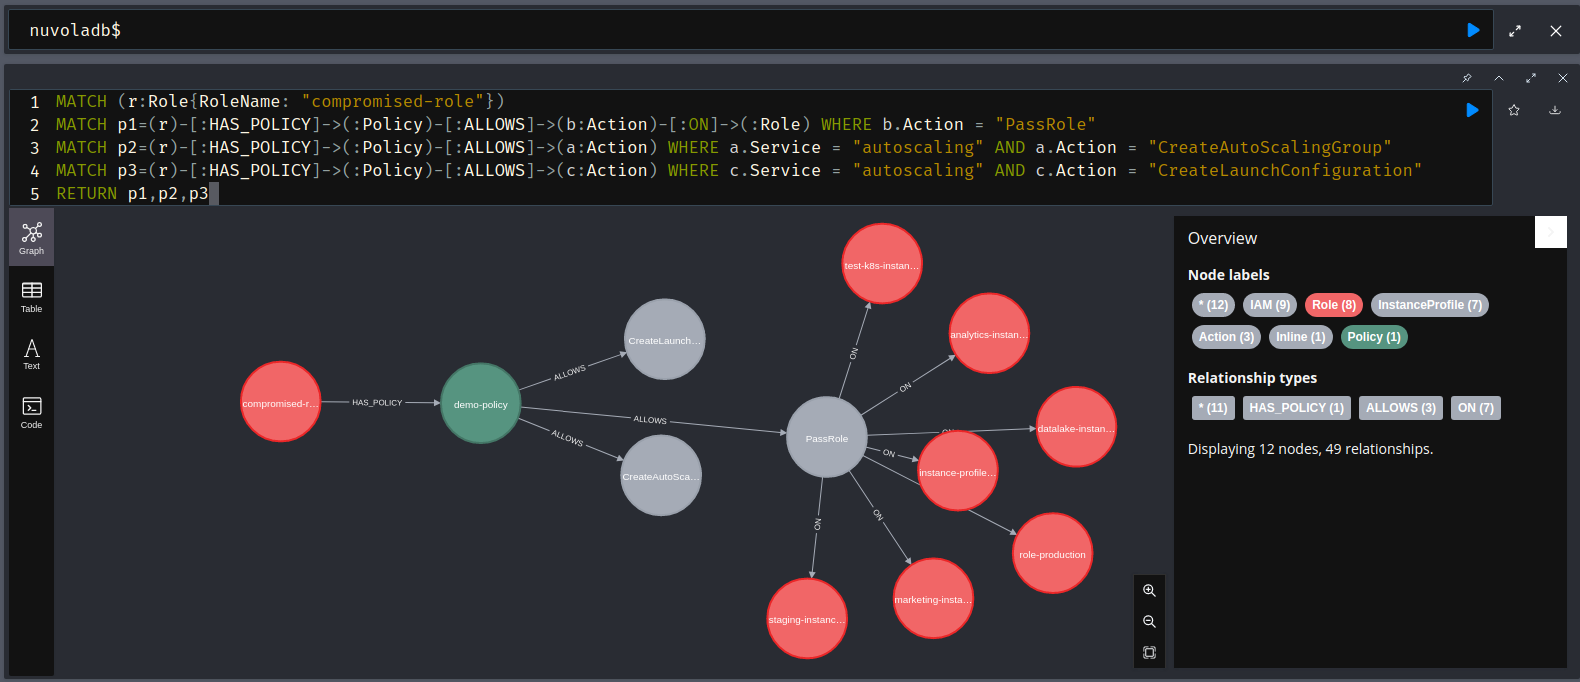 primait/nuvola
Graph-based AWS security analysis tool that dumps cloud configurations, detects misconfigurations, and maps attack paths using a Neo4j digital twin…
 bombobombone/cve-2026-73318
Proof-of-concept exploit for XenForo CVE-2026-73318, an authorization bypass allowing ACP administrators to trigger site-wide policy re-agreement.…
 bombobombone/cve-2026-73317
Proof-of-concept exploit and technical write-up for CVE-2026-73317, an authorization bypass in XenForo allowing limited admins to approve content as…
 synacktiv/sccmsecrets
SCCMSecrets.py aims at exploiting SCCM policies distribution for credentials harvesting, initial access and lateral movement.