
CVE-2020-24029
 redteambrasil/cve-2020-24029
Detailed disclosure of an unauthenticated password change vulnerability in ForLogic Qualiex v1 and v3, enabling remote privilege escalation and…
authenticationexploitationinformation-gathering+4
redteambrasil/cve-2020-24029Detailed disclosure of an unauthenticated password change vulnerability in ForLogic Qualiex v1 and v3, enabling remote privilege escalation and…
 prapul1/vulnhub-dc1-writeup
VulnHub DC-1 boot-to-root — exploiting CVE-2018-7600 (Drupalgeddon2) for RCE, extracting DB credentials from settings.php, forging admin password…
 jenderal92/wp-def
Wordpress Default Password
 saykino/cve-2026-31283
Documentation of CVE-2026-31283: an email bombing vulnerability in Totara LMS's forgot password API due to missing rate limiting, allowing…
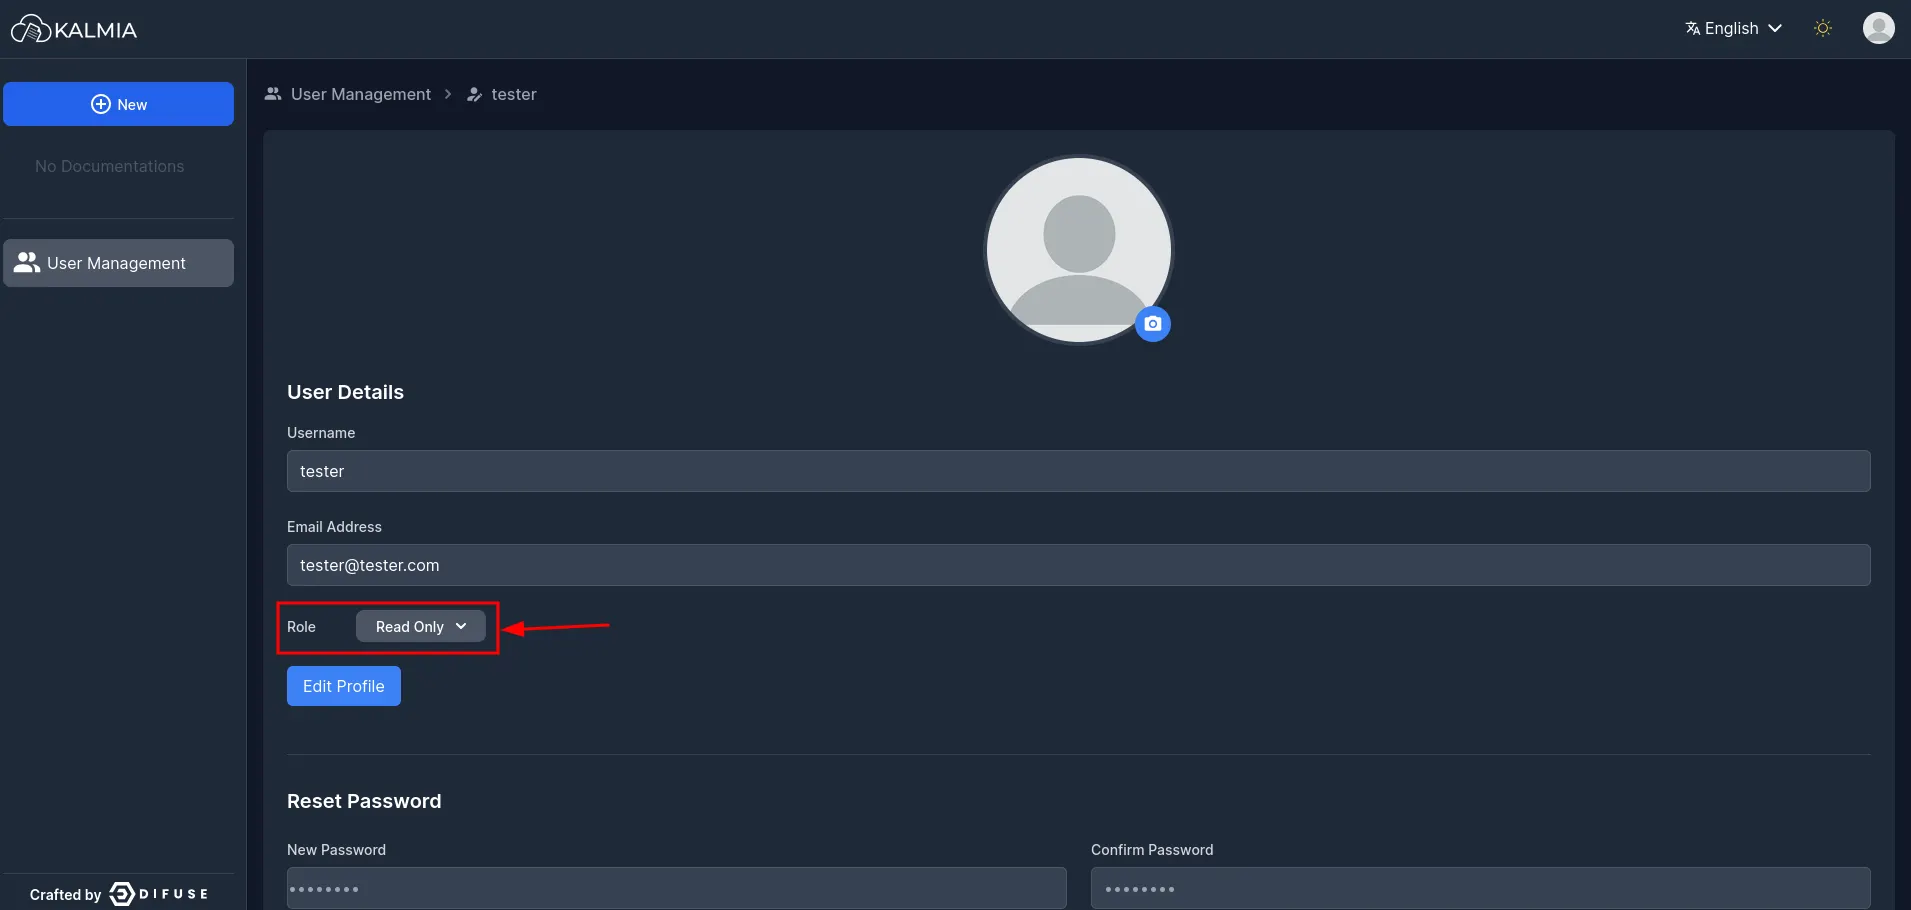 noxurge/cve-2025-65900
DifuseHQ Kalmia CMS version 0.2.0 contains an Incorrect Access Control vulnerability in the /kal-api/auth/users API endpoint. Due to insufficient…
 saykino/cve-2025-54321
Documentation of CVE-2025-54321: an email bombing vulnerability in Ascertia SigningHub's reset password function due to missing rate limiting,…
 rodolfomarianocy/xpl-modernwms-cve-2024-57698
It is possible to view the MD5 hash of the admin password and other attributes without authentication, even after initial setup and password change.…
 gh-ost00/cve-2024-28987-poc
Web Help Desk Hardcoded Credential Vulnerability (CVE-2024-28987)
 anmolksachan/cve-2020-2733
Exploit for CVE-2020-2733 in JD Edwards EnterpriseOne Tools, demonstrating unauthenticated admin password decryption and authentication bypass to…
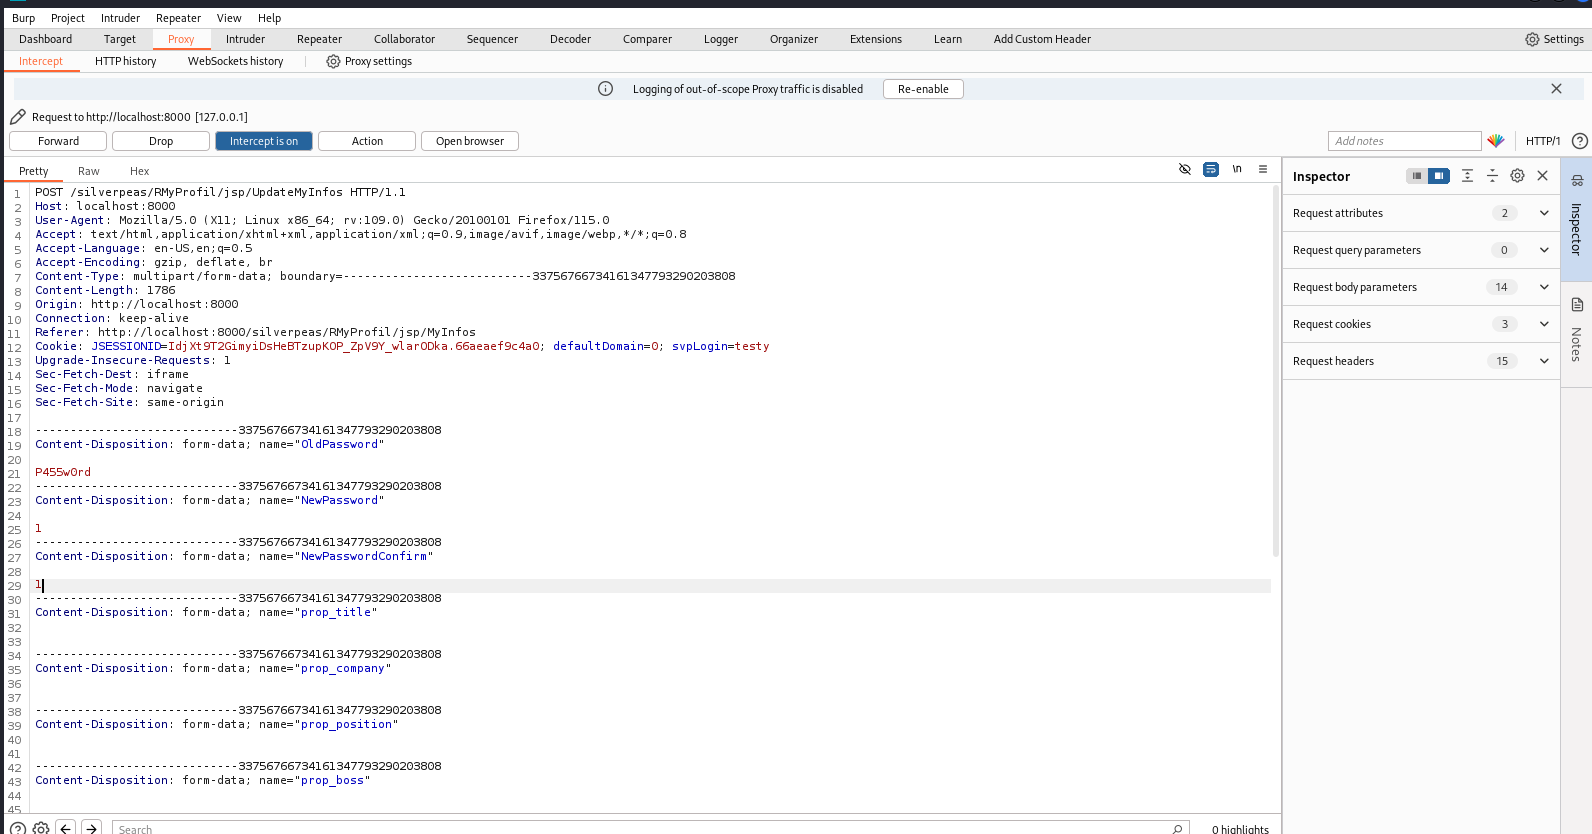 njmbb8/cve-2024-42850
An issue in Silverpeas v6.4.2 and lower allows for the bypassing of password complexity requirements.
 vt0x78/cve-2024-31989
Exploit for CVE-2024-31989.
 redfox-security/digisol-dg--gr1321-s-password-storage-in-plaintext--cve-2024-4232
Proof-of-concept exploit for CVE-2024-4232 targeting plaintext password storage in Digisol DG-GR1321 routers. Demonstrates extraction of credentials…
 redfox-security/digisol-dg-gr1321-s-password-storage-in-plaintext-cve-2024-4232
Proof-of-concept demonstrating plaintext password storage vulnerability in Digisol DG-GR1321 routers, enabling credential exposure and unauthorized…
 funoverip/mcafee-sitelist-pwd-decryption
Password decryption tool for the McAfee SiteList.xml file
 soy-oreocato/cve-2022-42176
Proof-of-concept for CVE-2022-42176: hard-coded credentials in PCSecure configuration file allow local privilege escalation to admin panel and…
 sajaljat/cve-2023-46449
Proof-of-concept exploit for CVE-2023-46449: IDOR in Sourcecodester inventory management system v1.0 password change function enabling remote account…
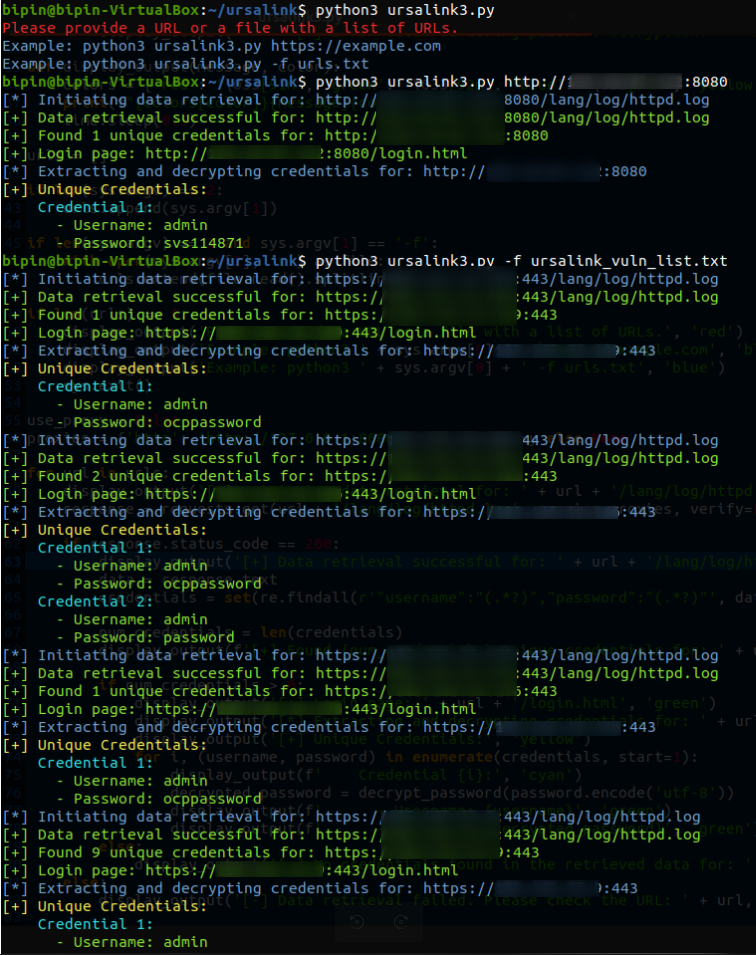 win3zz/cve-2023-43261
CVE-2023-43261 - Credential Leakage Through Unprotected System Logs and Weak Password Encryption
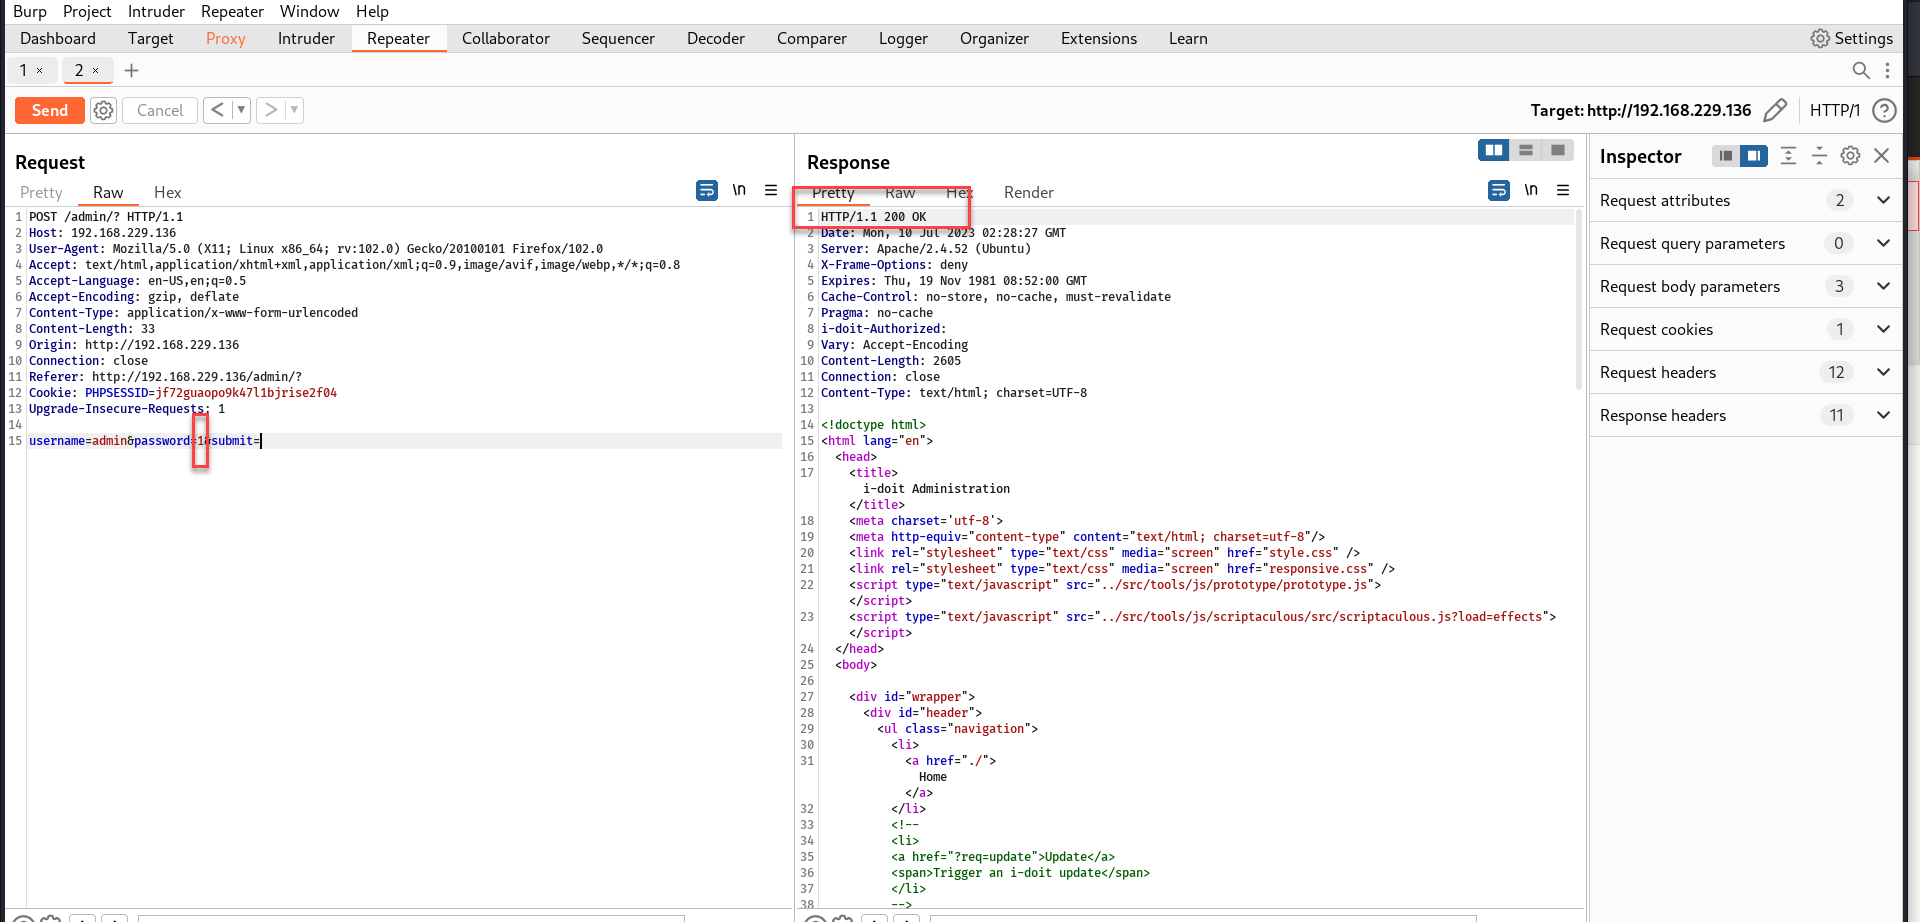 leekenghwa/cve-2023-37756-cwe-521-lead-to-malicious-plugin-upload-in-the-i-doit-pro-25-and-below
Proof-of-concept for CVE-2023-37756: weak password requirements in i-doit Pro admin-center enabling brute-force login and malicious plugin upload…