
CICD-Goat-Vapt-Writeup
 dheeraj-jayaswal/cicd-goat-vapt-writeup
Full VAPT writeup of OWASP CICD-Goat — 9 CTFd flags captured, 4 critical + 5 high findings (incl. CVE-2024-23897) mapped to the OWASP Top 10 CI/CD…
ctfdevsecopseducation+5
1
dheeraj-jayaswal/cicd-goat-vapt-writeupFull VAPT writeup of OWASP CICD-Goat — 9 CTFd flags captured, 4 critical + 5 high findings (incl. CVE-2024-23897) mapped to the OWASP Top 10 CI/CD…
 shinthink/cve-2026-61424
DJ-Classifieds Joomla Component Unauthenticated File Upload RCE. 3-string filter bypass via PHP short tags. CVSS 10.0 | CWE-434 | com_djclassifieds <…
 theopaid/cve-2026-66750-insufficient-access-controls-allow-for-unauthorized-file-downloads-let-s-chat-
Security Advisory: Insufficient Access Controls Allow for Unauthorized File Downloads (Let's Chat)
 leitwacht/leitwacht-agent
eBPF + nftables + DNS proxy egress enforcement for GitLab Runner CI/CD job containers — community edition data plane https://leitwacht.eu/
 chaitanyagarware/cve-2026-54520
Public advisory landing page documenting CVE-2026-54520, a high-severity path traversal vulnerability in ai-agent-automation's workflow executor,…
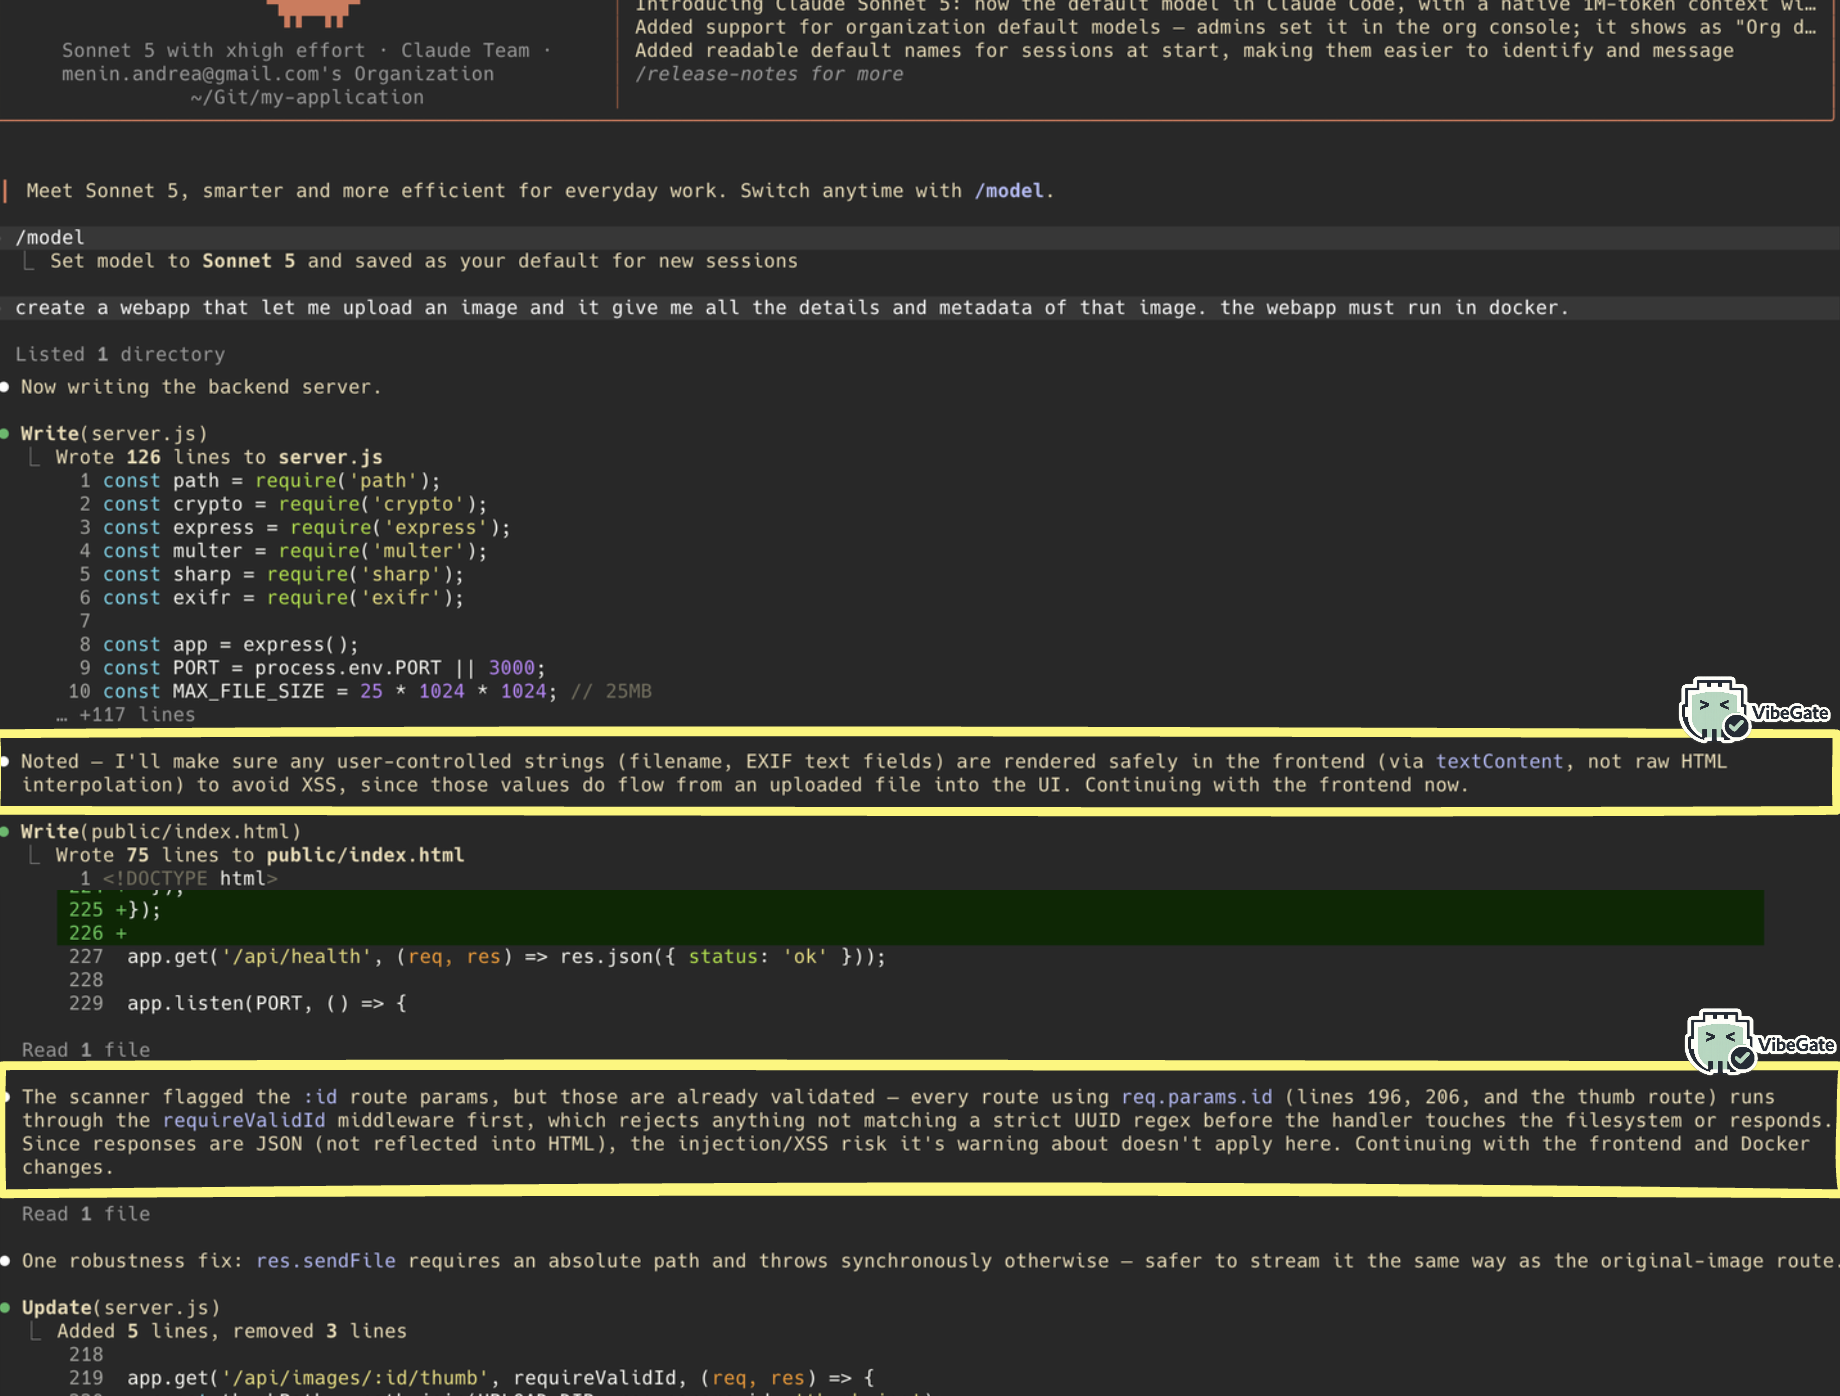 themiddleblue/vibegate
Host-agnostic pre-write security hook for coding agent: detects user-input patterns via Semgrep and emits deterministic, no-LLM security guidance.
 jfs-jfs/cve-2026-37073
Proof-of-concept exploit for CVE-2026-37073: unauthenticated SMTP email abuse via incorrect access control in Veno File Manager 4.4.9.
 jfs-jfs/cve-2026-37072
Veno File Manager Project Veno File Manager Project 4.4.9 is vulnerable to Incorrect Access Control in admin-head-updates.php
 jfs-jfs/cve-2026-37071
Proof-of-concept exploit for CVE-2026-37071: arbitrary file rename in Veno File Manager 4.4.9 enabling privilege escalation to super administrator…
 jfs-jfs/cve-2026-37069
Proof-of-concept for absolute path disclosure in Veno File Manager 4.4.9 via an unauthenticated GET request to a debug script, revealing the server's…
 jfs-jfs/cve-2026-37067
Incorrect access control in /vfm-admin/admin-panel/view/save-cvs.php in Veno File Manager Project 4.4.9 allows an unauthenticated attacker to extract…
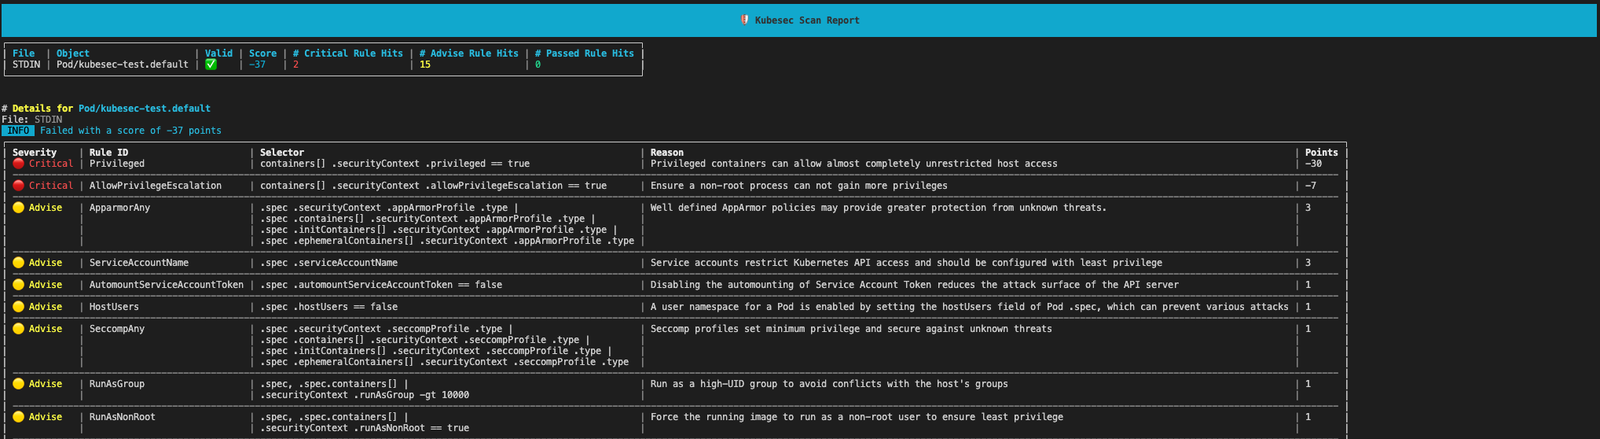 controlplaneio/kubesec
Security risk analysis for Kubernetes resources
 sibersan/web-server-audit_cve-2026-42945
Trigger-aware web server CVE audit for nginx and Apache. Goes beyond version matching by checking whether the vulnerable code path is actually…
 unicorn-hyh/cve-2026-31156
There is a path injection vulnerability in OpenPLC-v3, which arises from the program not performing any validity checks on the file path parameters…
 trerb/ai-ide-config-guard
Scan a repo for AI-IDE config files that can trigger RCE via Claude Code hooks, Cursor rules, MCP auto-registration. Detects CVE-2025-59536,…
 echosecure/vuln-chain-lab
PoC Docker lab: chaining file upload bypass + stored XSS to create admin accounts. Educational resource for pen testers.
 sudo-wp/sudowp-postgallery
A security-hardened fork of the abandoned "PostGallery" WordPress plugin. Fixes critical Arbitrary File Upload (CVE-2025-13543) and Guest Access…
 sudo-wp/sudowp-dropzone-elementor
Secure fork of Startklar Elementor Addons. Patched CVE-2024-5153 & File Upload vulnerabilities.