

milvus-auth-audit
 qianlijaingshan/milvus-auth-audit
Milvus 认证安全检测脚本:CVE-2025-64513 (sourceid后门) / CVE-2026-26190 (/expr弱token) / 内部端口53100
api-security-testingauthentication-authorizationdatabase-security+4
qianlijaingshan/milvus-auth-auditMilvus 认证安全检测脚本:CVE-2025-64513 (sourceid后门) / CVE-2026-26190 (/expr弱token) / 内部端口53100
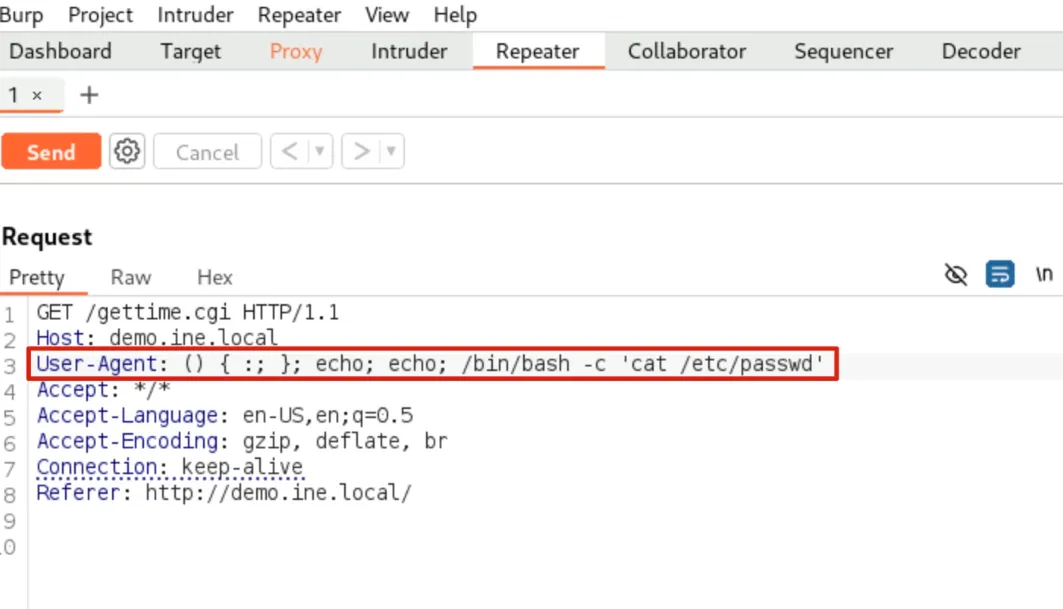 mtaha-sec/bash-apocalypse
Recreating Shellshock (CVE-2014-6271) - the bash vulnerability that endangered millions of servers. Automated exploitation toolkit + Burp Suite…
 bountyyfi/azure-apim-cross-tenant-signup-bypass
Security advisory: Azure APIM Developer Portal allows cross-tenant account registration by bypassing UI signup restrictions. Reported to MSRC twice -…
 michaeladamgroberman/cve-2025-10681
CVE-2025-10681: Hardcoded Azure Blob Storage Account Key — Gardyn Home Kit (ICSA-26-055-03)
 heroku/heroku-cve-2013-0269
Inspect all of your Heroku apps for vulnerable versions of the JSON gem
 heroku/heroku-cve-2013-0333
Scans Heroku applications for a critical Rails remote code execution vulnerability (CVE-2013-0333) and identifies unpatched instances requiring…
 dannyendortest/java-vulnerable
EXPOSURE demo target: Tomcat (CVE-2016-0714) + Apache Rave (CVE-2013-1814) + Java filter-padding deps
 amnnrth/cve-2025-34291_cors_security_scanner
A lightweight Python-based security assessment tool for detecting dangerous Cross-Origin Resource Sharing (CORS) misconfigurations - CVE-2025-34291.
 jasetpen/cve-2025-69428
A critical access control vulnerability in locally deployed Pro-Bit application in versions less than v1.77.4 allows unauthenticated attackers to…
 zsxen/cve-2025-1974
Windows 11-first educational lab for studying CVE-2025-1974 in ingress-nginx. Provides safe attack emulation and defense validation with local…
 kso4more/cve-2025-0108
Reproduces CVE-2025-0108 path confusion vulnerability in Nginx/Apache stacks. Includes a vulnerable PoC and a patched implementation demonstrating…
 sudo-wp/sudowp-postgallery
A security-hardened fork of the abandoned "PostGallery" WordPress plugin. Fixes critical Arbitrary File Upload (CVE-2025-13543) and Guest Access…
 helleflo1312/orchestrated-powershell-for-cve-2023-24932
Automated PowerShell orchestrator for applying Secure Boot mitigations against CVE-2023-24932 (BlackLotus). Handles registry changes, reboots,…
 gregk4sec/cve-2025-31651
Original CVE-2025-31651 disclosure with proof-of-concept exploit for Apache Tomcat rewrite rule bypass. Includes technical analysis, reproduction…
 enochgitgamefied/nextjs-cve-2025-29927-docker-lab
Docker-based lab for exploring and reproducing the Next.js CVE-2025-29927 middleware authorization bypass vulnerability. Includes vulnerable app,…
 tagoletta/cve-2025-69459
Proof-of-concept exploit for CVE-2025-69459, demonstrating broken access control in Movie Rating System 1.0 that allows unauthenticated admin account…
 eyodav/cve-2025-34171
CasaOS expose multiple unauthenticated API endpoints that allow remote disclosure of sensitive configuration files and system debug information