
agent-bom
 msaad00/agent-bom
Open security scanner and self-hosted control plane for AI, MCP, and cloud. One evidence model — run scans in your environment, centralize findings,…
ai-securitycloud-securitycontainer-security+6
31
msaad00/agent-bomOpen security scanner and self-hosted control plane for AI, MCP, and cloud. One evidence model — run scans in your environment, centralize findings,…
 snyk/cli
Snyk CLI scans and monitors your projects for security vulnerabilities.
 complianceascode/content
Generates SCAP, Ansible, Bash, and CEL security content for compliance evaluation and automated hardening across Linux hosts, containers, and…
 prowler-cloud/prowler
Prowler is the world’s most widely used open-source cloud security platform that automates security and compliance across any cloud environment.…
 kyverno/kyverno
Enforce security and compliance on Kubernetes clusters via admission controls, resource mutation, background scans, and container image signature…
 checkmarx/kics
Static analysis scanner for infrastructure-as-code that detects security vulnerabilities, compliance violations, and misconfigurations across…
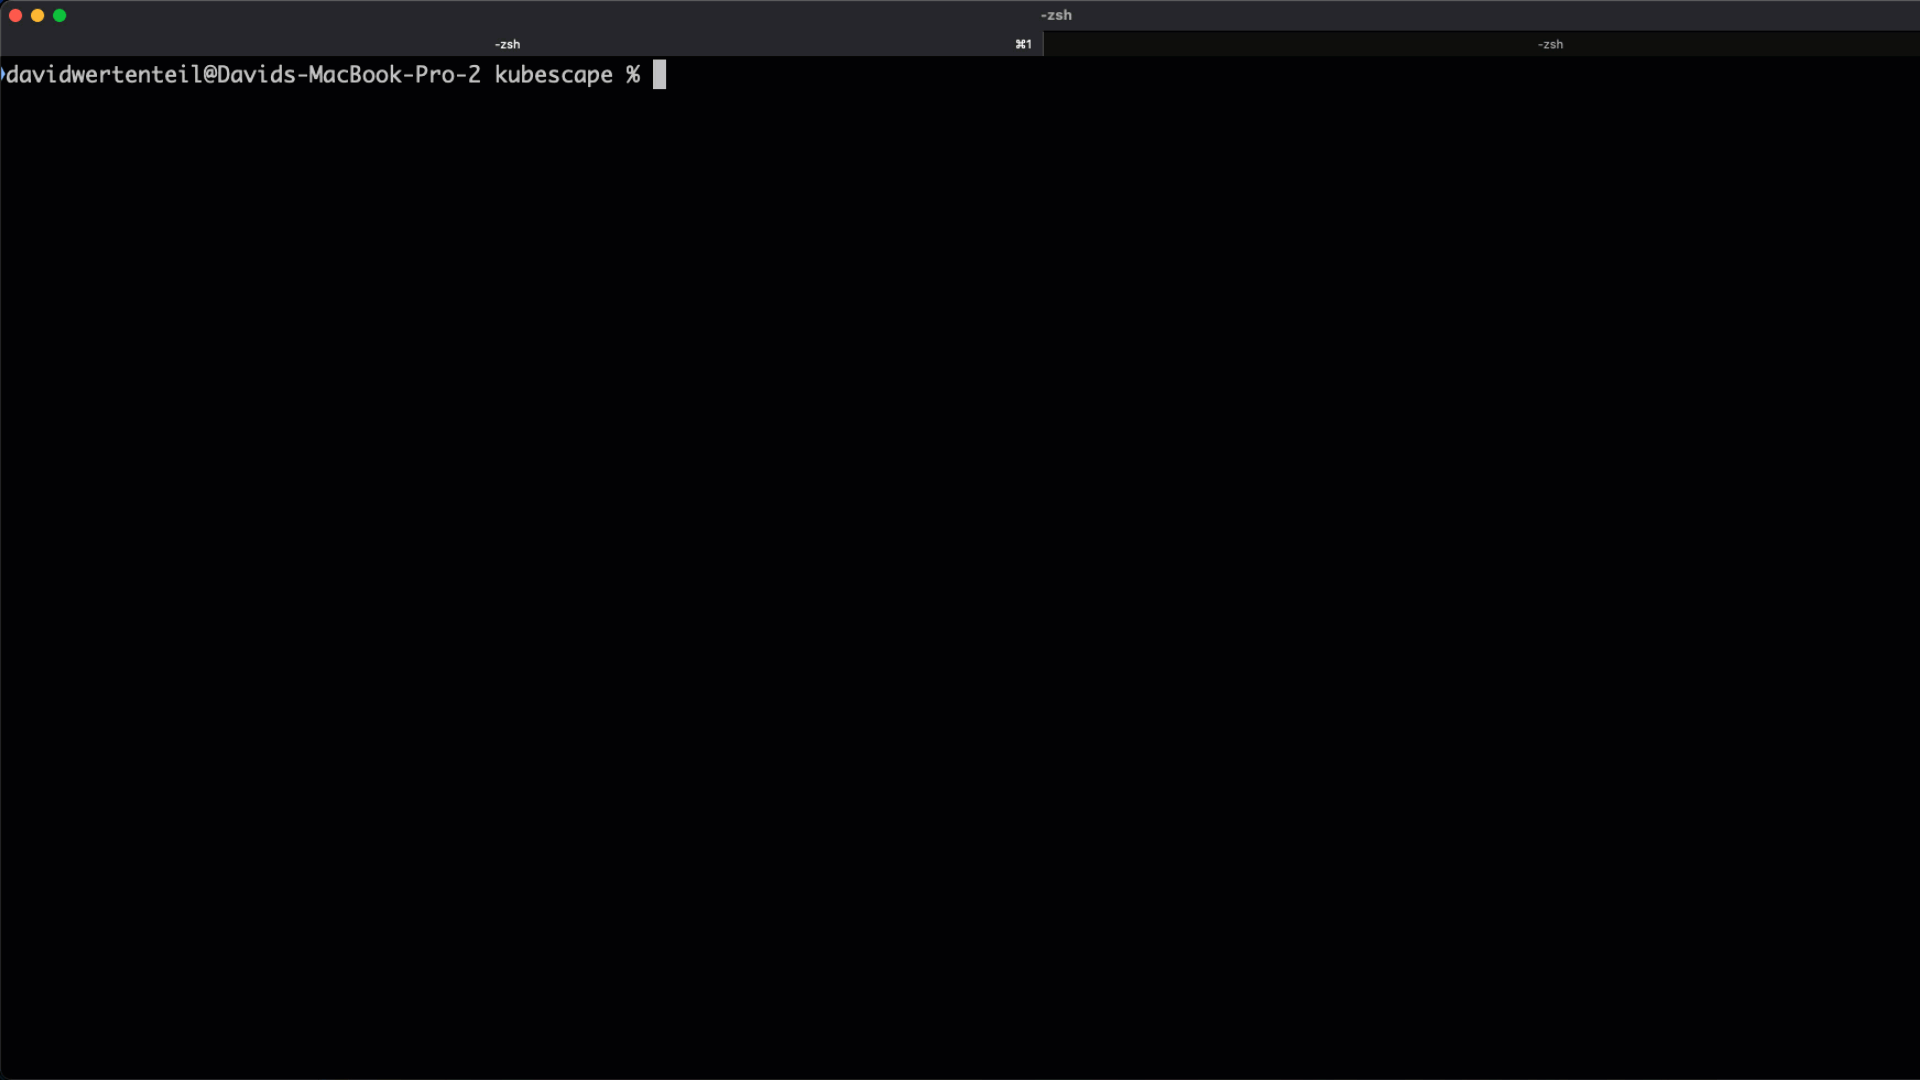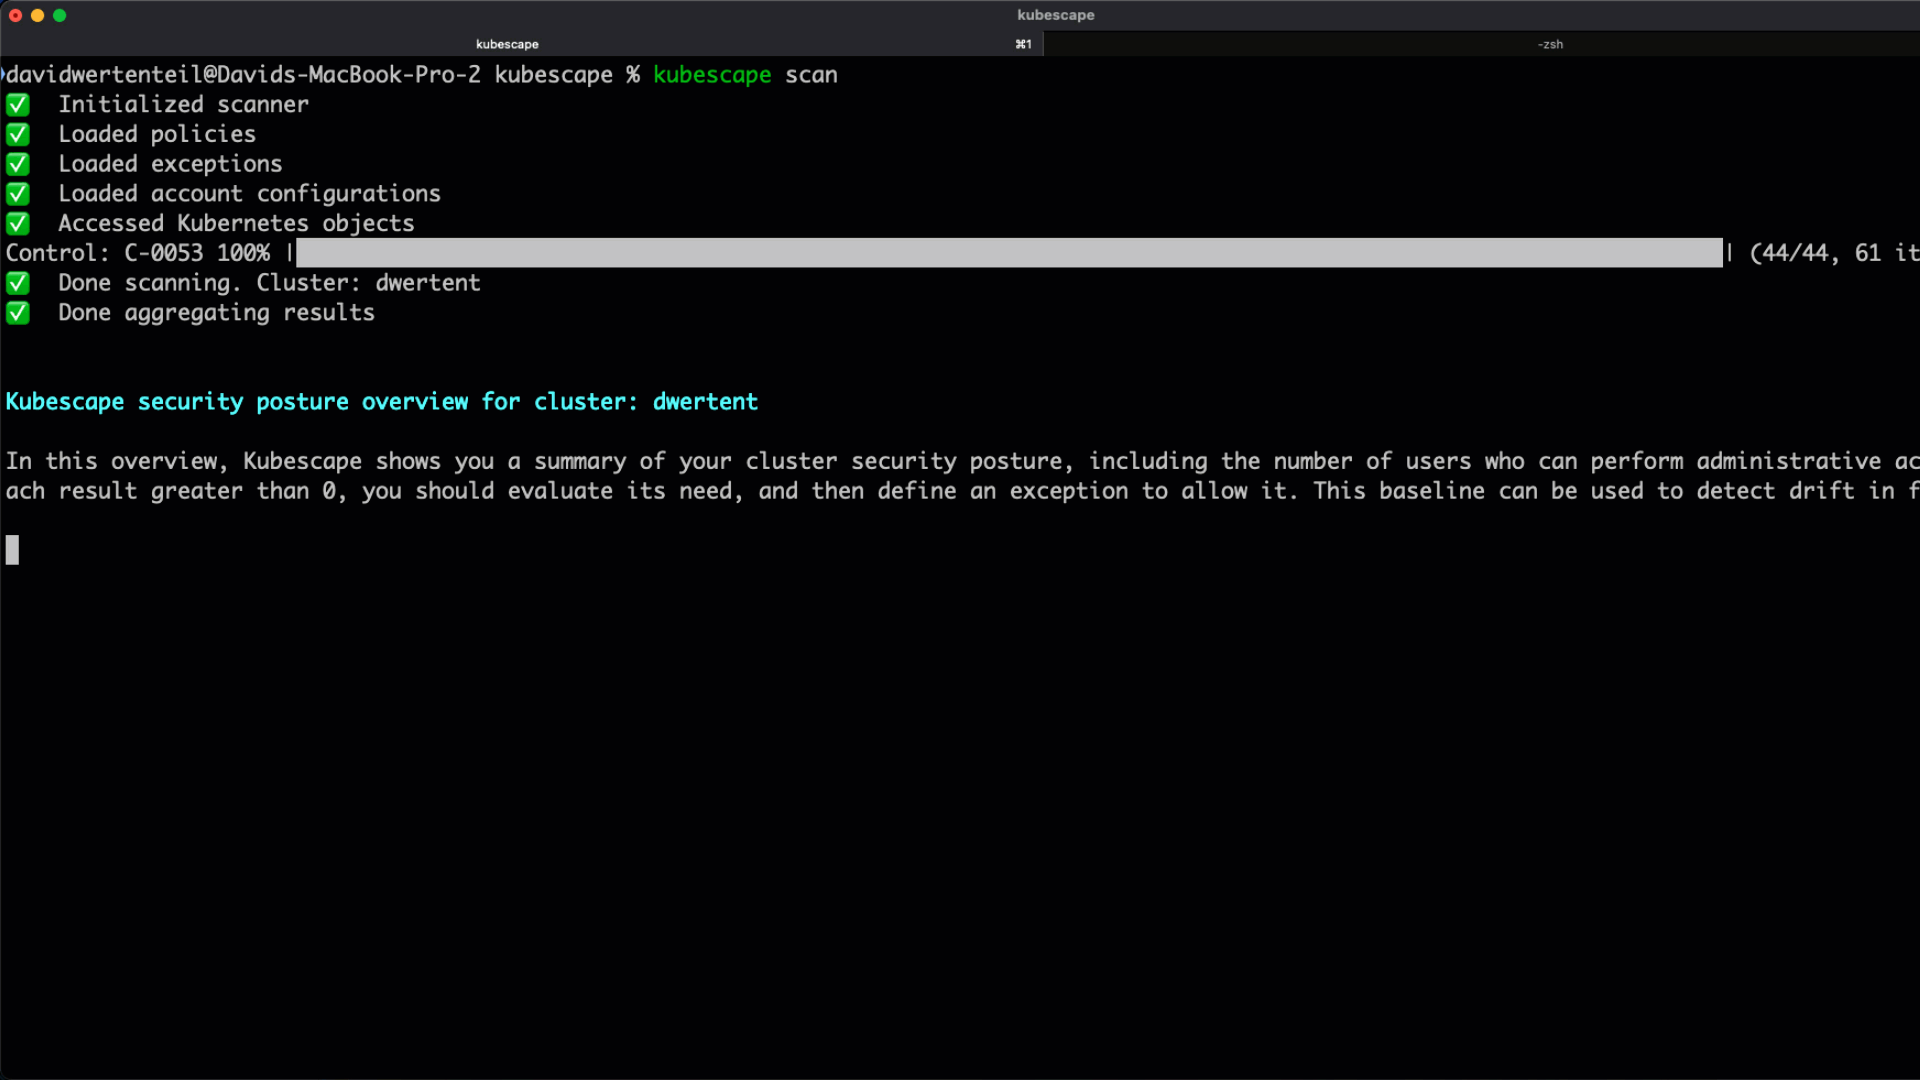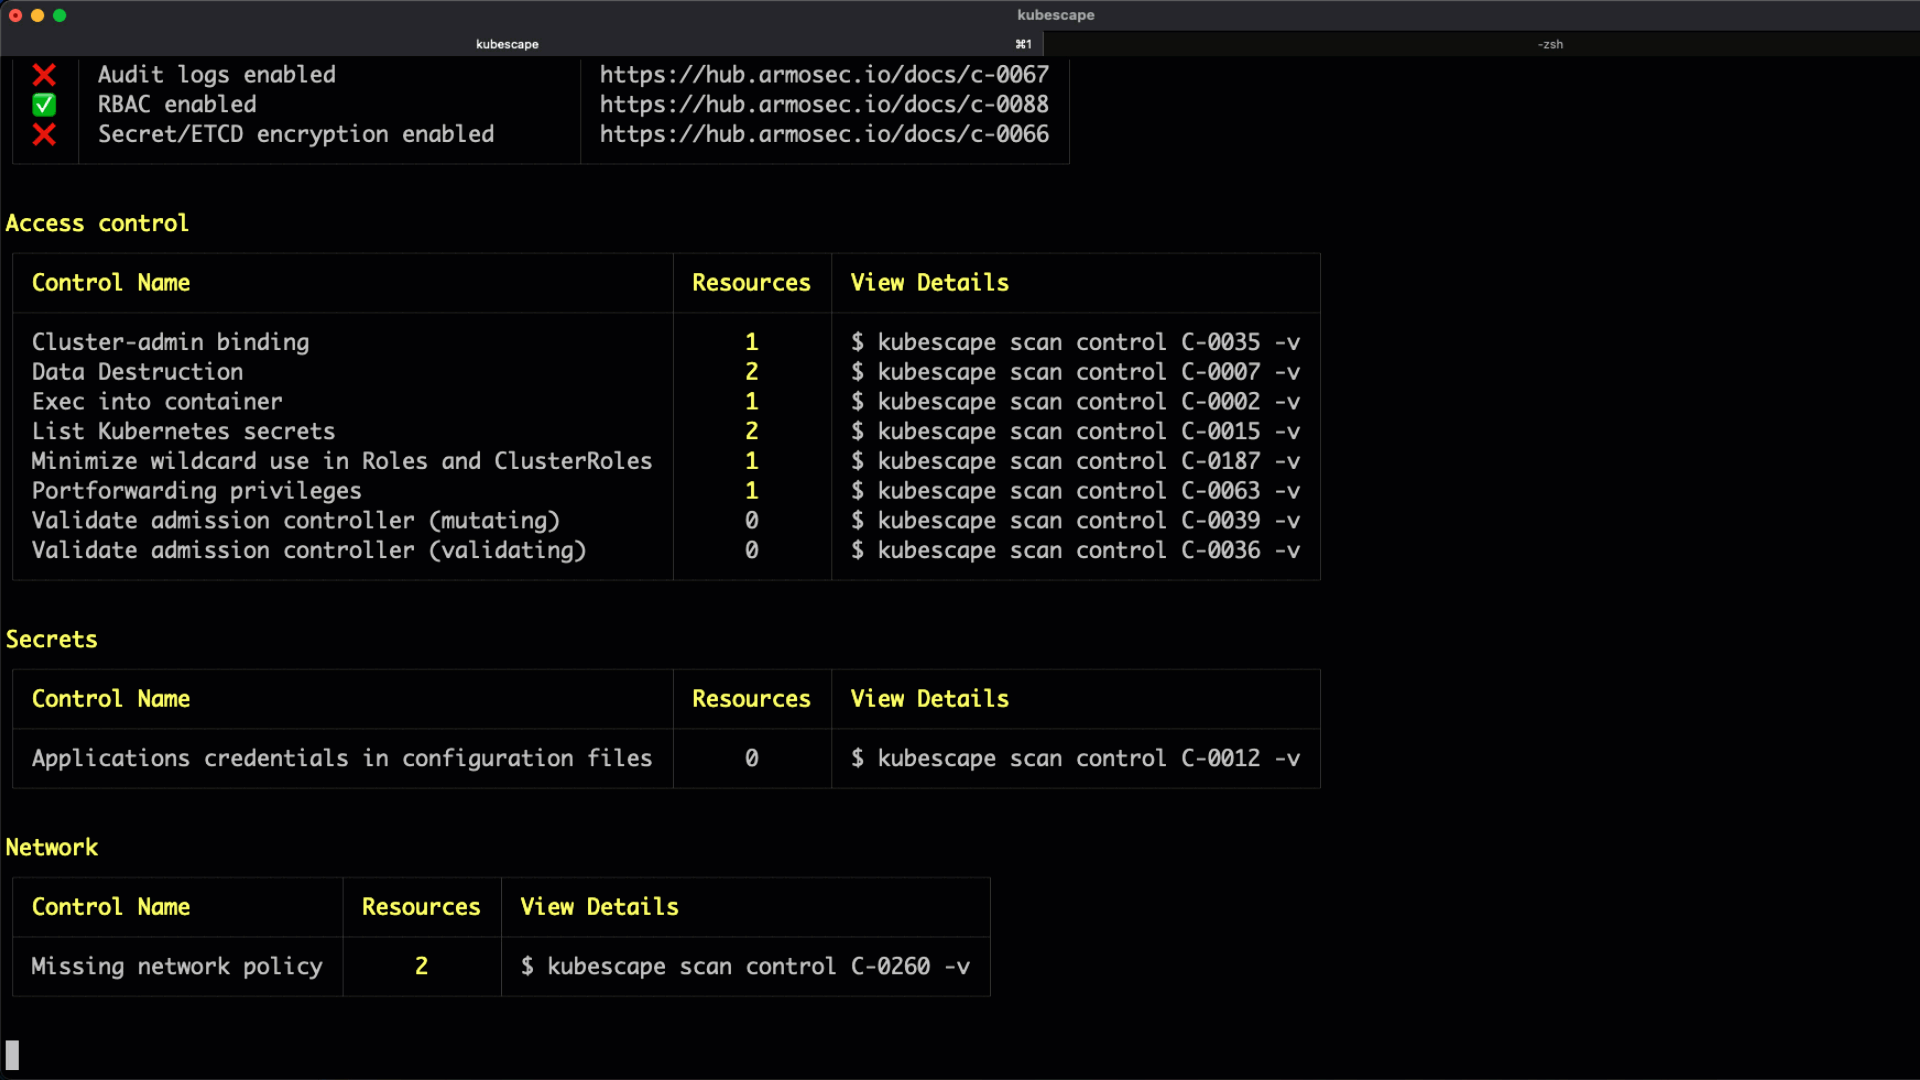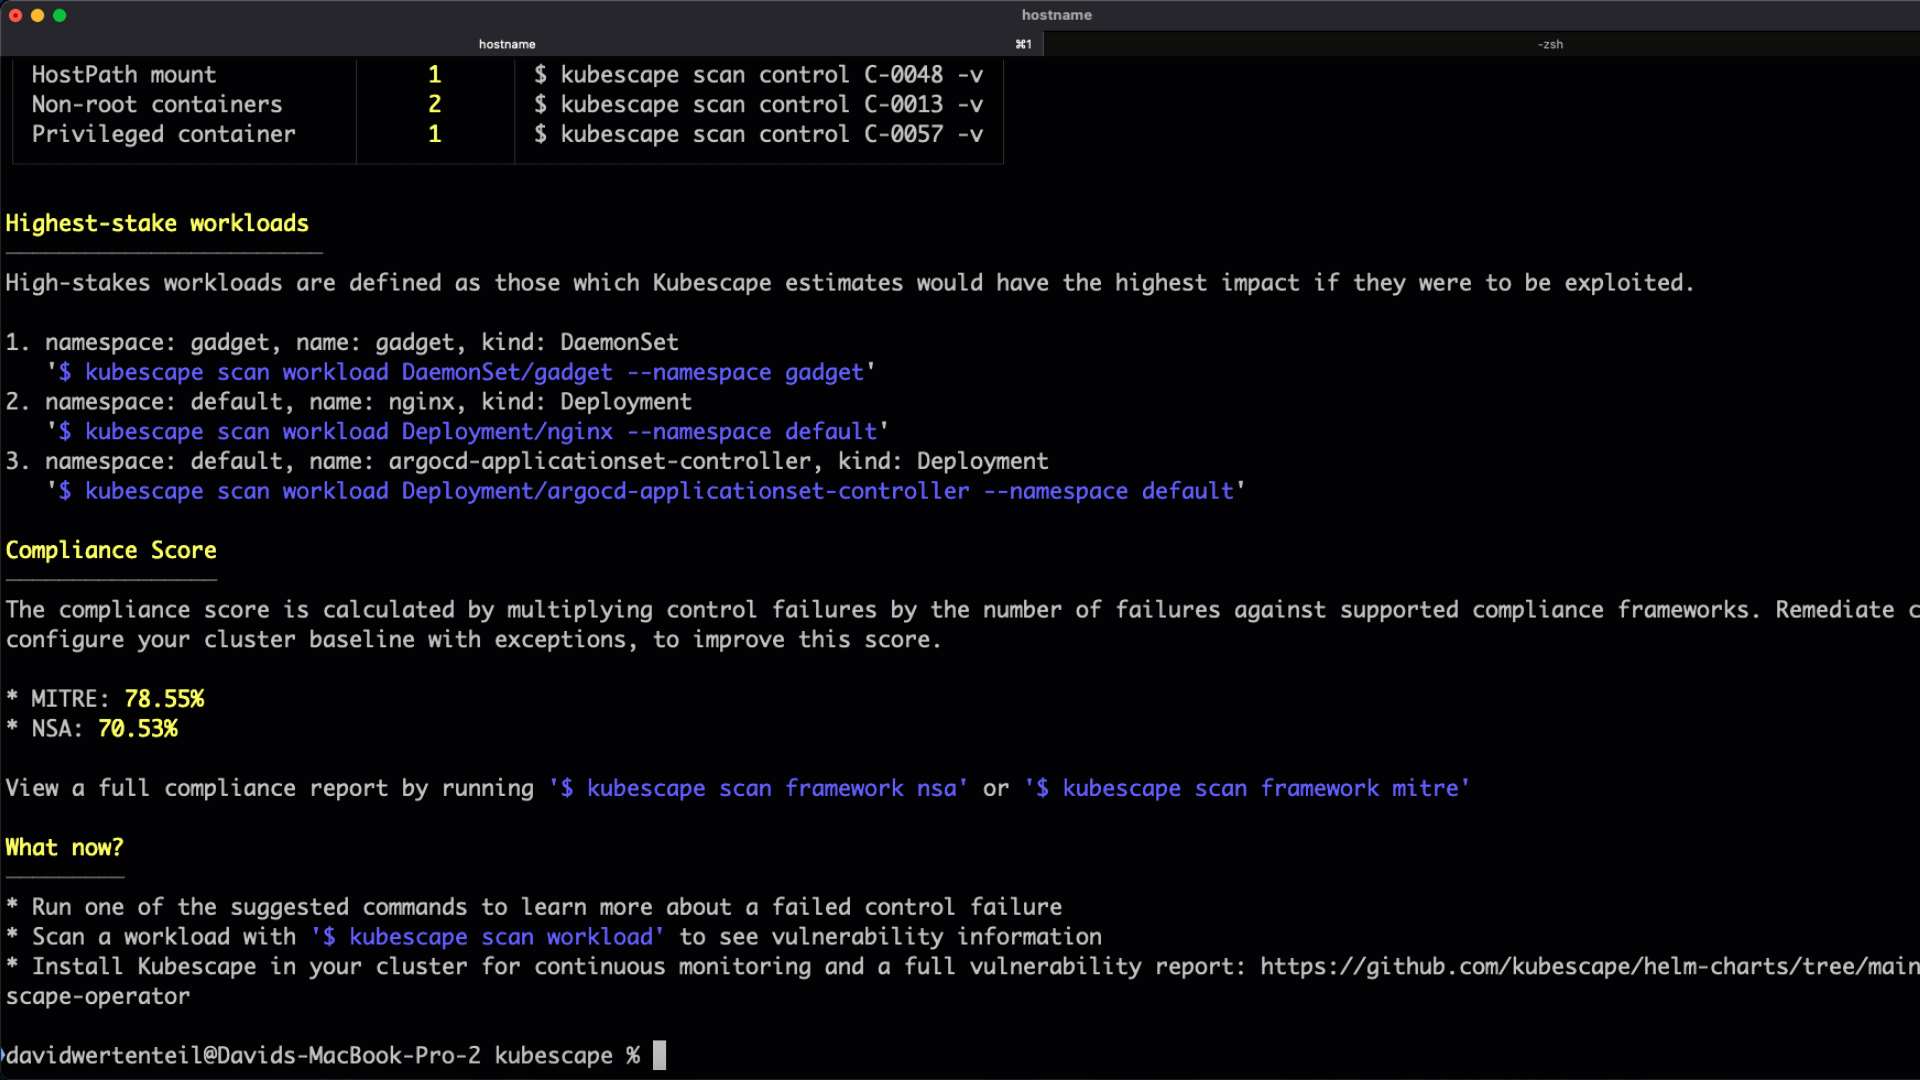 kubescape/kubescape
Open-source Kubernetes security platform scanning clusters, manifests, and images for misconfigurations, vulnerabilities, and compliance against NSA,…
 skyscanner/cfripper
Library and CLI tool for analysing CloudFormation templates and check them for security compliance.
 cynative/cynative
Read-only AI agent that queries your cloud, code, and runtime infrastructure to surface misconfigurations, leaked secrets, and privilege escalation…
 corazawaf/coraza
Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
 open-policy-agent/gatekeeper
Kubernetes policy engine with OPA-based admission control, mutation, and audit for enforcing security and compliance configurations.
 jvoisin/snuffleupagus
Security module for php7 and php8 - Killing bugclasses and virtual-patching the rest!
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
 facebook/mcpguard-dynamic
Kernel-level eBPF sandbox for securing LLM agent tool calls made through the Model Context Protocol (MCP)
 neffisback/wsuks
Automating the MITM attack on WSUS
 coreruleset/coreruleset
Generic attack detection rule set for web application firewalls, protecting against OWASP Top Ten and common vulnerabilities with minimal false…
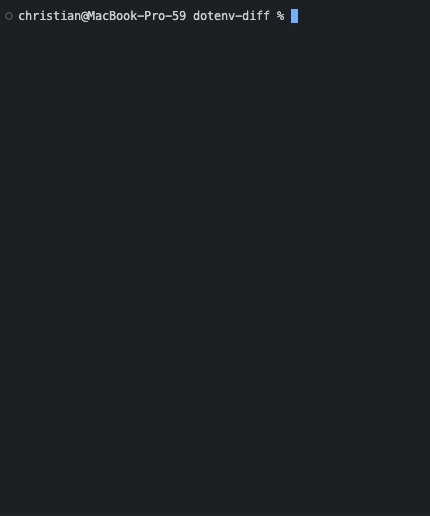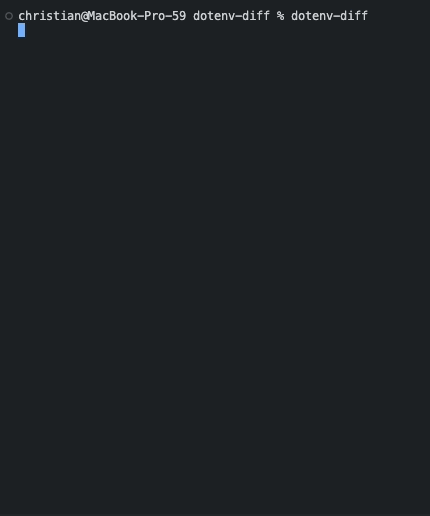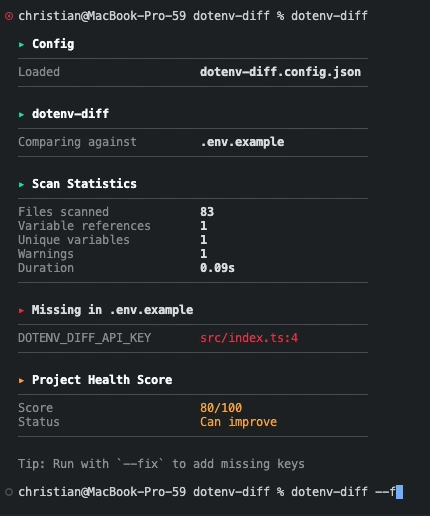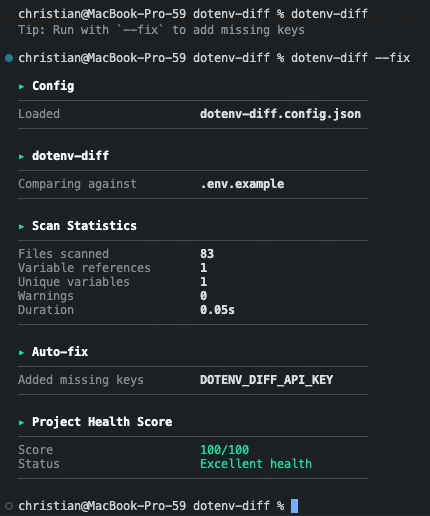 chrilleweb/dotenv-diff
Validate environment variable usage in codebase
 bridgecrewio/checkov
Static analysis tool for infrastructure as code that detects cloud misconfigurations, vulnerabilities, and secrets across Terraform, Kubernetes,…