

IDWolf
 g4bri-3l3/idwolf
Read-only Active Directory & Microsoft Entra ID hygiene auditor in pure PowerShell. Collect once, analyze offline: deterministic findings, attack…
cloud-securityconfiguration-auditingdefensive-tools+6
g4bri-3l3/idwolfRead-only Active Directory & Microsoft Entra ID hygiene auditor in pure PowerShell. Collect once, analyze offline: deterministic findings, attack…
 bombobombone/cve-2026-73317
Proof-of-concept exploit and technical write-up for CVE-2026-73317, an authorization bypass in XenForo allowing limited admins to approve content as…
 johenlastgen-jlg/cve-2026-11961
CVE-2026-11961 — UserRegistration: WordPress User Registration <= 5.2.2 Privilege Escalation. Misconfigured Membership Roles → Unauthenticated Admin…
 zephrfish/ludus-defender-lab
MDE/MDI Defender setup for Ludus
 d0n601/cve-2025-12135
WPBookit <= 1.0.6 - Unauthenticated Stored Cross-Site Scripting
 jenderal92/wp-def
Wordpress Default Password
 learner202649/cve-2026-47101-poc
The code for personally reproducing the corresponding vulnerability
 shoucheng3/nahsra__antisamy_cve-2016-10006_1-5-3
Fast, configurable HTML sanitization library for preventing XSS and malicious code injection from untrusted user input. Provides a policy-driven API…
 rz1027/cve-2026-20896
Public PoC and detector for CVE-2026-20896 ("Gitea Docker: One Header, Any User")
 xiaoxiaoranxxx/cve-2025-56815
Datart 1.0.0-rc.3 is vulnerable to Directory Traversal in the POST /viz/image interface, since the server directly uses MultipartFile.transferTo() to…
 saykino/cve-2025-54320
Proof-of-concept for CVE-2025-54320: an email bombing vulnerability in Ascertia SigningHub's Invite User API due to missing rate limiting, allowing…
 saykino/cve-2025-54321
Documentation of CVE-2025-54321: an email bombing vulnerability in Ascertia SigningHub's reset password function due to missing rate limiting,…
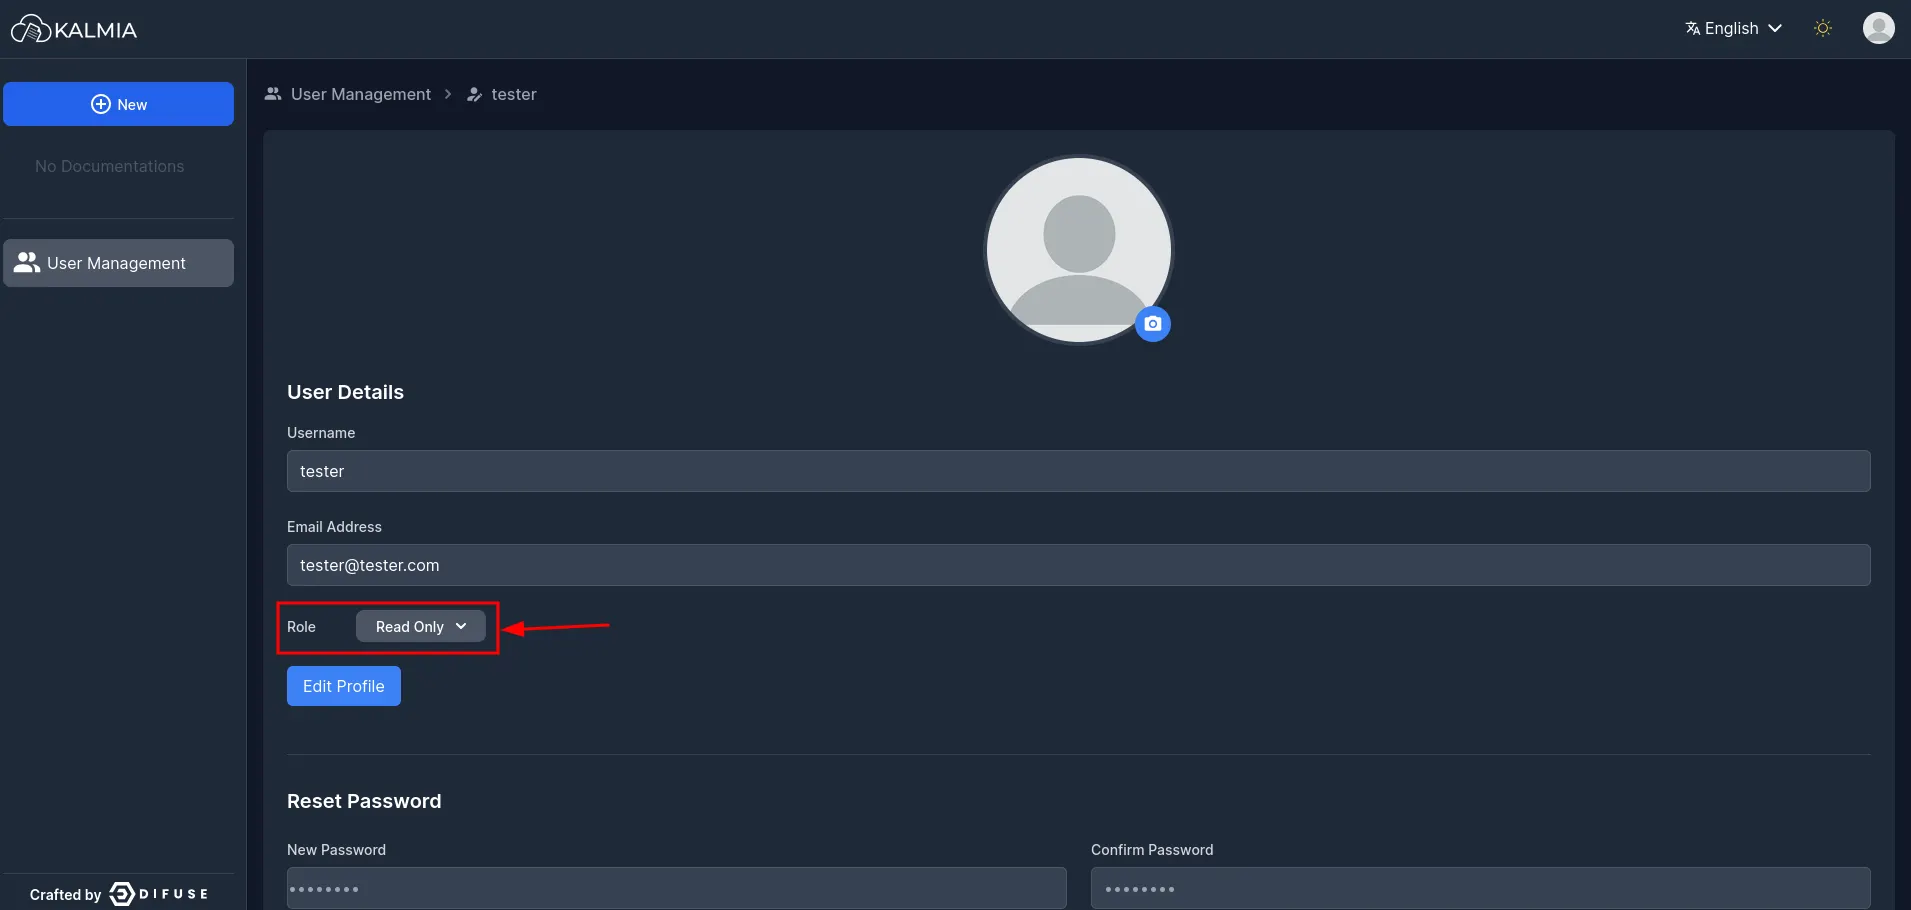 noxurge/cve-2025-65900
DifuseHQ Kalmia CMS version 0.2.0 contains an Incorrect Access Control vulnerability in the /kal-api/auth/users API endpoint. Due to insufficient…
 tansique-17/cve-2025-26199
Public Disclosure
 csuribird/cve-2025-2304
This Python script exploits a critical mass assignment vulnerability in Camaleon CMS version 2.9.0, allowing any registered user to escalate their…
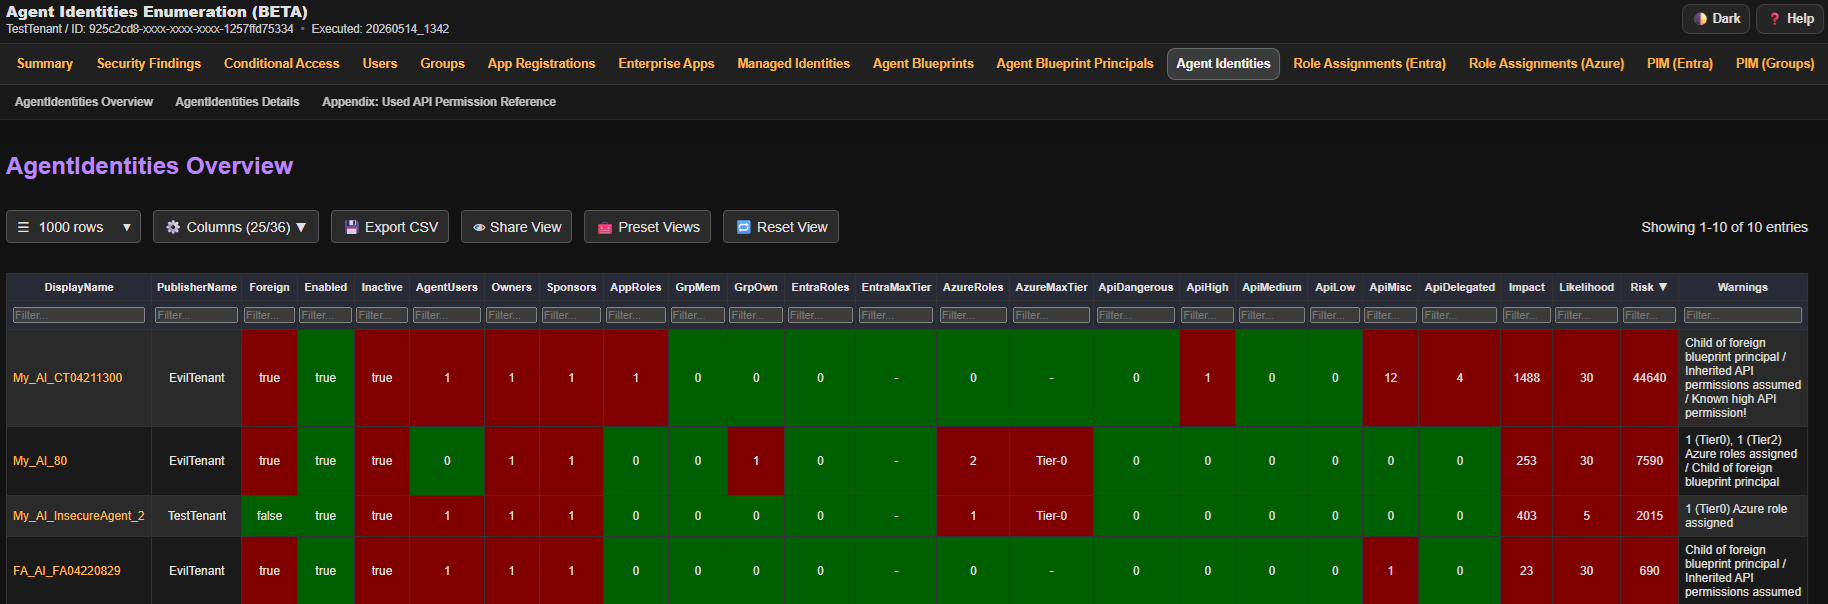 compasssecurity/entrafalcon
A lightweight PowerShell tool for assessing the security posture of Microsoft Entra ID environments. It helps identify privileged objects, risky…
 randomrobbiebf/cve-2024-12172
WP Courses LMS – Online Courses Builder, eLearning Courses, Courses Solution, Education Courses <= 3.2.21 - Missing Authorization to Authenticated…
 maikroservice/cve-2022-45265
Proof-of-concept exploit for CVE-2022-45265 targeting Sourcecodester Sanitization Management System 1.0 via unauthenticated user modification through…