
chef-mysql-hardening
 dev-sec/chef-mysql-hardening
This chef cookbook provides security configuration for mysql.
configuration-auditingdatabase-securitydefensive-tools+3
27
dev-sec/chef-mysql-hardeningThis chef cookbook provides security configuration for mysql.
 yijikeji/cve-2022-29170
Grafana is an open-source platform for monitoring and observability. In Grafana Enterprise, the Request security feature allows list allows to…
 mthamil107/db_audit_research
Self-Defeating Audits: reproducible lab showing a low-privilege PostgreSQL role reversibly blinding a trigger-based auditor + poisoning attribution…
 eh-amish/windows-defender-security-auditor-cve-2026-50656-
Read-only PowerShell security auditor for Windows endpoints and servers: checks Defender configuration, patch status, credentials, persistence,…
 neelkotnis/azure-security-auditor
CLI tool to audit Azure security posture, RBAC, NSGs, storage, identity, and encryption
 proviesec/google-dorks
Useful Google Dorks for WebSecurity and Bug Bounty
 george0papasotiriou/cve-2026-11115-database-connection-string-injection-via-env-variable
 neffisback/wsuks
Automating the MITM attack on WSUS
 xuwu-xuwu/cve-2026-68004
Standalone PoC for unauthenticated RTMP publish in SRS media servers; verifies the vulnerability, supports HTTP API side-channel check, and enables…
 rootsecdev/microburstsecretshunter
Scans exported Azure domain dumps for plaintext passwords, connection strings, storage keys, and other secrets; generates redacted CSV/HTML reports…
 george0papasotiriou/cve-2026-21018-opc-ua-authentication-bypass-via-none-security-policy
Proof-of-concept exploit for OPC UA authentication bypass using None security policy, including a simulated server to demonstrate unauthorized…
 qianlijaingshan/milvus-auth-audit
Milvus 认证安全检测脚本:CVE-2025-64513 (sourceid后门) / CVE-2026-26190 (/expr弱token) / 内部端口53100
 george0papasotiriou/cve-2026-22007-ntp-monlist-amplification-over-ipv6
Python PoC for CVE-2026-22007: NTP monlist amplification over IPv6, including a simulated vulnerable server and spoofed UDP reflection attack.
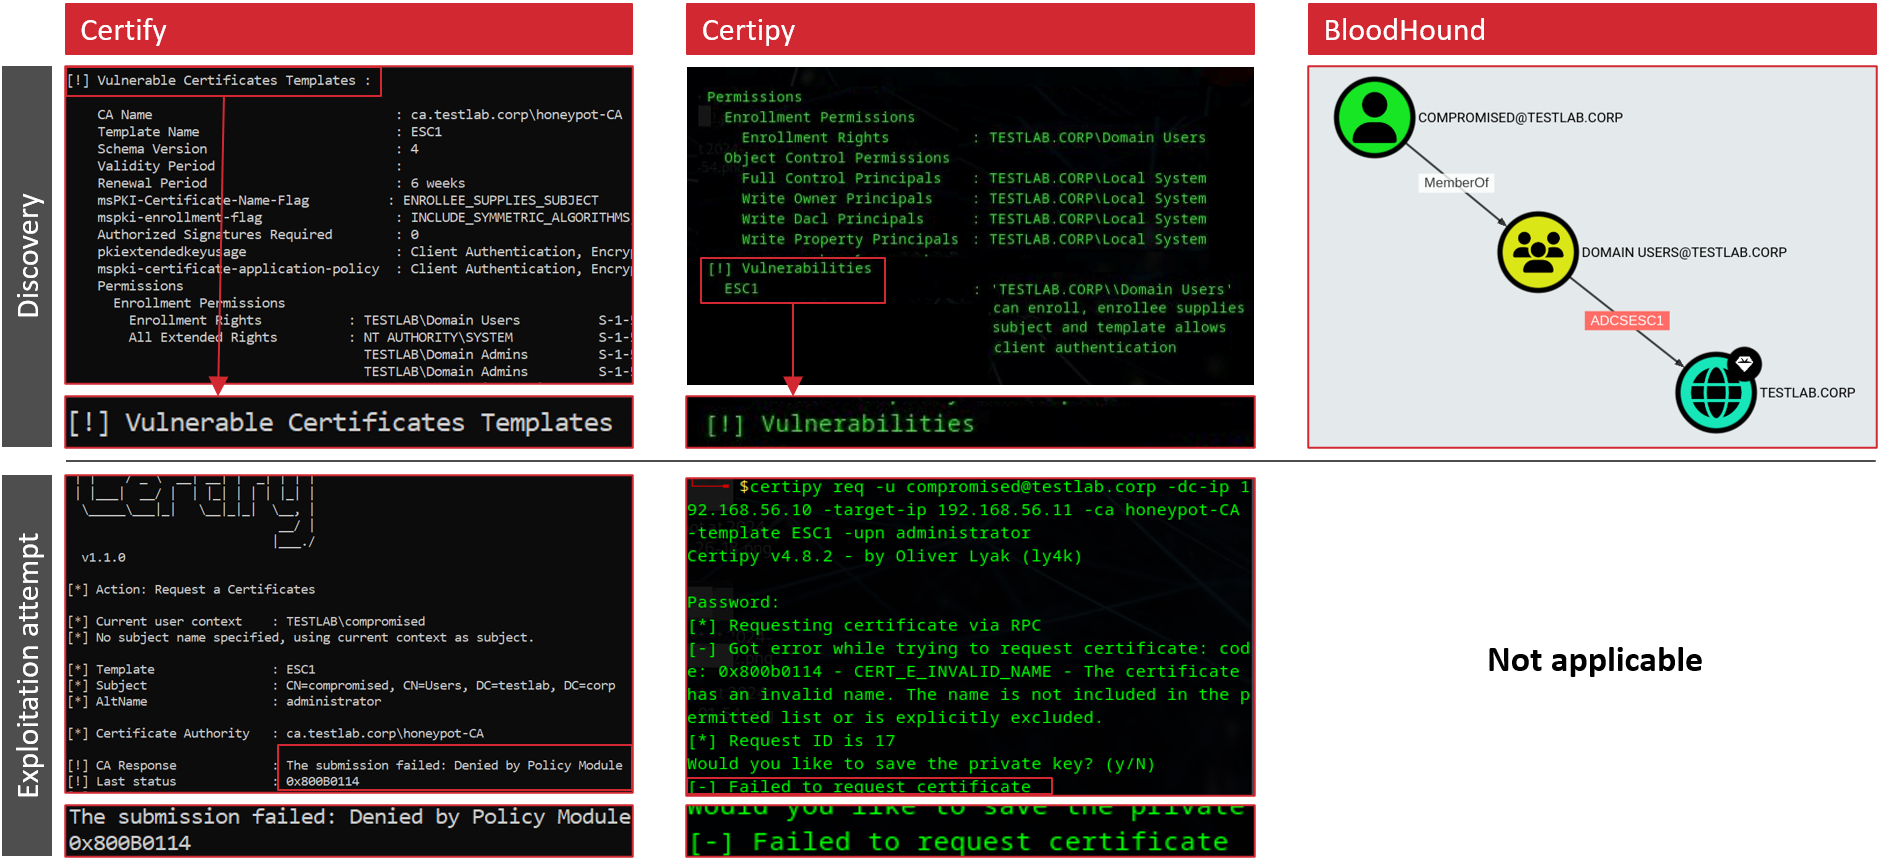 srlabs/certiception
An ADCS honeypot to catch attackers in your internal network.
 george0papasotiriou/cve-2026-9090-modbus-tcp-write-to-read-only-coils-via-function-code-spoofing
PoC Modbus TCP exploit demonstrating spoofed writes to read-only coils in simulated PLCs, highlighting SCADA/ICS access control flaws.
 iamlucif3r/aws-key-hunter
[Just for fun] Find exposed AWS keys (VALID KEYS ONLY) on github
 epsylon/prommetrix
Prommetrix can obtain relevant information from the instances of 'Node Exporter' executed by 'Prometheus'.
 randomrobbiebf/redis-checker
Checks for exposed Redis servers