CVE-2026-26720-Twenty-RCE

Proof-of-concept for authenticated remote code execution in Twenty CRM via unsandboxed serverless workflow functions, allowing arbitrary Node.js…

Proof-of-concept for authenticated remote code execution in Twenty CRM via unsandboxed serverless workflow functions, allowing arbitrary Node.js…

Collection of Semgrep rules for static code analysis, detecting security vulnerabilities, and enforcing secure coding practices across multiple…

KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…


A static + runtime security scanner for MCP (Model Context Protocol) servers

Static analysis security rules for vulnerability detection and audit-focused code review across Java, Go, Python, C#, Kotlin, PHP, Kubernetes, and…

[Just for fun] Find exposed AWS keys (VALID KEYS ONLY) on github

VisualCodeGrepper - Code security scanning tool.

WPBookit <= 1.0.6 - Unauthenticated Stored Cross-Site Scripting

📦 :octocat: A GitHub Action that performs a security scan of your GitHub Actions.

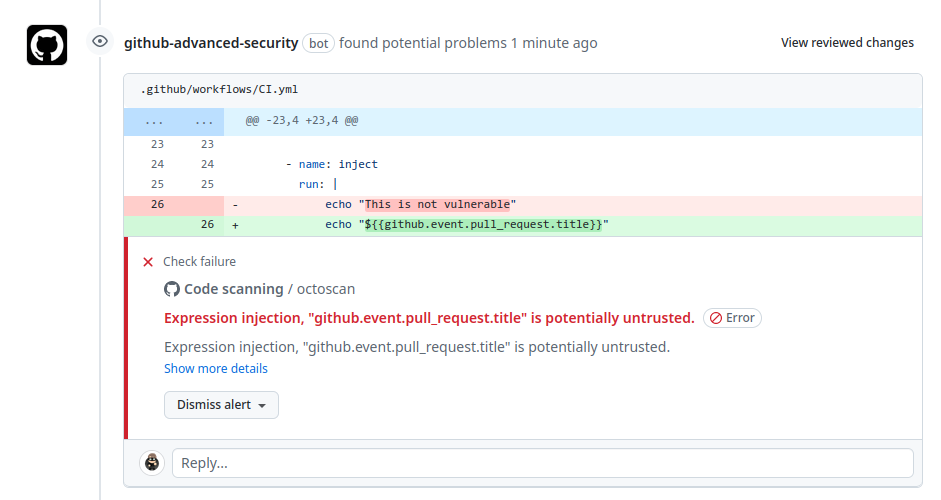
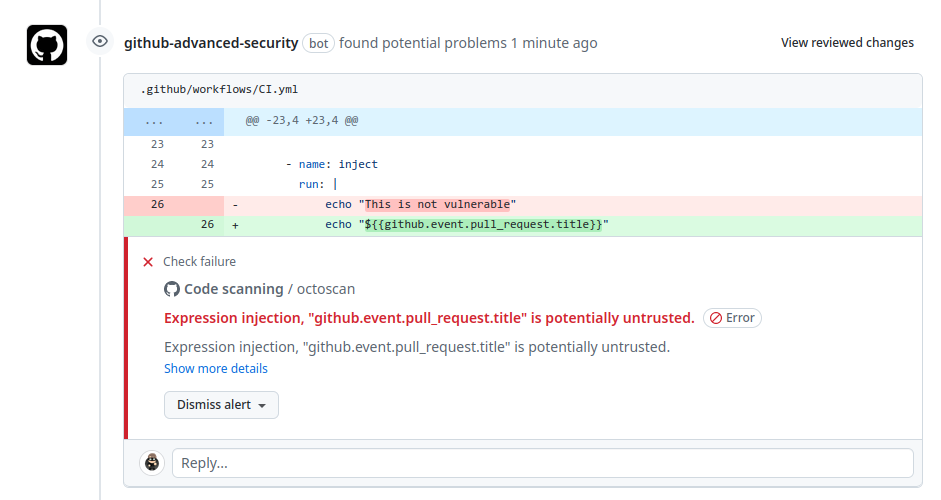
Octoscan is a static vulnerability scanner for GitHub action workflows.

ngxray — nginx config security scanner


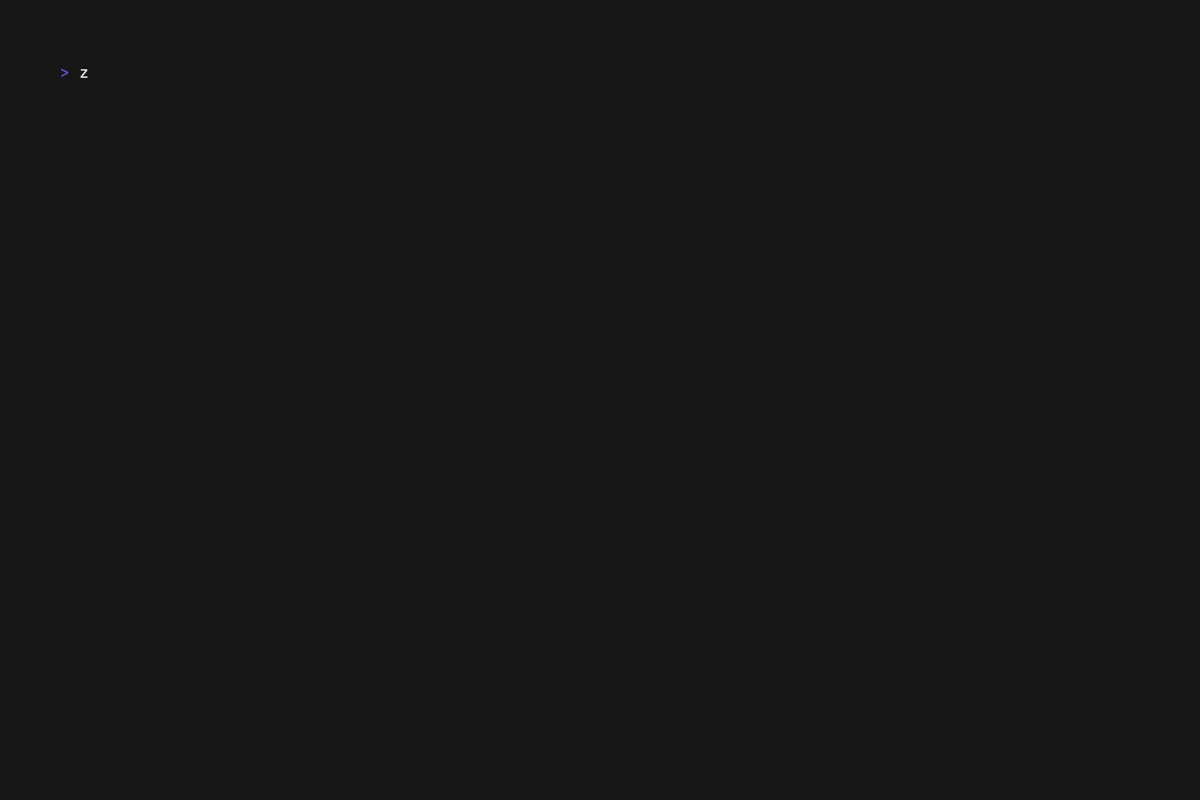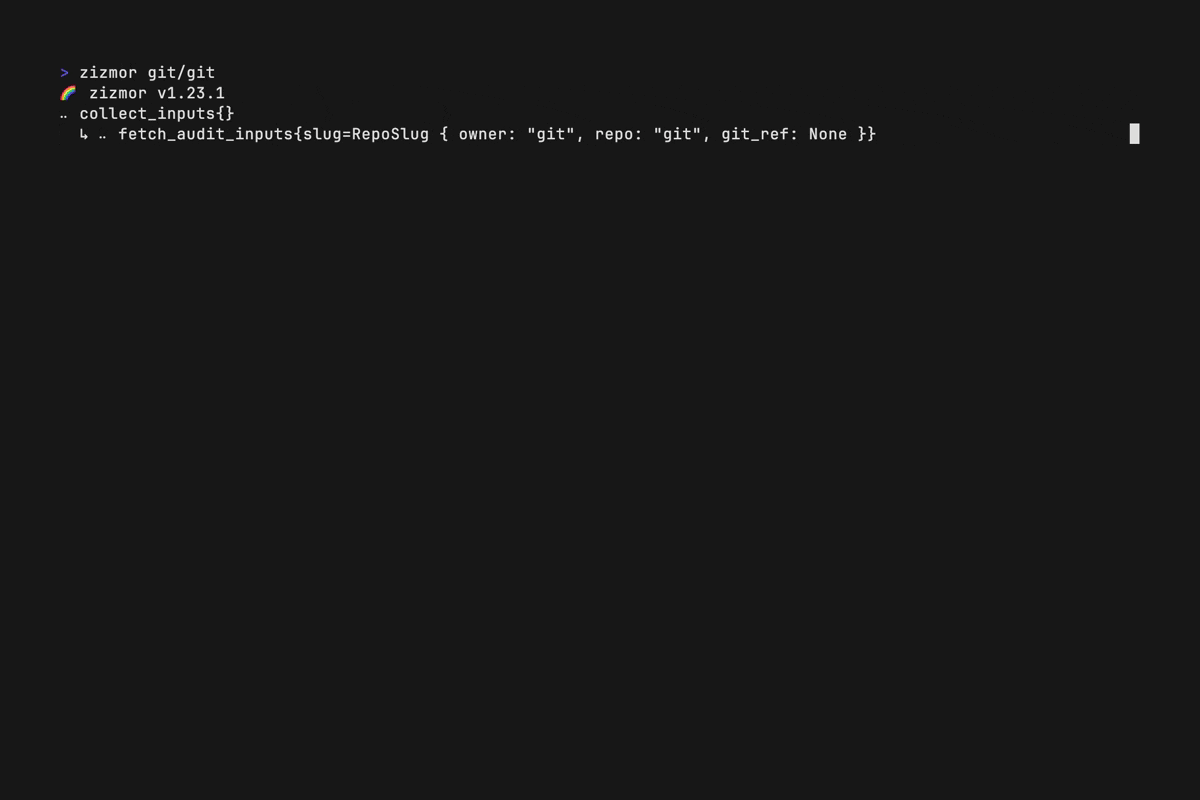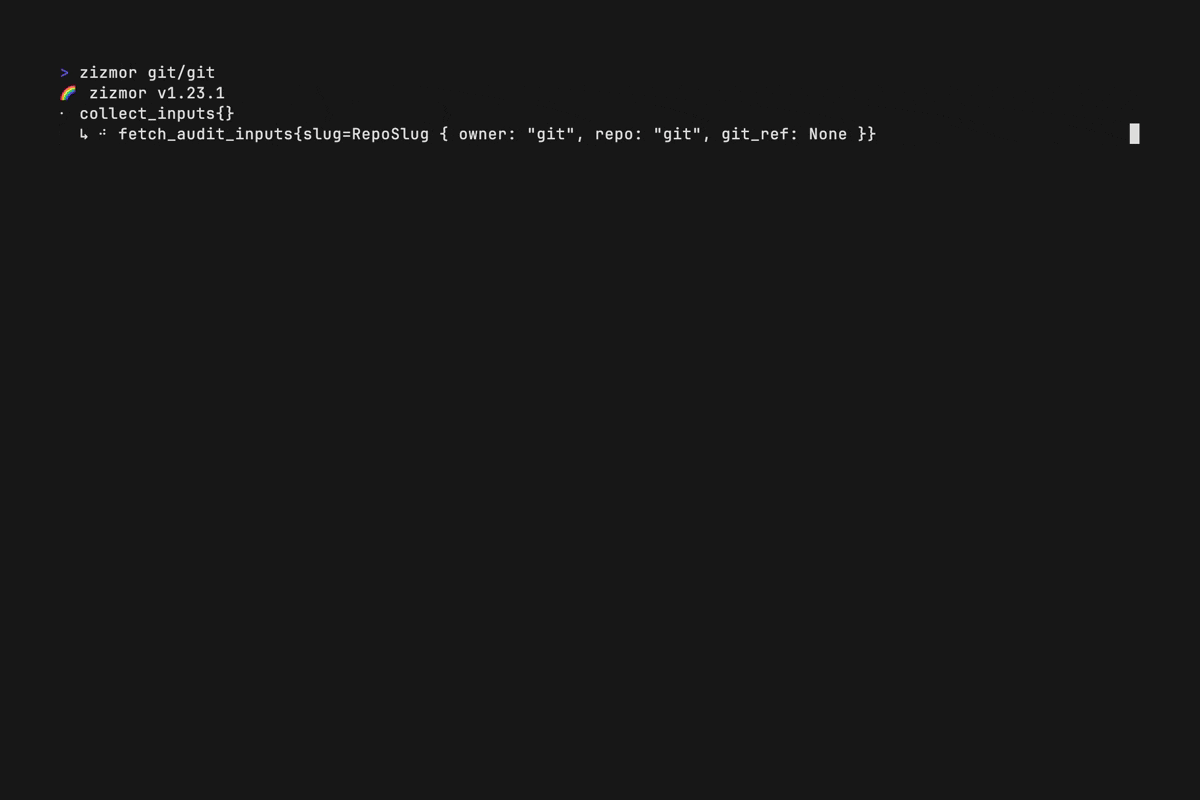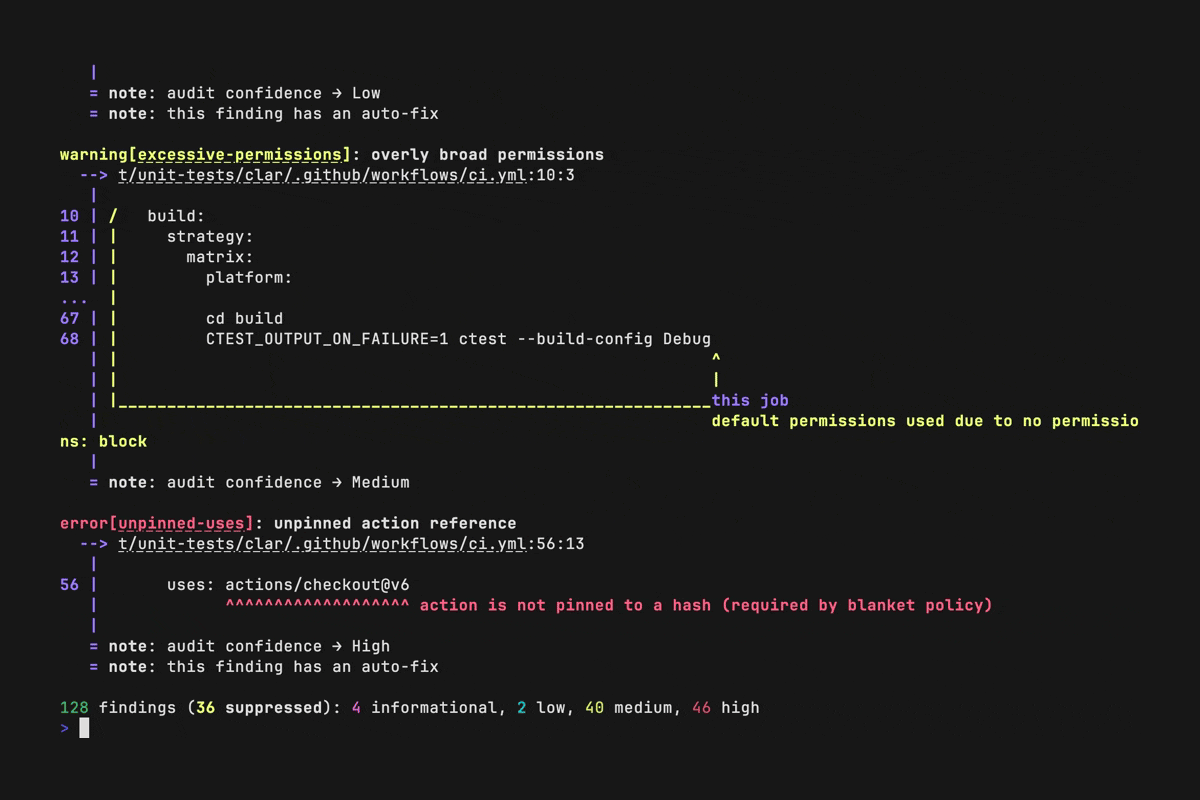
Static analysis tool for CI/CD systems that detects and fixes security issues in GitHub Actions, Dependabot, and pre-commit configurations, including…

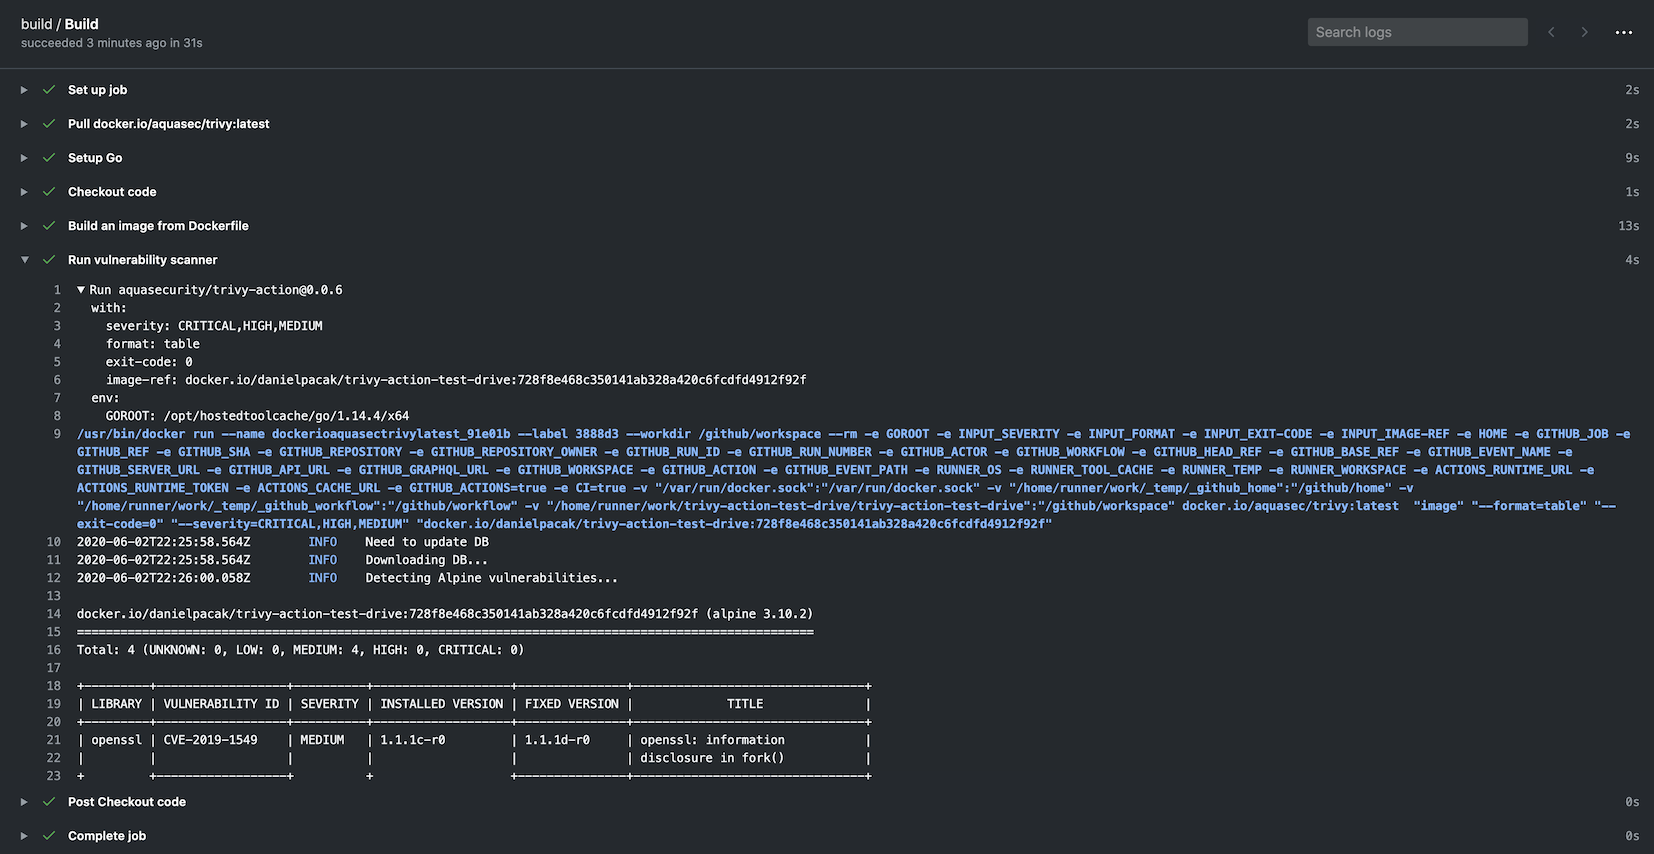
Runs Trivy as GitHub action to scan your Docker container image for vulnerabilities

CVE-2026-42533 Nginx

CVE-2026-60137Temporary Emergency Mitigation for CVE-2026-60137 & CVE-2026-63030 (wp2shell)