
semgrep-rules
 trailofbits/semgrep-rules
Collection of Semgrep rules for static code analysis, detecting security vulnerabilities, and enforcing secure coding practices across multiple…
code-analysisdevsecopsmisconfiguration+2
533
trailofbits/semgrep-rulesCollection of Semgrep rules for static code analysis, detecting security vulnerabilities, and enforcing secure coding practices across multiple…
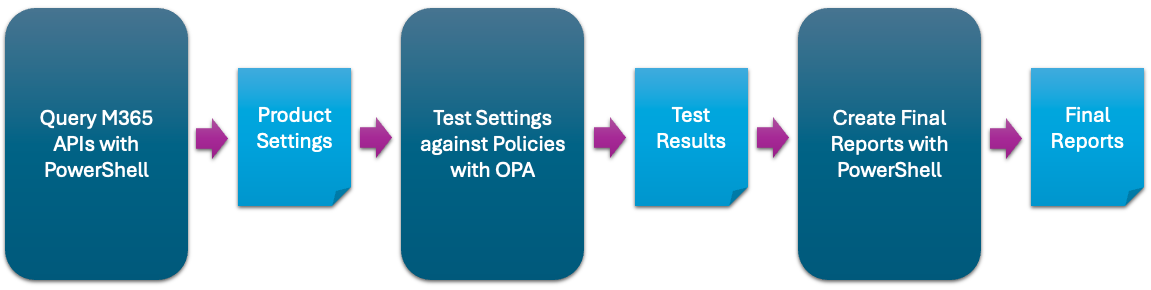 cisagov/scubagear
Automation to assess the state of your M365 tenant against CISA's baselines
 roxanne_ardary/aurea
Aurea is an open-source, AI-powered platform that secures infrastructure-as-code (IaC) across Terraform, Kubernetes, Docker, and Ansible. It…
 comparedarray/printix-cve-2022-25089
An "Incorrect Use of a Privileged API" vulnerability in PrintixService.exe, in Printix's "Printix Secure Cloud Print Management", Version 1.3.1106.0…
 comparedarray/printix-cve-2022-29552
A "Incorrect Use of Privileged APIs" vulnerability in PrintixService.exe, in Kofax Printix's "Printix Secure Cloud Print Management", Version…
 comparedarray/printix-cve-2022-29554
A "Mishandling of Input to API" or "Exposed Dangerous Method or Function" vulnerability in PrintixService.exe, in Kofax Printix's "Printix Secure…
 comparedarray/printix-cve-2022-30006
[Reserved for CVE-2022-30006]
 jordan922/cve-2025-8088
Python tool for safe archive handling, path traversal awareness, and secure extraction. Inspired by CVE-2025-8088.
 edmondscommerce/cve-2011-2461_magento_patch
Patched Adobe Flex SWF files (editor.swf, uploader.swf, uploaderSingle.swf) to fix the CVE-2011-2461 CSRF vulnerability in Magento. Replace…
 guettli/fix-cve-2020-15228
Python script that automatically patches GitHub Actions workflow files to replace deprecated and insecure ::set-env and ::add-path commands with the…
 gensecaihq/cve-2024-3094-vulnerability-checker-fixer
Shell script and Ansible playbook to detect and remediate CVE-2024-3094 in xz-utils by checking package versions, upgrading or downgrading to a…
 g-u-i-d/cve-2024-10449-patch
Patch for CVE-2024-10449: replaces vulnerable loginAction.php with a hardened version that requires database configuration for secure authentication.
 alebedev87/gatekeeper-cve-2020-8554
OPA Gatekeeper constraint policy that detects and prevents Kubernetes clusters from being vulnerable to CVE-2020-8554, enforcing secure configuration.
 helleflo1312/orchestrated-powershell-for-cve-2023-24932
Automated PowerShell orchestrator for applying Secure Boot mitigations against CVE-2023-24932 (BlackLotus). Handles registry changes, reboots,…
 kavin71725/cve-2025-12543-fix-for-wildfly
Docker base image with backported Host header validation fix for CVE-2025-12543 in Undertow 1.4.x, enabling secure deployment of WildFly 11…
 sudo-wp/sudowp-dropzone-elementor
Secure fork of Startklar Elementor Addons. Patched CVE-2024-5153 & File Upload vulnerabilities.
 sudo-wp/sudowp-adminer
A secure, zero-trust database management tool for WordPress. Fixes critical SSRF vulnerabilities (CVE-2021-21311) by enforcing local connections only.