

kubesec
 controlplaneio/kubesec
Security risk analysis for Kubernetes resources
cloud-infrastructure-securitycloud-securityconfiguration-auditing+7
1.5k
controlplaneio/kubesecSecurity risk analysis for Kubernetes resources
 kyverno/kyverno
Enforce security and compliance on Kubernetes clusters via admission controls, resource mutation, background scans, and container image signature…
 aquasecurity/trivy-enforcer
[EXPERIMENTAL] Kubernetes Operator for Image Assurance
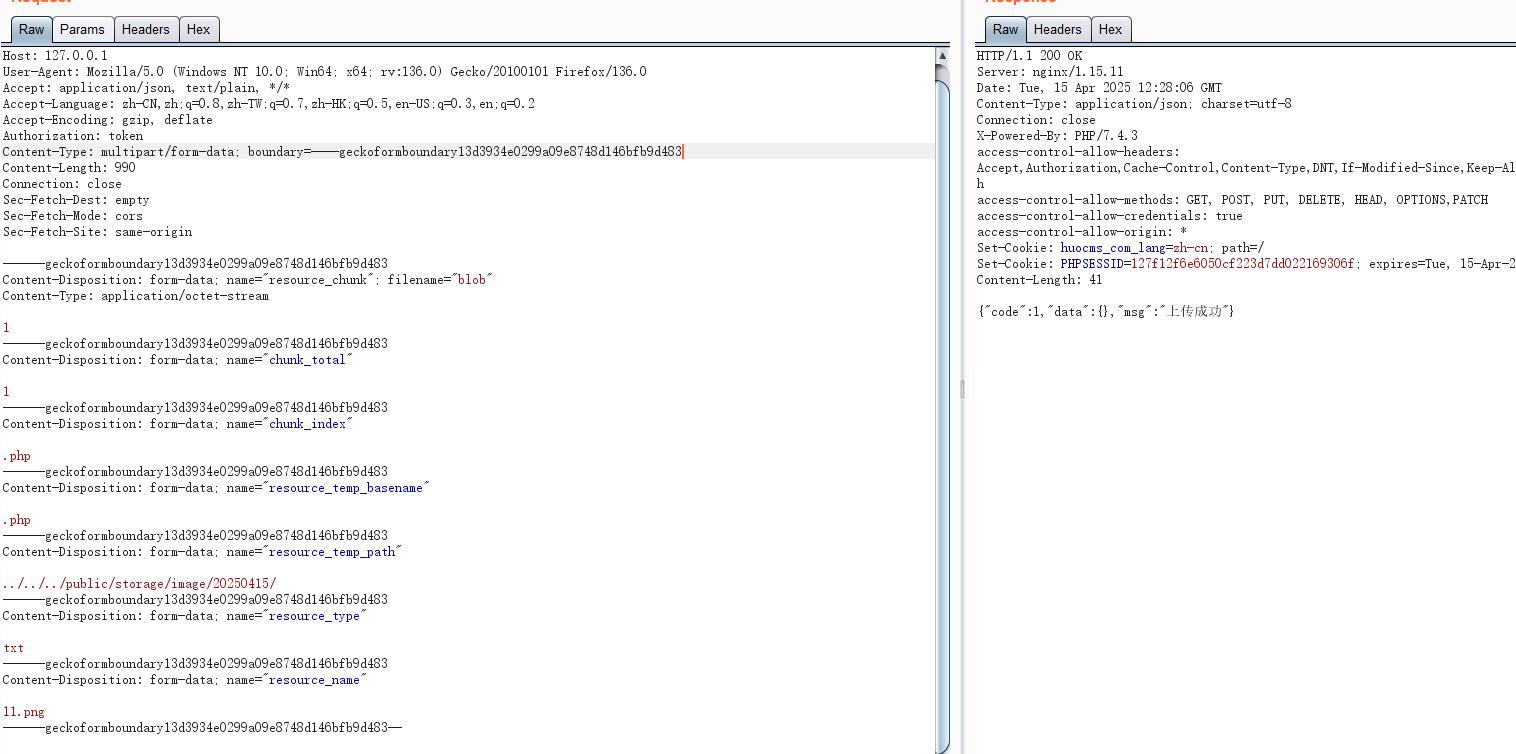 yggcwhat/cve-2025-46078
Vulnerability Description
 shaheryar773/mitigate-cve-2026-23869-react-server-component-loops
Technical troubleshooting repository for fixing infinite rendering vulnerability loops and resource exhaustion threats under CVE-2026-23869 cleanly.
 sibikrish001/cve-2025-55462
Technical documentation and proof-of-concept for CVE-2025-55462, a CORS misconfiguration in Eramba v3.26.0 allowing cross-origin authentication…
 trevorputbrese/cve-2024-38819-lab
Hands-on lab demonstrating CVE-2024-38819 Spring Framework path traversal vulnerability with vulnerable and patched Spring Boot deployments for…
 f4rber/cve-2020-36287
The dashboard gadgets preference resource of the Atlassian gadgets plugin used in Jira Server and Jira Data Center before version 8.13.5, and from…
 dovankha/cve-2024-34221
Proof-of-concept for CVE-2024-34221: insecure permission vulnerability in SourceCodester Human Resource Management System 1.0 allowing unauthorized…
 dovankha/cve-2024-34223
Proof-of-concept for CVE-2024-34223: insecure permission vulnerability in SourceCodester HRMS 1.0 allowing unauthorized leave ticket…
 stolichnayer/cve-2025-22828
Apache CloudStack vulnerability allows unauthorized access to annotations on certain resources.
 amnnrth/cve-2025-34291_cors_security_scanner
A lightweight Python-based security assessment tool for detecting dangerous Cross-Origin Resource Sharing (CORS) misconfigurations - CVE-2025-34291.
 echosecure/vuln-chain-lab
PoC Docker lab: chaining file upload bypass + stored XSS to create admin accounts. Educational resource for pen testers.
 rub-nds/corstest
A simple CORS misconfiguration scanner
 lc/theftfuzzer
TheftFuzzer is a tool that fuzzes Cross-Origin Resource Sharing implementations for common misconfigurations.
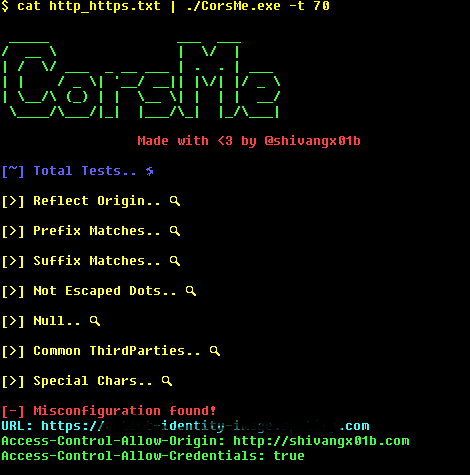 shivangx01b/corsme
Cross Origin Resource Sharing MisConfiguration Scanner
 summitroute/aws_exposable_resources
Curated catalog of AWS resource types that can be publicly exposed, with CLI commands for creating and auditing public access configurations across…
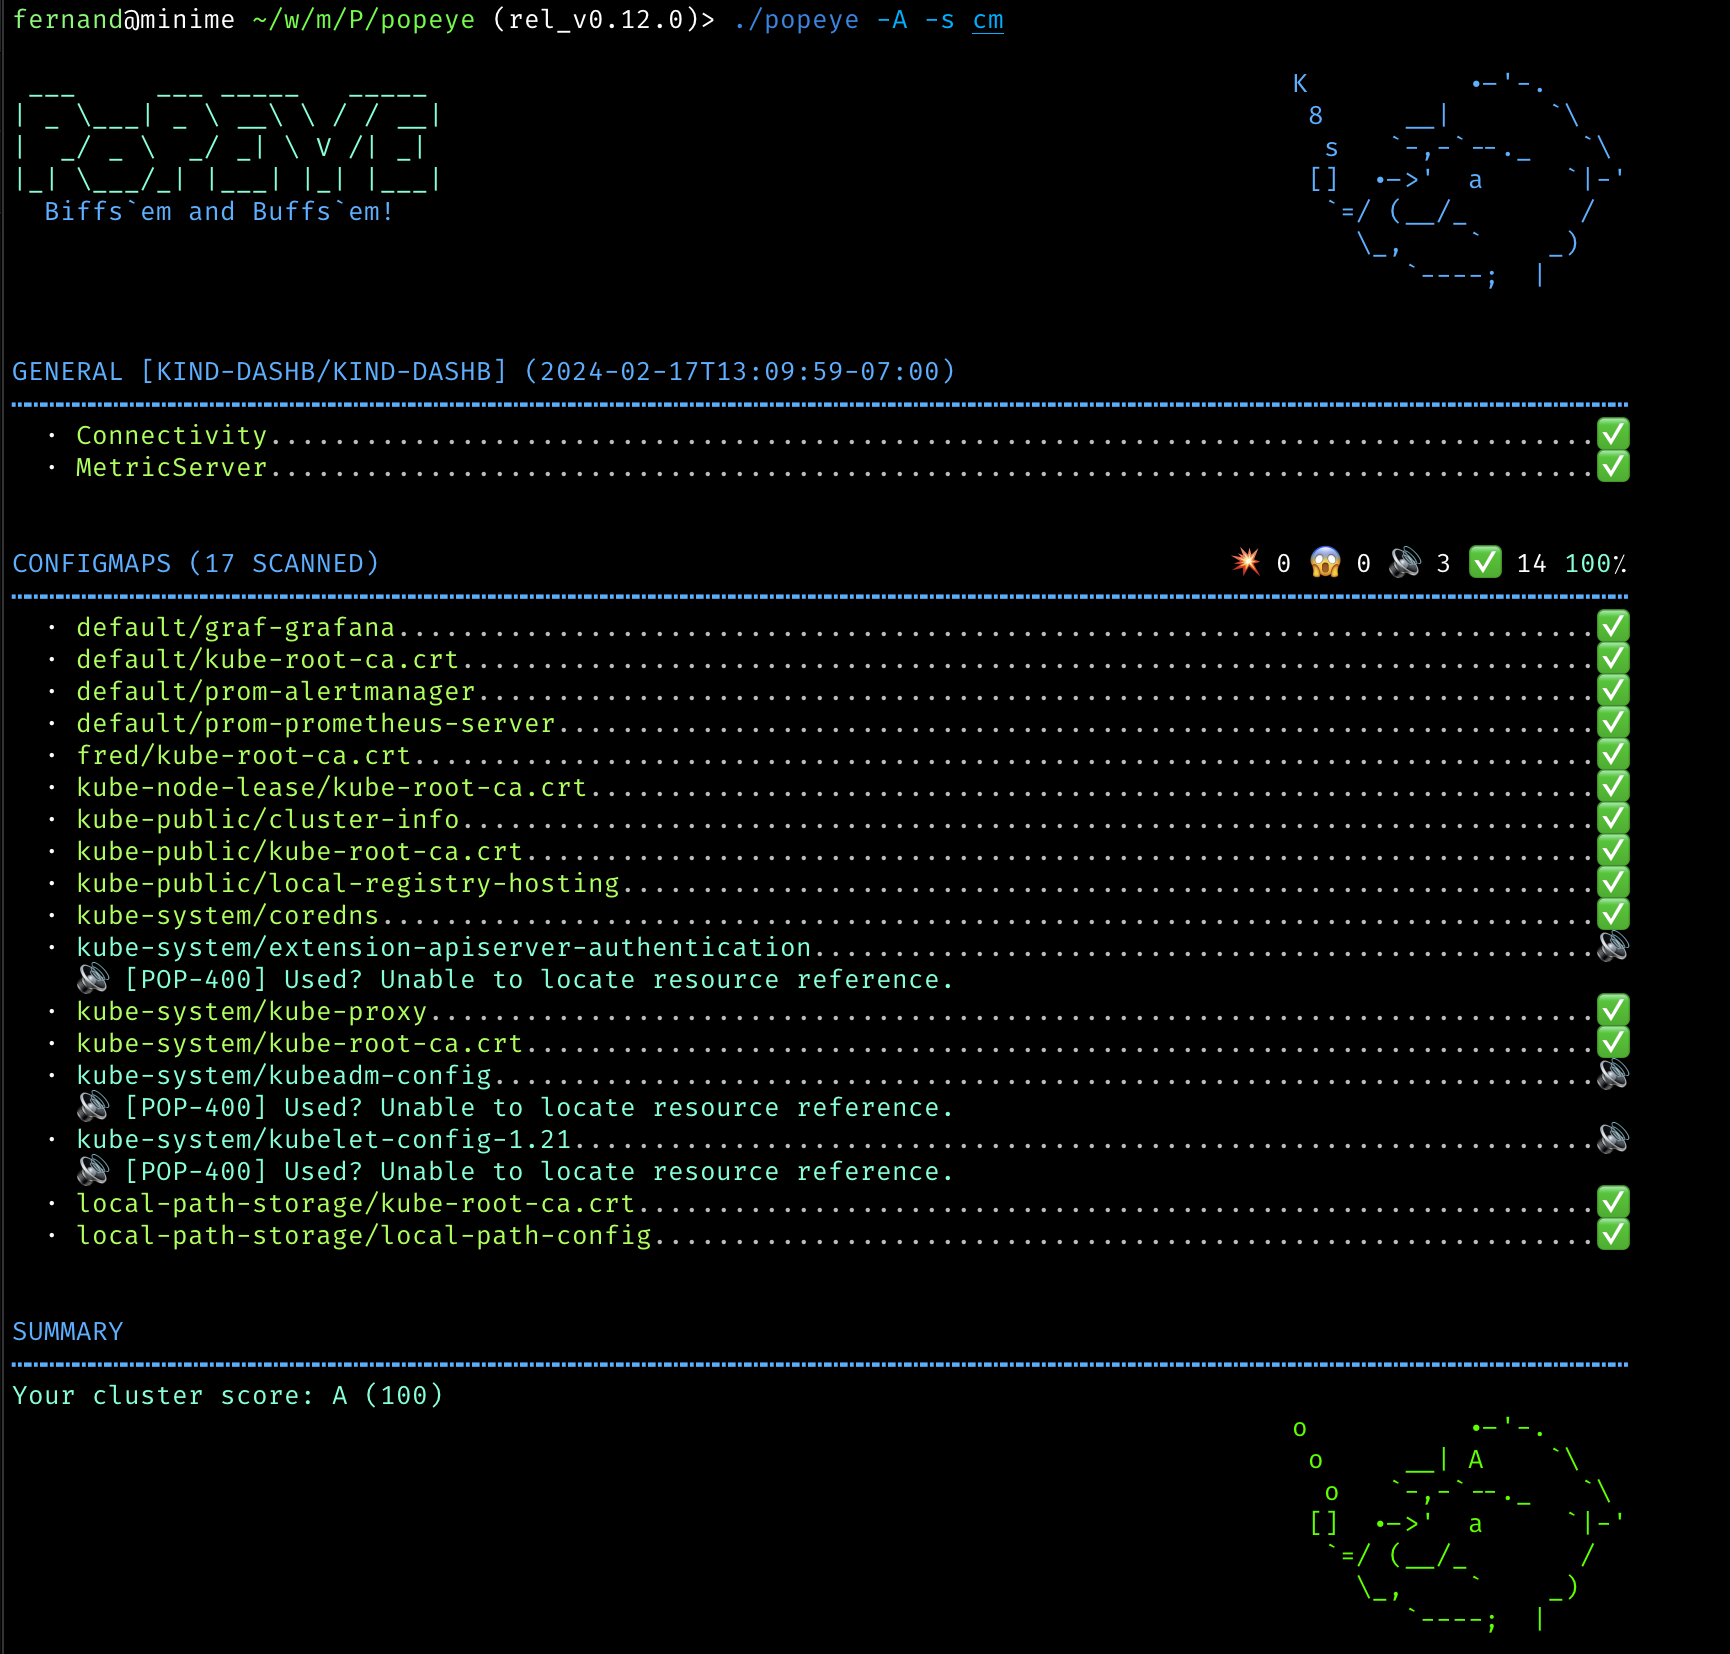 derailed/popeye
👀 A Kubernetes cluster resource sanitizer