bring-your-own-key-cve-2026-73678-unauthenticated-rce-in-mindsdb-cowork

PoC exploit for CVE-2026-73678: unauthenticated RCE in MindsDB Cowork via attacker-supplied LLM key and unsandboxed scratchpad exec to run OS…

PoC exploit for CVE-2026-73678: unauthenticated RCE in MindsDB Cowork via attacker-supplied LLM key and unsandboxed scratchpad exec to run OS…

Burp Suite Extension useful to verify OAUTHv2 and OpenID security

Scanner: CVE-2025-34291 Langflow Origin Validation Error / CORS Misconfiguration — Python checker (CISA KEV)

Academic purposes only. Attack against Salesforce lightning with guest privilege.

Python script to bypass Azure APIM signup when UI is disabled, this is different from the CVE-2025-66390 as it does not require you to setup anything…

Milvus 认证安全检测脚本:CVE-2025-64513 (sourceid后门) / CVE-2026-26190 (/expr弱token) / 内部端口53100

Validates Google Maps API keys against 21 endpoints, revealing exposed services with PoC URLs, proxy support, and quiet mode for focused auditing.

Use Exposed KongAPI to act like a proxy and get metadata urls or internal urls

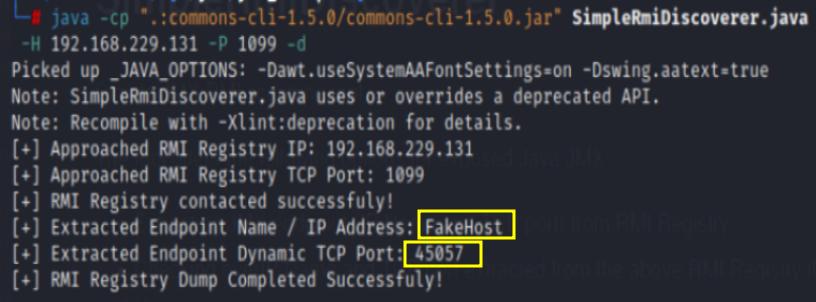
Simple JMX RMI scanning tool

find sensitive data leaking from ServiceNow instances.

Covered CVEs: CVE-2026-28755, CVE-2026-42926, CVE-2026-9256, CVE-2026-42055, CVE-2026-42533

Drop-in fix for the unpatched MCP STDIO command-injection flaw (CVE-2026-30623 family)

Supermicro IPMI/BMC Cleartext Password Scanner

AI-powered vulnerability scanner extension for Burp Suite with multi-provider support (Ollama, OpenAI, Claude, Gemini)

The code for personally reproducing the corresponding vulnerability

nginx 1.15.10 patch against cve-2021-23017 (ingress version)

演示 Next.js 中的 Middleware 授權繞過漏洞 (CVE-2025-29927) 允許未經授權的用戶存取受保護的資訊。

Here's a Python script that checks if the polyfill.io domain is present in the Content Security Policy (CSP) header of a given web application.