Windows-Defender-Security-Auditor-CVE-2026-50656-

Read-only PowerShell security auditor for Windows endpoints and servers: checks Defender configuration, patch status, credentials, persistence,…

Read-only PowerShell security auditor for Windows endpoints and servers: checks Defender configuration, patch status, credentials, persistence,…

HardeningKitty - Checks and hardens your Windows configuration

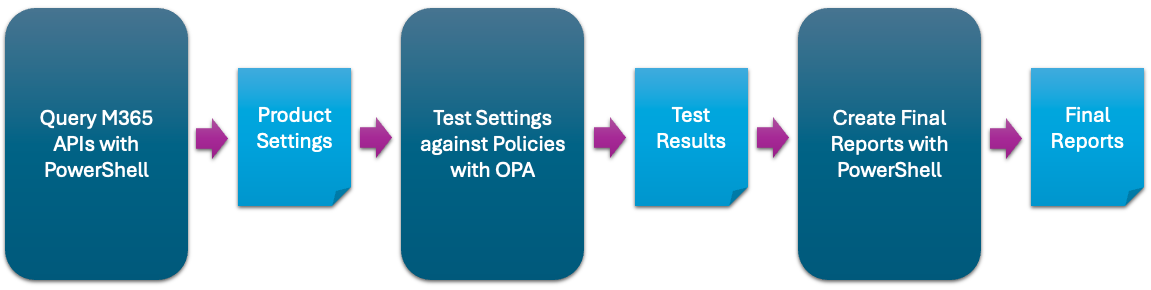
Automation to assess the state of your M365 tenant against CISA's baselines

HardeningKitty and Windows Hardening Settings

Windows Local Privilege Escalation Cookbook

Scans exported Azure domain dumps for plaintext passwords, connection strings, storage keys, and other secrets; generates redacted CSV/HTML reports…

A small tool built to find and fix common misconfigurations in Active Directory Certificate Services.

PowerShell script to mitigate CVE-2013-3900 by enabling stricter WinVerifyTrust Authenticode signature validation via registry configuration.

A simple script to remove Log4J JndiLookup.class from jars in a given directory, to temporarily protect from CVE-2021-45046 and CVE-2021-44228.

PowerShell scripts to apply and restore Microsoft's registry-based workaround for CVE-2022-30190 (Follina) vulnerability, deployable via InTune for…

PowerShell script to apply Microsoft's recommended registry-based workaround for CVE-2023-36884, mitigating remote code execution risk on Windows…

Fix WinVerifyTrust Signature Validation Vulnerability, CVE-2013-3900, QID-378332

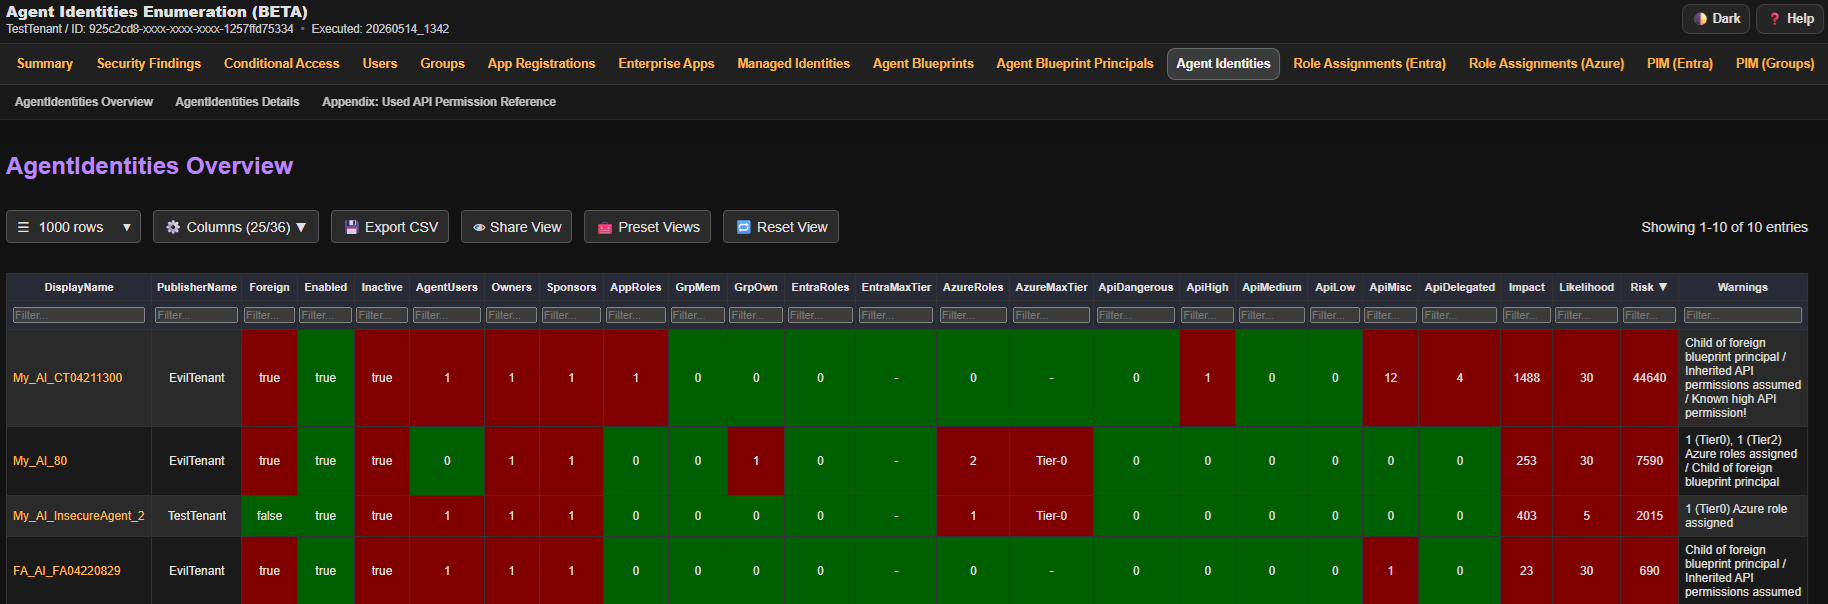
A lightweight PowerShell tool for assessing the security posture of Microsoft Entra ID environments. It helps identify privileged objects, risky…

Script to check for CVE-2023-36884 hardening

CVE-2021-36934 PowerShell Fix

My CVE-2017-8529 files

PowerShell script to remediate CVE-2013-3900 by enabling certificate padding check via registry hardening on Windows systems.

Mitigate log4shell (CVE-2021-44228) vulnerability attacks using Nginx LUA script