CVE-2026-22004-Git-LFS-Pointer-Poisoning-Supply-Chain-

Proof-of-concept for Git LFS pointer poisoning, with Bash and Python scripts that create a malicious repository, simulate a rogue LFS server, and…

Proof-of-concept for Git LFS pointer poisoning, with Bash and Python scripts that create a malicious repository, simulate a rogue LFS server, and…

JavaPayload is a collection of pure Java payloads to be used for post-exploitation from pure Java exploits or from common misconfigurations (like not…

WPBookit <= 1.0.6 - Unauthenticated Stored Cross-Site Scripting

[EXPERIMENTAL] Kubernetes Operator for Image Assurance

DJ-Classifieds Joomla Component Unauthenticated File Upload RCE. 3-string filter bypass via PHP short tags. CVSS 10.0 | CWE-434 | com_djclassifieds <…

Proof-of-concept for CVE-2023-37756: weak password requirements in i-doit Pro admin-center enabling brute-force login and malicious plugin upload…

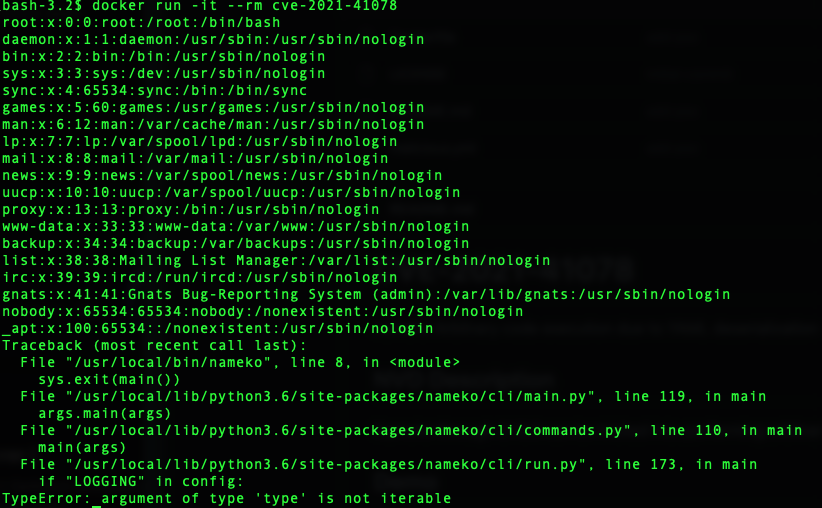
nameko Arbitrary code execution due to YAML deserialization

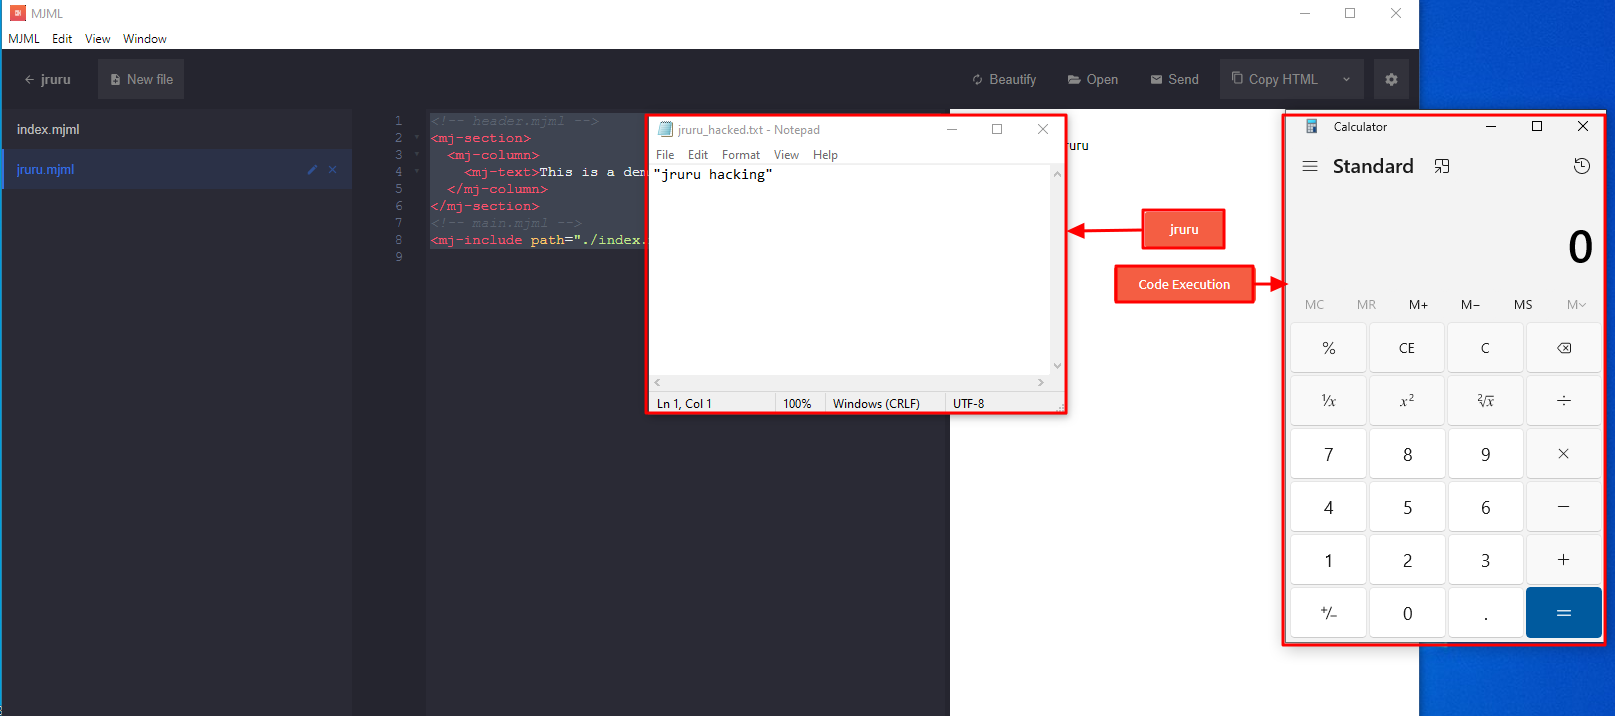
mjml-app v3.0.4 & 3.1.0-beta RCE exploit

A simple script to remove Log4J JndiLookup.class from jars in a given directory, to temporarily protect from CVE-2021-45046 and CVE-2021-44228.

Simple Dashboard <= 2.0 - Unauthenticated Privilege Escalation

CVE-2024-55963, allows unauthenticated remote code execution on Appsmith Enterprise platform due to a misconfigured PostgreSQL database included by…

Local privilege escalation exploit for Trend Micro OfficeScan Client <=10.0 via misconfigured ACLs on the installation folder, enabling system-level…

Mitigate log4shell (CVE-2021-44228) vulnerability attacks using Nginx LUA script


This tool creates a custom signature set on F5 WAF and apply to policies in blocking mode

Bash script to detect and remediate CVE-2024-3094, a critical supply-chain vulnerability in the XZ Utils library, with automatic safe version…

Shell script and Ansible playbook to detect and remediate CVE-2024-3094 in xz-utils by checking package versions, upgrading or downgrading to a…

A drop-in fix for CVE-2023-29689 - SSTI in PyroCMS, via a custom Twig Sandbox implementation