
semgrep-rules
 trailofbits/semgrep-rules
Collection of Semgrep rules for static code analysis, detecting security vulnerabilities, and enforcing secure coding practices across multiple…
code-analysisdevsecopsmisconfiguration+2
527
trailofbits/semgrep-rulesCollection of Semgrep rules for static code analysis, detecting security vulnerabilities, and enforcing secure coding practices across multiple…
 eh-amish/windows-defender-security-auditor-cve-2026-50656-
Read-only PowerShell security auditor for Windows endpoints and servers: checks Defender configuration, patch status, credentials, persistence,…
 nccgroup/raccoon
Salesforce object access auditor
 nccgroup/sfpoldevchk
Salesforce Policy Deviation Checker
 nccgroup/whalescan
Whalescan is a vulnerability scanner for Windows containers, which performs several benchmark checks, as well as checking for CVEs/vulnerable…
 mooseloveti/trinity-audio-cve-report
Disclosure for CVE-2025-9196
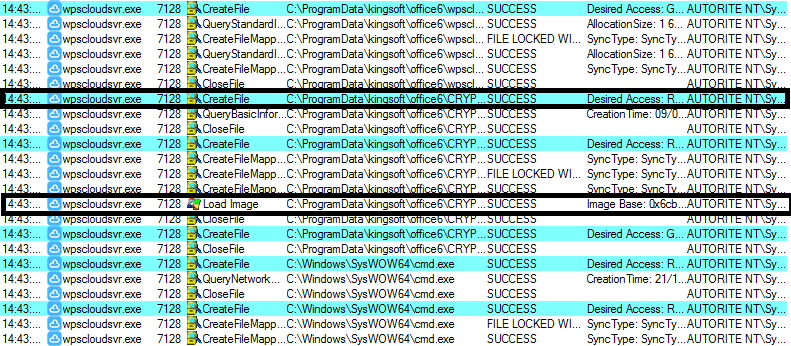 hadimed/kingsoft-wps-office-lpe
CVE-2022-25943
 dckento/cve-2021-40375
Broken Access Control in OpenEyes 3.5.1
 seqred-s-a/cve-2020-10551
Privilege escalation in QQBrowser
 h1thub/cve-2024-46635
Proof-of-concept for CVE-2024-46635: an improper input validation vulnerability in GongZhiDao System's API endpoint that exposes sensitive user…
 aman-parmar/cve-2025-54554
CVE-2025-54554 – Unauthenticated Access in tiaudit REST API leading to Sensitive Information Disclosure
 jsitech/jshielder
Hardening Script for Linux Servers/ Secure LAMP-LEMP Deployer/ CIS Benchmark
 bitthebyte/eagle
Multithreaded Plugin based vulnerability scanner for mass detection of web-based applications vulnerabilities
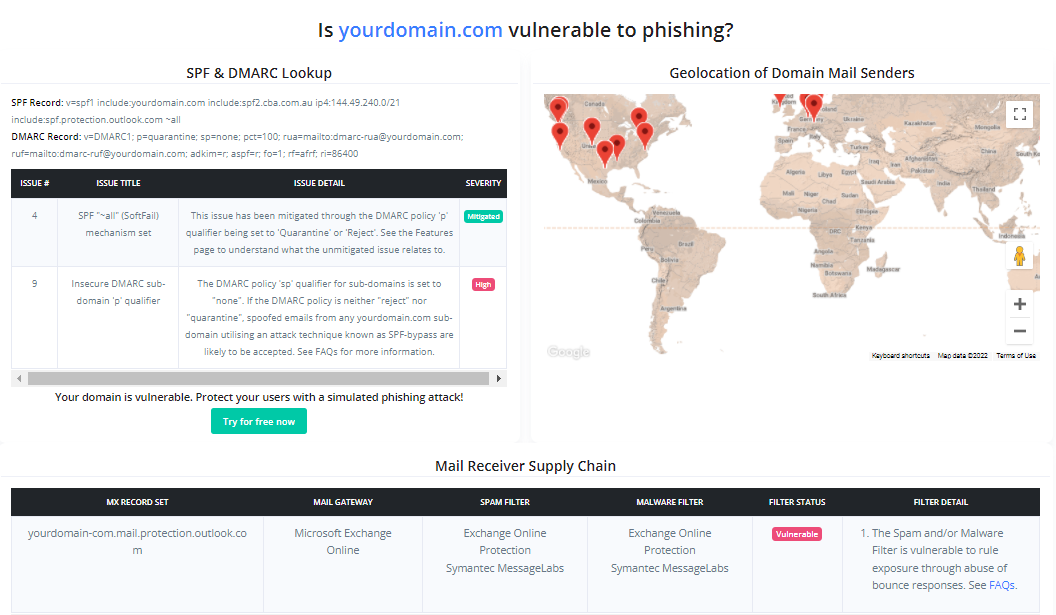 caniphish/phishious
An open-source Secure Email Gateway (SEG) evaluation toolkit designed for red-teamers.
 owasp/joomscan
Perl-based Joomla CMS vulnerability scanner automating version enumeration, component detection, exploit matching, firewall identification, and…