
siem
 ekitji/siem
Curated SIEM queries and techniques for offensive discovery of Windows privilege escalation, misconfigured ACLs, services, scheduled tasks, and…
curated-resourcesdefensive-toolseducation+7
47
ekitji/siemCurated SIEM queries and techniques for offensive discovery of Windows privilege escalation, misconfigured ACLs, services, scheduled tasks, and…
 bombobombone/cve-2026-73317
Proof-of-concept exploit and technical write-up for CVE-2026-73317, an authorization bypass in XenForo allowing limited admins to approve content as…
 bombobombone/cve-2026-73318
Proof-of-concept exploit for XenForo CVE-2026-73318, an authorization bypass allowing ACP administrators to trigger site-wide policy re-agreement.…
 stelligent/cfn_nag
Linting tool for CloudFormation templates
 stackrox/kube-linter
KubeLinter is a static analysis tool that checks Kubernetes YAML files and Helm charts to ensure the applications represented in them adhere to best…
 open-policy-agent/opa
Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…
 burjoy/cve-2024-40275_scanner
Scanner for CVE-2024-40725 Apache HTTP Server source-code disclosure; probes direct and subrequest paths, fingerprints affected versions, and outputs…
 eh-amish/windows-defender-security-auditor-cve-2026-50656-
Read-only PowerShell security auditor for Windows endpoints and servers: checks Defender configuration, patch status, credentials, persistence,…
 ac8999/cve-2026-27344
Missing Authorization in inseriswiss inseri core inseri-core allows Exploiting Incorrectly Configured Access Control Security Levels.This issue…
 neelkotnis/azure-security-auditor
CLI tool to audit Azure security posture, RBAC, NSGs, storage, identity, and encryption
 assurancemaladiesec/ad-description-password-finder
Retrieve AD accounts description and search for password in it
 scipag/hardeningkitty
HardeningKitty - Checks and hardens your Windows configuration
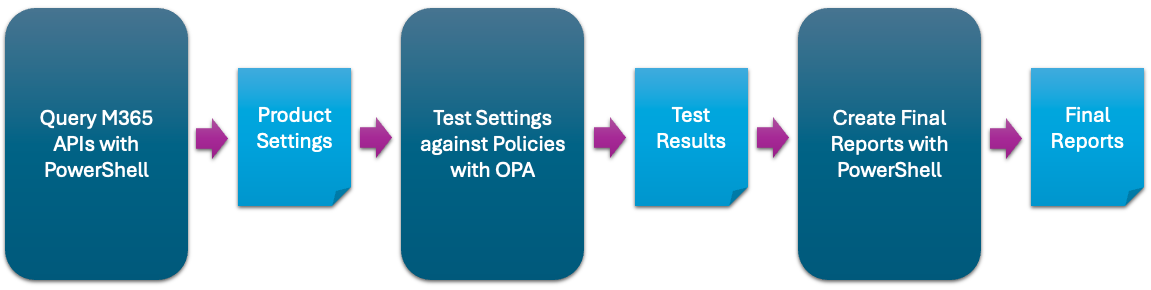 cisagov/scubagear
Automation to assess the state of your M365 tenant against CISA's baselines
 moniik/poc_salesforce_lightning
Academic purposes only. Attack against Salesforce lightning with guest privilege.
 johenlastgen-jlg/cve-2026-11961
CVE-2026-11961 — UserRegistration: WordPress User Registration <= 5.2.2 Privilege Escalation. Misconfigured Membership Roles → Unauthenticated Admin…
 renniepak/cspbypass
CSPBypass.com, a tool designed to help ethical hackers bypass restrictive Content Security Policies (CSP) and exploit XSS (Cross-Site Scripting)…
 george0papasotiriou/cve-2026-21017-ldap-anonymous-bind-privilege-escalation
Python proof-of-concept for LDAP anonymous bind privilege escalation, simulating insecure ACLs to create admin users via unauthenticated LDAP binds.
 coffinxp/google-api-key-scanner
Validates Google Maps API keys against 21 endpoints, revealing exposed services with PoC URLs, proxy support, and quiet mode for focused auditing.