
lynis
 cisofy/lynis
Agentless security auditing tool for Linux, macOS, and UNIX systems. Performs in-depth scans for vulnerabilities, configuration issues, and…
configuration-auditingdatabase-securitydefensive-tools+5
16.4k
cisofy/lynisAgentless security auditing tool for Linux, macOS, and UNIX systems. Performs in-depth scans for vulnerabilities, configuration issues, and…
 santandersecurityresearch/corsair_scan
Automated CORS misconfiguration scanner that tests Origin header injection, wildcard reflection, and credential leakage across web applications and…
 burjoy/cve-2024-40275_scanner
Scanner for CVE-2024-40725 Apache HTTP Server source-code disclosure; probes direct and subrequest paths, fingerprints affected versions, and outputs…
 stampery/mongoaudit
🔥 A powerful MongoDB auditing and pentesting tool 🔥
 nccgroup/vcg
VisualCodeGrepper - Code security scanning tool.
 rub-nds/corstest
A simple CORS misconfiguration scanner
 trufflesecurity/of-cors
Automated CORS misconfiguration discovery tool using typosquatting domains and browser service workers to probe internal networks of bug bounty…
 google/aura-inspector
Automated security testing tool for Salesforce Experience Cloud that discovers misconfigured Aura applications, accessible records, and unauthorized…
 hakaioffsec/navgix
Multi-threaded Go tool to detect nginx alias traversal vulnerabilities using heuristic and brute-force techniques for identifying vulnerable…
 iamlucif3r/aws-key-hunter
[Just for fun] Find exposed AWS keys (VALID KEYS ONLY) on github
 padayali-jd/pollyscan
A specialized vulnerability scanner designed to detect CVE-2024-38526, the Polyfill.io Supply Chain Attack, helping organizations identify and…
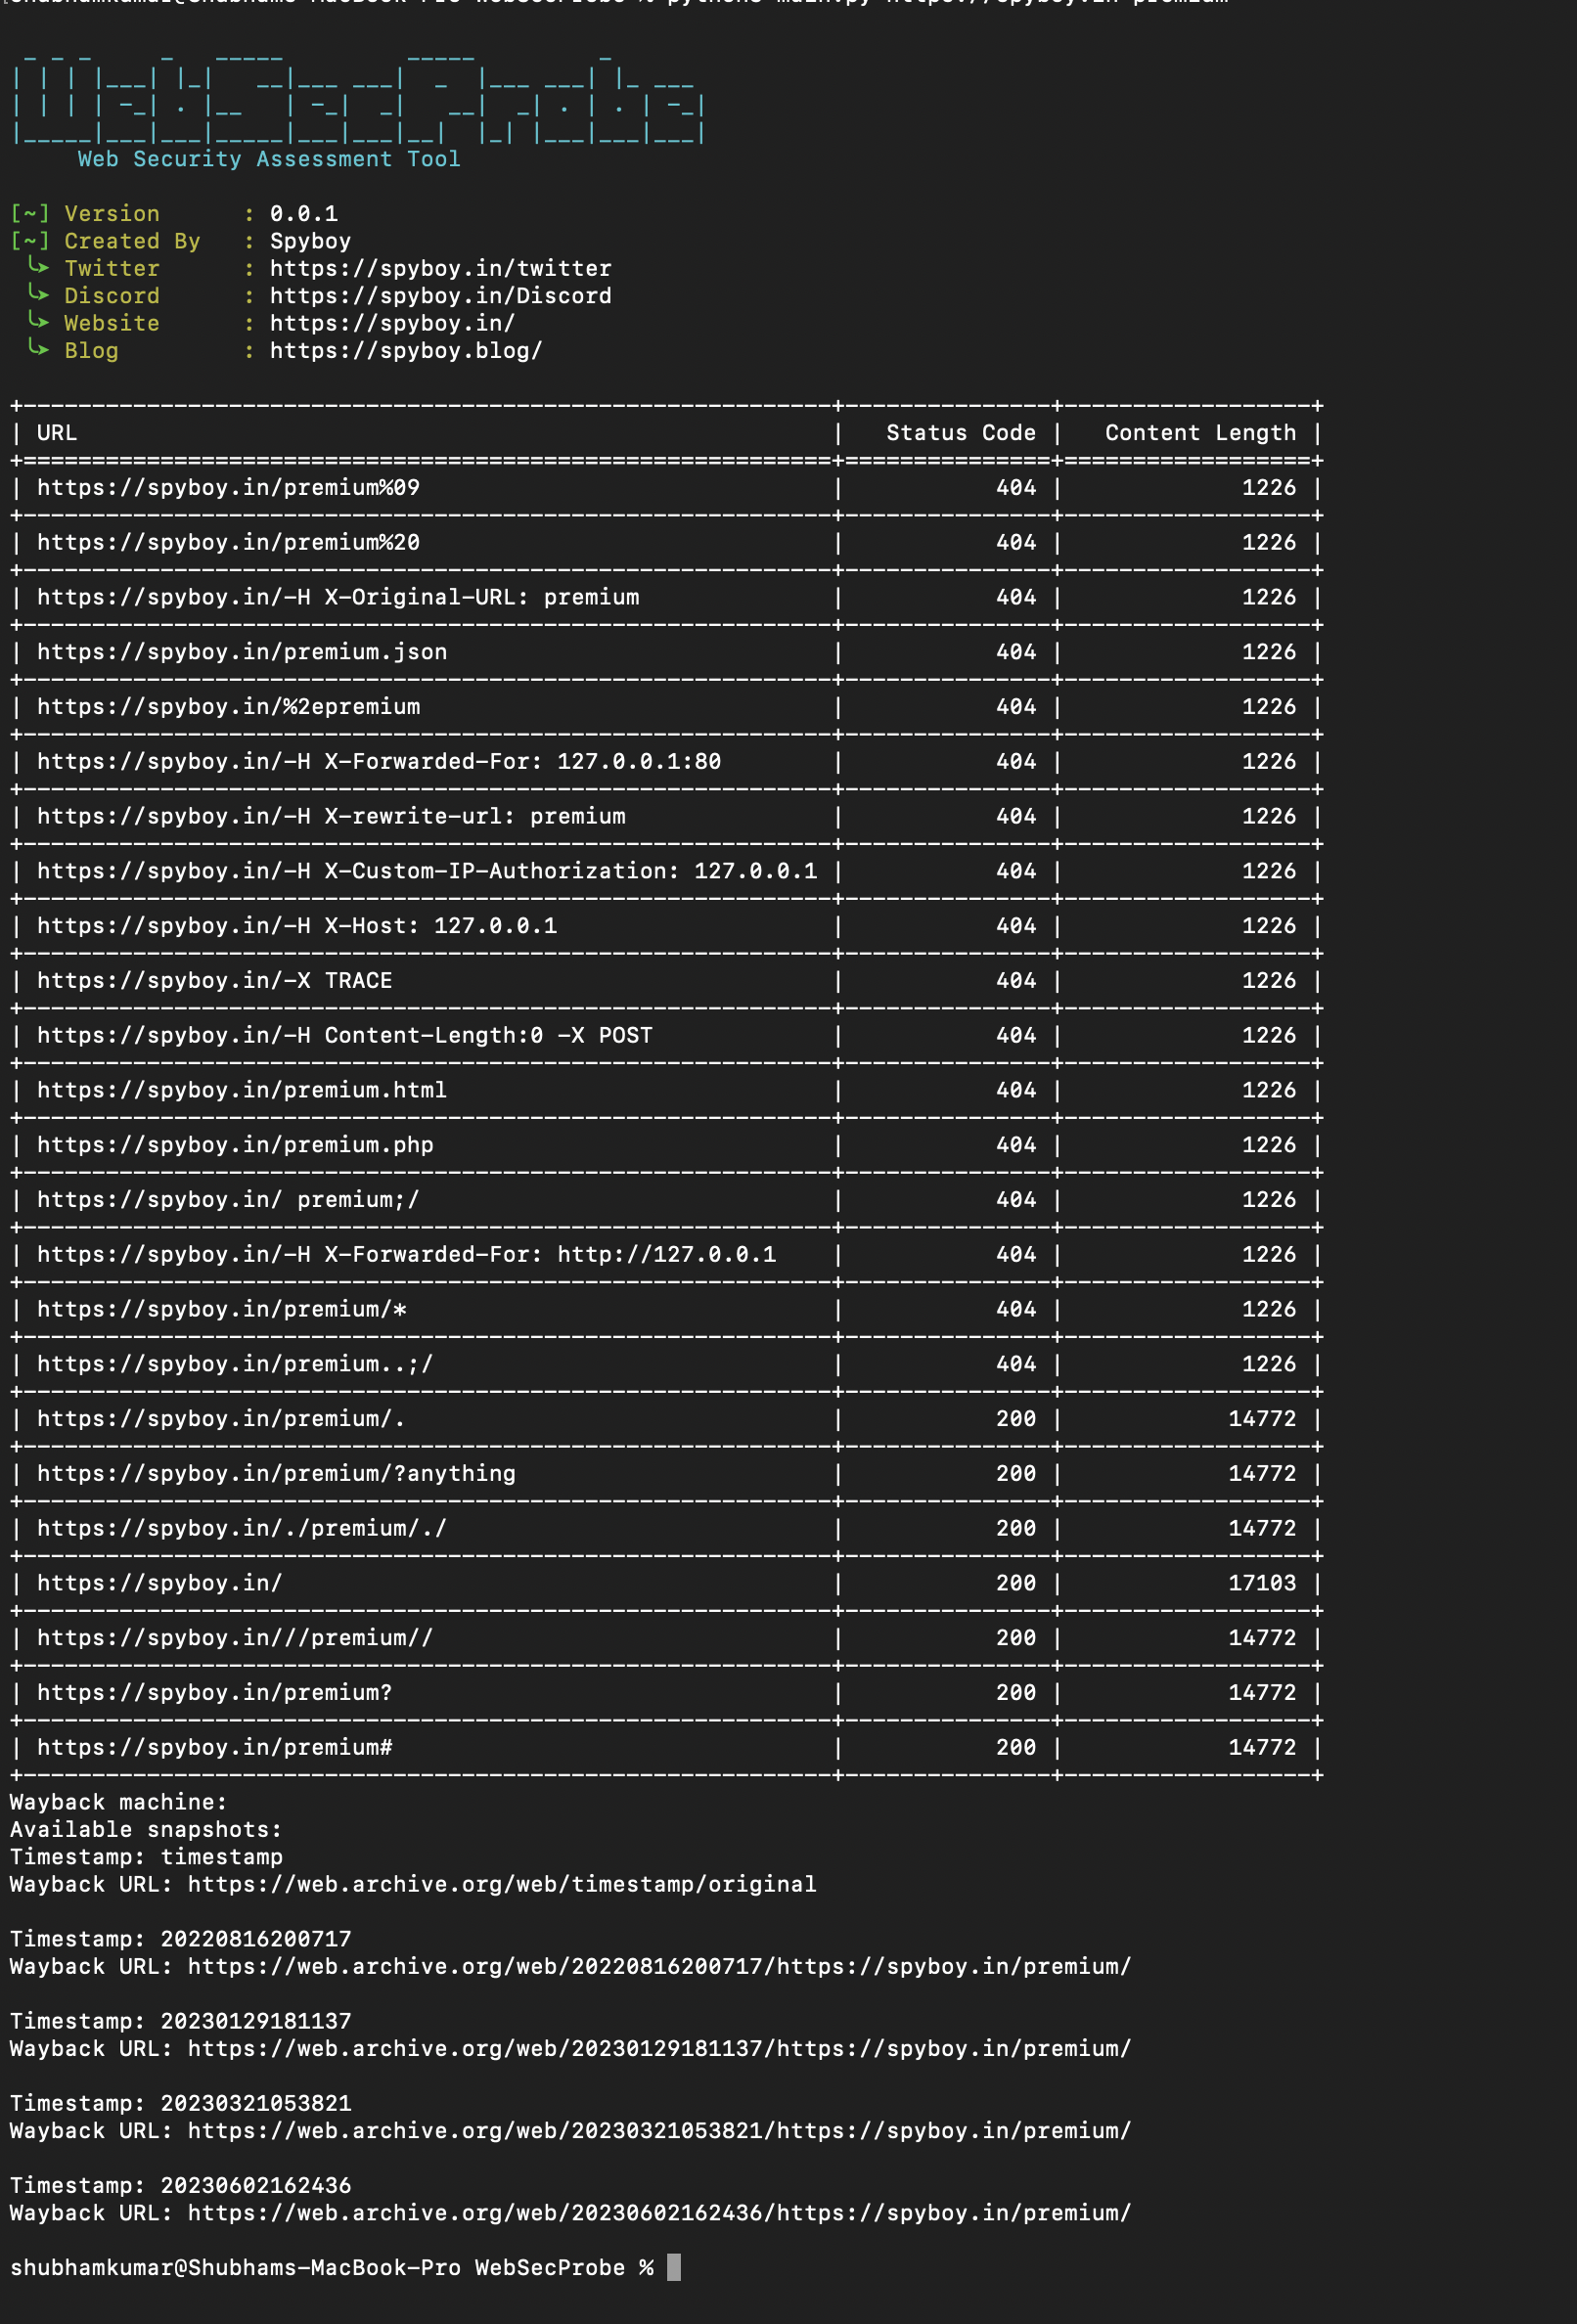 spyboy-productions/websecprobe
Security testing tool for analyzing HTTP 403 responses and identifying access control misconfigurations in web applications.
 yousseflahouifi/dbdtct
Python-based scanner that detects debug mode misconfigurations in web applications using multiple HTTP methods and fingerprinting techniques to…
 raffaele-forte/climber
Check UNIX/Linux systems for privilege escalation
 lc/theftfuzzer
TheftFuzzer is a tool that fuzzes Cross-Origin Resource Sharing implementations for common misconfigurations.
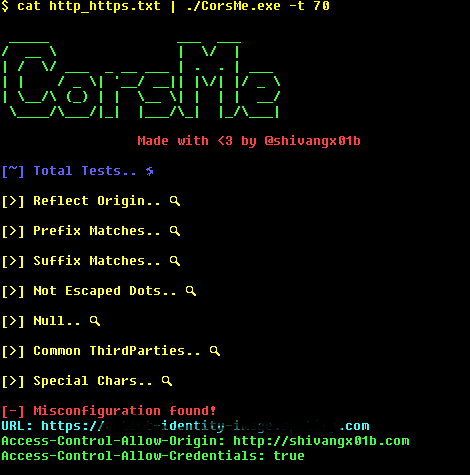 shivangx01b/corsme
Cross Origin Resource Sharing MisConfiguration Scanner
 nixwizard/kube-alien
Automated Kubernetes cluster penetration testing tool that exploits misconfigurations in API, Kubelet, etcd, and Dashboard to achieve node takeover…
 name/log4j-remediation
Discover and remediate Log4Shell vulnerability [CVE-2021-45105]