
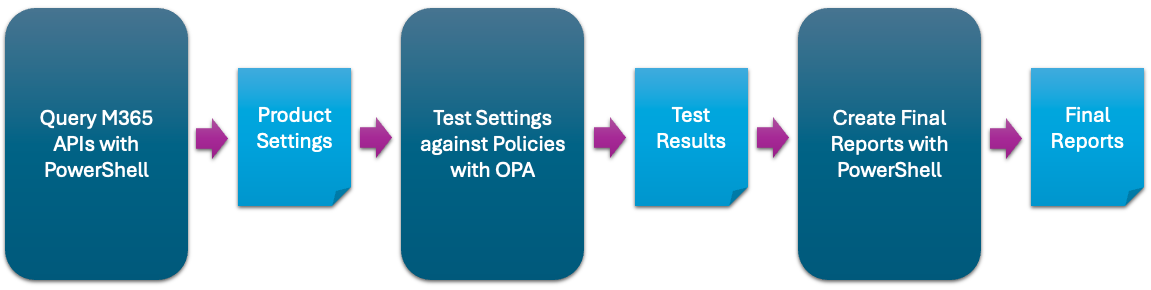
ScubaGear
 cisagov/scubagear
Automation to assess the state of your M365 tenant against CISA's baselines
cloud-securityconfiguration-auditingdefensive-tools+3
cisagov/scubagearAutomation to assess the state of your M365 tenant against CISA's baselines
 0x6d69636b/windows_hardening
HardeningKitty and Windows Hardening Settings
 evotecit/gpozaurr
Group Policy Eater is a PowerShell module that aims to gather information about Group Policies but also allows fixing issues that you may find in…
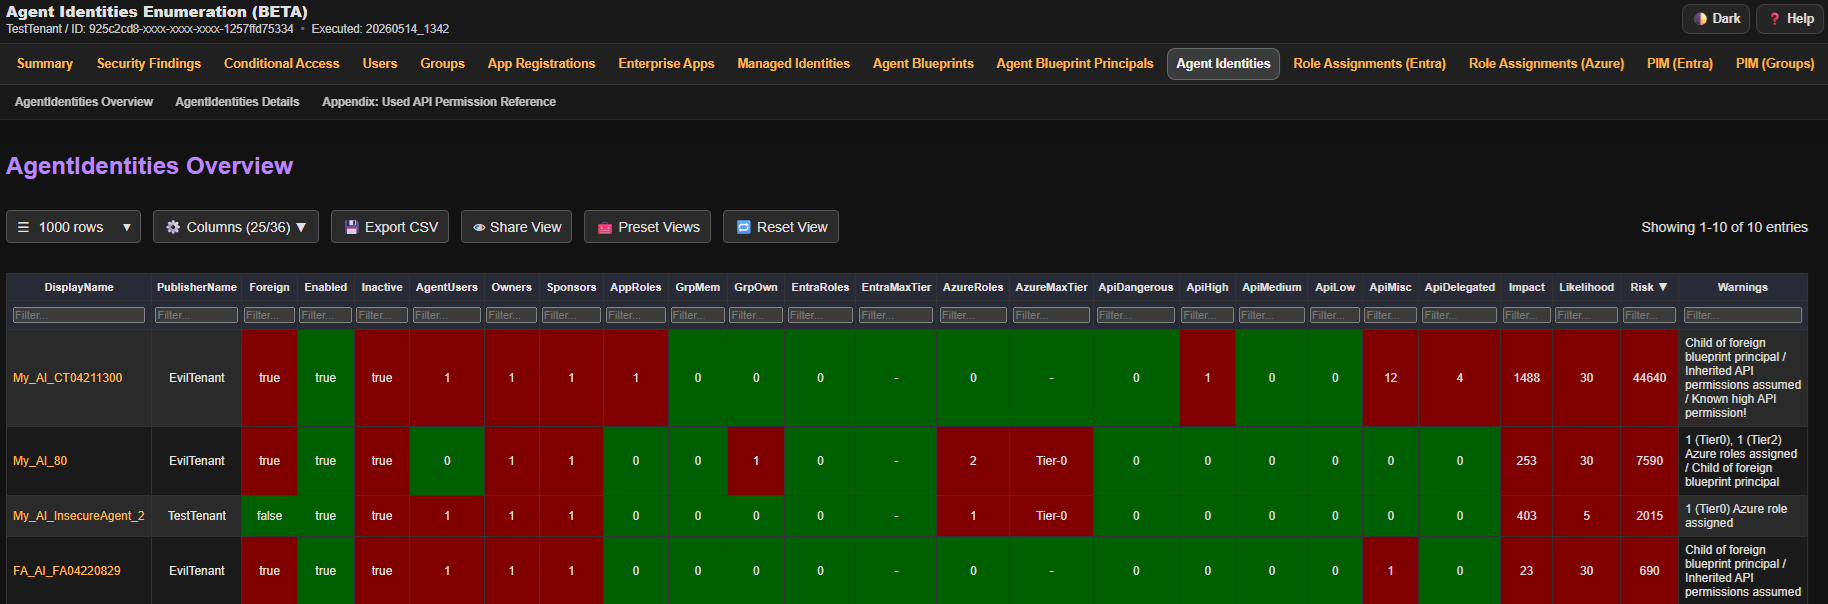 compasssecurity/entrafalcon
A lightweight PowerShell tool for assessing the security posture of Microsoft Entra ID environments. It helps identify privileged objects, risky…
 mandiant/mandiant-azure-ad-investigator
Read-only PowerShell module for detecting UNC2452 and other threat actor artifacts in Azure AD, auditing federated domains, service principals,…
 scipag/hardeningkitty
HardeningKitty - Checks and hardens your Windows configuration
 infiniroot/nginx-mitigate-log4shell
Mitigate log4shell (CVE-2021-44228) vulnerability attacks using Nginx LUA script
 eh-amish/windows-defender-security-auditor-cve-2026-50656-
Read-only PowerShell security auditor for Windows endpoints and servers: checks Defender configuration, patch status, credentials, persistence,…
 digital-dev/log4j-cve-2021-44228-remediation
This powershell script is intended to be used by anyone looking to remediate the Log4j Vulnerability within their environment. It can target multiple…
 nickvourd/windows-local-privilege-escalation-cookbook
Windows Local Privilege Escalation Cookbook
 jakehildreth/locksmith
A small tool built to find and fix common misconfigurations in Active Directory Certificate Services.
 rootsecdev/microburstsecretshunter
Scans exported Azure domain dumps for plaintext passwords, connection strings, storage keys, and other secrets; generates redacted CSV/HTML reports…
 im007/cve-2023-23397
PowerShell script to detect and remediate CVE-2023-23397 privilege escalation vulnerability in Microsoft Outlook and Exchange environments.
 oukridrig772/-winverifytrust-signature-validation-cve-2013-3900-mitigation
PowerShell script to mitigate CVE-2013-3900 by enabling stricter WinVerifyTrust Authenticode signature validation via registry configuration.
 nitrado/cve-2017-9798
Checks a shared hosting environment for CVE-2017-9798
 davidbr27/cve-2013-3900-remediation-script
PowerShell script to remediate CVE-2013-3900 by enabling certificate padding check via registry hardening on Windows systems.
 almogopp/disable-ipv6-cve-2024-38063-fix
A PowerShell script to temporarily mitigate the CVE-2024-38063 vulnerability by disabling IPv6 on Windows systems. This workaround modifies the…
 lukepasek/log4jjndilookupremove
A simple script to remove Log4J JndiLookup.class from jars in a given directory, to temporarily protect from CVE-2021-45046 and CVE-2021-44228.