

nuclei
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
anti-botapi-securityapi-security-testing+21
31.9k
projectdiscovery/nucleiFast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
 nightwatchcybersecurity/truegaze
Static analysis tool for Android/iOS apps focusing on security issues outside the source code
 firefart/stunner
Test and exploit STUN/TURN servers for misconfigurations, enabling internal network pivoting via SOCKS proxy, memory leak attacks, and internal port…
 cisofy/lynis
Agentless security auditing tool for Linux, macOS, and UNIX systems. Performs in-depth scans for vulnerabilities, configuration issues, and…
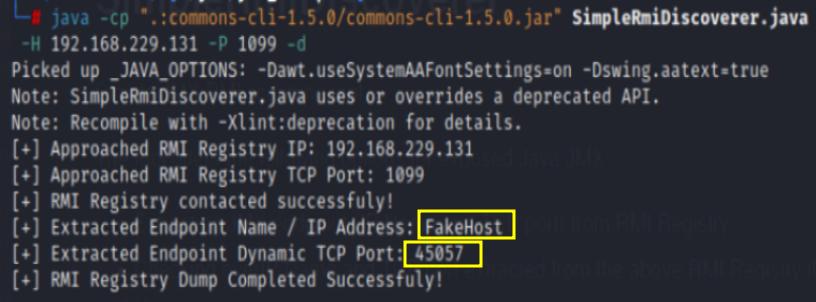 marcin-wolak/simplermidiscoverer
Simple JMX RMI scanning tool
 hahwul/s3reverse
The format of various s3 buckets is convert in one format. for bugbounty and security testing.
 open-policy-agent/opa
Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…
 bunkerity/bunkerweb
🛡️ Open-source and cloud-native Web Application Firewall (WAF)
 open-policy-agent/conftest
Write tests against structured configuration data using the Open Policy Agent Rego query language
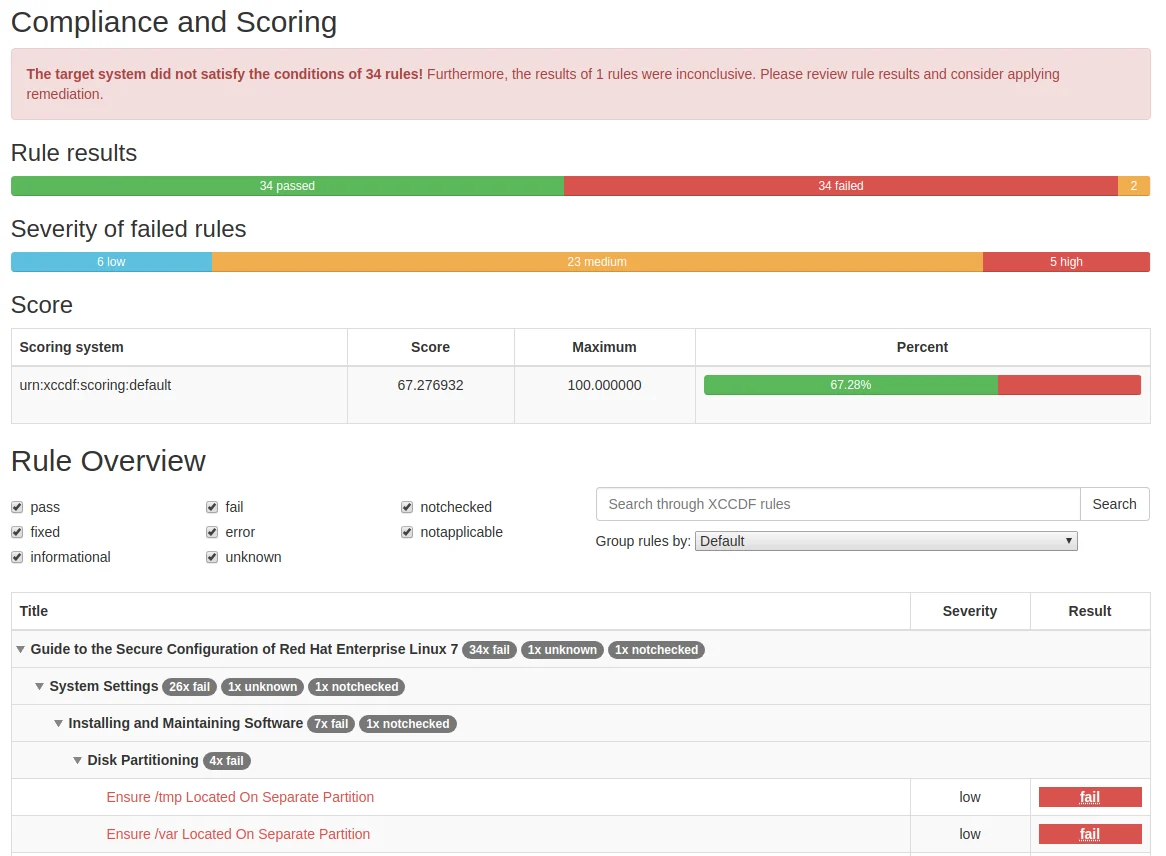 complianceascode/content
Generates SCAP, Ansible, Bash, and CEL security content for compliance evaluation and automated hardening across Linux hosts, containers, and…
 silentchainai/silentchain
AI-powered vulnerability scanner extension for Burp Suite with multi-provider support (Ollama, OpenAI, Claude, Gemini)
 santandersecurityresearch/corsair_scan
Automated CORS misconfiguration scanner that tests Origin header injection, wildcard reflection, and credential leakage across web applications and…
 owasp/openshield
Open source CSPM for Azure - scan for misconfigurations and quantum-unsafe cryptography, map findings to CIS/NIST/ISO27001/SOC2, and fix them with…
 zaydmulani09/sentrymcp
A static + runtime security scanner for MCP (Model Context Protocol) servers
 rolix44/kubestroyer
Go-based Kubernetes exploitation tool that scans for exposed ports and exploits cluster misconfigurations, including anonymous Kubelet RCE and etcd…
 sorami-consulting-au/ai-kubernetes-helm-chart-security
Evidence and data for the Sorami technical report on security defaults of 15 AI serving, vector database and MCP Helm charts on Kubernetes.
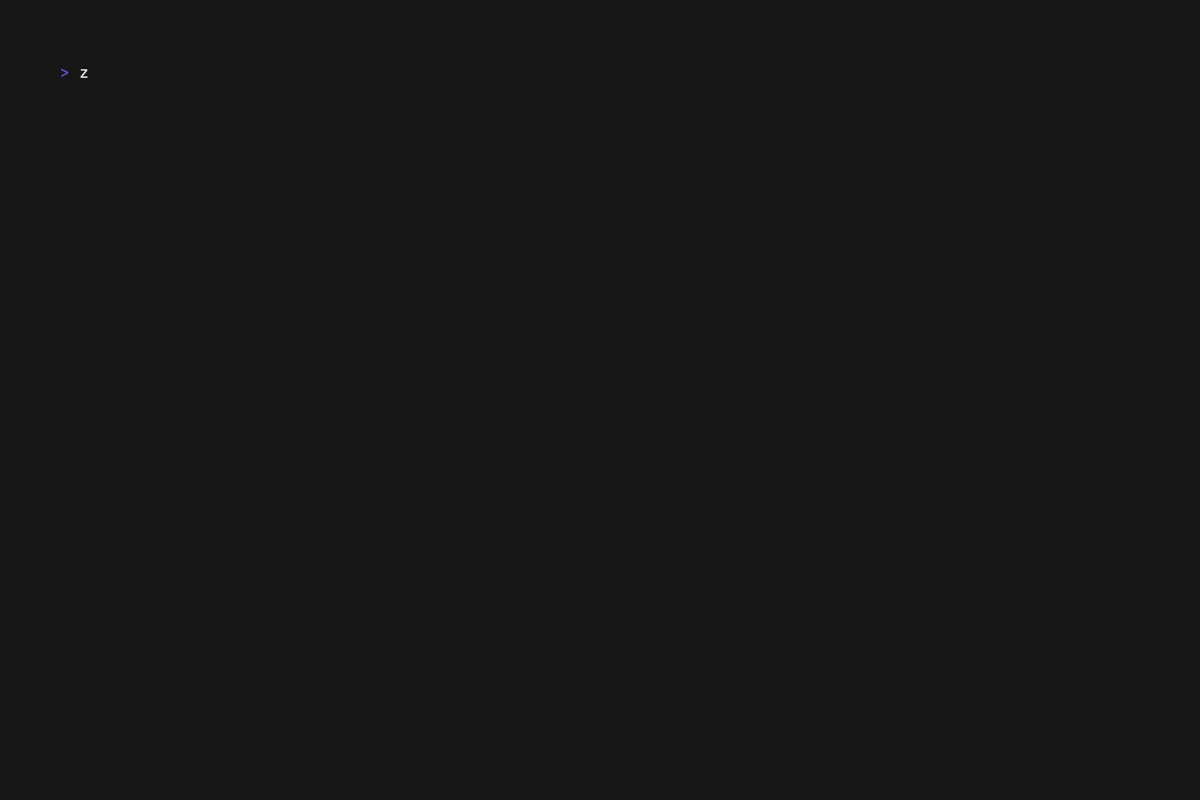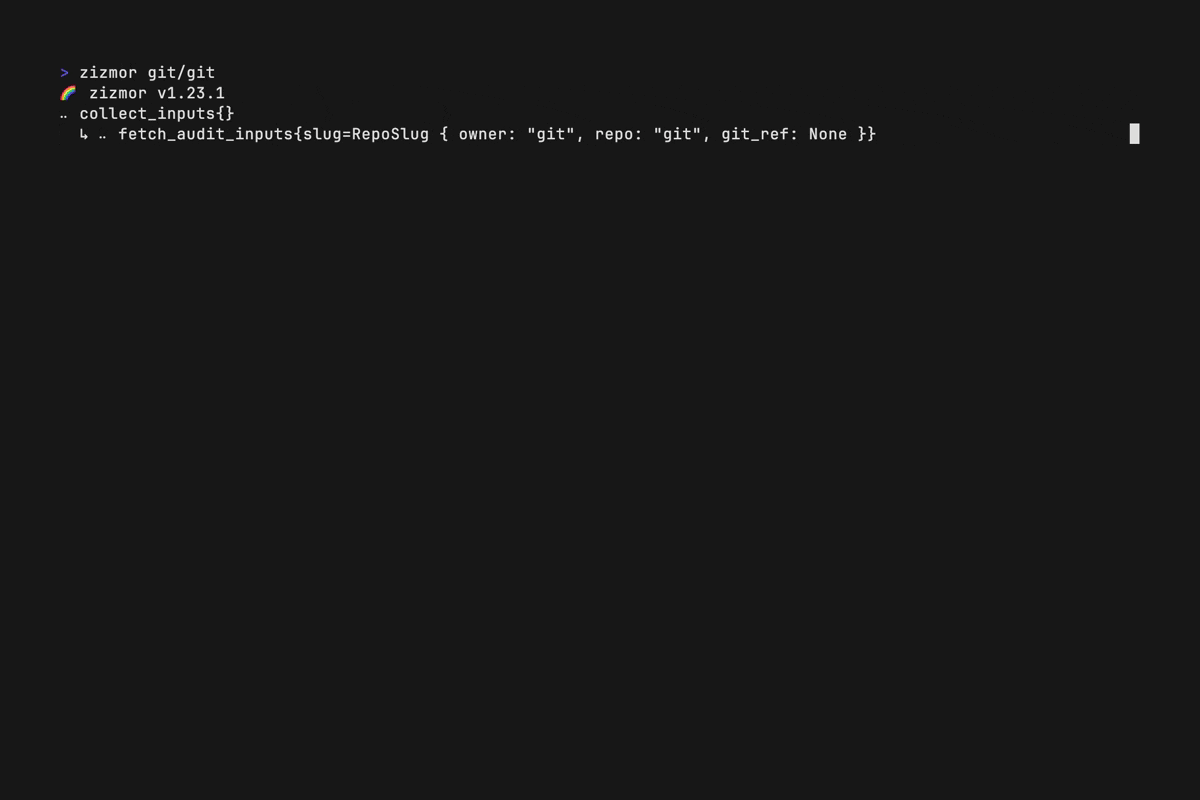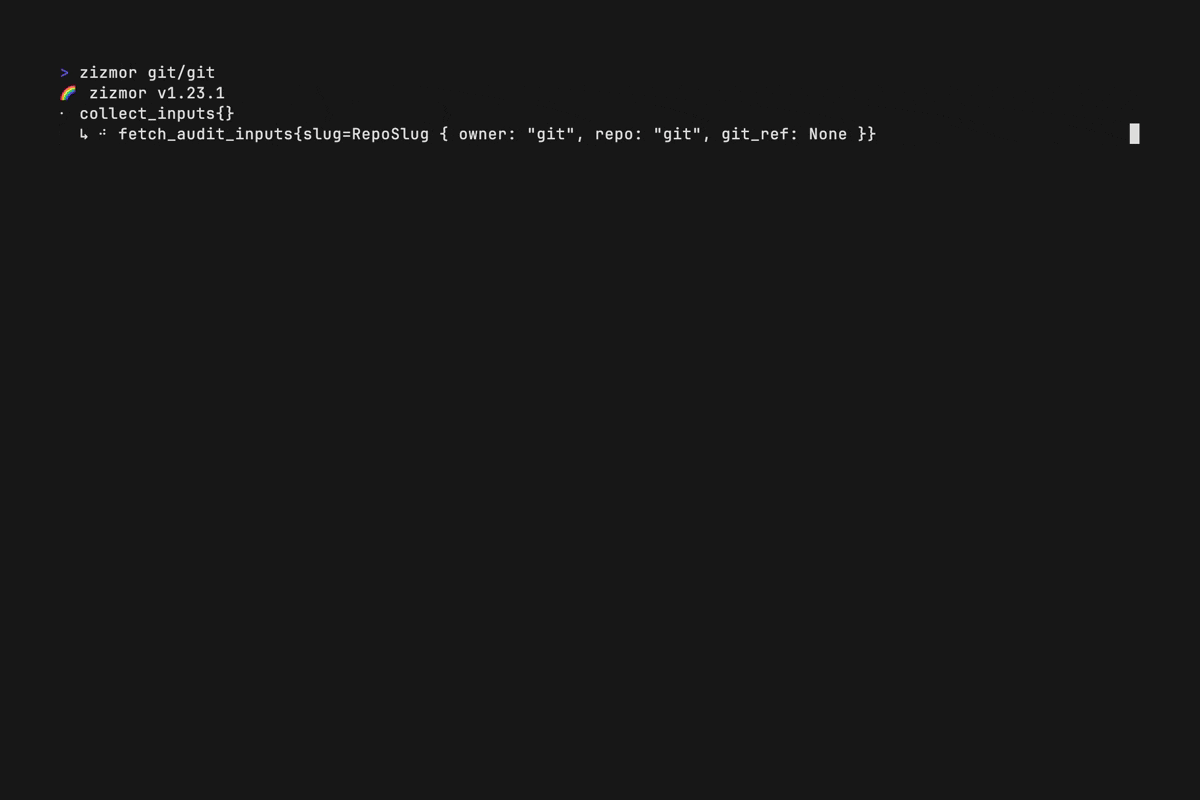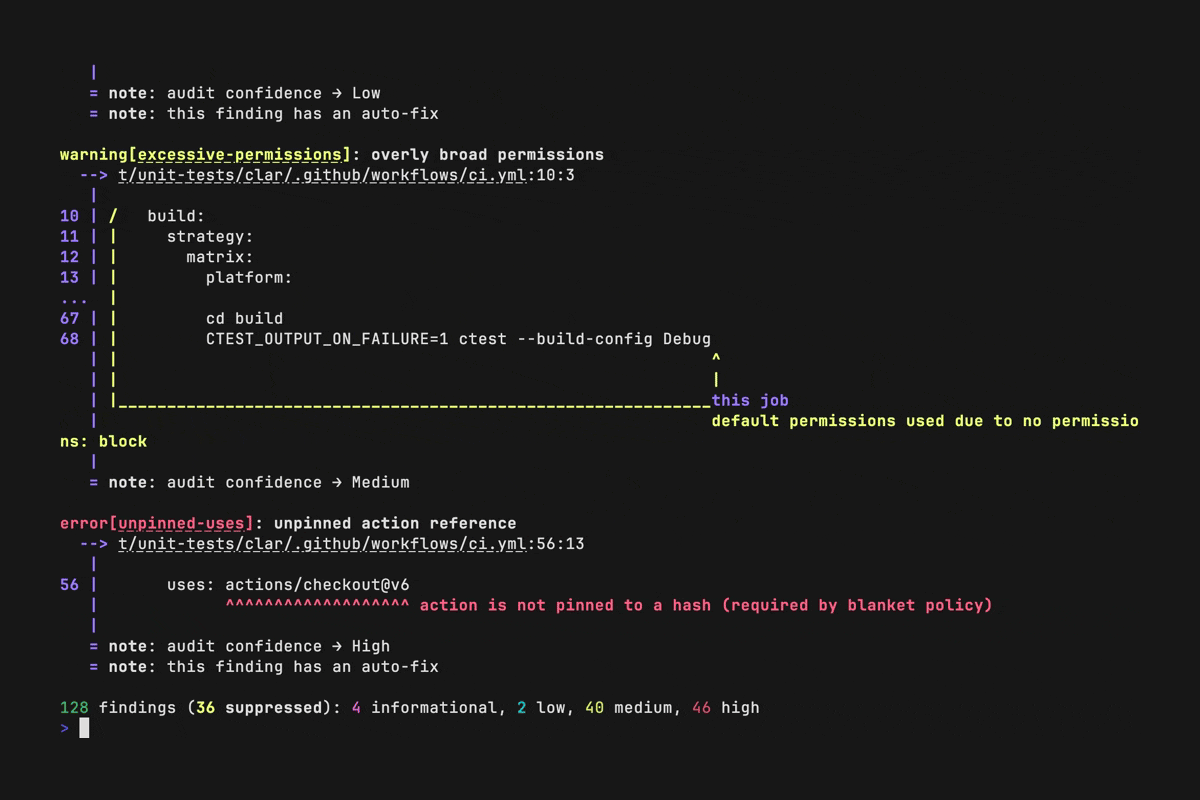 zizmorcore/zizmor
Static analysis tool for CI/CD systems that detects and fixes security issues in GitHub Actions, Dependabot, and pre-commit configurations, including…
 qianlijaingshan/milvus-auth-audit
Milvus 认证安全检测脚本:CVE-2025-64513 (sourceid后门) / CVE-2026-26190 (/expr弱token) / 内部端口53100