
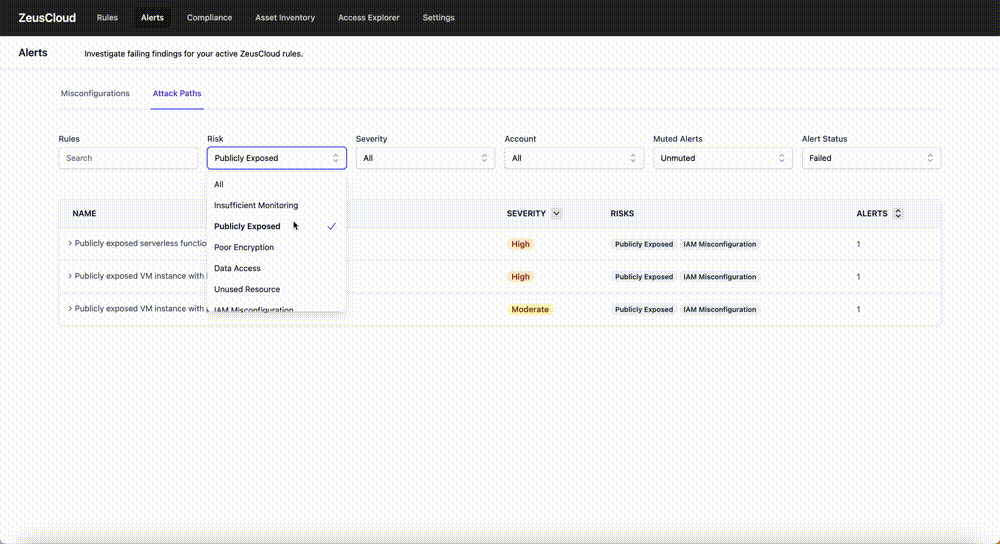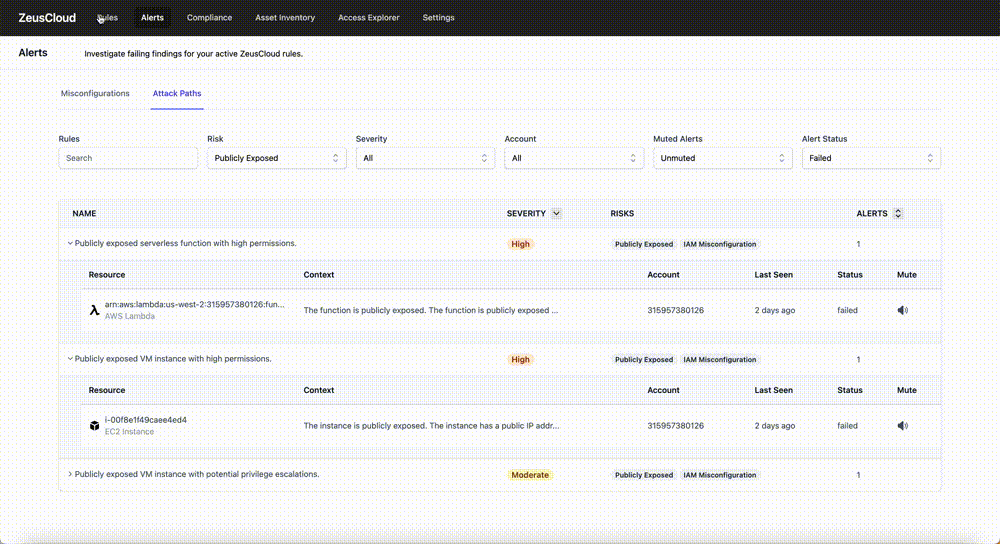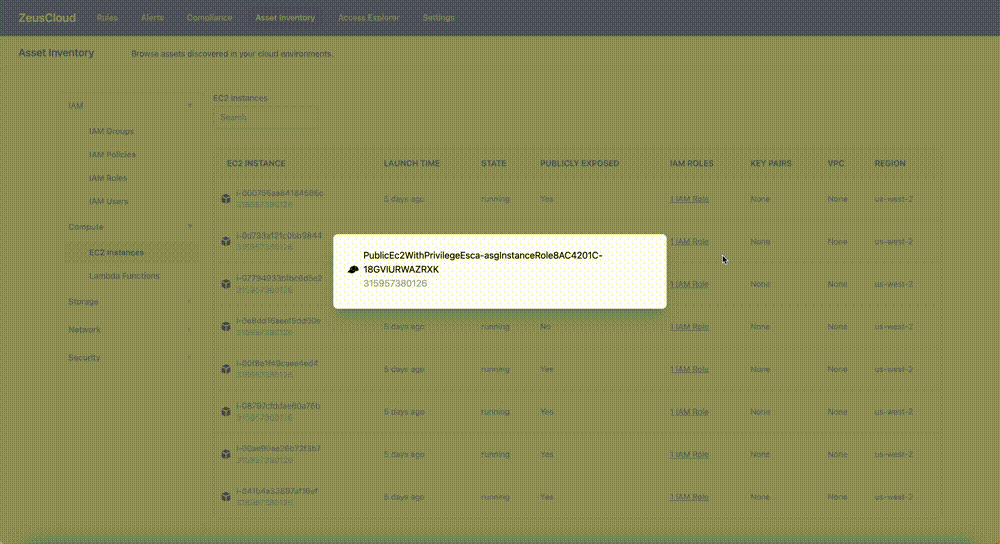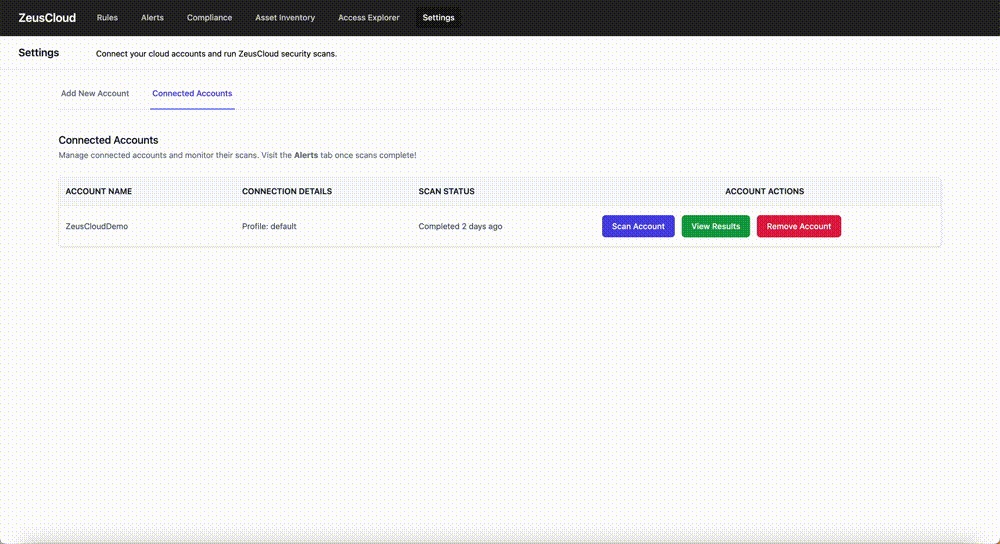
ZeusCloud
 zeus-labs/zeuscloud
Open-source cloud security platform that discovers attack paths, identifies misconfigurations, visualizes IAM access, and provides step-by-step…
cloud-infrastructure-securitycloud-securityconfiguration-auditing+2
733
zeus-labs/zeuscloudOpen-source cloud security platform that discovers attack paths, identifies misconfigurations, visualizes IAM access, and provides step-by-step…
 secuproject/adenum
AD Enum is a pentesting tool that allows to find misconfiguration through the the protocol LDAP and exploit some of those weaknesses with kerberos.
 nccgroup/scoutsuite
Multi-cloud security auditing tool that leverages cloud provider APIs to gather configuration data, assess security posture, and generate HTML…
 saykino/cve-2026-31283
Documentation of CVE-2026-31283: an email bombing vulnerability in Totara LMS's forgot password API due to missing rate limiting, allowing…
 hardentools/hardentools
Hardentools simply reduces the attack surface on Microsoft Windows computers by disabling low-hanging fruit risky features.
 coreruleset/coreruleset
Generic attack detection rule set for web application firewalls, protecting against OWASP Top Ten and common vulnerabilities with minimal false…
 corazawaf/coraza
Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
 subat0mik/misconfiguration-manager
Misconfiguration Manager is a central knowledge base for all known Microsoft Configuration Manager tradecraft and associated defensive and hardening…
 mandiant/azure_workshop
Terraform-deployable vulnerable-by-design Azure lab with realistic attack paths and common misconfigurations for practicing red teaming and security…
 praetorian-inc/trajan
A multi-platform CI/CD vulnerability detection and attack automation tool for identifying security weaknesses in pipeline configurations.
 moniik/poc_salesforce_lightning
Academic purposes only. Attack against Salesforce lightning with guest privilege.
 owasp/owasp-subtractive-hardening-top-10
The OWASP Subtractive Security Top 10 Project is an initiative to identify, document, and promote the highest-impact opportunities for reducing cyber…
 george0papasotiriou/cve-2026-5556-kubernetes-admission-controller-bypass-via-case-sensitivity
Exploit PoC and vulnerable admission webhook for CVE-2026-5556, demonstrating Kubernetes admission controller bypass via case-sensitive pod name…
 mthamil107/db_audit_research
Self-Defeating Audits: reproducible lab showing a low-privilege PostgreSQL role reversibly blinding a trigger-based auditor + poisoning attribution…
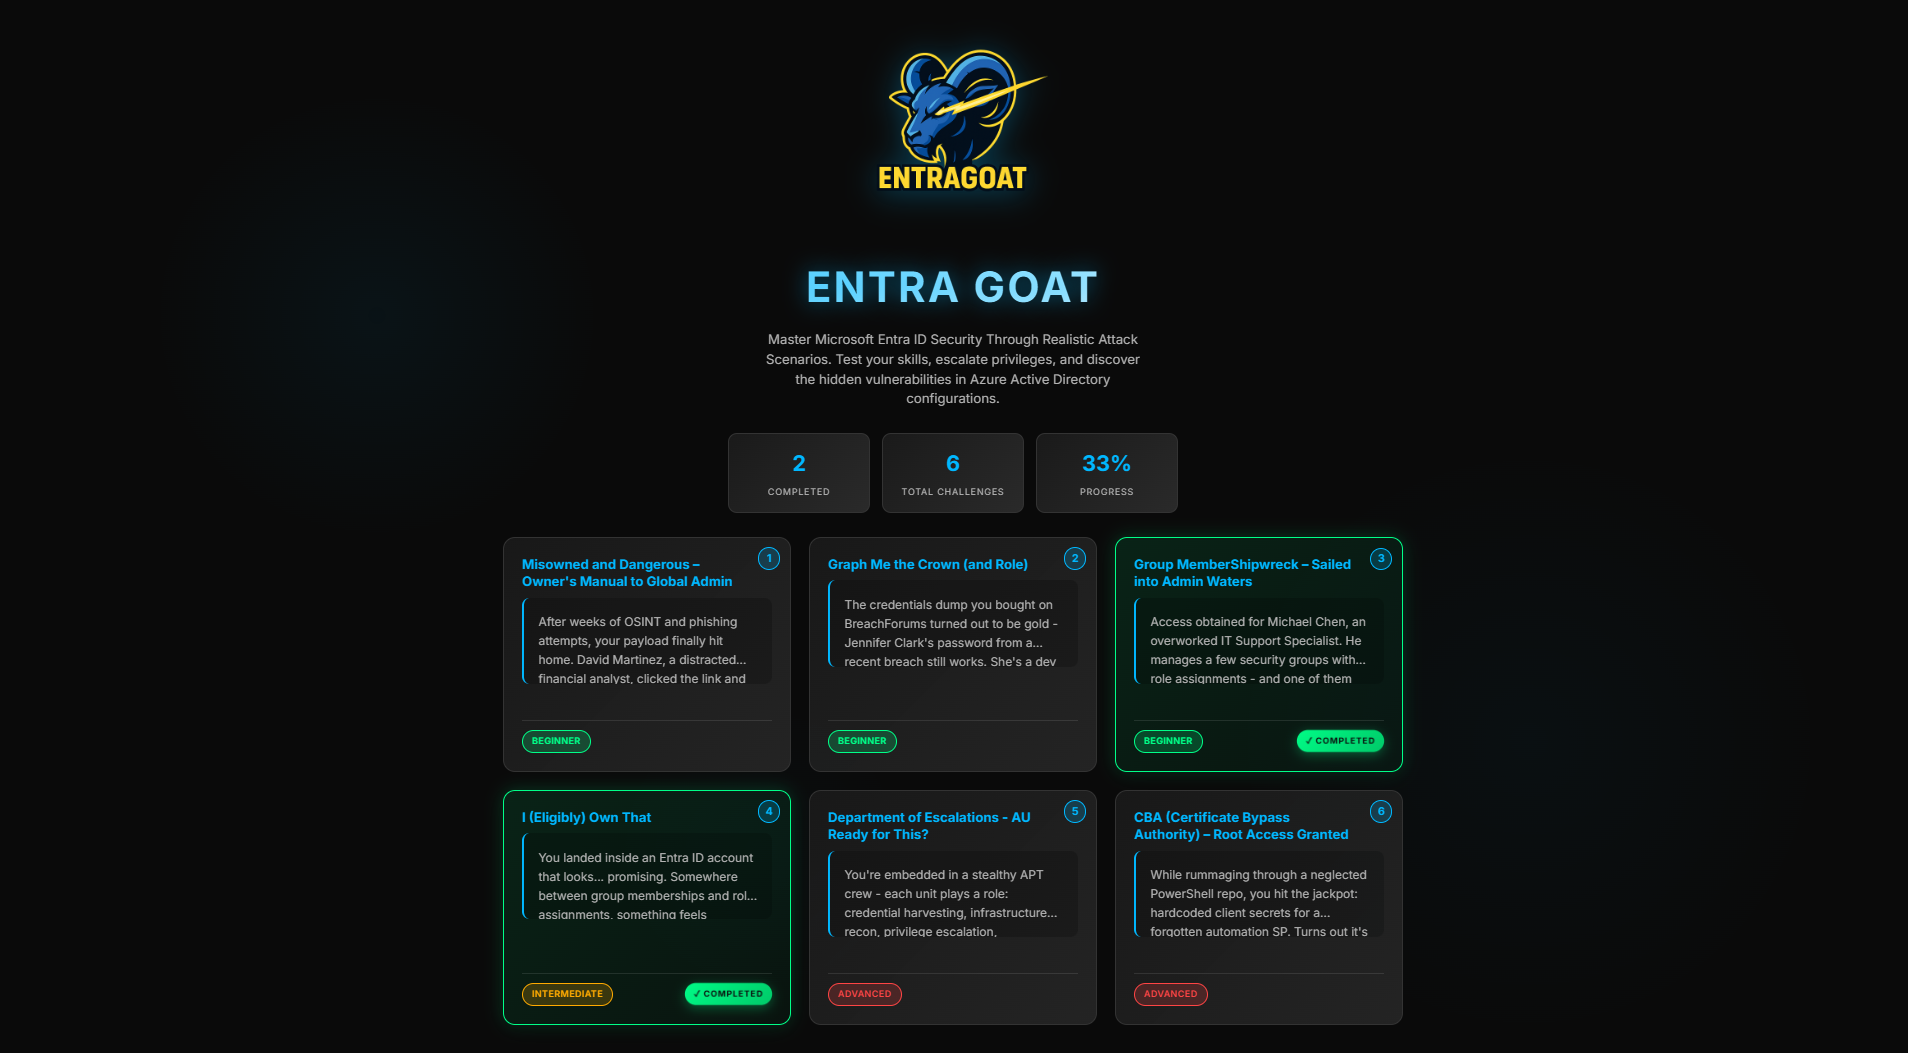 semperis/entragoat
A deliberately vulnerable Microsoft Entra ID environment. Learn identity security through hands-on, realistic attack challenges.
 xmcyber/xmgoat
Terraform-based Azure security lab with intentionally misconfigured environments for hands-on attack and compromise practice. Includes scenario flows…
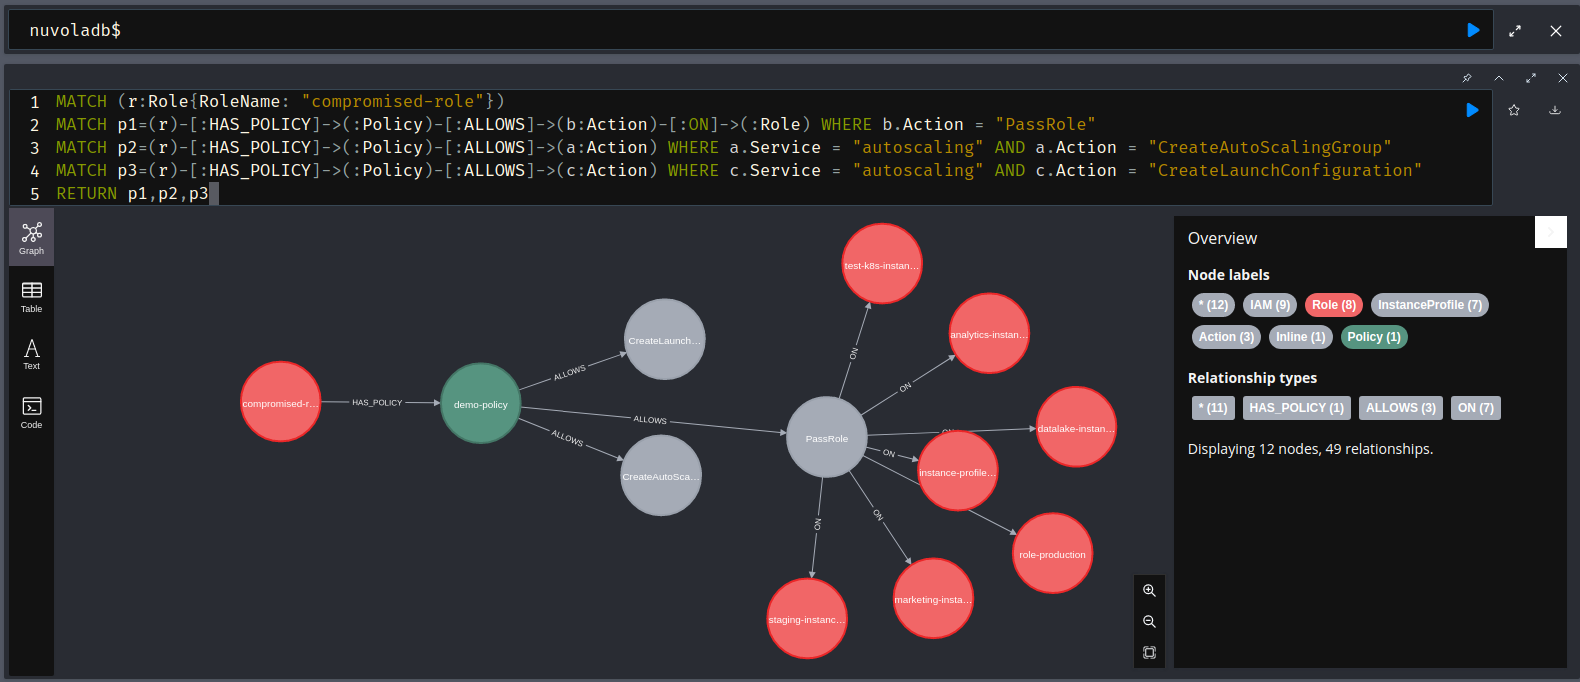 primait/nuvola
Graph-based AWS security analysis tool that dumps cloud configurations, detects misconfigurations, and maps attack paths using a Neo4j digital twin…
 fdzdev/cve-2024-50964
Documentation of CVE-2024-50964: critical DMARC policy bypass in DonWeb MX server allowing email spoofing, with low attack complexity and no required…