

nuclei
 projectdiscovery/nuclei
Fast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
anti-botapi-securityapi-security-testing+21
32.2k
projectdiscovery/nucleiFast YAML-based vulnerability scanner with template-driven detection engine for automated security testing across web apps, APIs, networks, DNS, and…
 kyverno/kyverno
Enforce security and compliance on Kubernetes clusters via admission controls, resource mutation, background scans, and container image signature…
 cloud-custodian/cloud-custodian
Rules engine for cloud security, cost optimization, and governance, DSL in yaml for policies to query, filter, and take actions on resources
 vulnz/sast
Free offline SAST engine for CI/CD: AST and cross-file taint analysis, secret detection with live validation, SCA/CVE, IaC misconfiguration, and…
 open-policy-agent/opa
Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…
 fairwindsops/polaris
Validation of best practices in your Kubernetes clusters
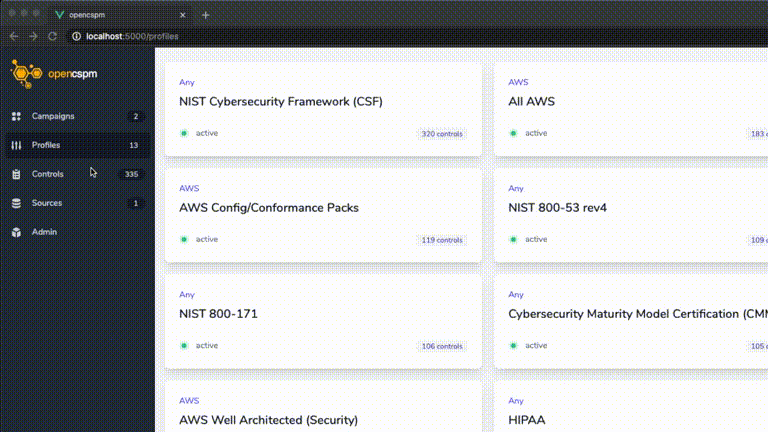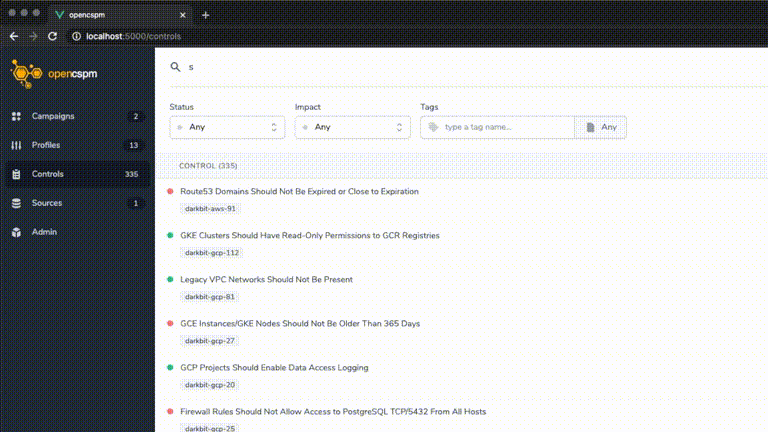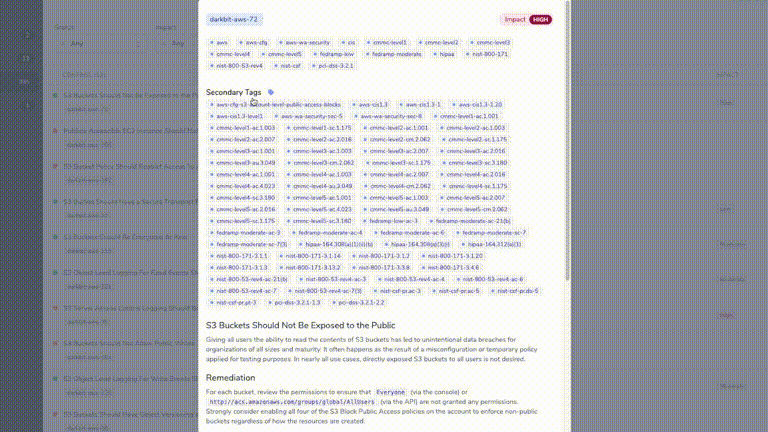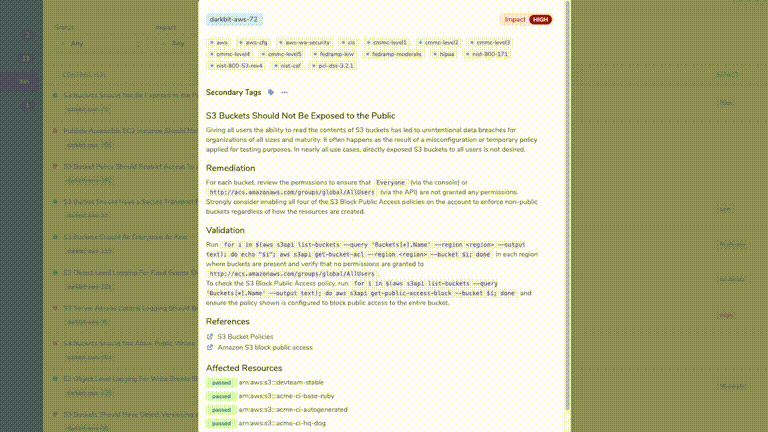 opencspm/opencspm
Open Cloud Security Posture Management Engine
 open-policy-agent/gatekeeper
Kubernetes policy engine with OPA-based admission control, mutation, and audit for enforcing security and compliance configurations.
 foxvr-sudo/bug-bounty-arsenal-v.3
Full-stack platform for authorized web application security scanning with a detector-based engine, async Celery workers, and a React dashboard for…
 zenzue/cve-2025-9074
Proof-of-concept exploit for CVE-2025-9074 demonstrating container-to-host file write via exposed Docker Engine API on Windows. For authorized…
 smaranchand/bucky
Bucky (An automatic S3 bucket discovery tool)
 niandy/nginx-patch
nginx 1.15.10 patch against cve-2021-23017 (ingress version)
 califio/ngxray
ngxray — nginx config security scanner
 k8scout/k8scout
Drop a single binary into a compromised Kubernetes pod and instantly map every realistic attack path to cluster-admin, node escape, secret theft,…