
Archived
rip_raw
 cado-security/rip_raw
Rip Raw is a small tool to analyse the memory of compromised Linux systems.
data-recoverydigital-forensicsforensics+3
 yezzfusl/cve_2023_38831_scanner
This Python application scans for the CVE-2023-38831 vulnerability in WinRAR.
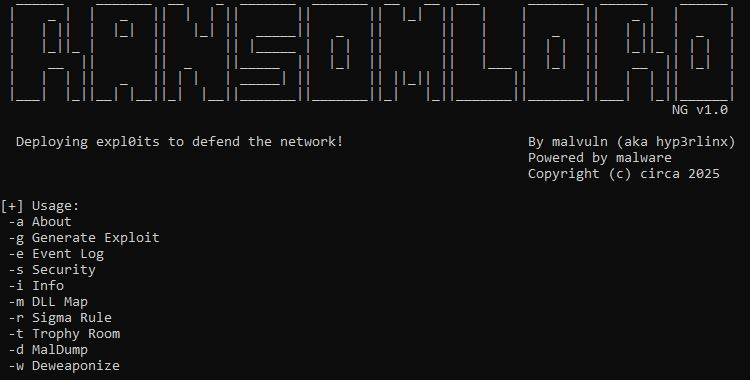 malvuln/ransomlord
RansomLord is a proof-of-concept Anti-Ransomware exploitation tool that automates the creation of PE files, used to compromise ransomware…
 offensive-panda/lsassreflectdumping
This tool leverages the Process Forking technique using the RtlCreateProcessReflection API to clone the lsass.exe process. Once the clone is created,…
 codewhitesec/handlekatz
PIC-based Lsass memory dumper using cloned handles to evade detection, producing obfuscated dumps with minimal memory footprint for red team…
 hasherezade/pe-sieve
Scans a given process. Recognizes and dumps a variety of potentially malicious implants (replaced/injected PEs, shellcodes, hooks, in-memory patches).
 v31l0x1/throttlestopppl
Poc for CVE-2025-7771 to modify PPL Protection
 viralmaniar/remote-desktop-caching-
This tool allows one to recover old RDP (mstsc) session information in the form of broken PNG files. These PNG files allows Red Team member to…
 travisfoley/dfirtriage
Digital forensic acquisition tool for Windows based incident response.
 securityjoes/forensicminer
A really good DFIR automation for collecting and analyzing evidence designed for cybersecurity professionals.
 forrest-orr/moneta
Moneta is a live usermode memory analysis tool for Windows with the capability to detect malware IOCs
 fortra/nanodump
The swiss army knife of LSASS dumping
 orlyjamie/mimikittenz
A post-exploitation powershell tool for extracting juicy info from memory.
 ivan-sincek/invoker
Penetration testing utility and antivirus assessment tool.
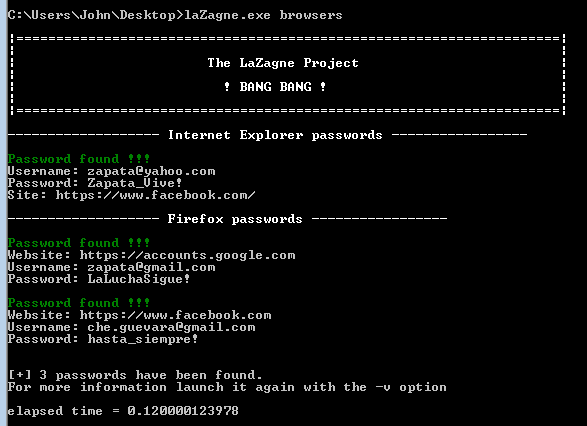 alessandroz/lazagne
Cross-platform credential recovery tool that extracts stored passwords from browsers, email clients, databases, system mechanisms, and network…
 naksyn/moduleshifting
Stealthier variation of Module Stomping and Module Overloading injection techniques that reduces memory IoCs. Implemented in Python ctypes
 hullabrian/eventhorizon
Tool that gathers a customizable set of ETW telemetry and generates user-defined detections