frida-il2cpp-datacollector

Frida-based tool that ports Cheat Engine's MonoDataCollector to Android and iOS, enabling runtime Mono/IL2CPP data collection and memory inspection…

Frida-based tool that ports Cheat Engine's MonoDataCollector to Android and iOS, enabling runtime Mono/IL2CPP data collection and memory inspection…

Python-based memory shell injection tool for CVE-2022-22947, supporting Spring, Netty, and Godzilla memory shells with simple CLI usage.

SALT - SLUB ALlocator Tracer for the Linux kernel

Portable, dependency-free incident response tool that automates forensic artifact collection from Unix-like systems, including memory acquisition,…

Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…

Windows tool for dumping malware PE files from memory back to disk for analysis.

memory search and patch tool on debuggable apk without root & ndk

Main repository to pull all NCC Group Cisco ASA-related tool projects.

Tool to make in memory man in the middle

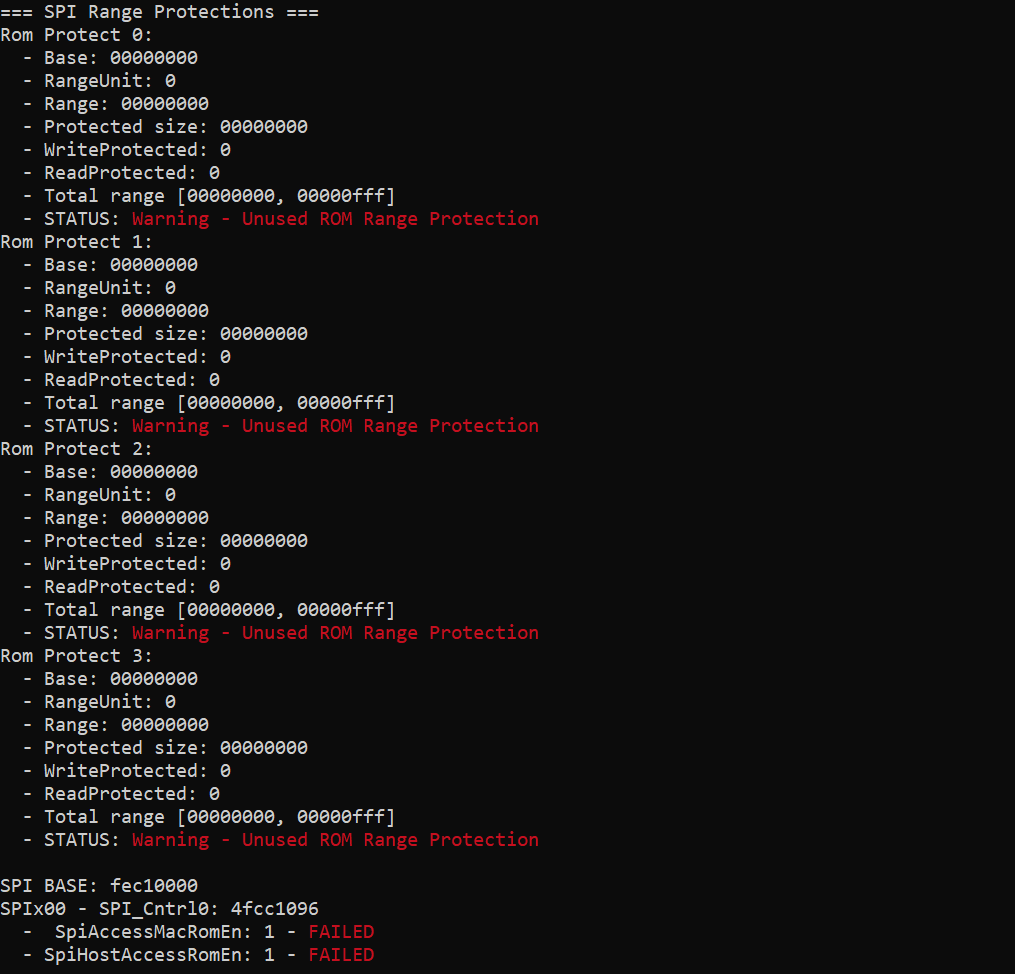
Platform security assessment tool for dumping and analyzing UEFI/SMM registers, PCI config space, physical memory, SPI flash, and S3 bootscripts with…

A generic game/software hacking tool written from the ground up in Rust.

Memory modification tool for re-signed ipa supports iOS apps running on iPhone and Apple Silicon Mac without jailbreaking.

In-memory stealth detection tool that identifies process hollowing, module stomping, unbacked executable regions, and anomalous CONTEXT structures…

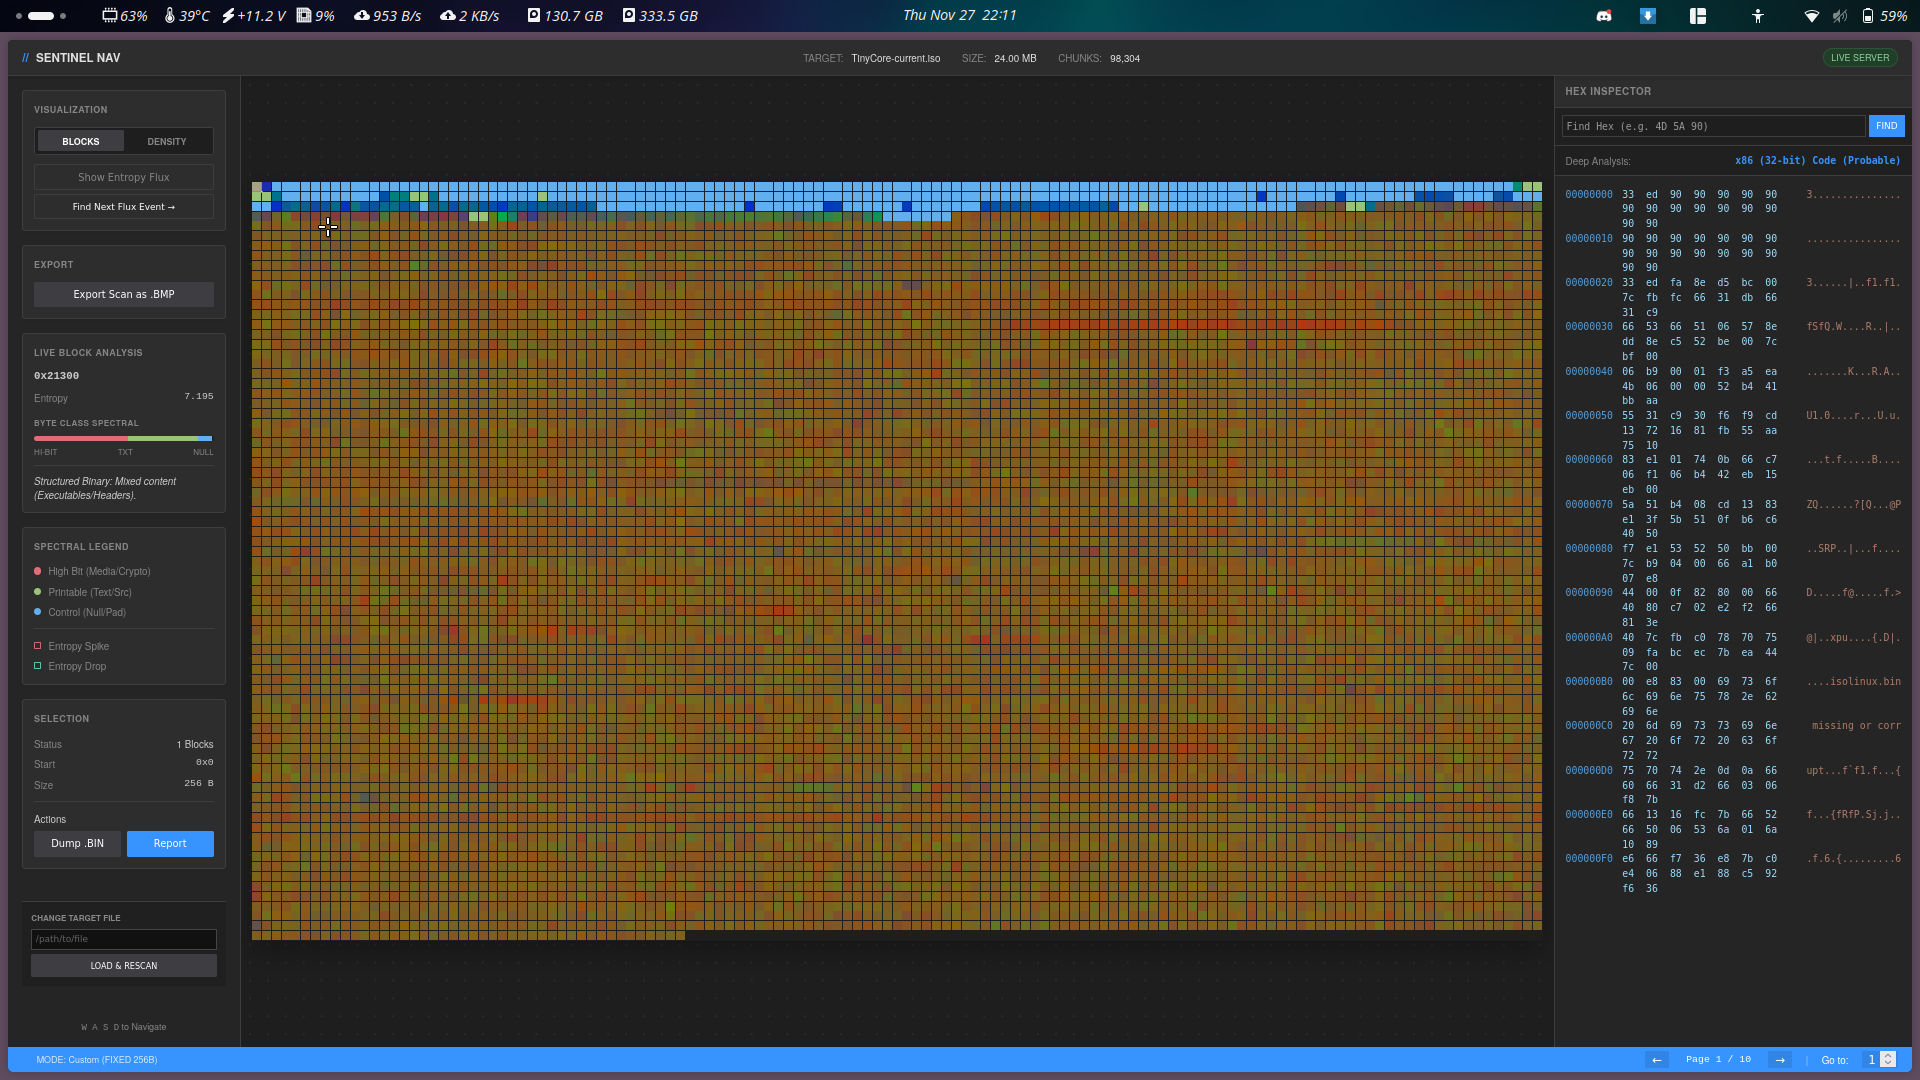
SentinelNav: zero-dependency, pure Python binary visualization and forensics tool.

Live memory analysis tool for detecting reflectively loaded .NET DLLs by scanning process memory regions for abnormal flags, page types, and PE…

Windows memory-forensics and threat hunting tool that scans live process memory for malicious patterns, injection techniques, and reflectively loaded…

ML-assisted forensic analysis tool that automates memory, disk, and live system triage on Windows using Volatility 3, autorunsc, and sigcheck to…

Interrogate is a proof-of-concept tool for identification of cryptographic keys in binary material (regardless of target operating system), first and…