Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
75 results
watchTowr-vs-Netscaler-CVE-2026-8451 preview

watchTowr-vs-Netscaler-CVE-2026-8451

GitHubwatchtowrlabs/watchtowr-vs-netscaler-cve-2026-8451

Python exploit tool for CVE-2026-8451 Citrix Netscaler memory overread vulnerability. Generates detection artifacts by leaking memory from target…

exploitationinformation-gatheringmemory-forensics+3
13
3 months ago
CVE-2021-46702 preview

CVE-2021-46702

GitHubexmak-s/cve-2021-46702

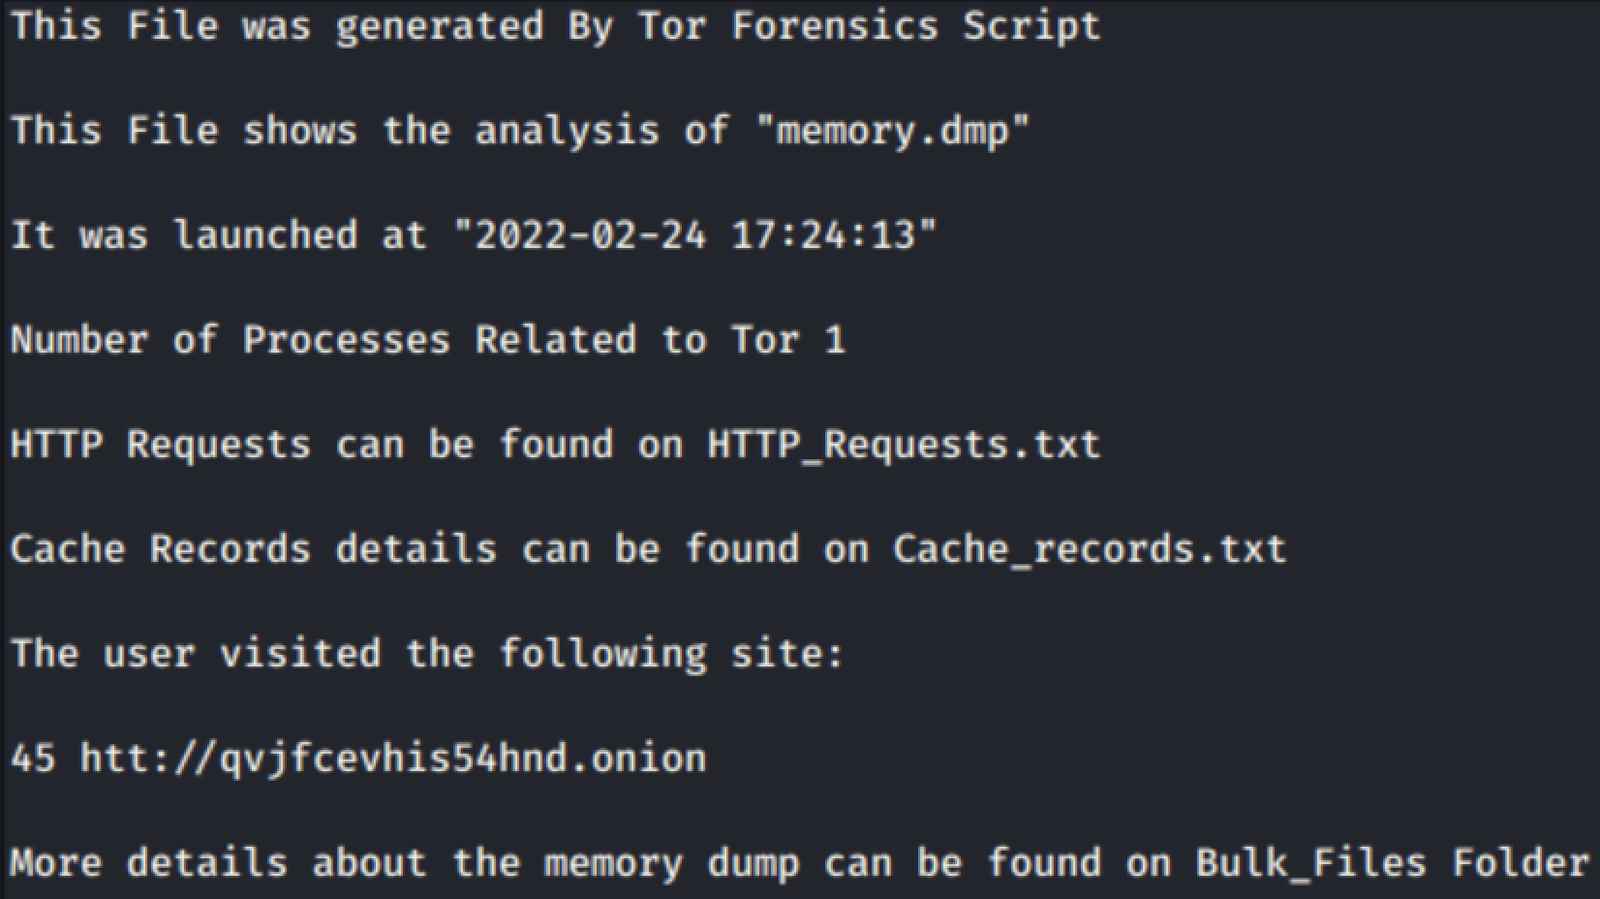
Proof-of-concept script that analyzes Windows memory dumps to recover visited Tor onion services, bypassing Tor Browser's anonymity by exploiting…

digital-forensicsexploitationinformation-gathering+2
64 years ago
memgrep preview

memgrep

GitHubnccgroup/memgrep

Memory searching utilities

binary-analysisdigital-forensicsforensics+3
4412 years ago
CVE-2016-6415-BenignCertain-Monitor preview

CVE-2016-6415-BenignCertain-Monitor

GitHub3ndg4me/cve-2016-6415-benigncertain-monitor

Re-implementation of VirtueSecurity's benigncertain-monitor

exploitationinformation-gatheringmemory-forensics+3
115 years ago
IPED preview

IPED

GitHubsepinf-inc/iped

IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…

data-recoverydigital-forensicsdisk-forensics+9
3.0k3 days ago
dissect preview

dissect

GitHubfox-it/dissect

Dissect is a digital forensics & incident response framework and toolset that allows you to quickly access and analyse forensic artefacts from…

data-recoverydigital-forensicsdisk-forensics+5
1.2k3 days ago
NativeDump preview

NativeDump

GitHubricardojoserf/nativedump

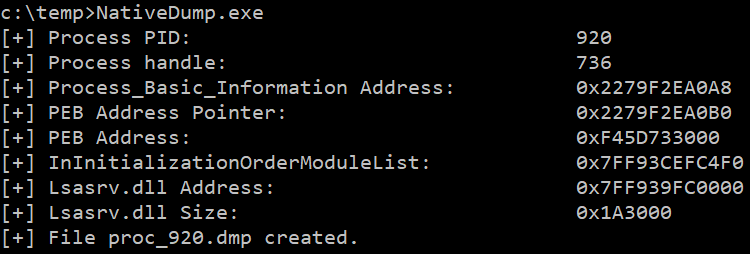
Dump lsass using only NTAPI functions by hand-crafting Minidump files (without MiniDumpWriteDump!!!)

memory-forensicspost-exploitationred-teaming
7491 month ago
Hunt-Sleeping-Beacons preview

Hunt-Sleeping-Beacons

GitHubtheflink/hunt-sleeping-beacons

Callstack scanner that identifies IOCs of unpacked or injected C2 agents by analyzing thread idle behavior, unbacked memory, module stomping, APCs,…

binary-analysisdefensive-toolsforensics+3
6848 months ago
Limon preview

Limon

GitHubmonnappa22/limon

Limon is a sandbox developed as a research project written in python, which automatically collects, analyzes, and reports on the run time indicators…

dynamic-analysis-sandboxingmalware-analysismemory-forensics+1
40510 years ago
physmem2profit preview

physmem2profit

GitHubreverseclabs/physmem2profit

Physmem2profit can be used to create a minidump of a target hosts' LSASS process by analysing physical memory remotely

data-exfiltrationdigital-forensicsmemory-forensics+4
4224 years ago
ghost preview

ghost

GitHubpandaadir05/ghost

Detects process injection and memory manipulation used by malware. Finds RWX regions, shellcode patterns, API hooks, thread hijacking, and process…

binary-analysisdefensive-toolsforensics+6
3892 months ago
artifacts-kit preview

artifacts-kit

GitHubforrest-orr/artifacts-kit

Pseudo-malicious usermode memory artifact generator kit designed to easily mimic the footprints left by real malware on an infected Windows OS.

exploitationforensicsmalware-analysis+5
2282 years ago
Learning-Linux-Binary-Analysis preview

Learning-Linux-Binary-Analysis

GitHubpacktpublishing/learning-linux-binary-analysis

Learning Linux Binary Analysis, published by Packt

binary-analysisbinary-exploitationdebuggers+7
893 years ago
MemTracer preview

MemTracer

GitHubmayhamad/memtracer

Live memory analysis tool for detecting reflectively loaded .NET DLLs by scanning process memory regions for abnormal flags, page types, and PE…

digital-forensicsforensicsmalware-analysis+1
644 years ago
gentlemen-decryptor preview

gentlemen-decryptor

GitHubbedrock-safeguard/gentlemen-decryptor

First-ever decryptor for The Gentlemen ransomware — recovers encryption keys from process memory dumps using X25519 ephemeral key extraction. 35/35…

cryptographydigital-forensicseducation+7
314 months ago
CVE-2016-0846 preview

CVE-2016-0846

GitHubsecmob/cve-2016-0846

arbitrary memory read/write by IMemroy OOB

binary-exploitationexploitationmemory-forensics+2
3610 years ago
CovenantDecryptor preview

CovenantDecryptor

GitHubnaacbin/covenantdecryptor

Decrypts Covenant C2 communications by extracting RSA private keys from minidumps, recovering AES session keys, and converting network captures to…

command-and-controlcryptographydigital-forensics+4
372 years ago
CVE-2020-1493 preview

CVE-2020-1493

GitHub0neb1n/cve-2020-1493

Technical analysis and PoC details for CVE-2020-1493, a zero-click Outlook RCE triggered by malformed MS-TNEF attachments leading to remote code…

binary-exploitationemail-securityexploitation+3
256 years ago
Previous12345Next