
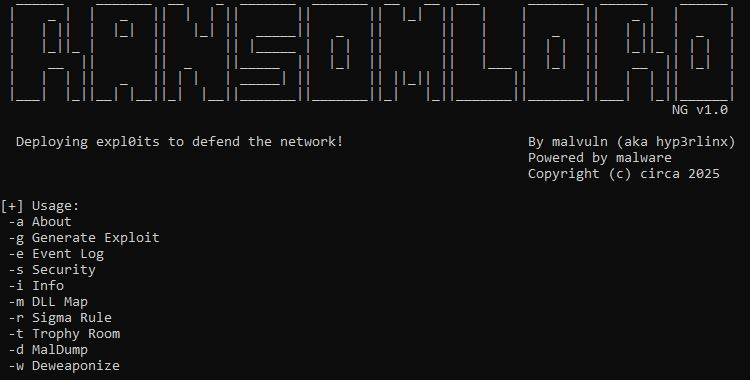
RansomLord
 malvuln/ransomlord
RansomLord is a proof-of-concept Anti-Ransomware exploitation tool that automates the creation of PE files, used to compromise ransomware…
binary-exploitationdefensive-toolsexploitation+4
515
malvuln/ransomlordRansomLord is a proof-of-concept Anti-Ransomware exploitation tool that automates the creation of PE files, used to compromise ransomware…
 jir4vv1t/cve-2025-43529
Technical exploit for CVE-2025-43529, a WebKit DFG JIT compiler vulnerability enabling use-after-free via missing store barrier in concurrent GC,…
 whw0x455/cve-2023-41992
Proof-of-concept for CVE-2023-41992, a macOS kernel vulnerability, demonstrating exploitation techniques and providing a patch analysis.
 dukptkey/cve-2020-9273
Analysis and exploitation of an use-after-free in ProFTPd
 jprx/cve-2024-54507
Proof-of-concept exploit for CVE-2024-54507, an integer type confusion vulnerability in XNU kernel, with technical writeup and exploitation details.
 xf1les/fsop-finder
Binary Ninja plugin that scans glibc libio for FSOP code paths capable of hijacking control flow and stack pointer, aiding heap exploitation research.
 kuzeyardabulut/cve-2024-1065
Proof-of-concept exploit for CVE-2024-1065, demonstrating page cache exploitation via a use-after-free in the ARM Mali GPU kernel driver to achieve…
 hoangprod/cve-2021-31956-poc
Proof-of-concept exploit for CVE-2021-31956, a Windows kernel NTFS elevation-of-privilege vulnerability. Demonstrates exploitation techniques…
 lsinus/cachemeifyoucan
SLUBStick exploitation of CVE-2022-2588. Converting a DF into a cross-cache arbitrary memory R/W primitive through PTE manipulation.
 datntsec/cve-2020-1206
Technical analysis of CVE-2020-1206 (SMBleed) kernel information disclosure vulnerability in Windows SMBv3, including unauthenticated memory leak…
 colaoo123/cve-2022-22555
Exploit for CVE-2022-22555, a Linux kernel heap buffer overflow vulnerability enabling local privilege escalation. Includes proof-of-concept code and…
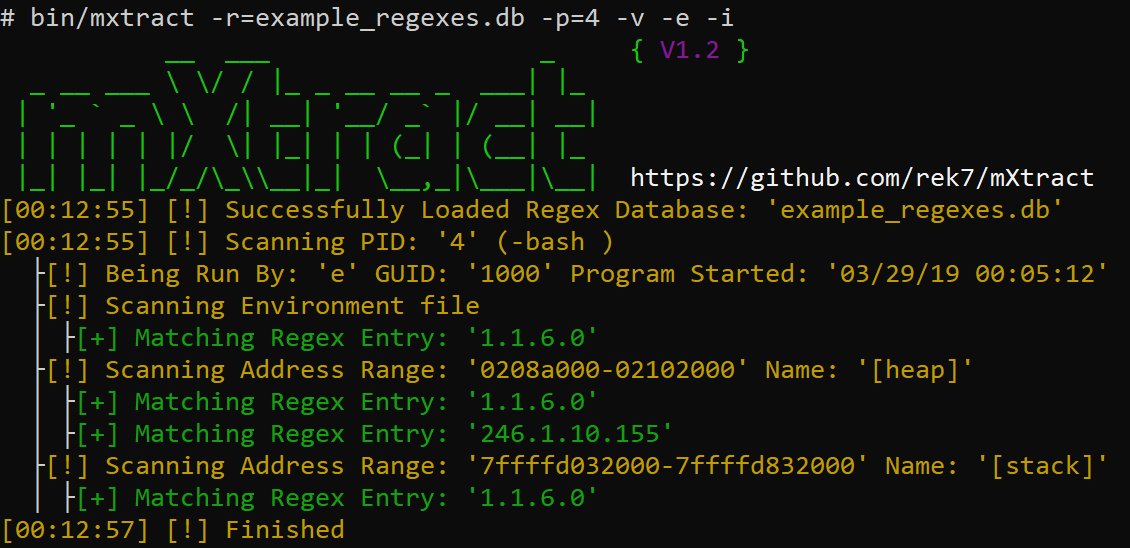 rek7/mxtract
mXtract - Memory Extractor & Analyzer
 alexcyberx/cve-2025-14847_expolit
Exploit tool for CVE-2025-14847, a MongoDB memory disclosure vulnerability, enabling multi-threaded extraction of sensitive data and secrets from…
 lzty/cve-2025-7771
Rust-based PoC exploit for CVE-2025-7771 providing arbitrary read/write primitives via a vulnerable driver, with virtual-to-physical address…
 ufrisk/pcileech
Direct Memory Access (DMA) Attack Software
 stephenfewer/reflectivedllinjection
Reflective DLL injection is a library injection technique in which the concept of reflective programming is employed to perform the loading of a…
 thewover/donut
Generates x86, x64, or AMD64+x86 position-independent shellcode that loads .NET Assemblies, PE files, and other Windows payloads from memory and runs…
 monoxgas/srdi
Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode