

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
27 results
LaZagne preview

LaZagne

GitHubalessandroz/lazagne

Cross-platform credential recovery tool that extracts stored passwords from browsers, email clients, databases, system mechanisms, and network…

encryption-decryption-toolsforensicshash-analysis+8
11.0k
1 year ago
patriot preview

patriot

GitHubjoe-desimone/patriot

In-memory stealth detection tool that identifies process hollowing, module stomping, unbacked executable regions, and anomalous CONTEXT structures…
anomaly-detectionbinary-analysisdefensive-tools+3
1644 years ago
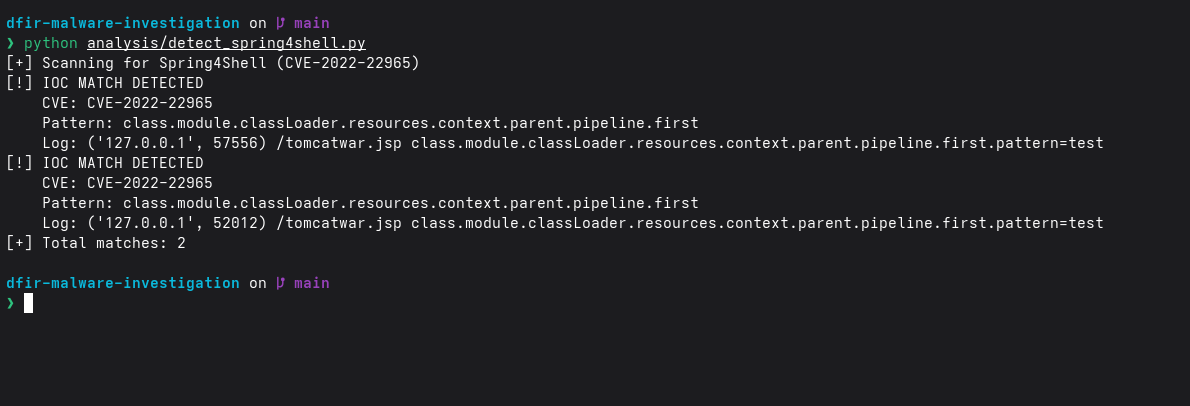
dfir-malware-investigation preview

dfir-malware-investigation

GitHubsuyash-r-k/dfir-malware-investigation

Spring4Shell (CVE-2022-22965) DFIR lab with exploit simulation, Python WAF, IOC-based detection, and PCAP analysis.
digital-forensicseducationincident-response+9
8 months ago
Limon preview

Limon

GitHubmonnappa22/limon

Limon is a sandbox developed as a research project written in python, which automatically collects, analyzes, and reports on the run time indicators…

dynamic-analysis-sandboxingmalware-analysismemory-forensics+1
40510 years ago
google-poc preview

google-poc

GitHub0xxa/google-poc

This repo contains instructions to reproduce CVE-2025-13425: Null Pointer dereference / Array over-indexing vulnerability that I found in Google's…

binary-analysisexploitationfirmware-analysis+3
10 months ago
Hunt-Sleeping-Beacons preview

Hunt-Sleeping-Beacons

GitHubtheflink/hunt-sleeping-beacons

Callstack scanner that identifies IOCs of unpacked or injected C2 agents by analyzing thread idle behavior, unbacked memory, module stomping, APCs,…

binary-analysisdefensive-toolsforensics+3
6818 months ago
memaddressanalysis preview

memaddressanalysis

GitHubnccgroup/memaddressanalysis

Research project related to memory address analysis
binary-analysismemory-forensicspapers-research+1
1412 years ago
NORM-EDR preview

NORM-EDR

GitHubamberchalia/norm-edr

Experimental kernel-mode EDR research project focused on explainable detection of suspicious in-memory execution patterns, producing human-readable…
binary-analysisdefensive-toolseducation+4
116 months ago
Project-Field-Analysis-and-Memory-Leak-Demonstration preview

Project-Field-Analysis-and-Memory-Leak-Demonstration

GitHubartemcyberlab/project-field-analysis-and-memory-leak-demonstration

The objective of this project was to assess a remote host for the Heartbleed vulnerability (CVE-2014-0160), verify its presence, and exploit it to…

educationexploitationinformation-gathering+3
1 year ago
CVE-2021-41160 preview

CVE-2021-41160

GitHubjajangjaman/cve-2021-41160

FreeRDP is a free implementation of the Remote Desktop Protocol (RDP), released under the Apache license. In affected versions a malicious server…

binary-analysiseducationexploitation+3
3 years ago
dnSpy preview

dnSpy

GitHubdnspyex/dnspy

Unofficial revival of the well known .NET debugger and assembly editor, dnSpy
ai-assisted-reversingbinary-analysisbinary-exploitation+10
11.2k1 month ago
memhunter preview

memhunter

GitHubmarcosd4h/memhunter

Live hunting of code injection techniques
defensive-toolsincident-responsemalware-analysis+1
3837 years ago
analyzer preview

analyzer

GitHubqeeqbox/analyzer

Analyze, extract and visualize features, artifacts and IoCs of files and memory dumps (Windows, Linux, Android, iPhone, Blackberry, macOS binaries,…
digital-forensicsdynamic-analysis-sandboxingforensics+8
3232 years ago
CVE-2018-17182 preview

CVE-2018-17182

GitHubjas502n/cve-2018-17182

Linux kernel use-after-free (UAF) privilege escalation exploit for CVE-2018-17182, providing root shell access on affected kernels (3.16 to 4.18.8).…

binary-exploitationexploitationmemory-forensics+2
1307 years ago
NovaLdr preview

NovaLdr

GitHubblacksnufkin/novaldr

Threadless Module Stomping In Rust with some features (In memory of those murdered in the Nova party massacre)
code-analysiseducationexploitation+7
2652 years ago
TiEtwAgent preview

TiEtwAgent

GitHubxuanxuan0/tietwagent

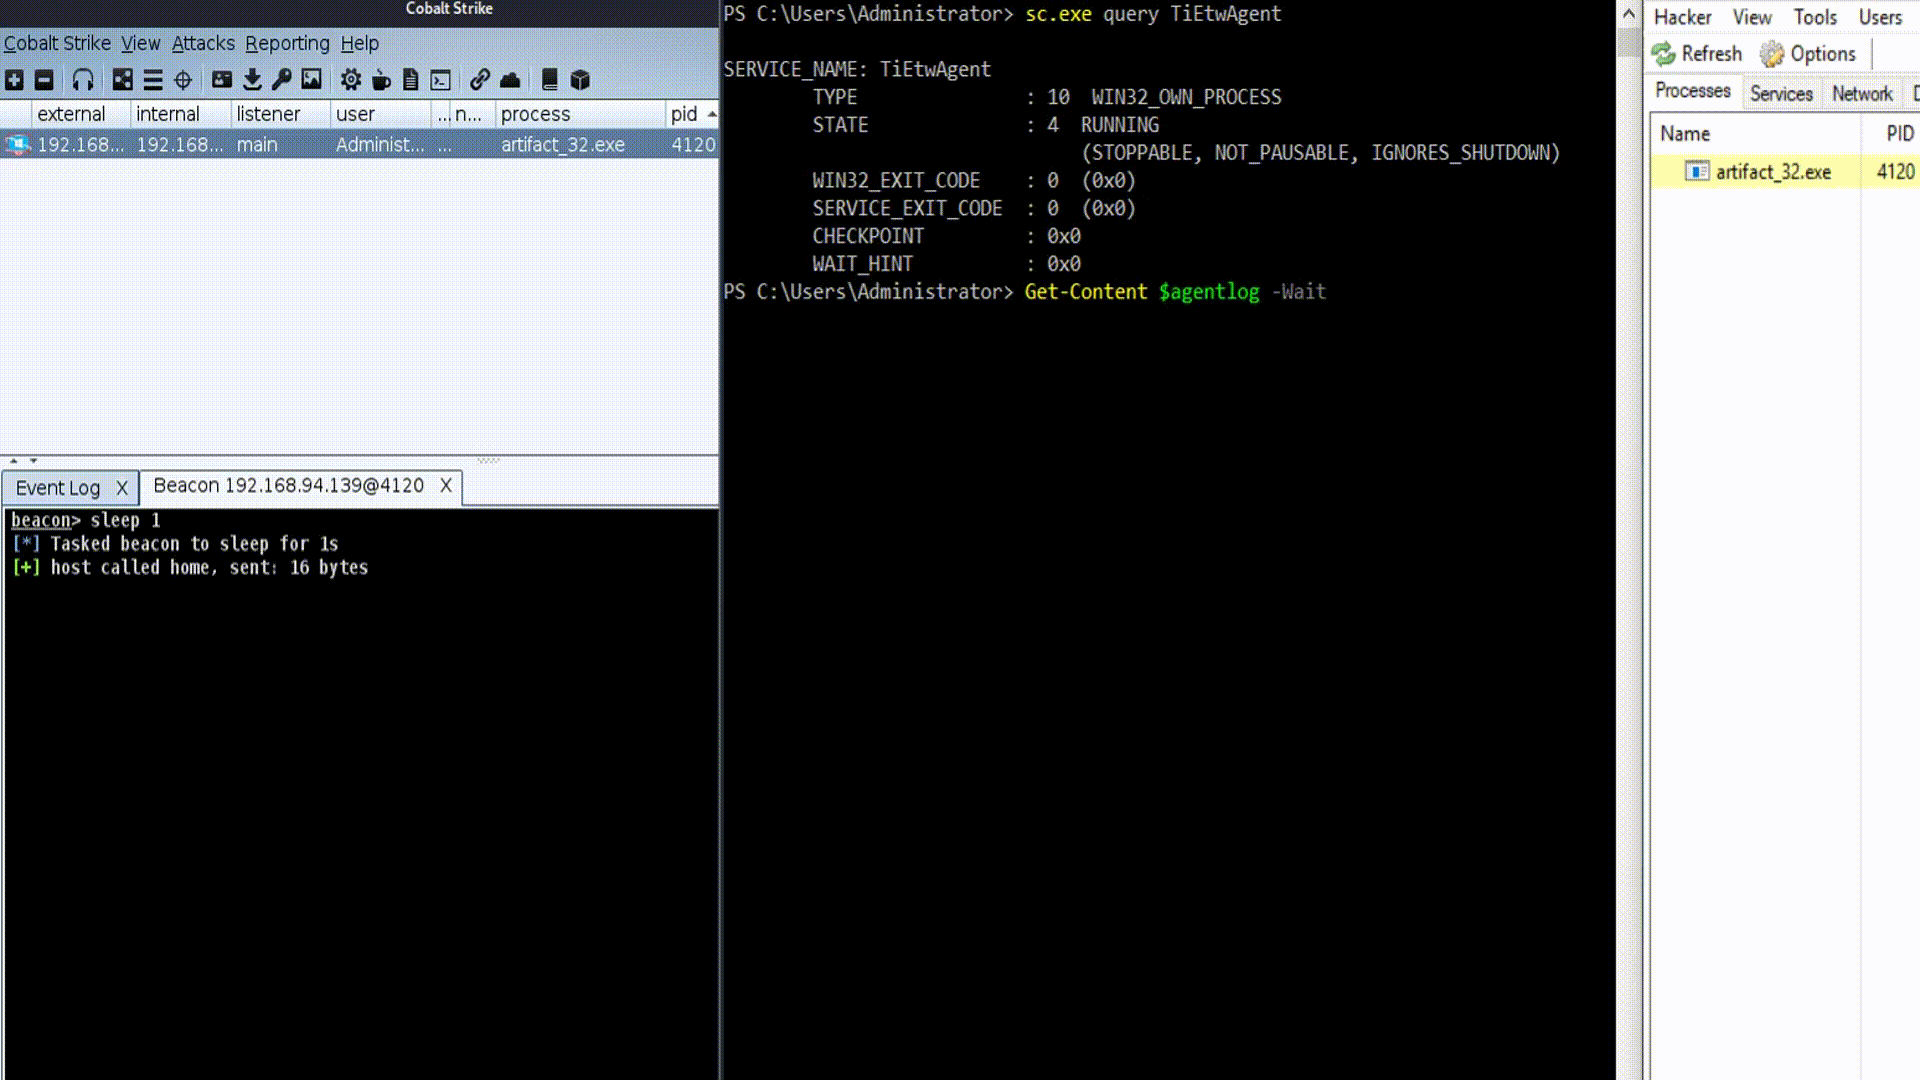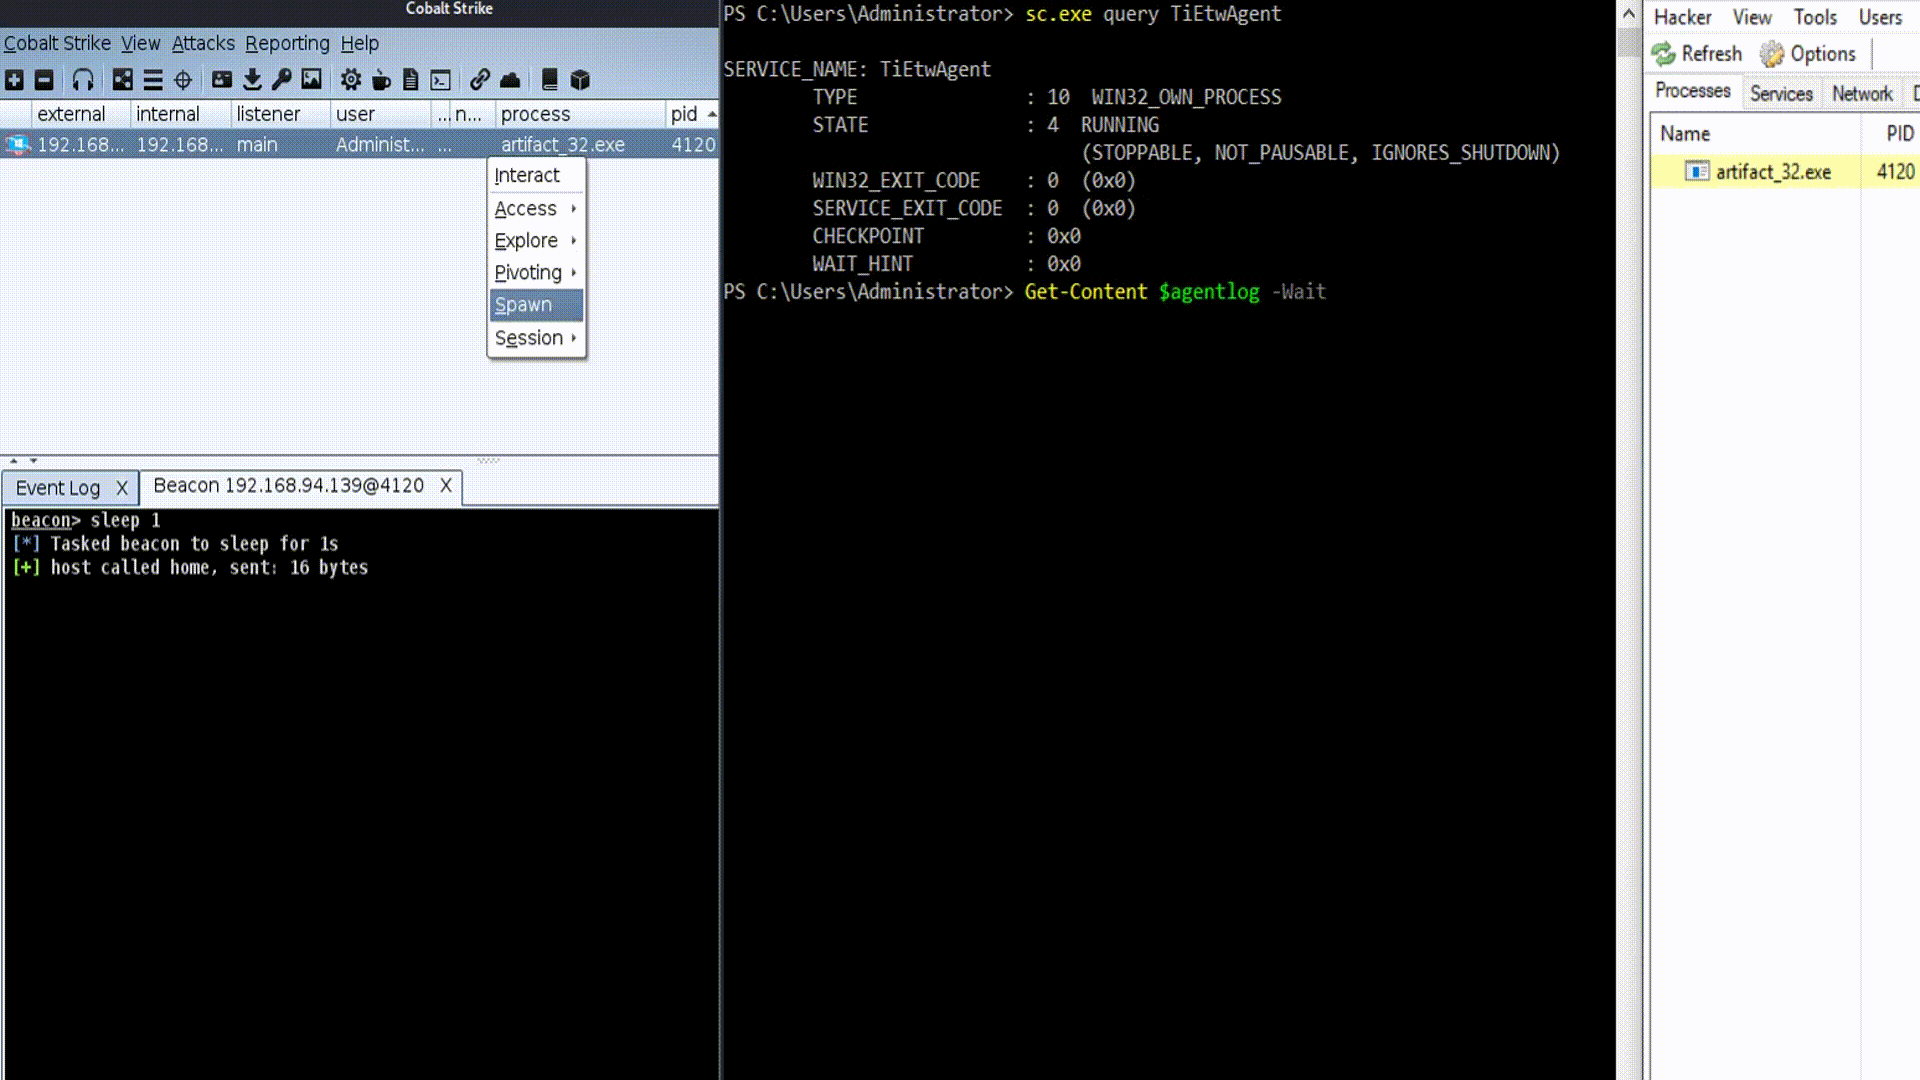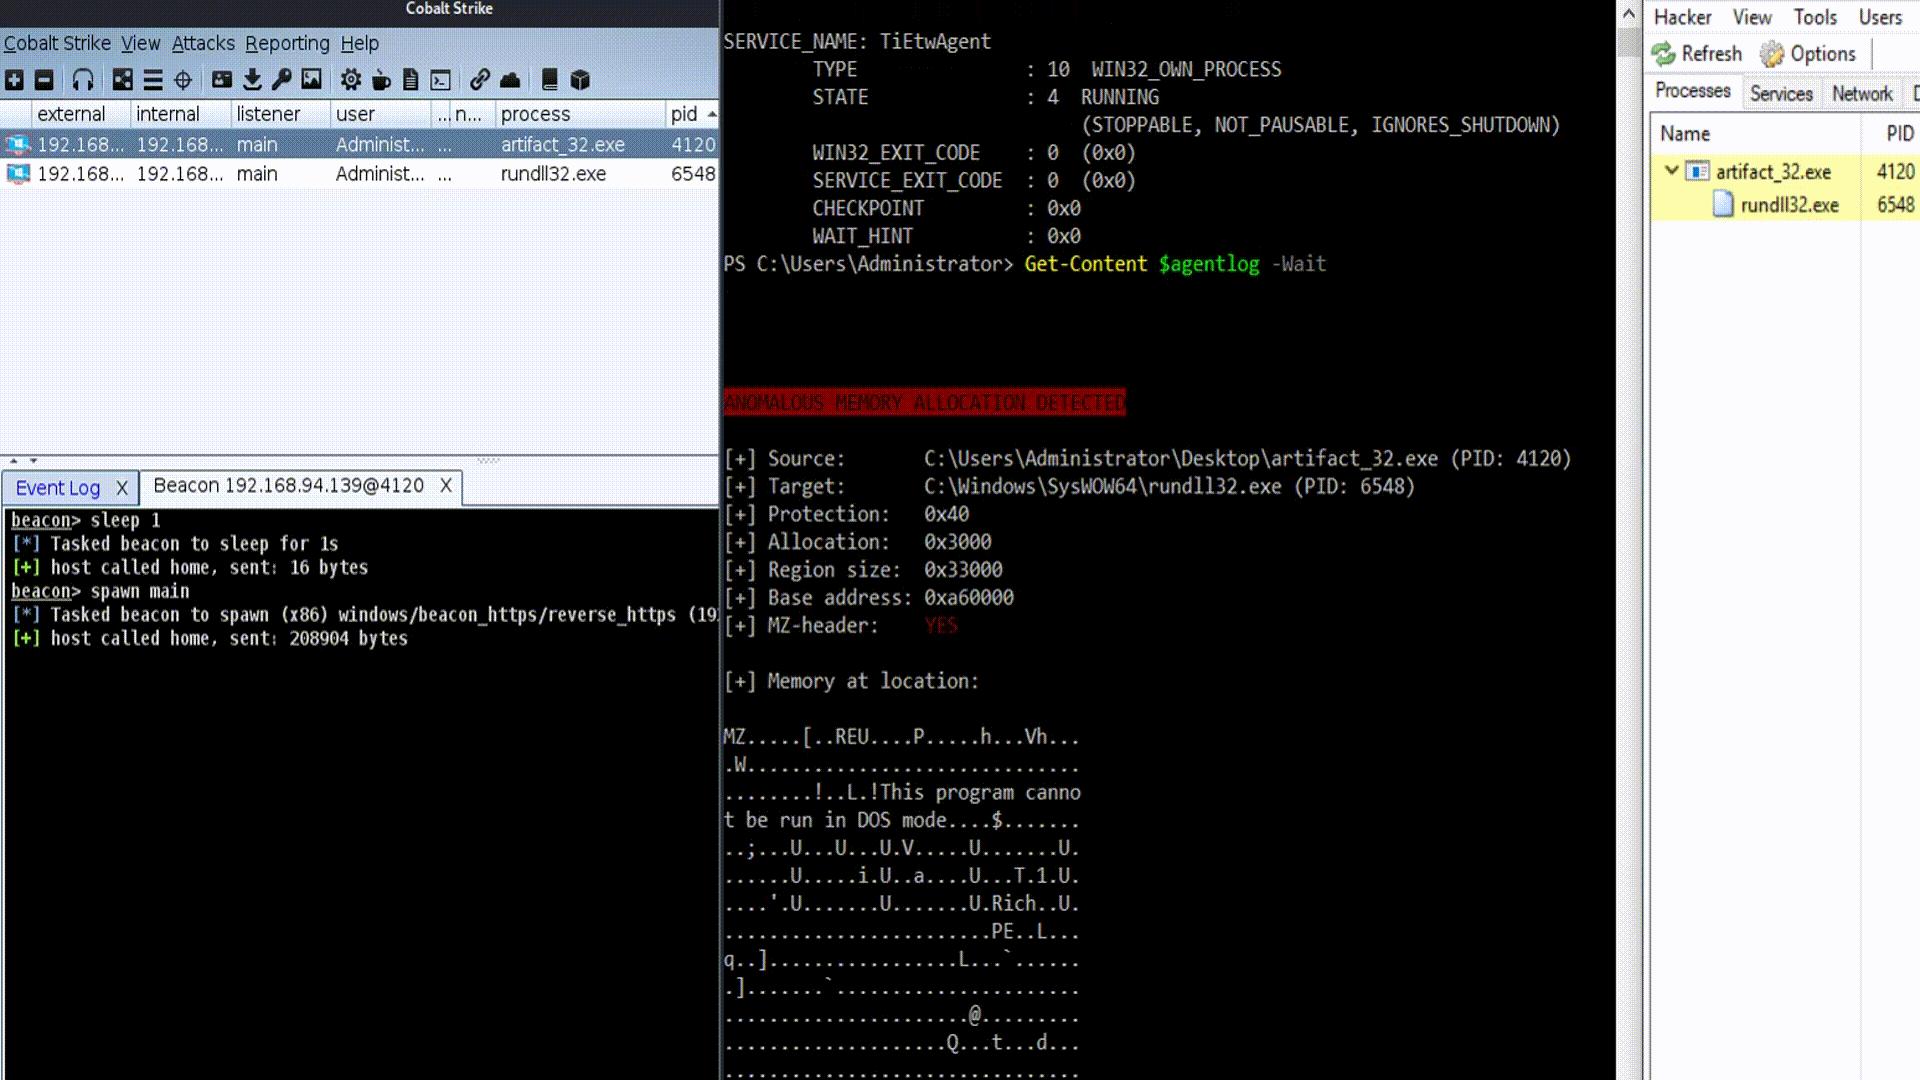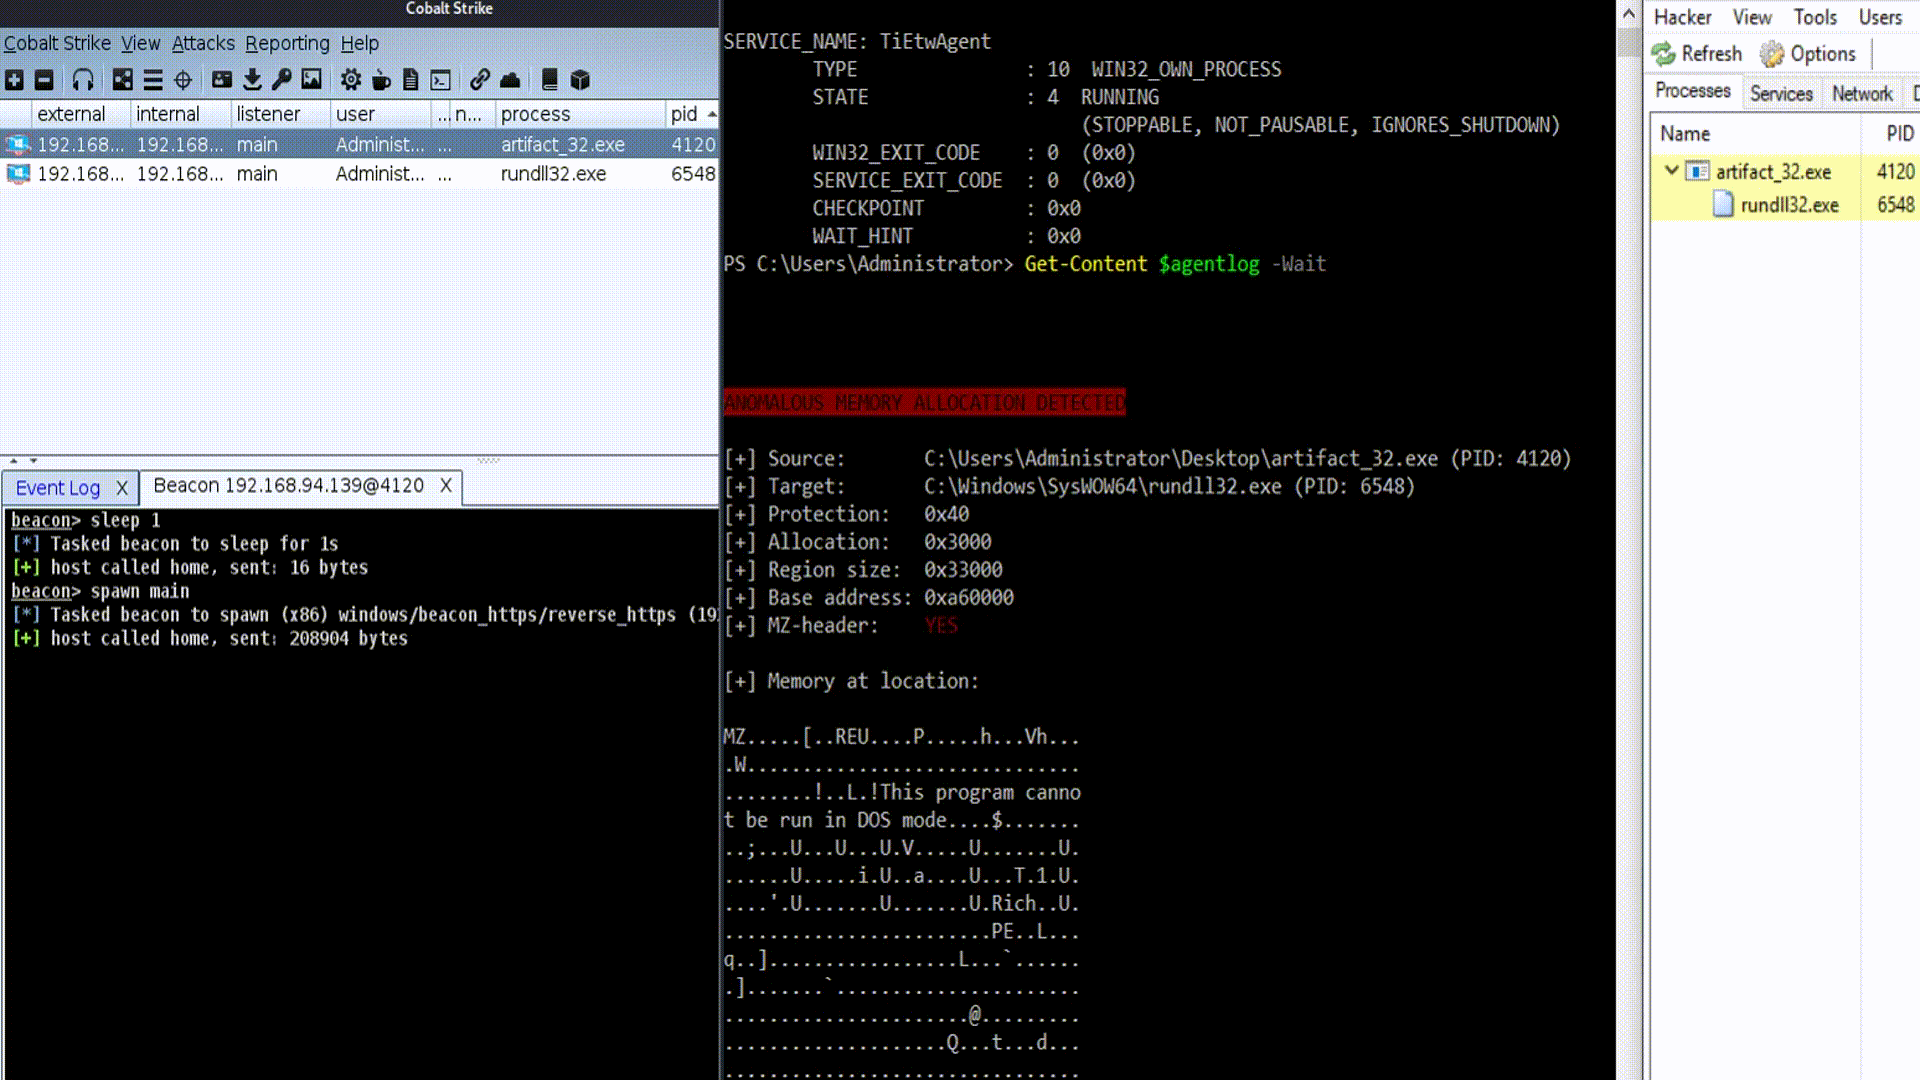
PoC memory injection detection agent based on ETW, for offensive and defensive research purposes
defensive-toolseducationmalware-analysis+1
2995 years ago
pesieve-go preview

pesieve-go

GitHubhasherezade/pesieve-go

Golang bindings for PE-sieve
binary-analysisdynamic-code-analysismalware-analysis+1
432 years ago
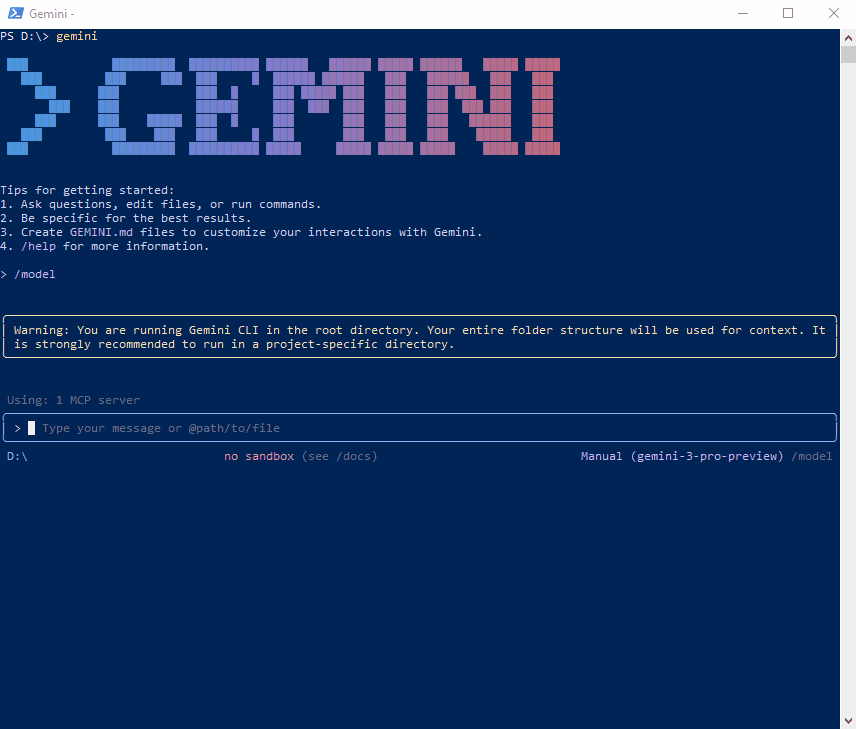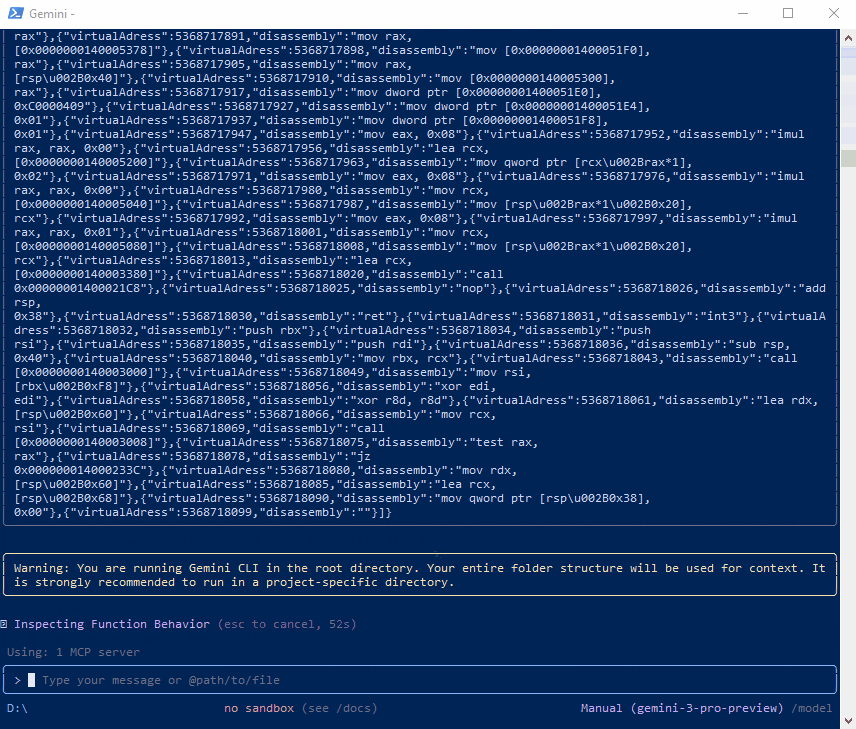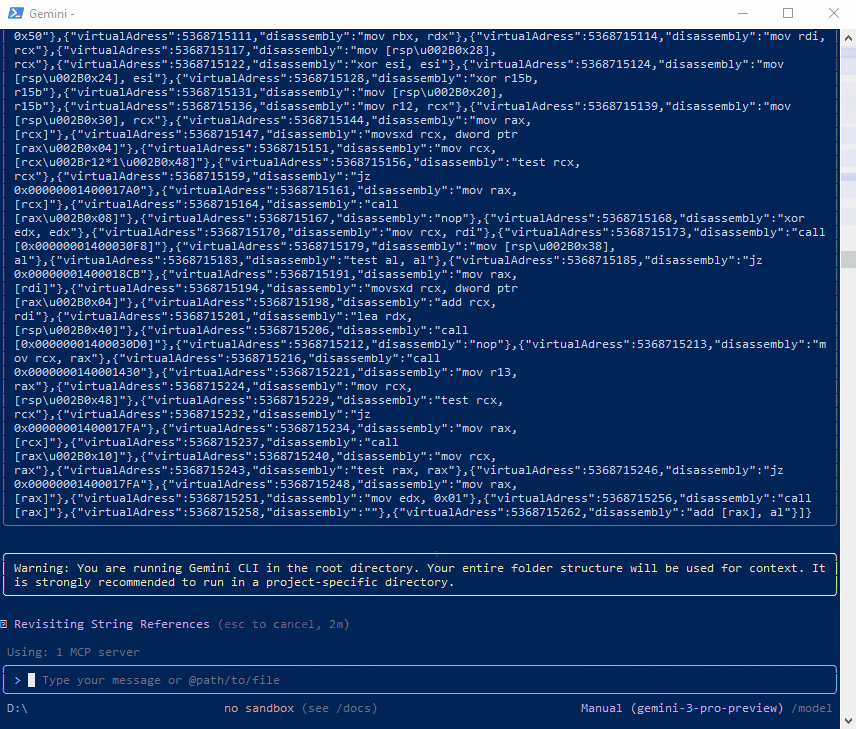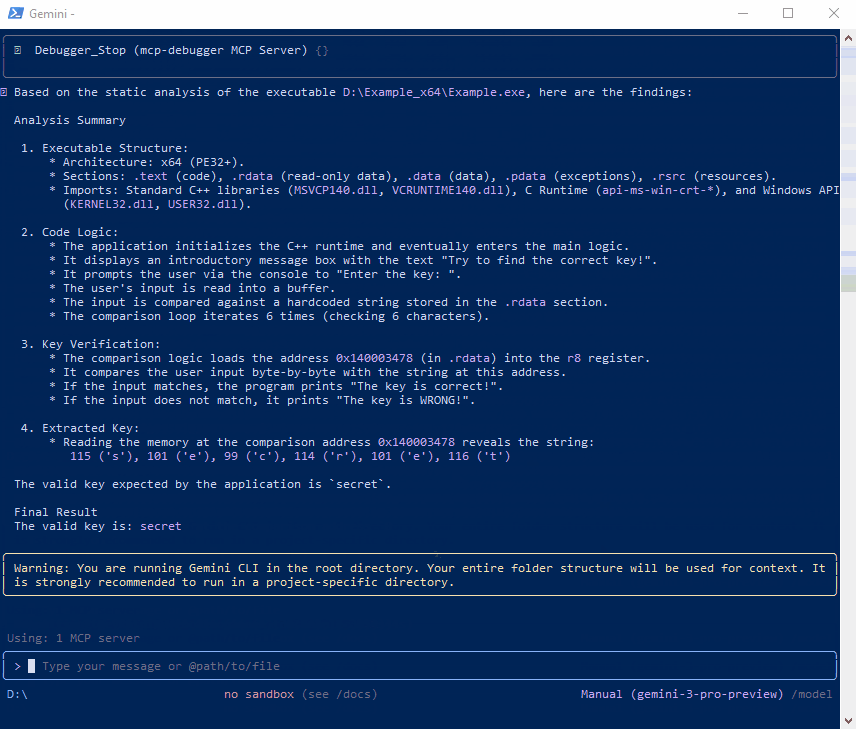
MCPDebugger preview

MCPDebugger

GitHubfatmike-gh/mcpdebugger

A MCP Debugger Server for Windows executables (x86 and x64). Exposes debugger functionality as MCP Tools for static / dynamic analysis of the…

ai-assisted-reversingbinary-analysisdebuggers+4
136 months ago
Previous12Next