

aes-finder
 mmozeiko/aes-finder
Utility to find AES keys in running processes
binary-analysiscryptographyencryption-decryption-tools+2
mmozeiko/aes-finderUtility to find AES keys in running processes
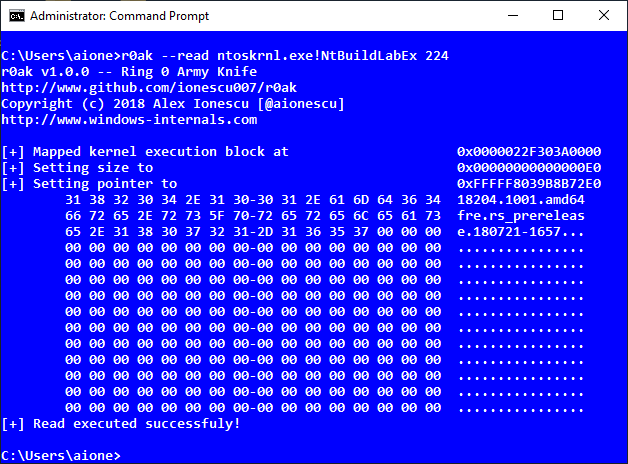 harryanon/r0ak
Windows command-line utility for reading, writing, and executing kernel-mode code from Administrator context using a font validation execution…
 bohops/rogueassemblyhunter
Rogue Assembly Hunter is a utility for discovering 'interesting' .NET CLR modules in running processes.
 piat0n/baremetal-ram-dumper
A bare-metal x86 utility to dump physical RAM directly to disk. Built and tested for Cold Boot Attack experiments on frozen memory.
 hackmichnet/aztokenfinder
Offensive token-harvesting utility that searches x64 process memory and TokenBroker cache files for Azure AD/O365 JWT tokens across Office, Edge,…
 prox0959/memguard
Zero-dependency Windows EDR utility that detects and mitigates unauthorized LSASS memory access, handle duplication, and LOLBin credential dumping in…
 dbrant/bios_memimage
RAM imaging utility.
 ivan-sincek/invoker
Penetration testing utility and antivirus assessment tool.
 volatilityfoundation/dwarf2json
convert ELF/DWARF symbol and type information into vol3's intermediate JSON


 volatilityfoundation/volatility
An advanced memory forensics framework