

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
38 results
capa preview

capa

GitHubmandiant/capa

Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…

ai-assisted-reversingbinary-analysiscode-analysis+10
6.2k
13 days ago
donut preview

donut

GitHubthewover/donut

Generates x86, x64, or AMD64+x86 position-independent shellcode that loads .NET Assemblies, PE files, and other Windows payloads from memory and runs…
exploitationids-ips-evasionmemory-forensics+7
4.7k1 year ago
Process-Dump preview

Process-Dump

GitHubglmcdona/process-dump

Windows tool for dumping malware PE files from memory back to disk for analysis.
binary-analysisforensicsmalware-analysis+2
1.9k3 years ago
NativeDump preview

NativeDump

GitHubricardojoserf/nativedump

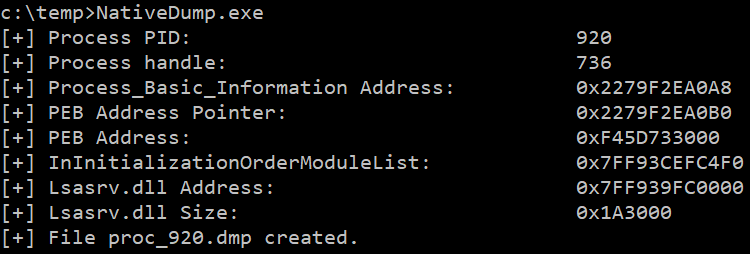
Dump lsass using only NTAPI functions by hand-crafting Minidump files (without MiniDumpWriteDump!!!)
memory-forensicspost-exploitationred-teaming
7501 month ago
Fastir_Collector preview

Fastir_Collector

GitHubsekoialab/fastir_collector

Live Windows forensic acquisition tool that collects system artefacts (registry, memory, disk, files) into CSV/JSON for early compromise detection…

digital-forensicsdisk-forensicsforensics+3
5215 years ago
irflow-timeline preview

irflow-timeline

GitHubr3nzsec/irflow-timeline

DFIR Timeline Analysis for macOS — SQLite-backed viewer for CSV, TSV, XLSX, EVTX, Plaso, $MFT, and $J files with AI Artifacts, AI Secret Hunt,…
digital-forensicsdisk-forensicsforensics+7
36913 days ago
CobaltStrikeScan preview

CobaltStrikeScan

GitHubapr4h/cobaltstrikescan

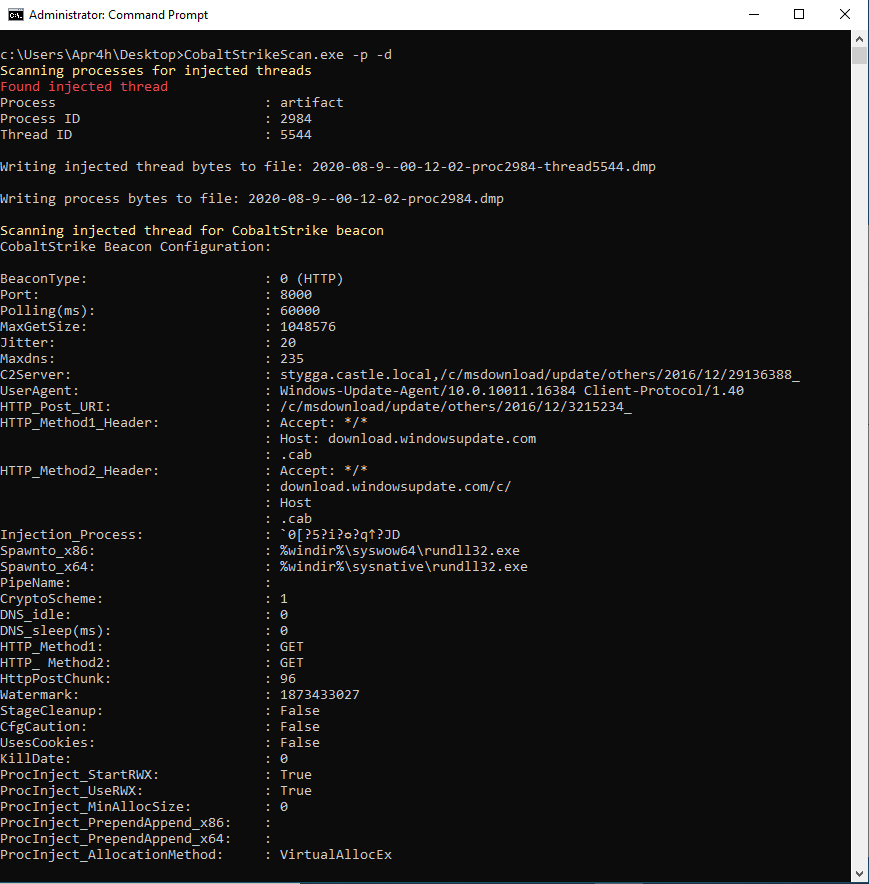
Scan files or process memory for CobaltStrike beacons and parse their configuration

defensive-toolsdigital-forensicsforensics+4
9175 years ago
Remote-Desktop-Caching- preview

Remote-Desktop-Caching-

GitHubviralmaniar/remote-desktop-caching-

This tool allows one to recover old RDP (mstsc) session information in the form of broken PNG files. These PNG files allows Red Team member to…

digital-forensicsforensicsincident-response+4
2188 years ago
analyzer preview

analyzer

GitHubqeeqbox/analyzer

Analyze, extract and visualize features, artifacts and IoCs of files and memory dumps (Windows, Linux, Android, iPhone, Blackberry, macOS binaries,…

digital-forensicsdynamic-analysis-sandboxingforensics+8
3222 years ago
PPLBlade preview

PPLBlade

GitHubtastypepperoni/pplblade

Bypasses PPL protection to dump LSASS process memory, obfuscates dump files with XOR, and exfiltrates them remotely via RAW or SMB without writing to…
data-exfiltrationexploitationmemory-forensics+2
6013 years ago
RansomLord preview

RansomLord

GitHubmalvuln/ransomlord

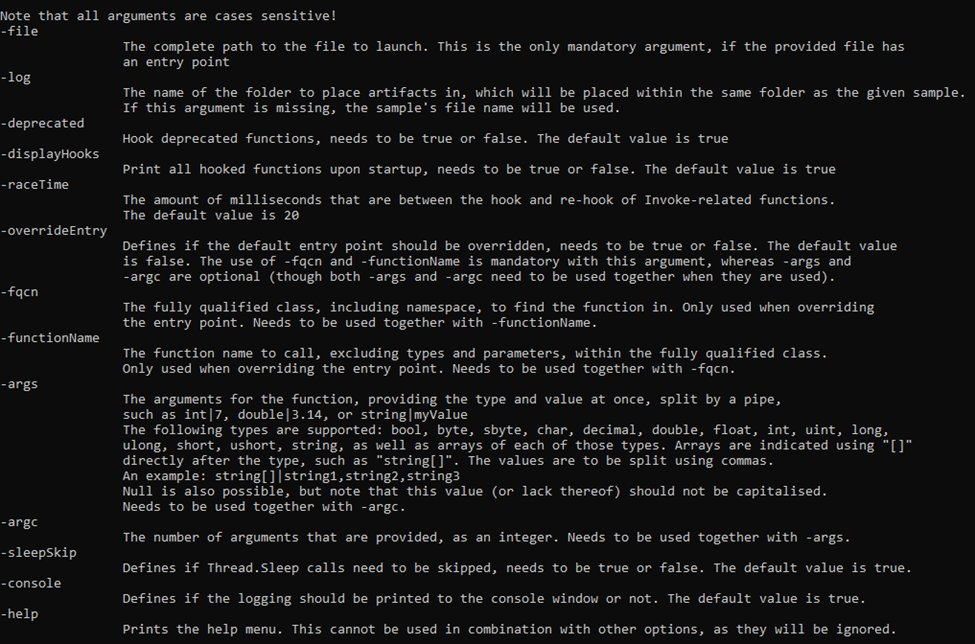
RansomLord is a proof-of-concept Anti-Ransomware exploitation tool that automates the creation of PE files, used to compromise ransomware…
binary-exploitationdefensive-toolsexploitation+4
5151 year ago
DotDumper preview

DotDumper

GitHubadvanced-threat-research/dotdumper

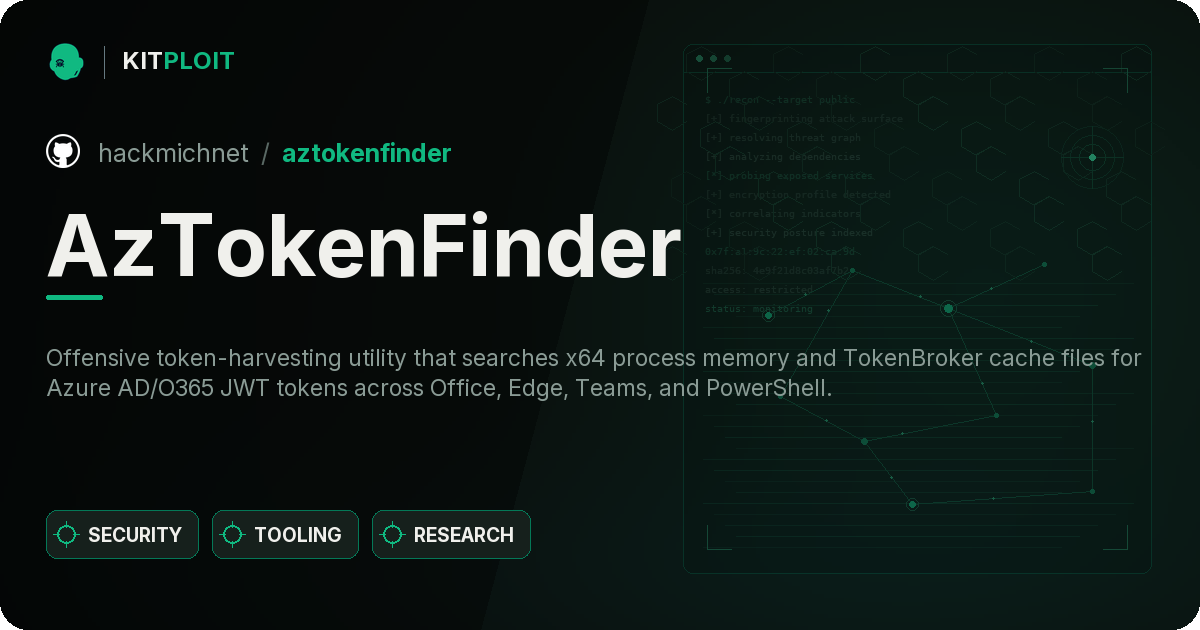
An automatic unpacker and logger for DotNet Framework targeting files
binary-analysisdebuggersdynamic-analysis-sandboxing+4
2643 years ago
AzTokenFinder preview

AzTokenFinder

GitHubhackmichnet/aztokenfinder

Offensive token-harvesting utility that searches x64 process memory and TokenBroker cache files for Azure AD/O365 JWT tokens across Office, Edge,…
authenticationcloud-securitymemory-forensics+3
1093 years ago
gentlemen-decryptor preview

gentlemen-decryptor

GitHubbedrock-safeguard/gentlemen-decryptor

First-ever decryptor for The Gentlemen ransomware — recovers encryption keys from process memory dumps using X25519 ephemeral key extraction. 35/35…
cryptographydigital-forensicseducation+7
314 months ago
magic-extractor preview

magic-extractor

GitHubxchwarze/magic-extractor

Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.
binary-analysisdata-recoverydigital-forensics+8
4227 days ago
Sandb0x-Xtract0r preview

Sandb0x-Xtract0r

GitHubdarnellwashingtonjr94-art/sandb0x-xtract0r

Automated cross-platform sandbox that detonates suspicious files in isolated VMs/emulators, captures network and memory artifacts, and creates LLM…

dynamic-analysis-sandboxingmalware-analysismemory-forensics+3
32 days ago
CVE-2022-30292 preview

CVE-2022-30292

GitHubsprushed/cve-2022-30292

Technical documentation and analysis of CVE-2022-30292, a heap-based buffer overflow in Squirrel 3.2 leading to denial of service, sandbox escape,…
binary-exploitationcode-analysisexploitation+2
24 years ago
Filedumper preview

Filedumper

GitHubseyyidkadir/filedumper

Windows memory forensics tool for dumping files from process memory regions, searching byte patterns (PDF, JPG, SWF), and performing live process…

data-recoverydigital-forensicsforensics+3
18 months ago
Previous123Next