

ltm
 agent-hellboy/ltm
ltm is a machine-history debugger for Linux. It records process, file, network, memory, and block-I/O metadata via eBPF, then lets you query the…
debuggersdigital-forensicsdisk-forensics+7
25
agent-hellboy/ltmltm is a machine-history debugger for Linux. It records process, file, network, memory, and block-I/O metadata via eBPF, then lets you query the…
 amossys/memitm
Tool to make in memory man in the middle
 haitam-lazaar/libextractor-ole2-rce
PoC for a Critical stack-based buffer overflow in GNU libextractor ≤ 1.14. A malicious .doc file triggers an unbounded VLA allocation causing…
 viralmaniar/remote-desktop-caching-
This tool allows one to recover old RDP (mstsc) session information in the form of broken PNG files. These PNG files allows Red Team member to…
 ctm1/cve-2023-32784-keepass-linux
KeePass Master Password Extraction PoC for Linux
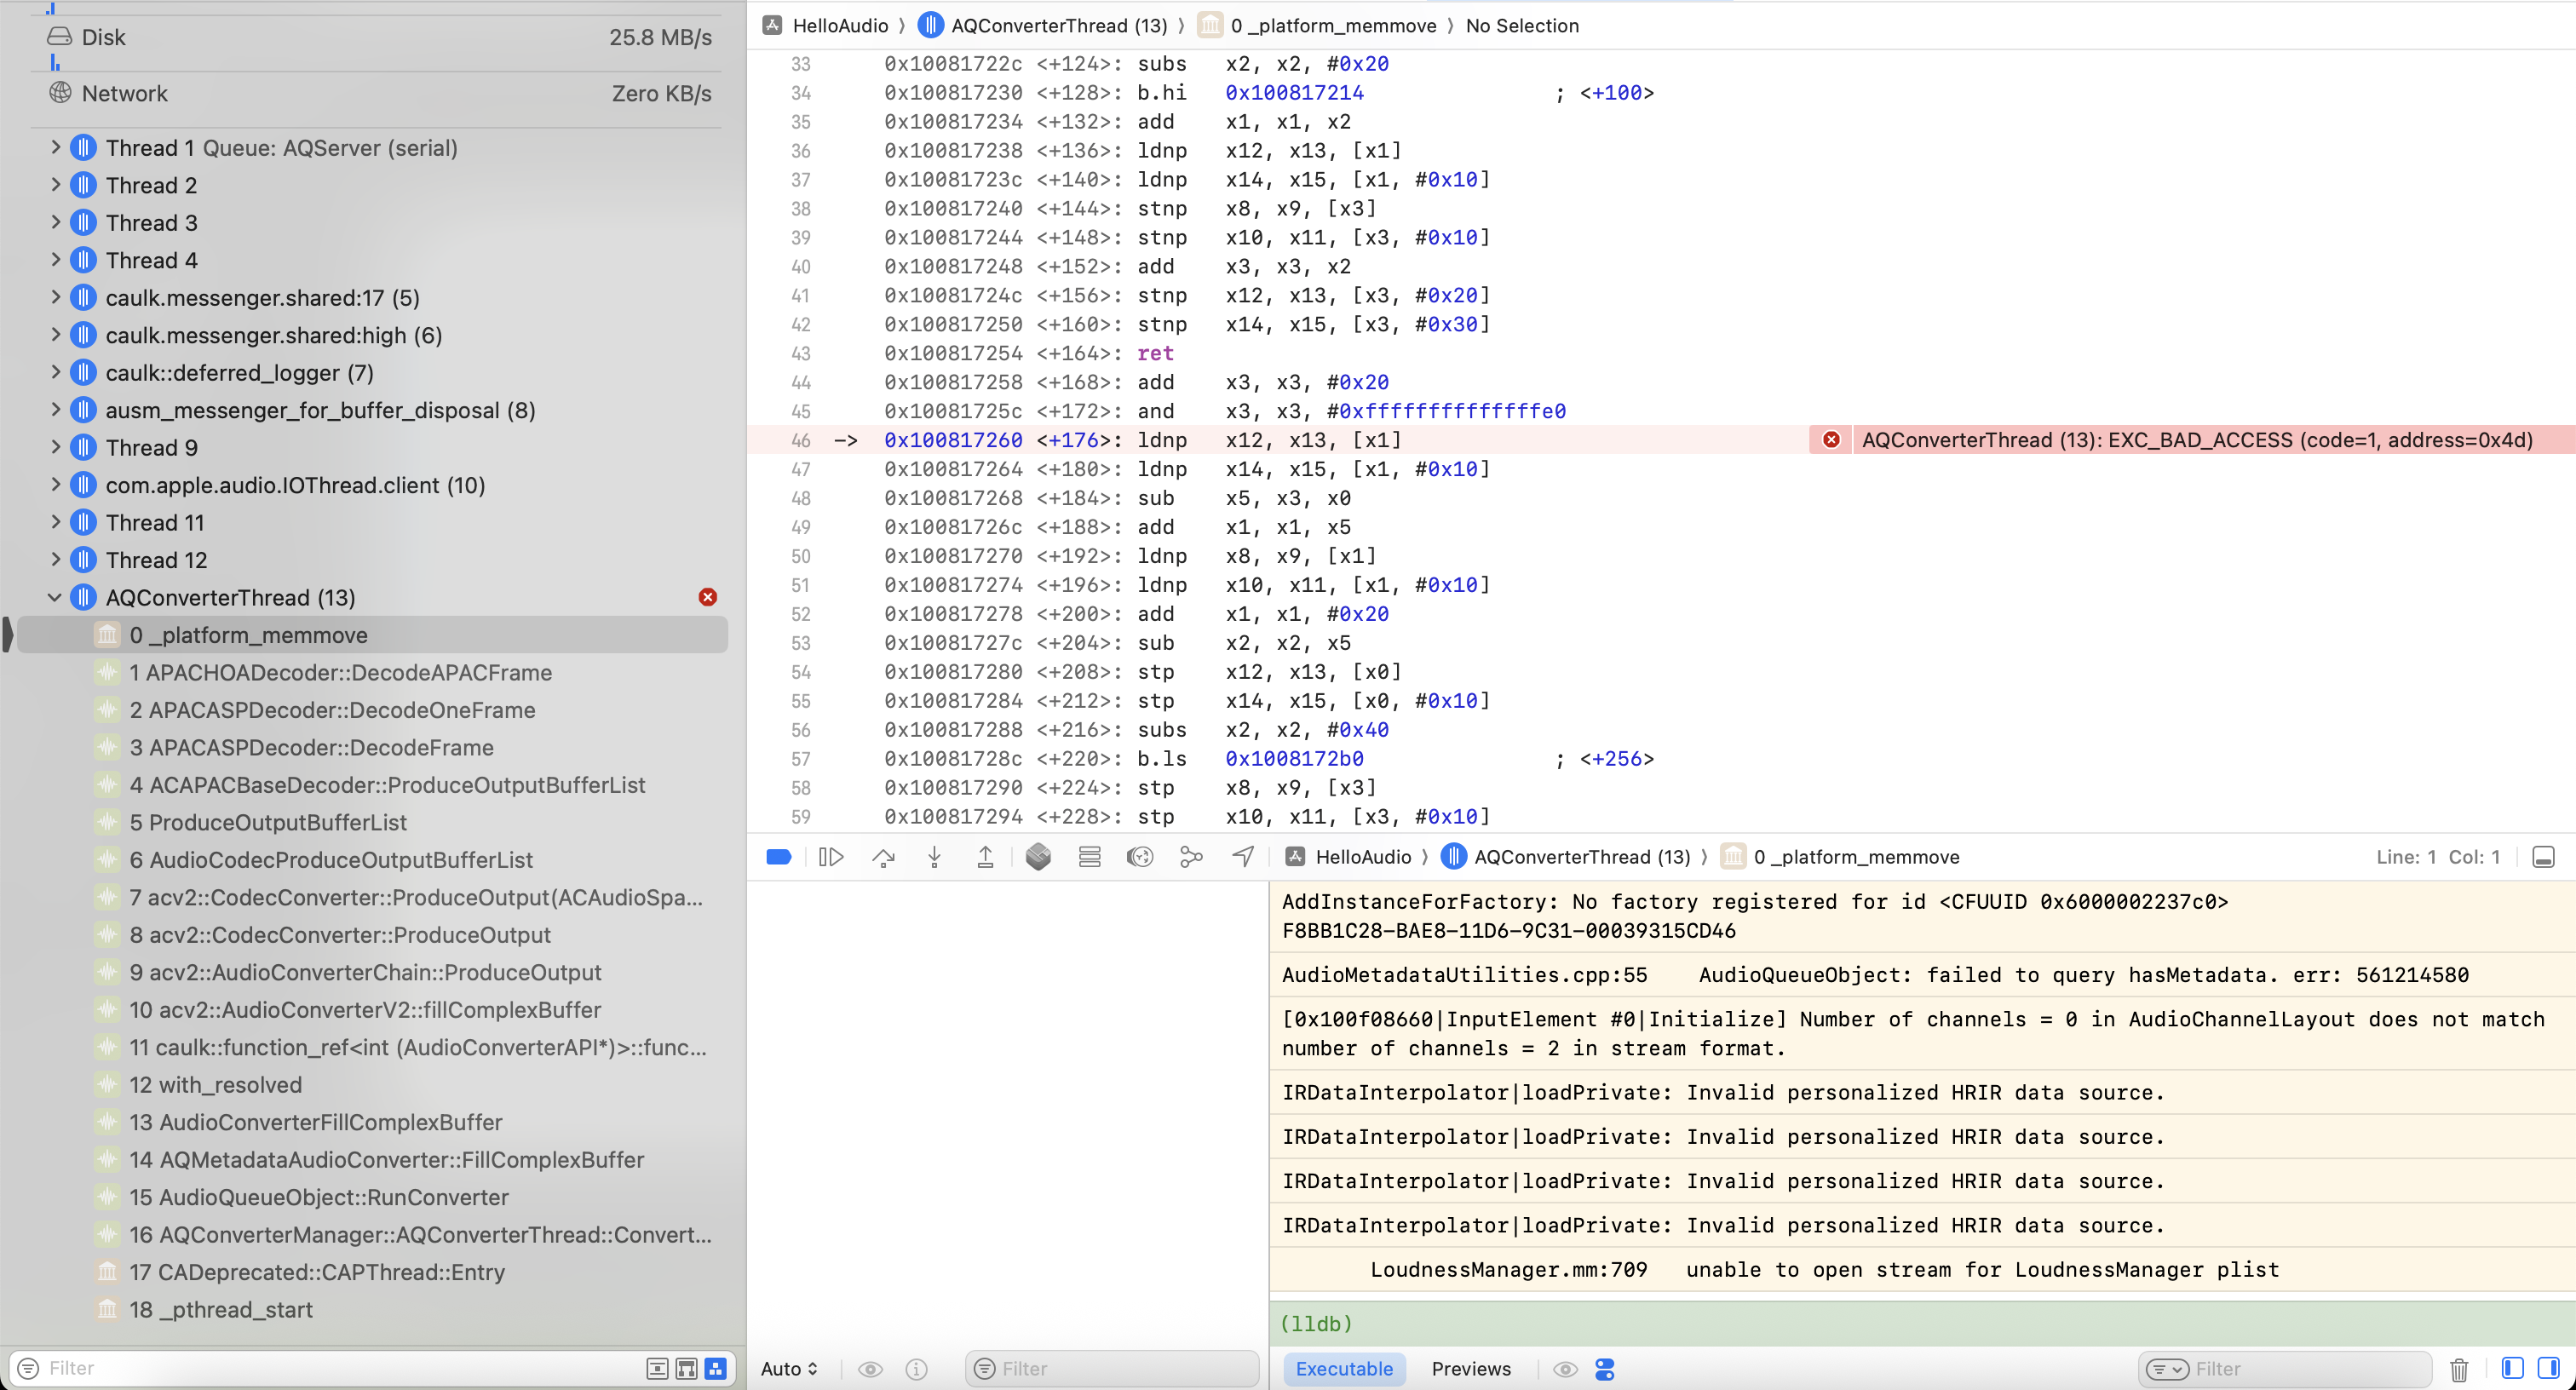 zhuowei/apple-positional-audio-codec-invalid-header
CVE-2025-31200 - @Noahhw46 figured it out
 illegal-instruction-co/processhacker-mcp
Runtime process analysis and memory hacking MCP server for AI agents. Supports dynamic extension loading, read-only mode, audit logging, and…
 artemcyberlab/project-field-analysis-and-memory-leak-demonstration
The objective of this project was to assess a remote host for the Heartbleed vulnerability (CVE-2014-0160), verify its presence, and exploit it to…
 gmh5225/evilkaspersky
Windows kernel driver experiment based on KasperskyHook that uses direct syscalls for interprocess memory copying, with support for unloading the…
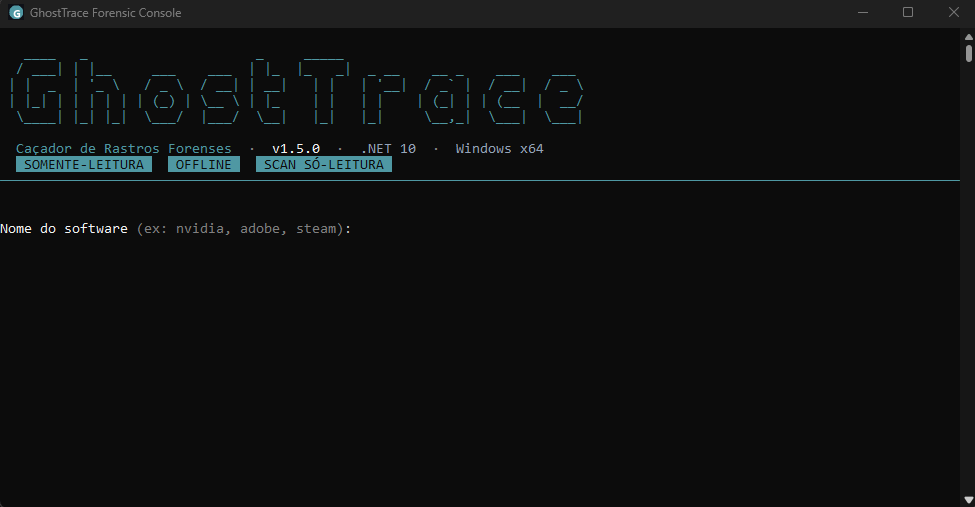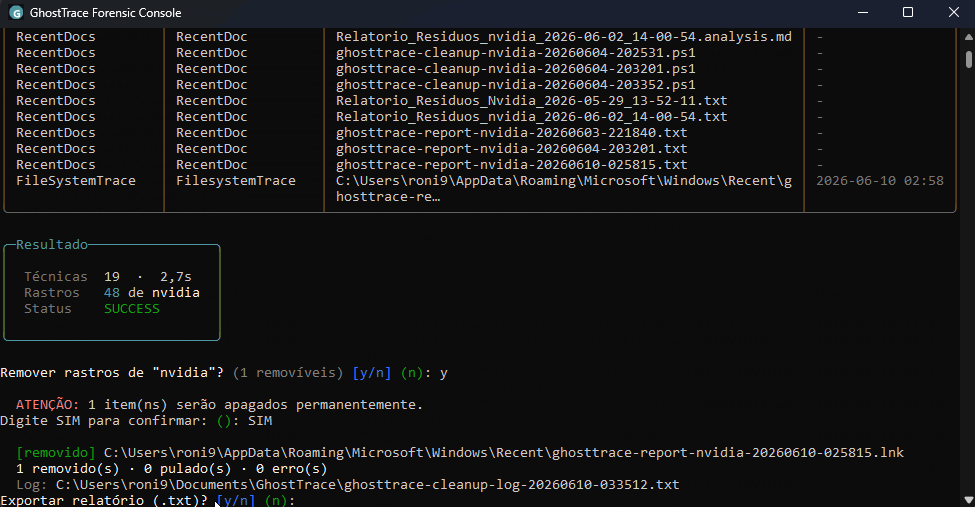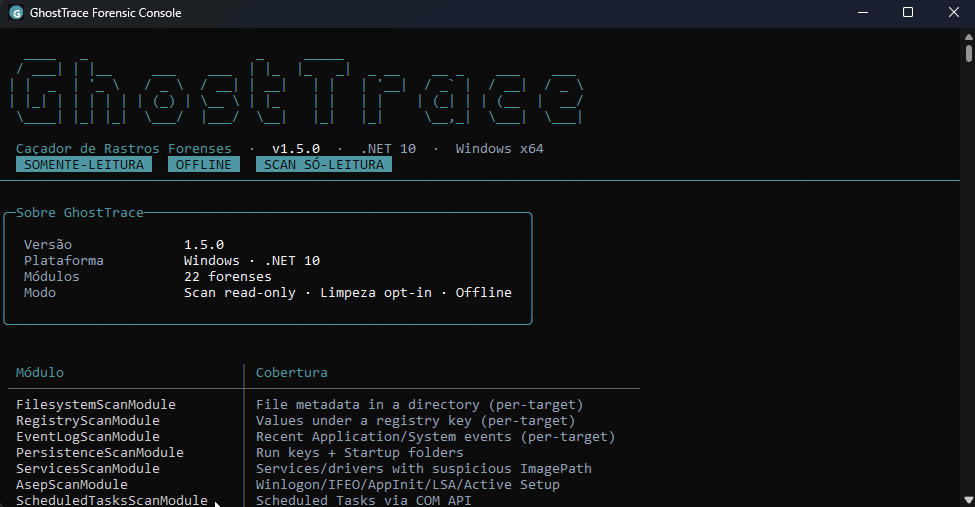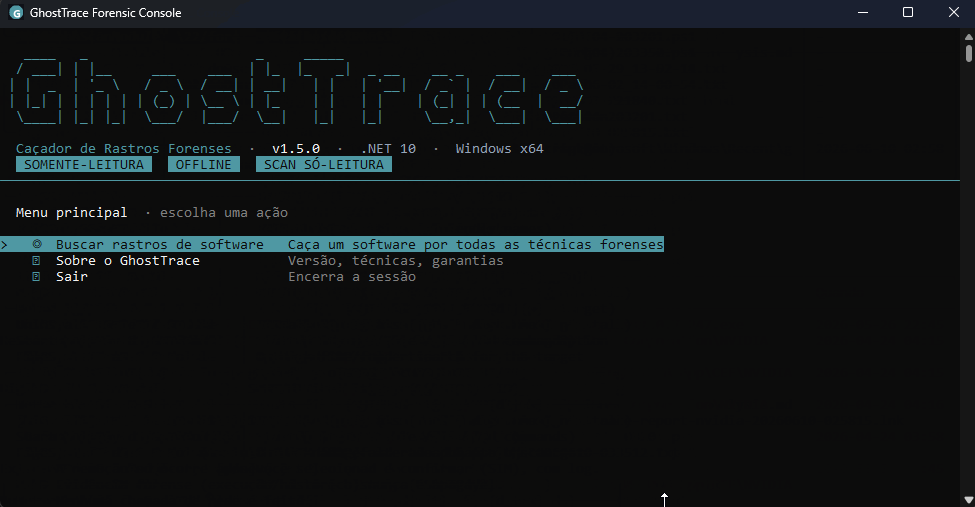 devzinh/ghosttrace
Read-only Windows forensic scanner for software traces — persistence, execution artifacts (Prefetch, Shimcache, BAM), user activity and Ghost Tasks…
 tufanturhan/cve-2022-21971-windows-runtime-rce
Proof-of-concept exploit for CVE-2022-21971, an uninitialized pointer free vulnerability in Windows Runtime's prauthproviders.dll, triggered via…
 sandi-go/cve-2018-8389
Technical analysis and proof-of-concept for CVE-2018-8389, a use-after-free vulnerability in Internet Explorer's jscript.dll allowing remote code…
 0vercl0k/cve-2022-21971
PoC for CVE-2022-21971 "Windows Runtime Remote Code Execution Vulnerability"
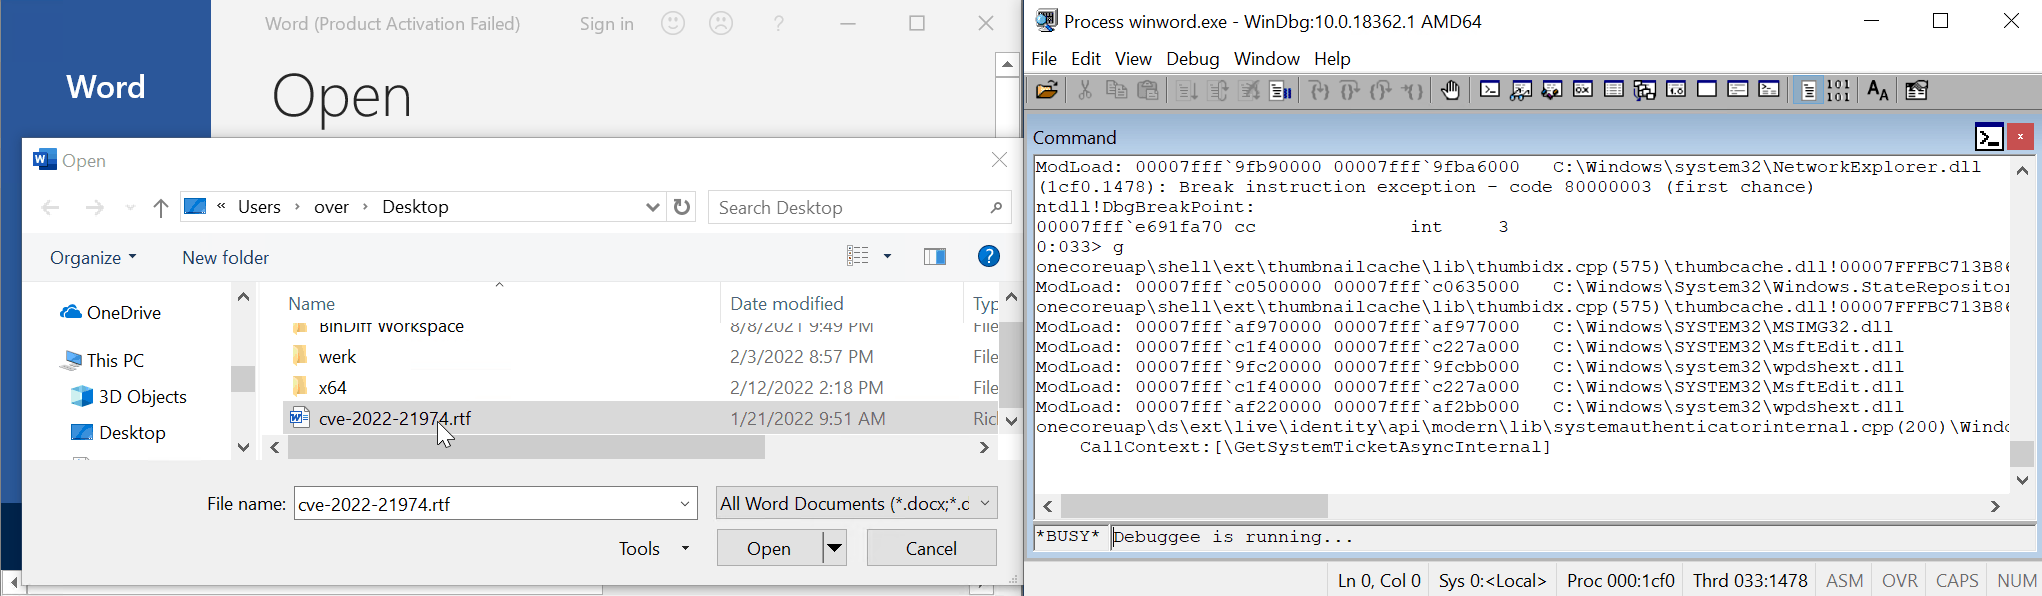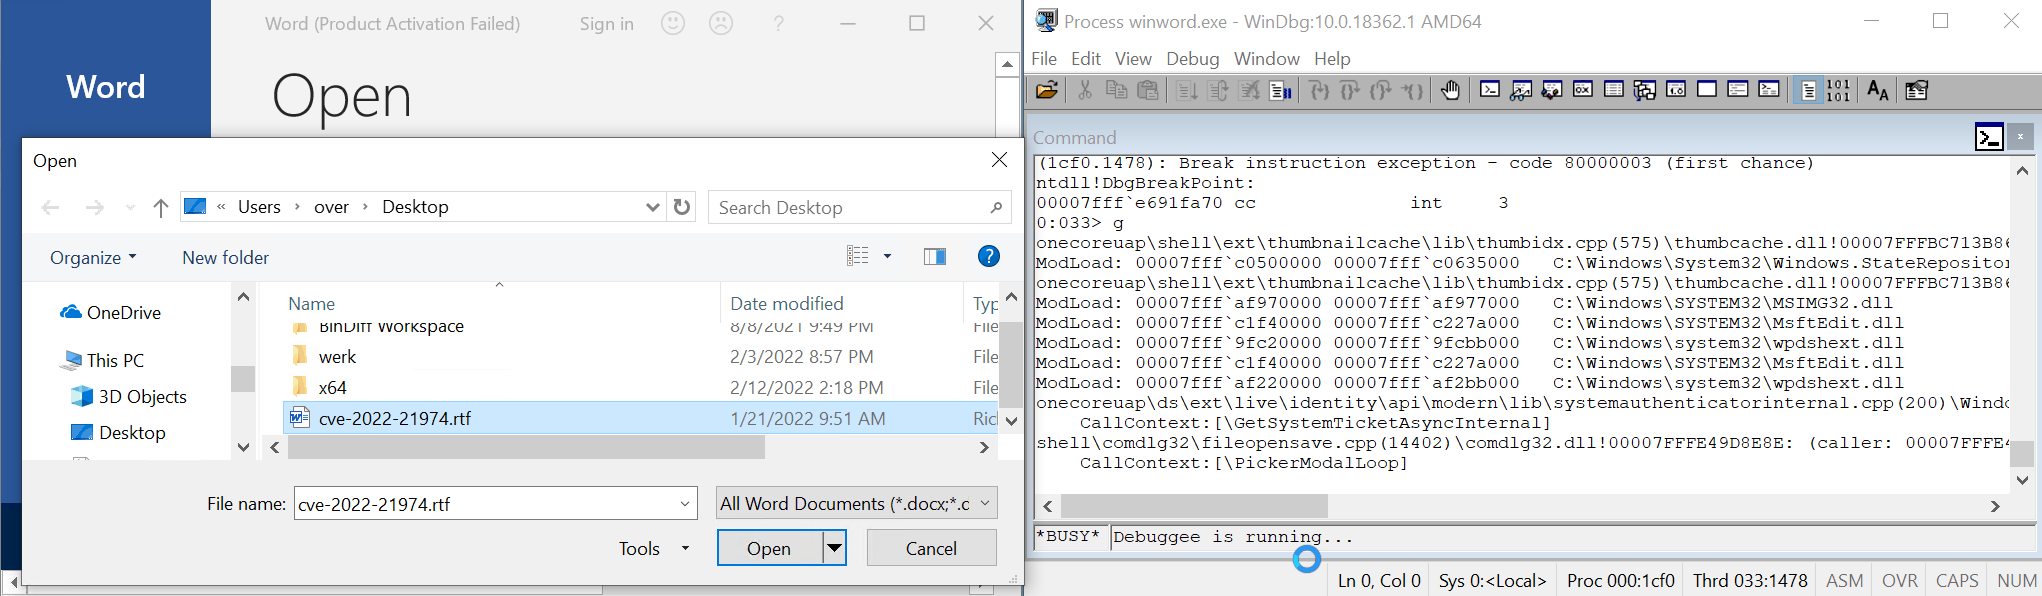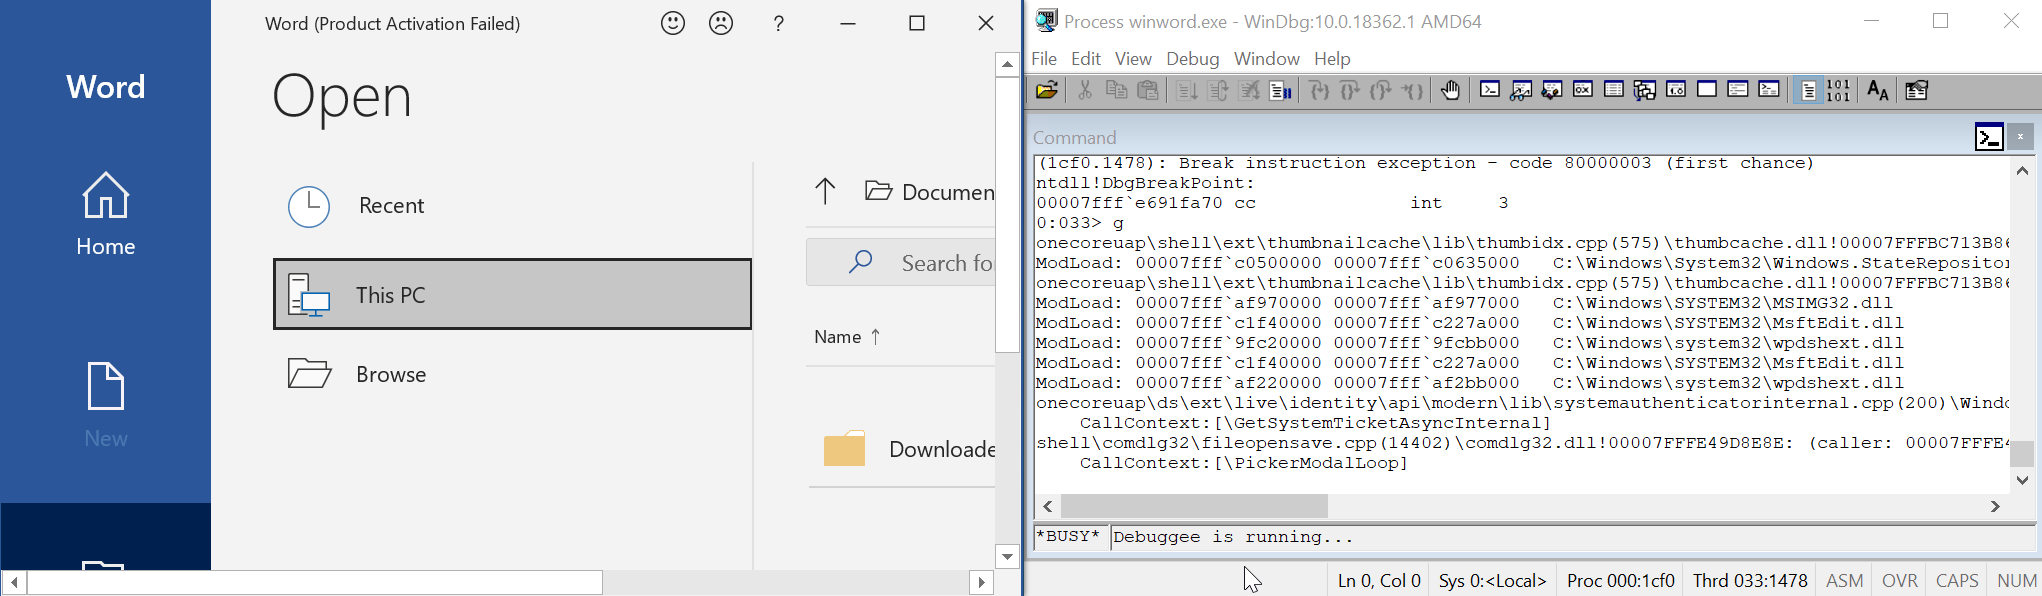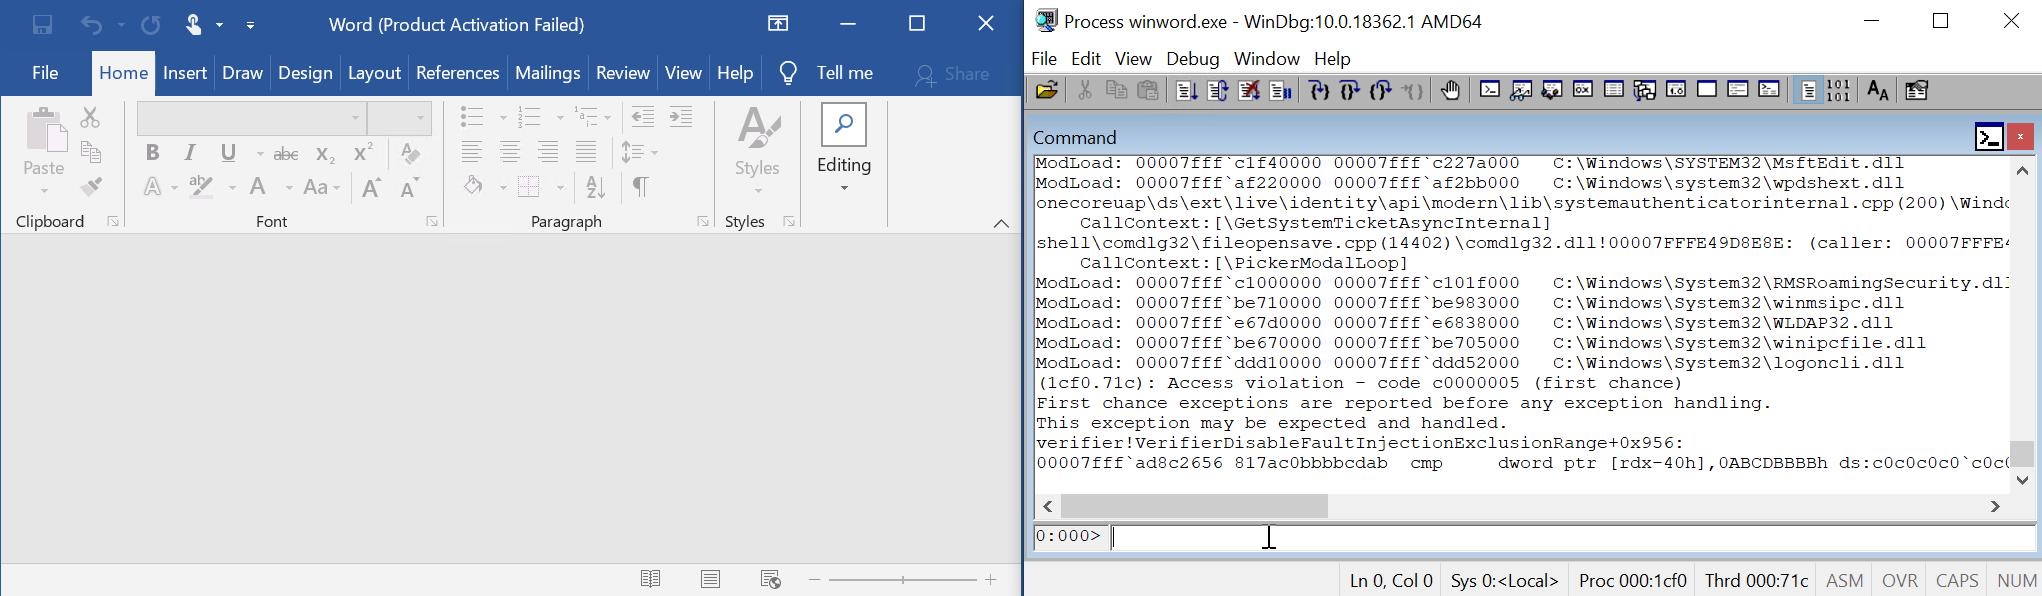 0vercl0k/cve-2022-21974
PoC for CVE-2022-21974 "Roaming Security Rights Management Services Remote Code Execution Vulnerability"
 xchwarze/magic-extractor
Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.
 tamirzb/cve-2017-13253
PoC code for CVE-2017-13253
 jvidhan/cve-2026-43687
Reverse engineering notes and a self-contained PoC for the macOS NFS client access-cache race (CVE-2026-43687), with kext disassembly diff and dtrace…
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…