

ModuleShifting
 naksyn/moduleshifting
Stealthier variation of Module Stomping and Module Overloading injection techniques that reduces memory IoCs. Implemented in Python ctypes
binary-exploitationmemory-forensicspayload-development+1
135
naksyn/moduleshiftingStealthier variation of Module Stomping and Module Overloading injection techniques that reduces memory IoCs. Implemented in Python ctypes
 whw0x455/cve-2023-41992
Proof-of-concept for CVE-2023-41992, a macOS kernel vulnerability, demonstrating exploitation techniques and providing a patch analysis.
 hoangprod/cve-2021-31956-poc
Proof-of-concept exploit for CVE-2021-31956, a Windows kernel NTFS elevation-of-privilege vulnerability. Demonstrates exploitation techniques…
 rebelle3/cve-2017-7117
Educational exploit for CVE-2017-7117, a type-confusion and use-after-free vulnerability in iOS 10.3.4 JavaScriptCore, demonstrating memory spraying…
 datntsec/cve-2020-1206
Technical analysis of CVE-2020-1206 (SMBleed) kernel information disclosure vulnerability in Windows SMBv3, including unauthenticated memory leak…
 day6reak/cve-2014-1773
Technical analysis of CVE-2014-1773, a heap corruption vulnerability in Internet Explorer's MSHTML engine, with detailed crash callstack,…
 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
 marcosd4h/memhunter
Live hunting of code injection techniques
 0xsp-srd/aether
Windows memory-forensics and threat hunting tool that scans live process memory for malicious patterns, injection techniques, and reflectively loaded…
 withsecurelabs/volatility-plugins
Volatility plugins for memory forensics, including detection of Gargoyle memory scanning evasion techniques.
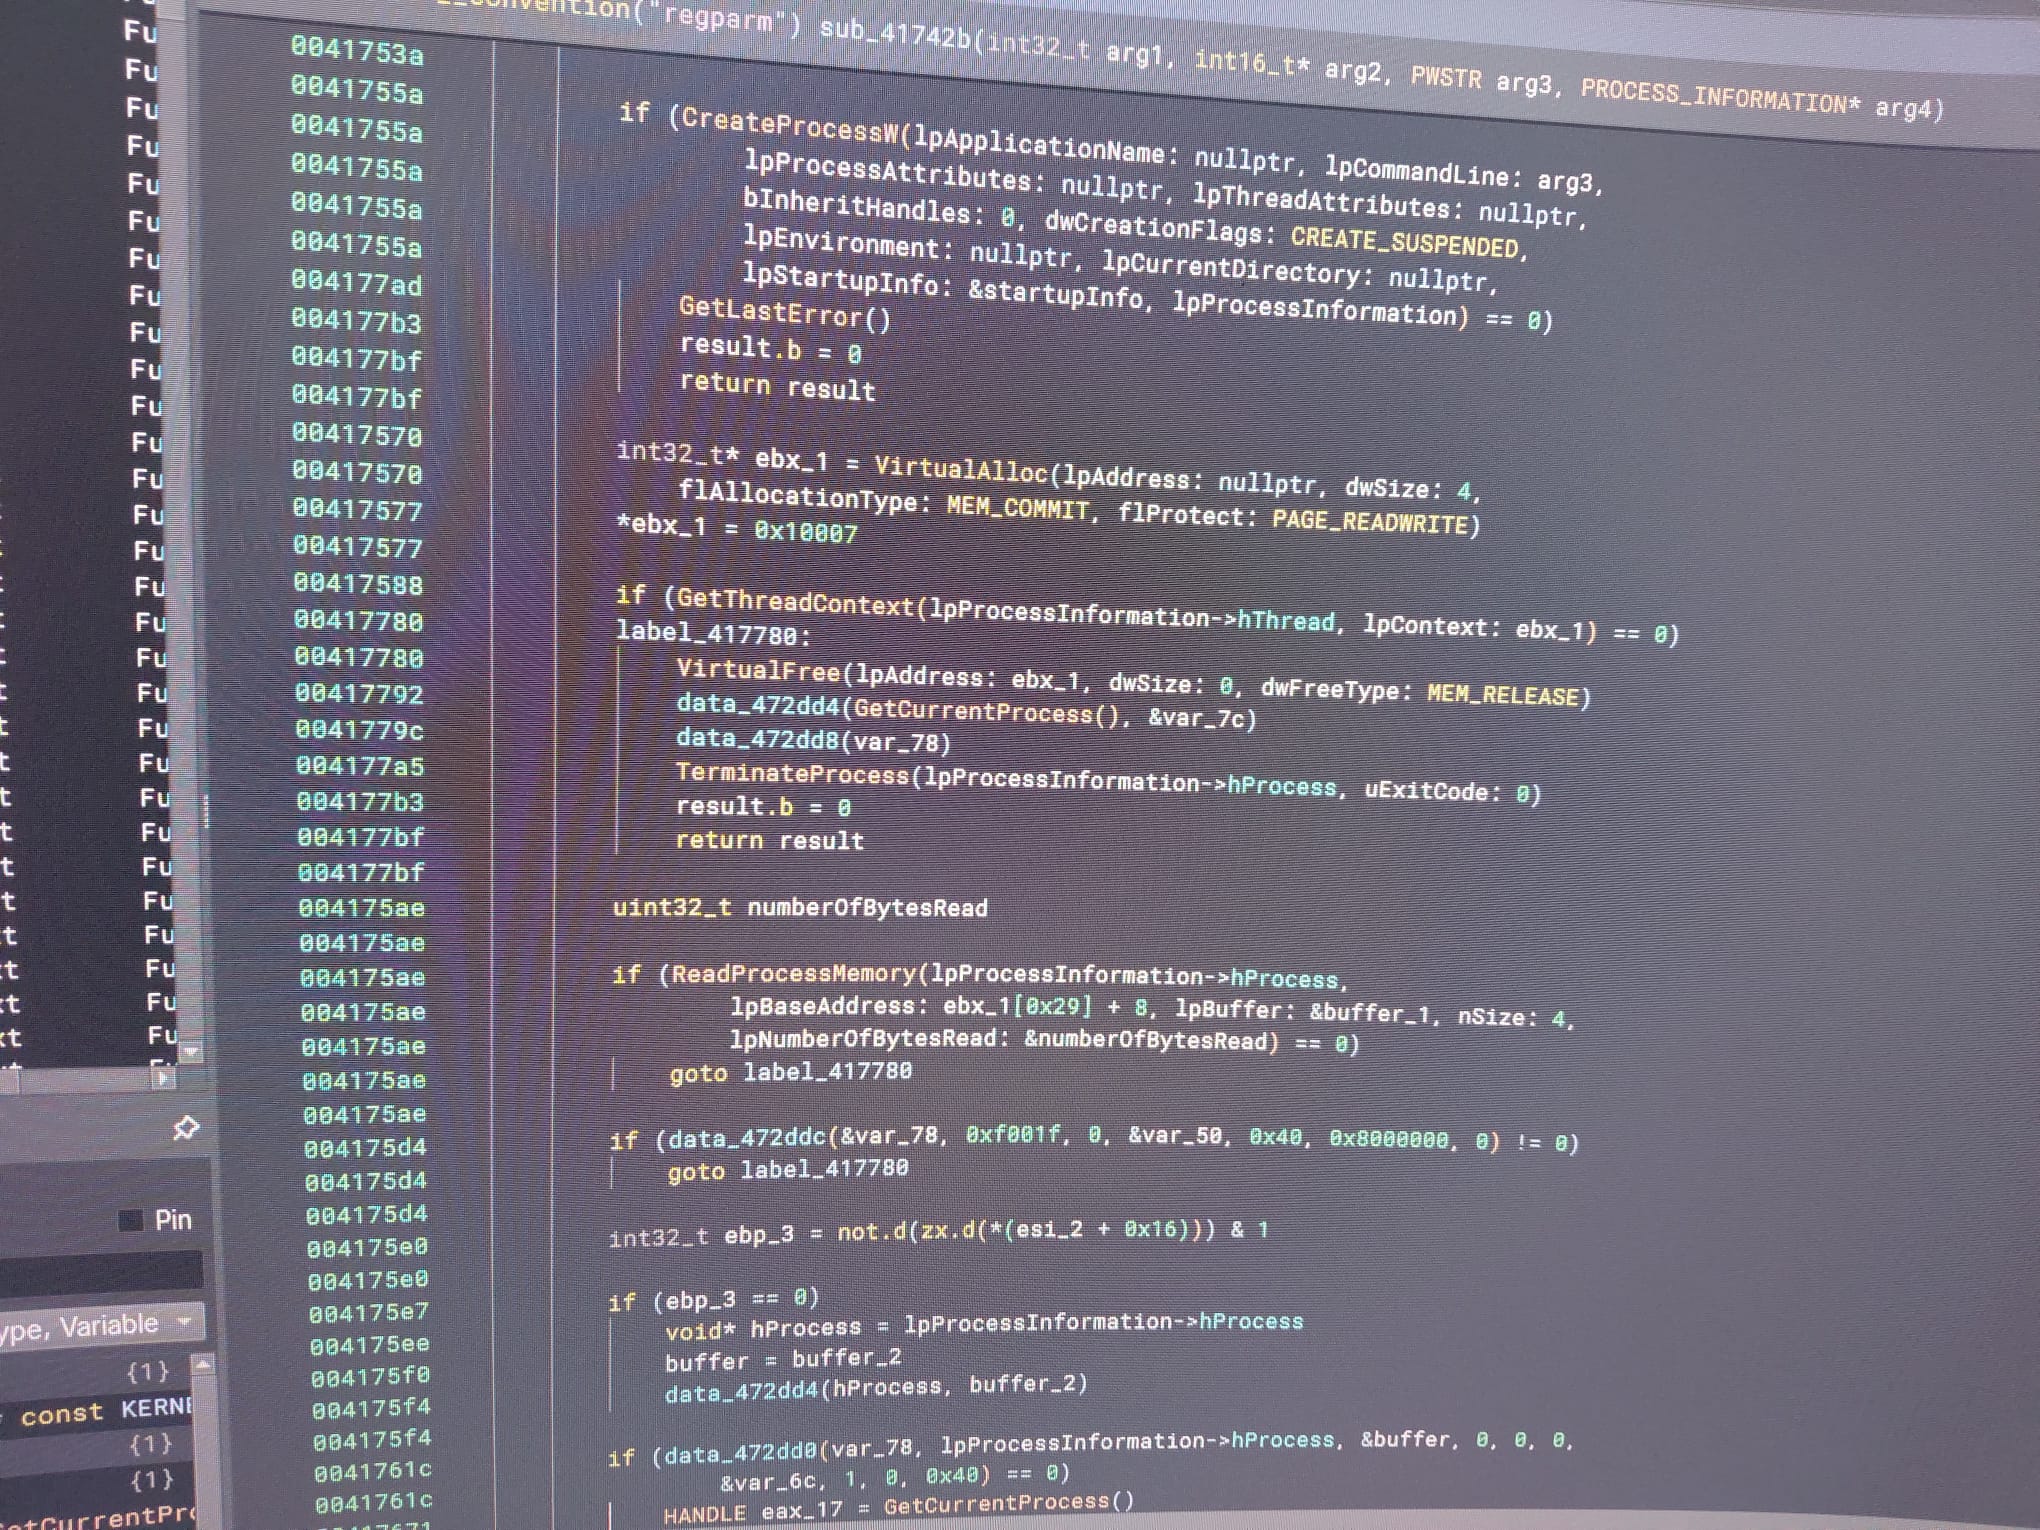 kaandemir993/-remcos-rat-fileless-svchost-injection-obfuscated-payload-analysis-
"Reverse engineering analysis of a fileless Remcos RAT variant that injects into svchost.exe via Native API calls. Covers obfuscated payload…
 adem-hosni/mappedimagesdetector
Lightweight native Windows memory scanner for AV/EDR platforms, detecting suspicious mapped images and manual DLL injection techniques by IAT thunk
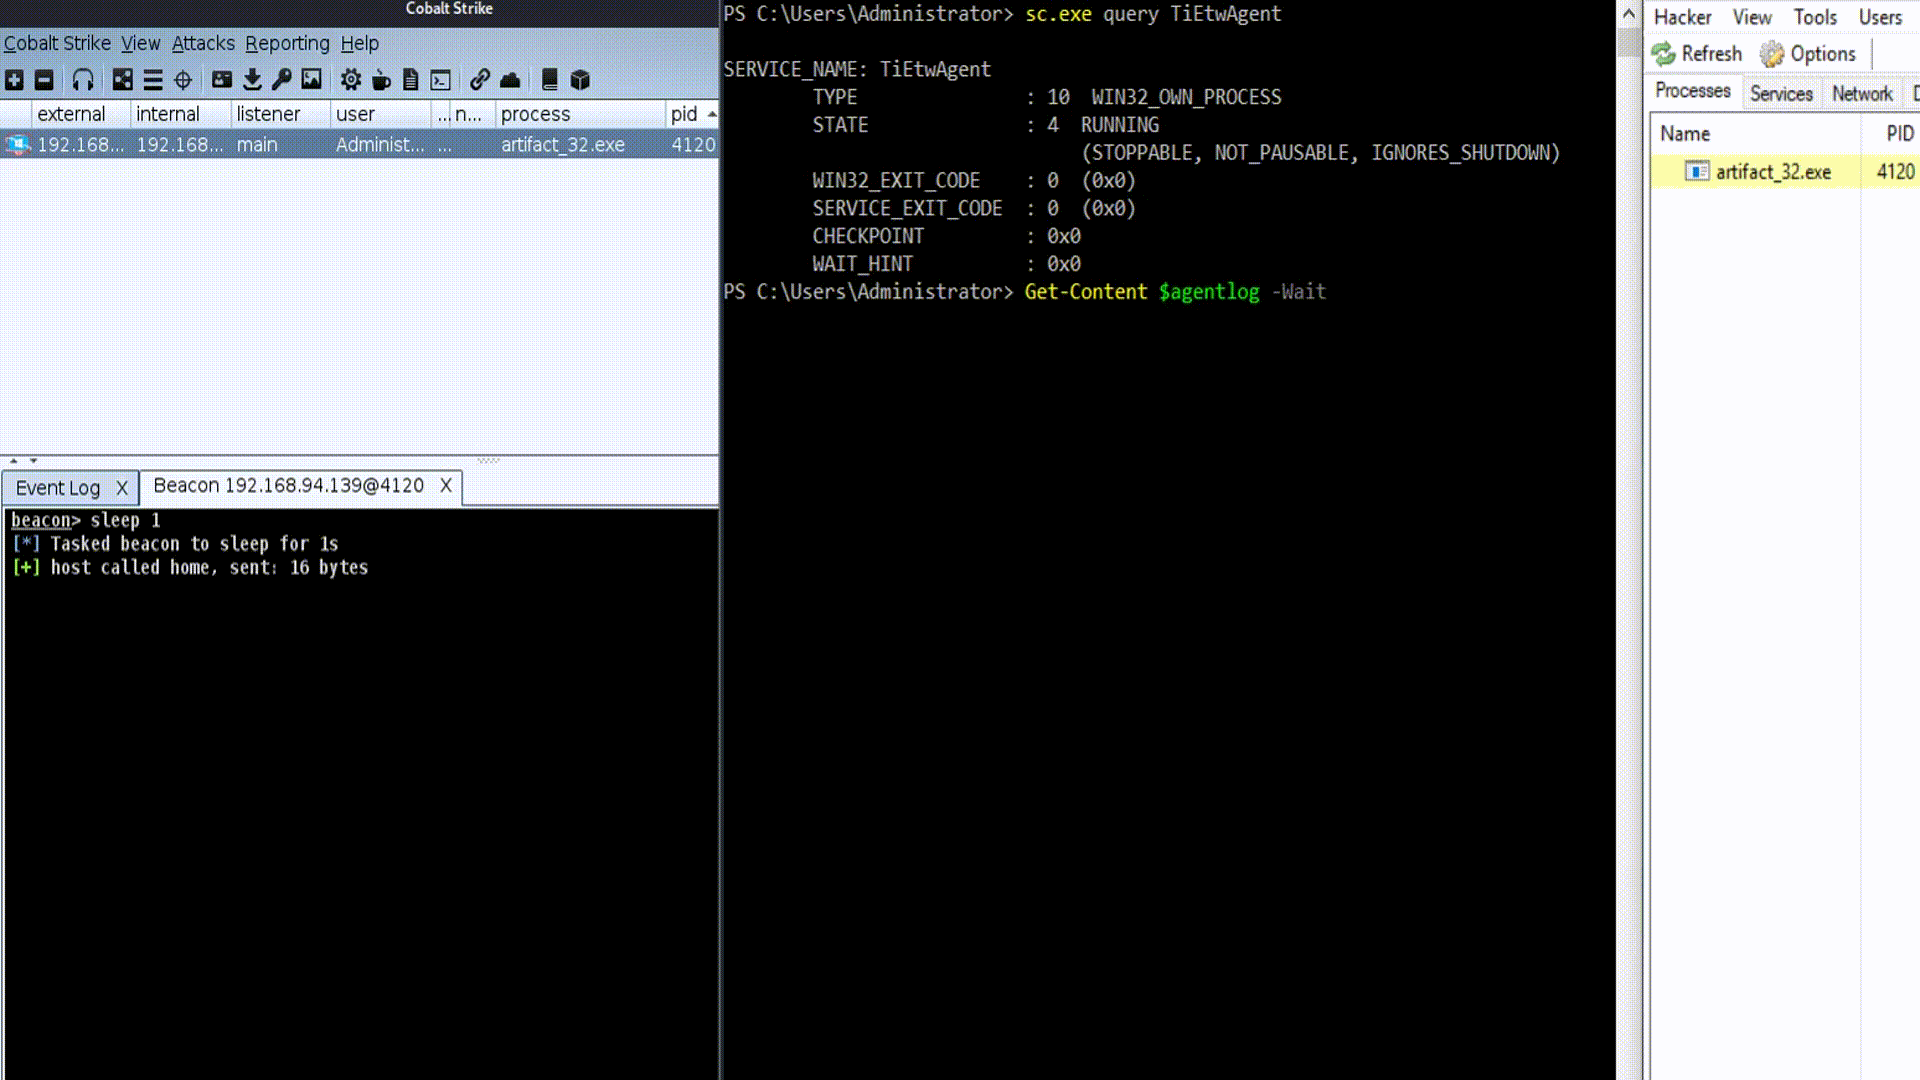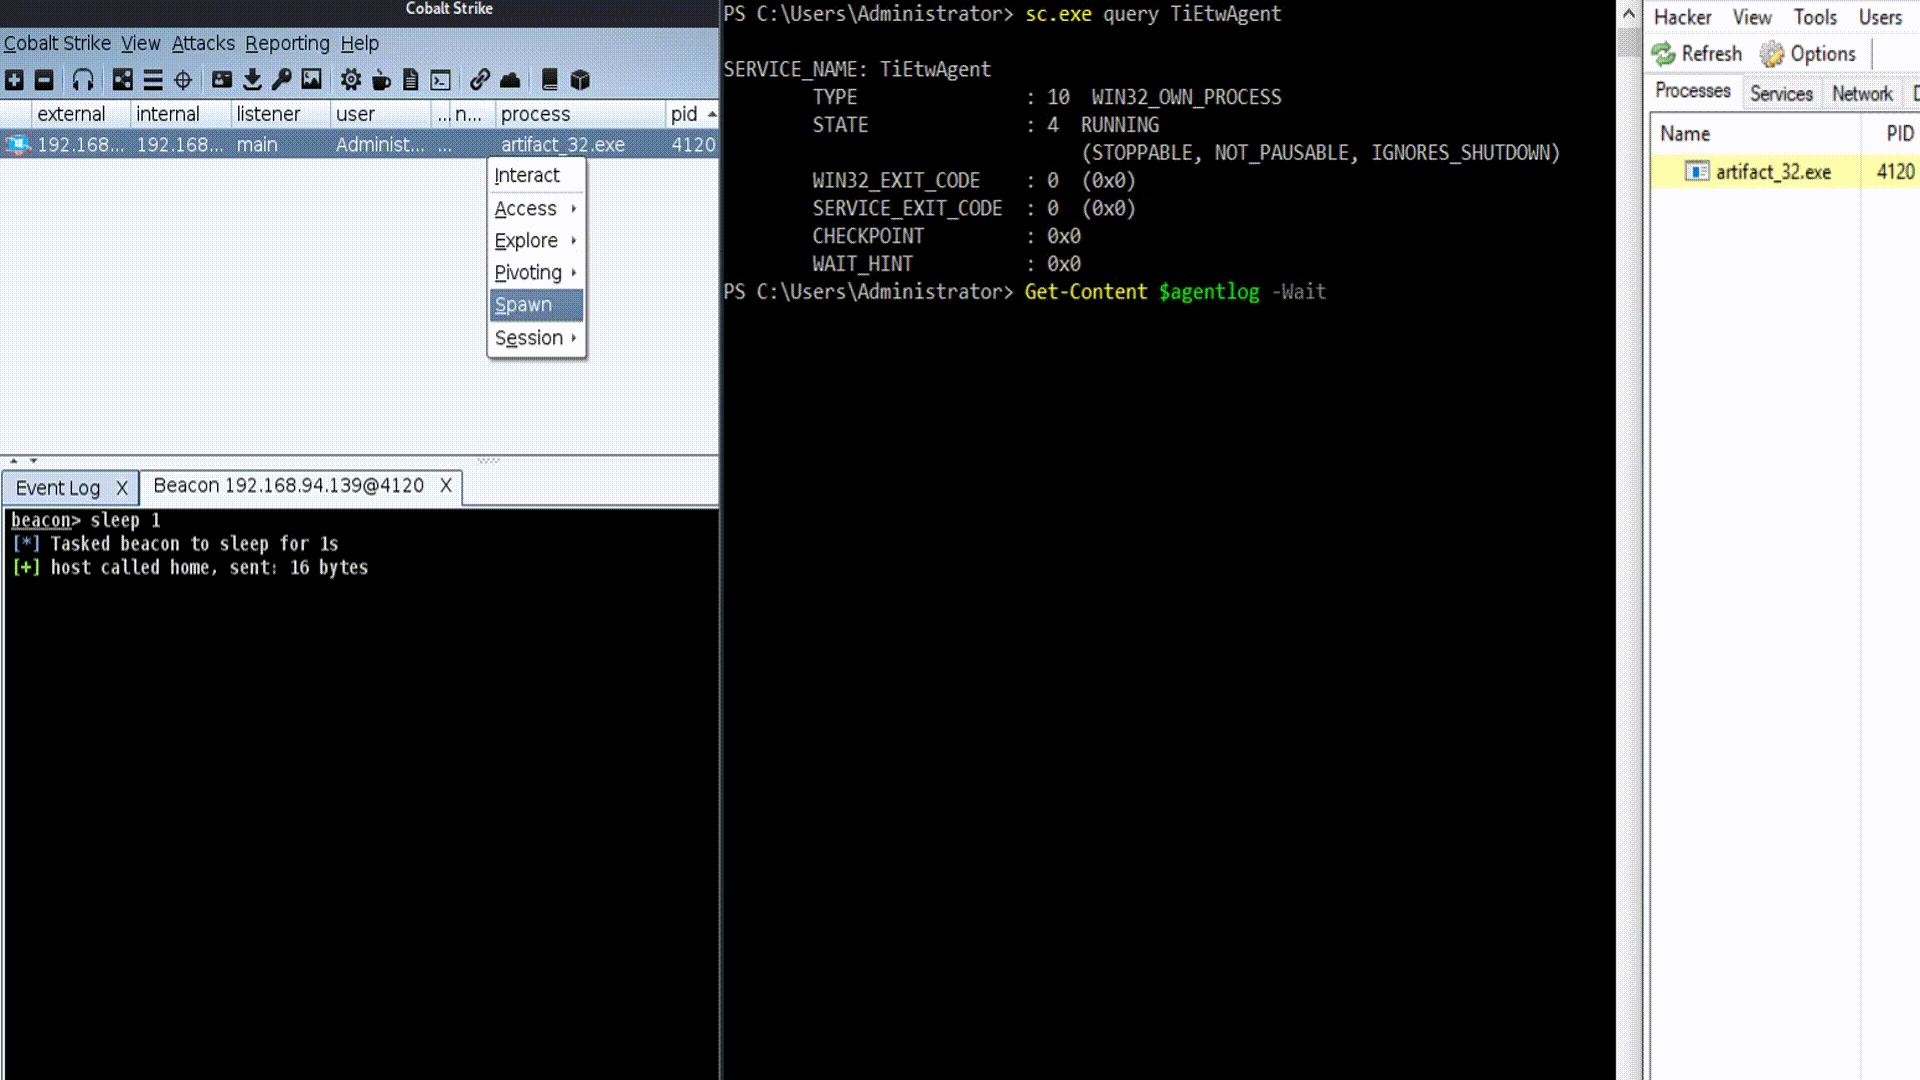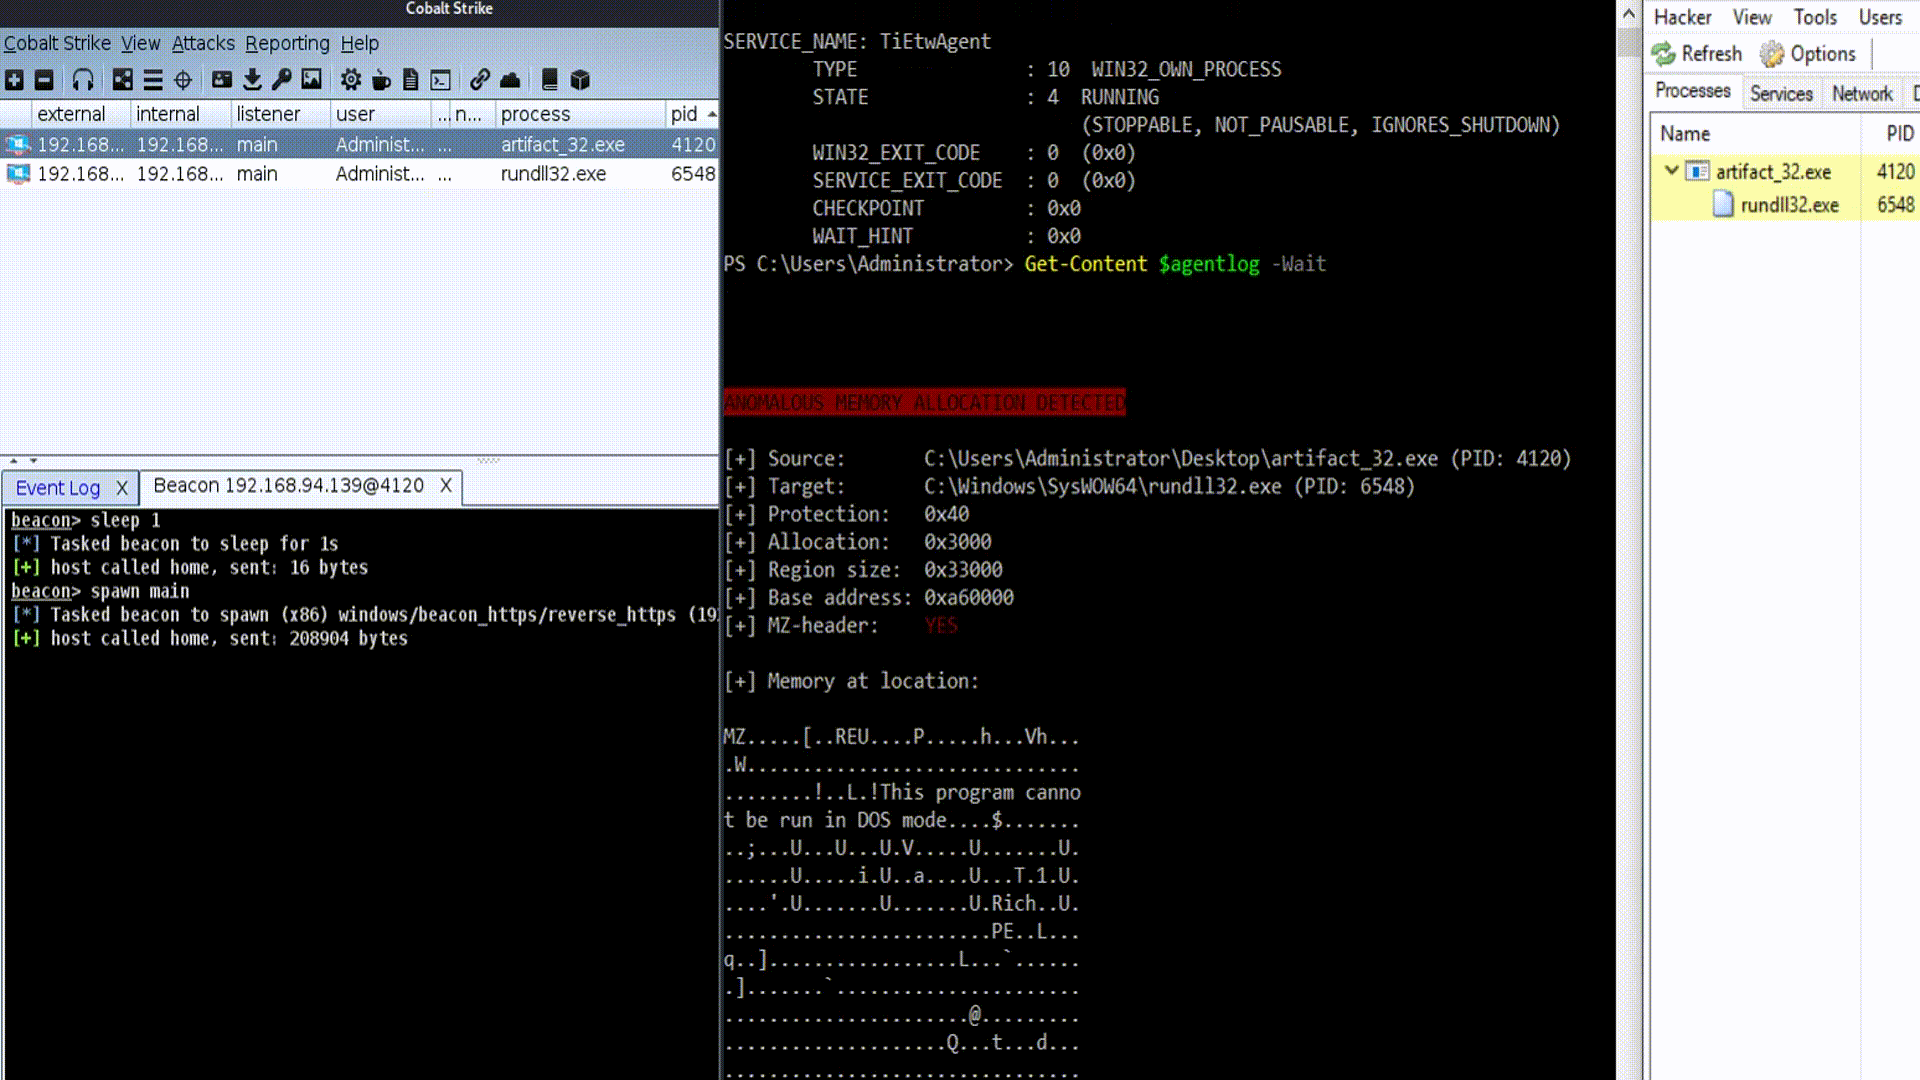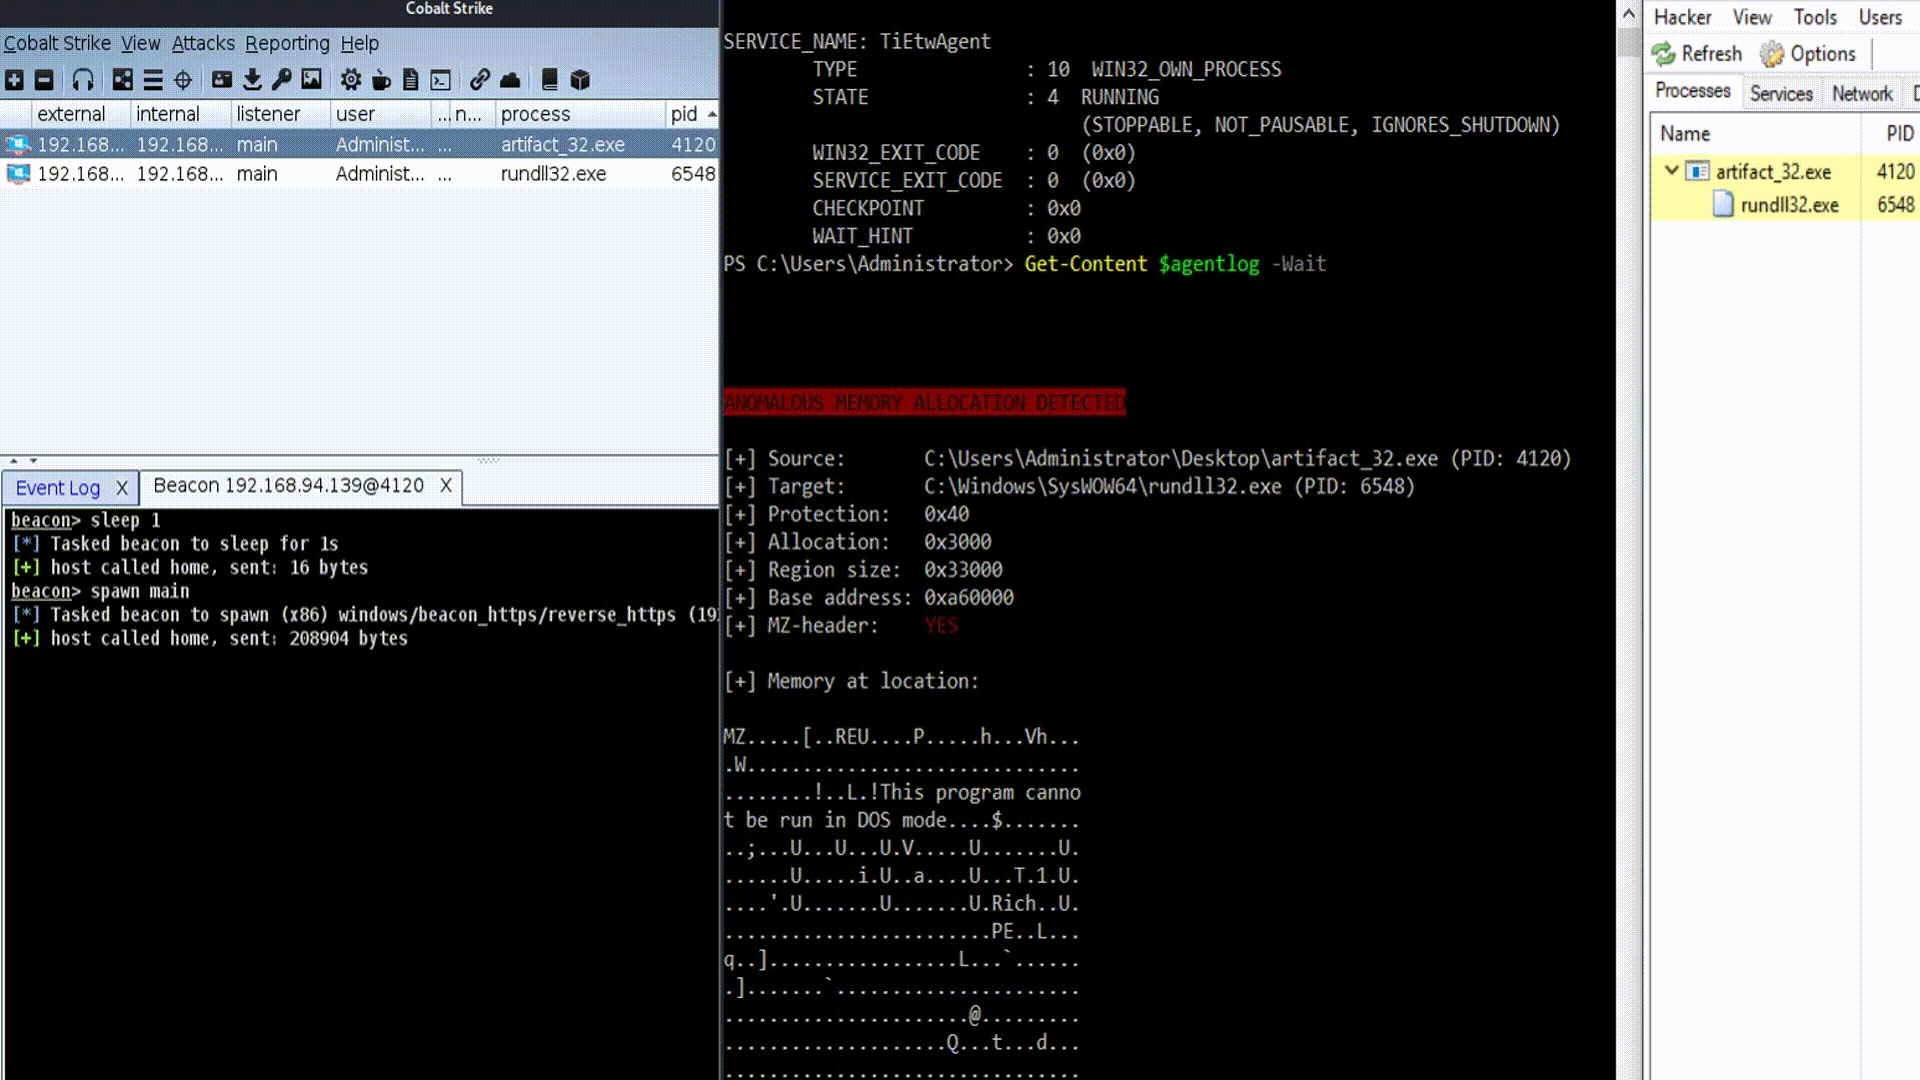 xuanxuan0/tietwagent
PoC memory injection detection agent based on ETW, for offensive and defensive research purposes
 joe-desimone/patriot
In-memory stealth detection tool that identifies process hollowing, module stomping, unbacked executable regions, and anomalous CONTEXT structures…
 cecio/xenoboxx
Hardware Sandbox Toolkit
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
 werwolv/imhex
🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy