
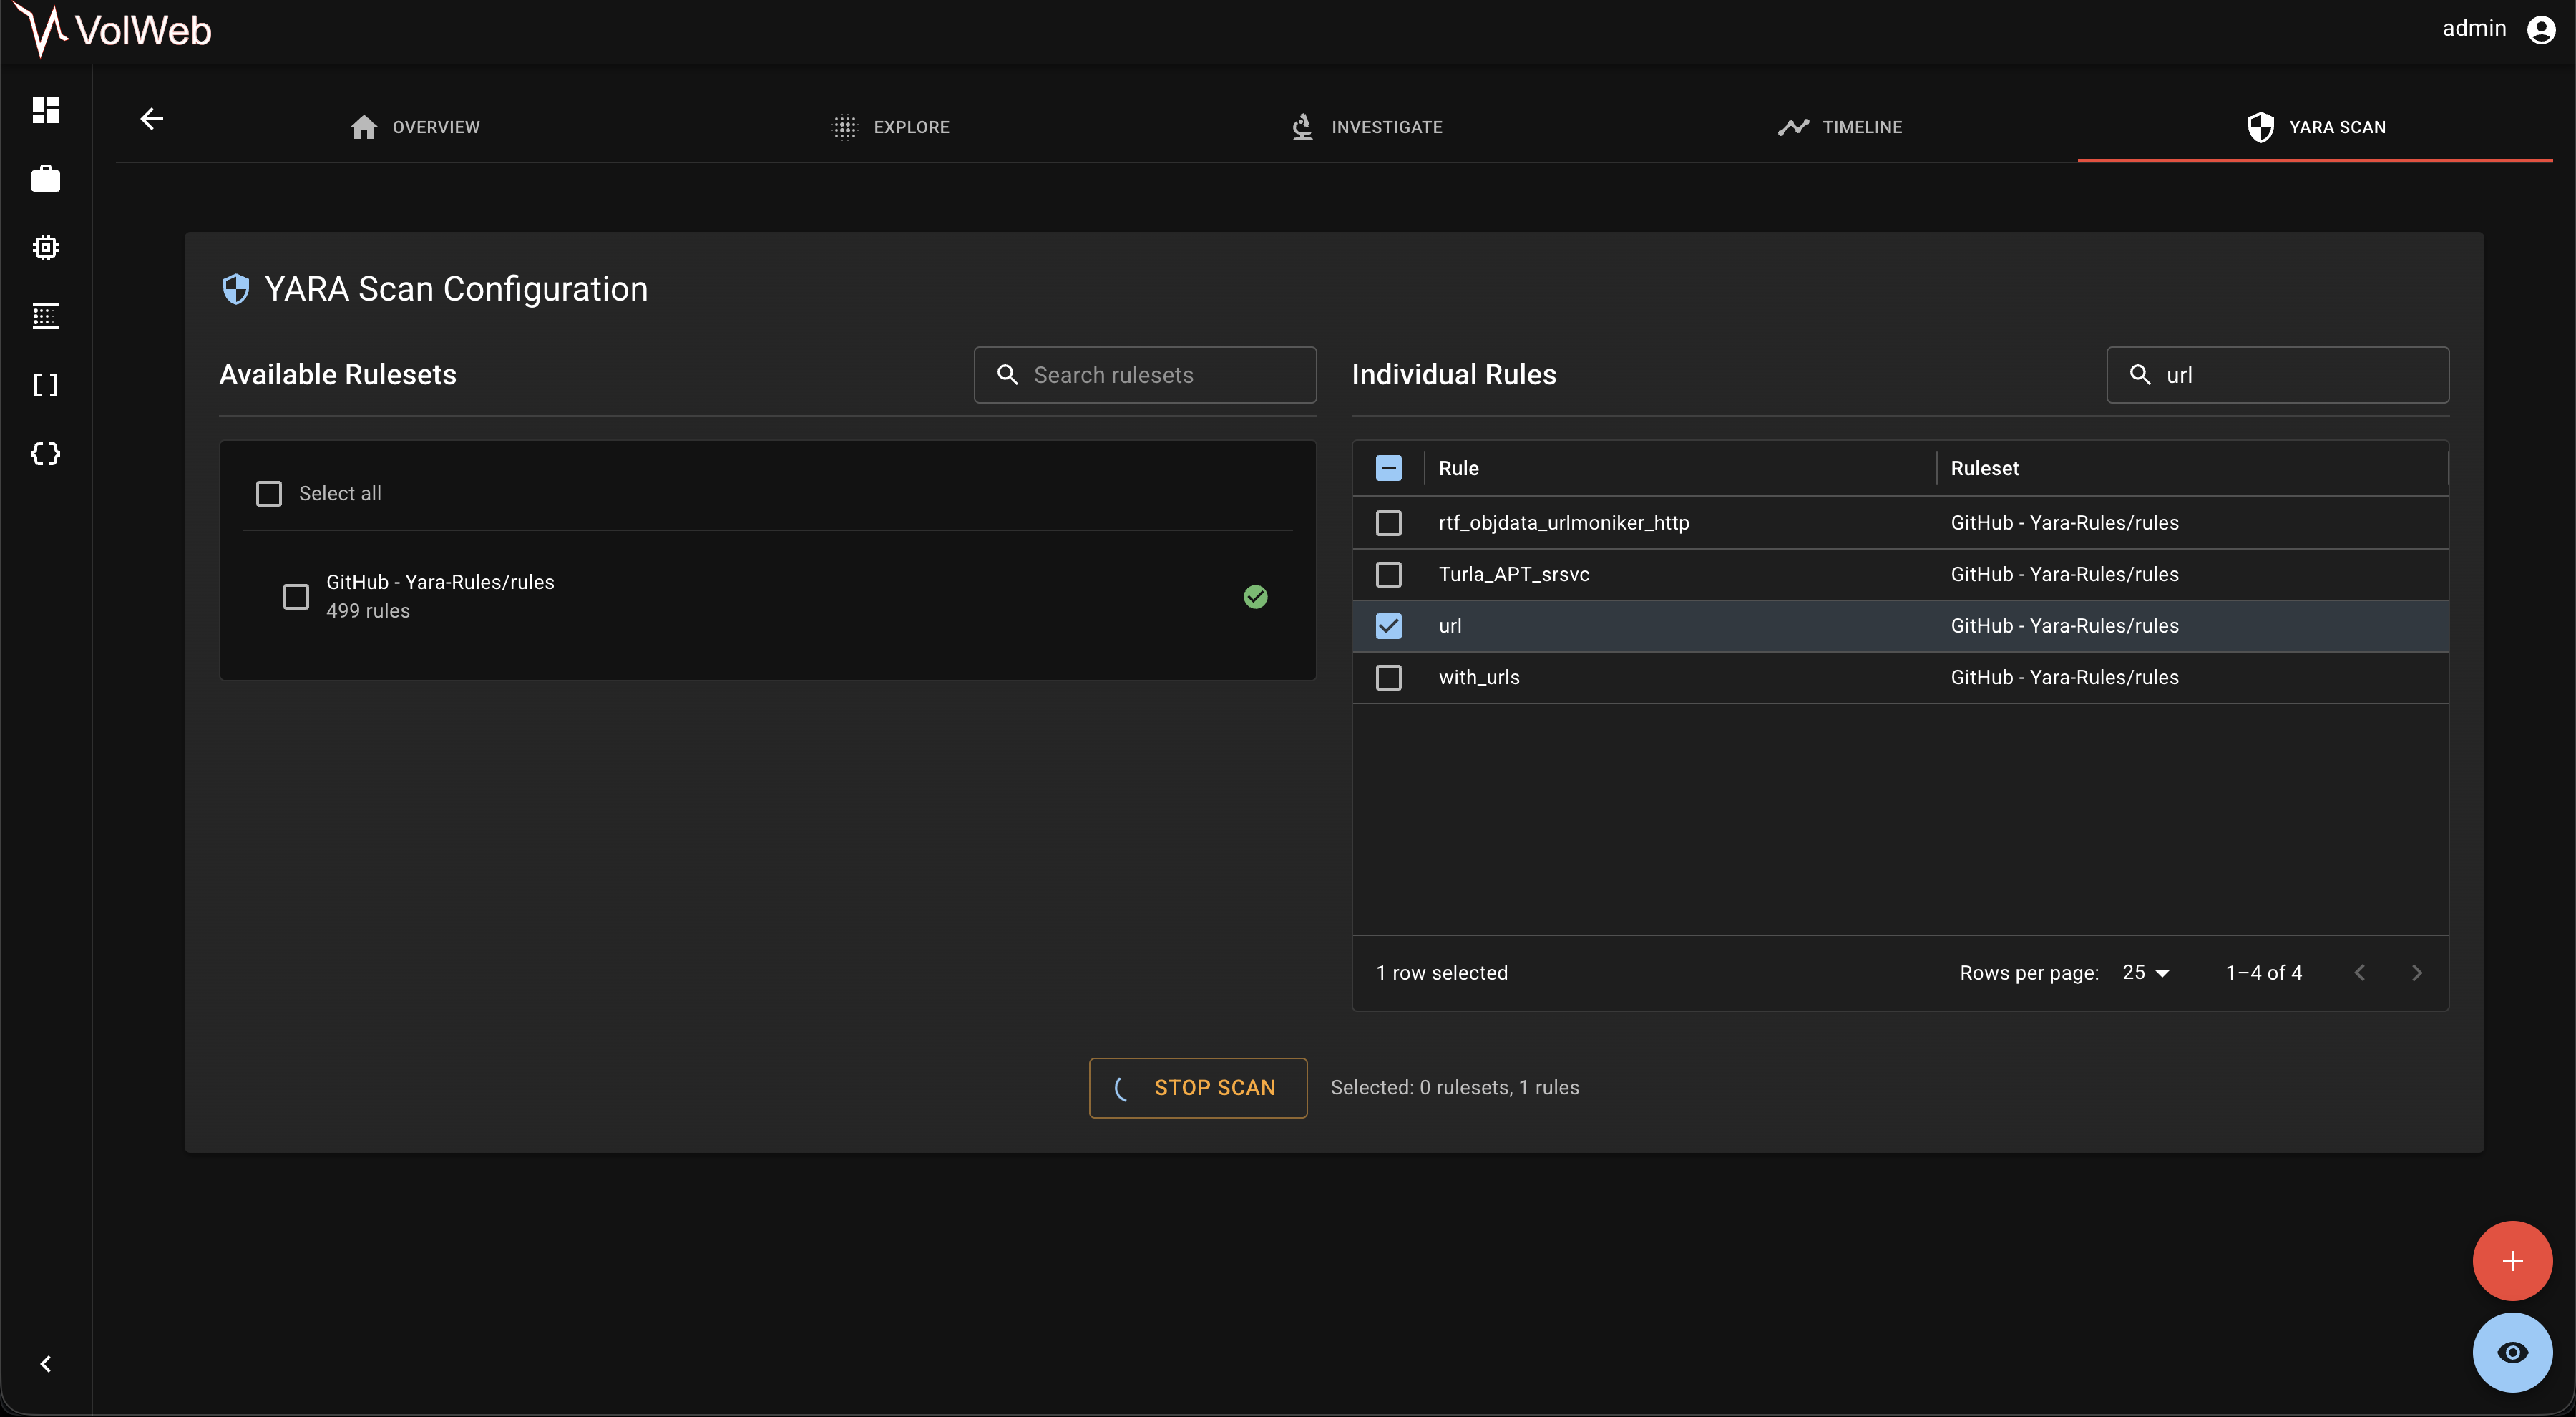
VolWeb
 k1nd0ne/volweb
A centralized and enhanced memory analysis platform
digital-forensicseducationforensics+5
k1nd0ne/volwebA centralized and enhanced memory analysis platform
 angr/angr
A powerful and user-friendly binary analysis platform!
 google/timesketch
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…
 reclassnet/reclass.net
More than a ReClass port to the .NET platform.
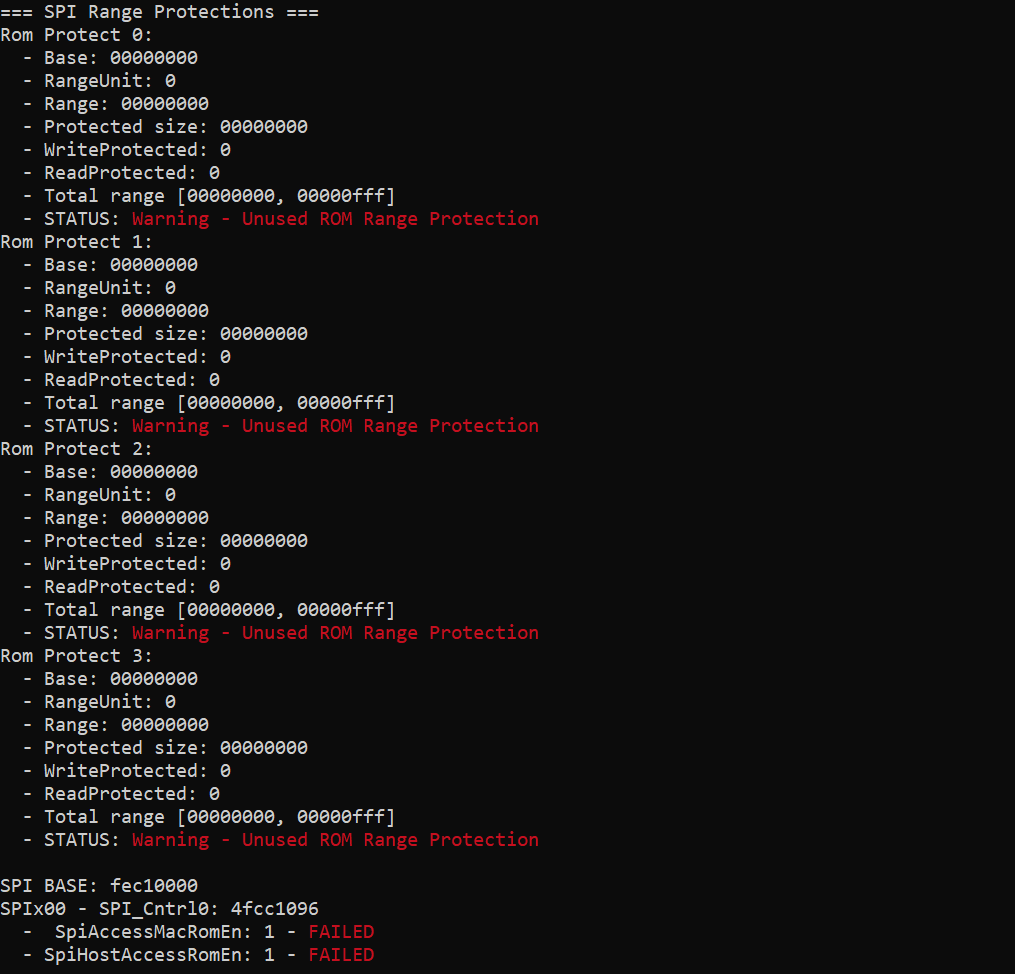 ioactive/platbox
Platform security assessment tool for dumping and analyzing UEFI/SMM registers, PCI config space, physical memory, SPI flash, and S3 bootscripts with…
 rin449/bhpai
Multi-format malware analysis platform combining a stealth Ring-3 Windows sandbox, static PE/PDF analyzers, ransomware key recovery, and an AI…
 apple-oss-distributions/xnu
Hybrid kernel combining Mach, FreeBSD, and IOKit for macOS and iOS. Provides core OS services, driver framework, and security policy enforcement on…
 cryptolok/crykex
Linux Memory Cryptographic Keys Extractor
 frida/frida-gum
Cross-platform instrumentation and introspection library written in C
 mozilla/mig
Distributed & real time digital forensics at the speed of the cloud
 frankwxu/digital-forensics-lab
Free hands-on digital forensics labs for students and faculty
 qi4l/jyso
Dual-purpose JNDI injection and Java deserialization exploitation framework with advanced bypass capabilities for WAF, RASP, and high JDK versions.…
 dump-guy/malware-analysis-and-reverse-engineering
Some of my publicly available Malware analysis and Reverse engineering.
 azr43lkn1ght/dfir-labs
Hands-on DFIR challenges covering digital forensics, incident response, malware analysis, and threat hunting with CTF-style flags and real-world…
 eugnis/spectre-attack
Example of using revealed "Spectre" exploit (CVE-2017-5753 and CVE-2017-5715)
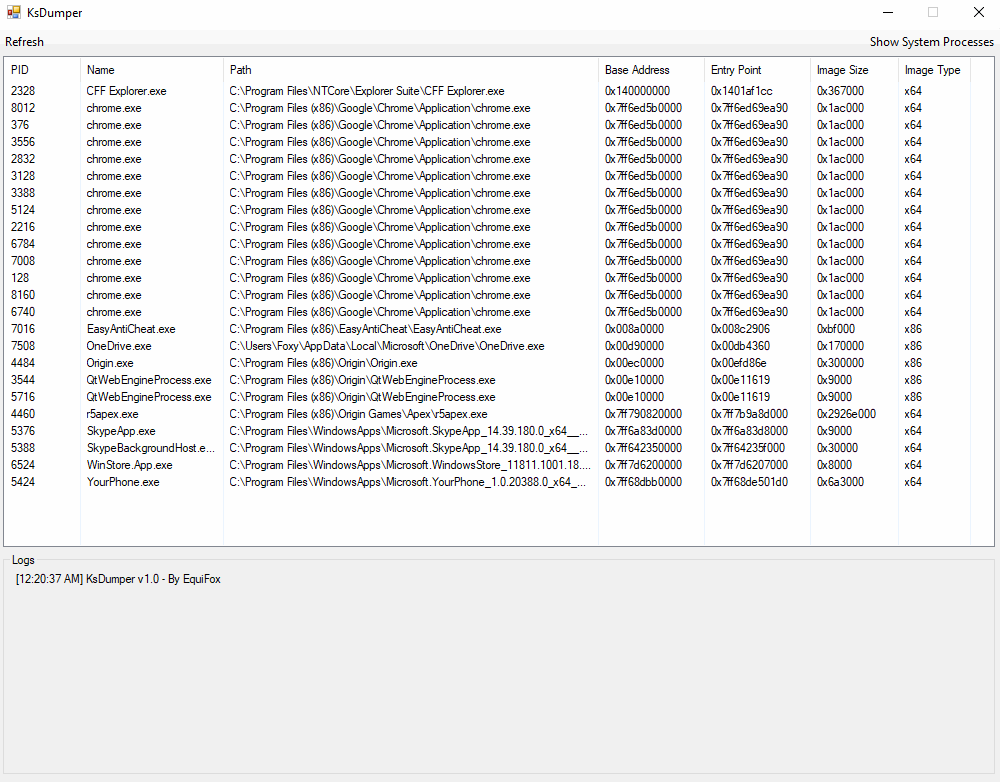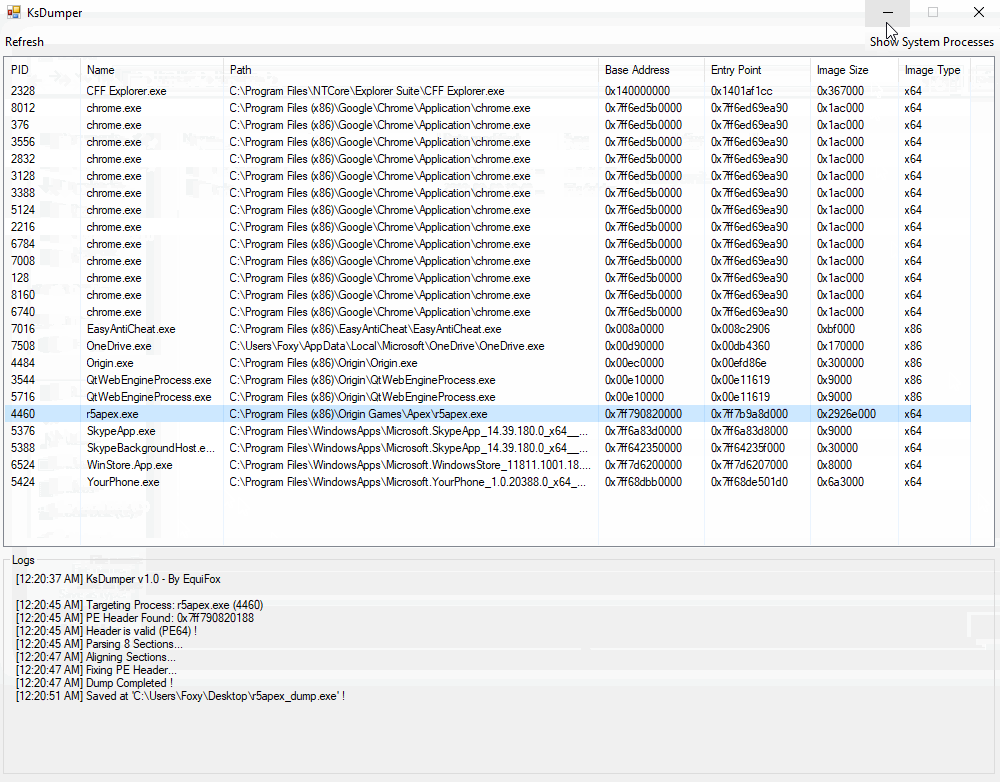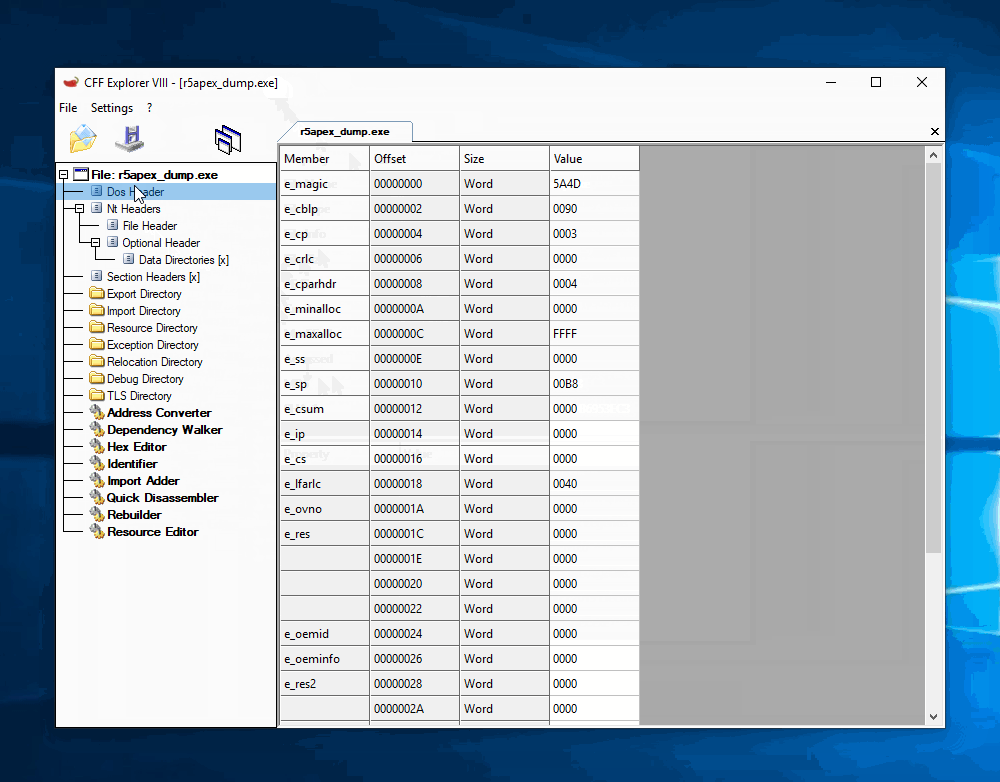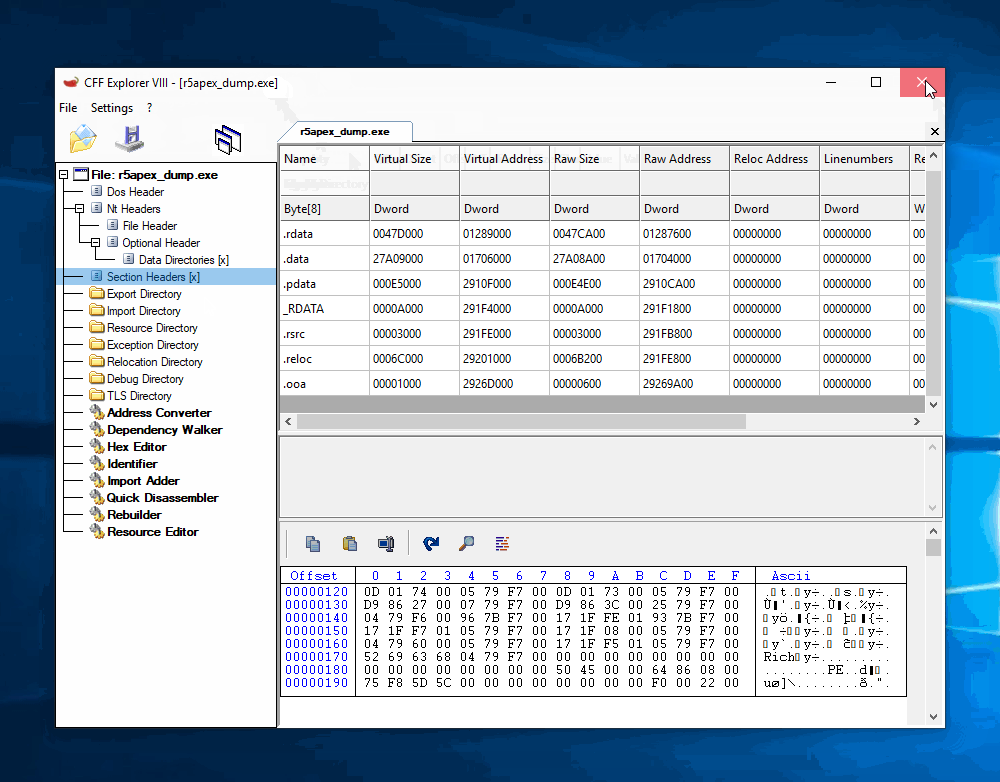 equifox/ksdumper
Dumping processes using the power of kernel space !
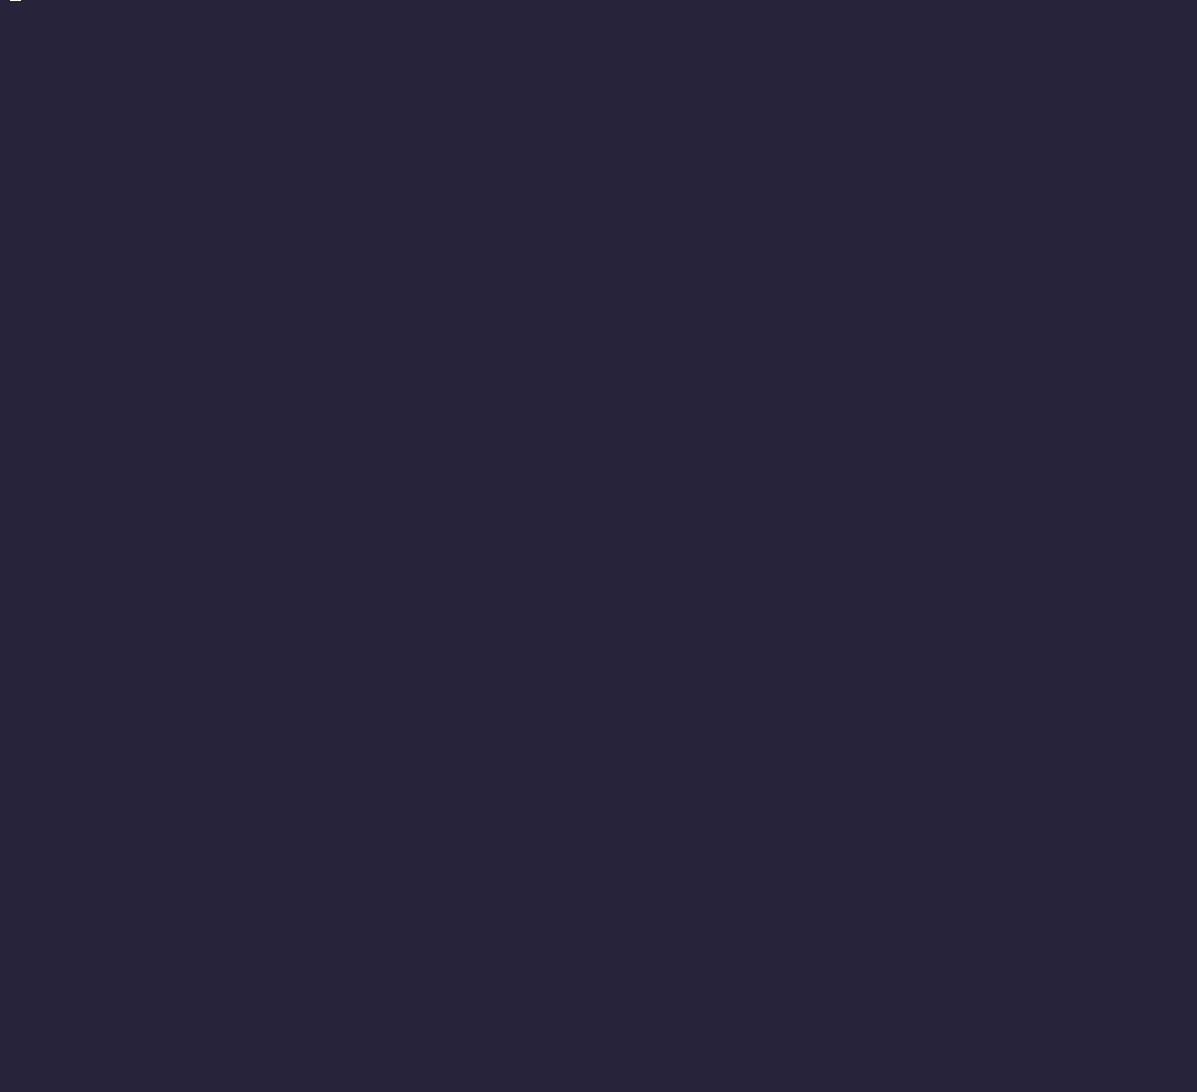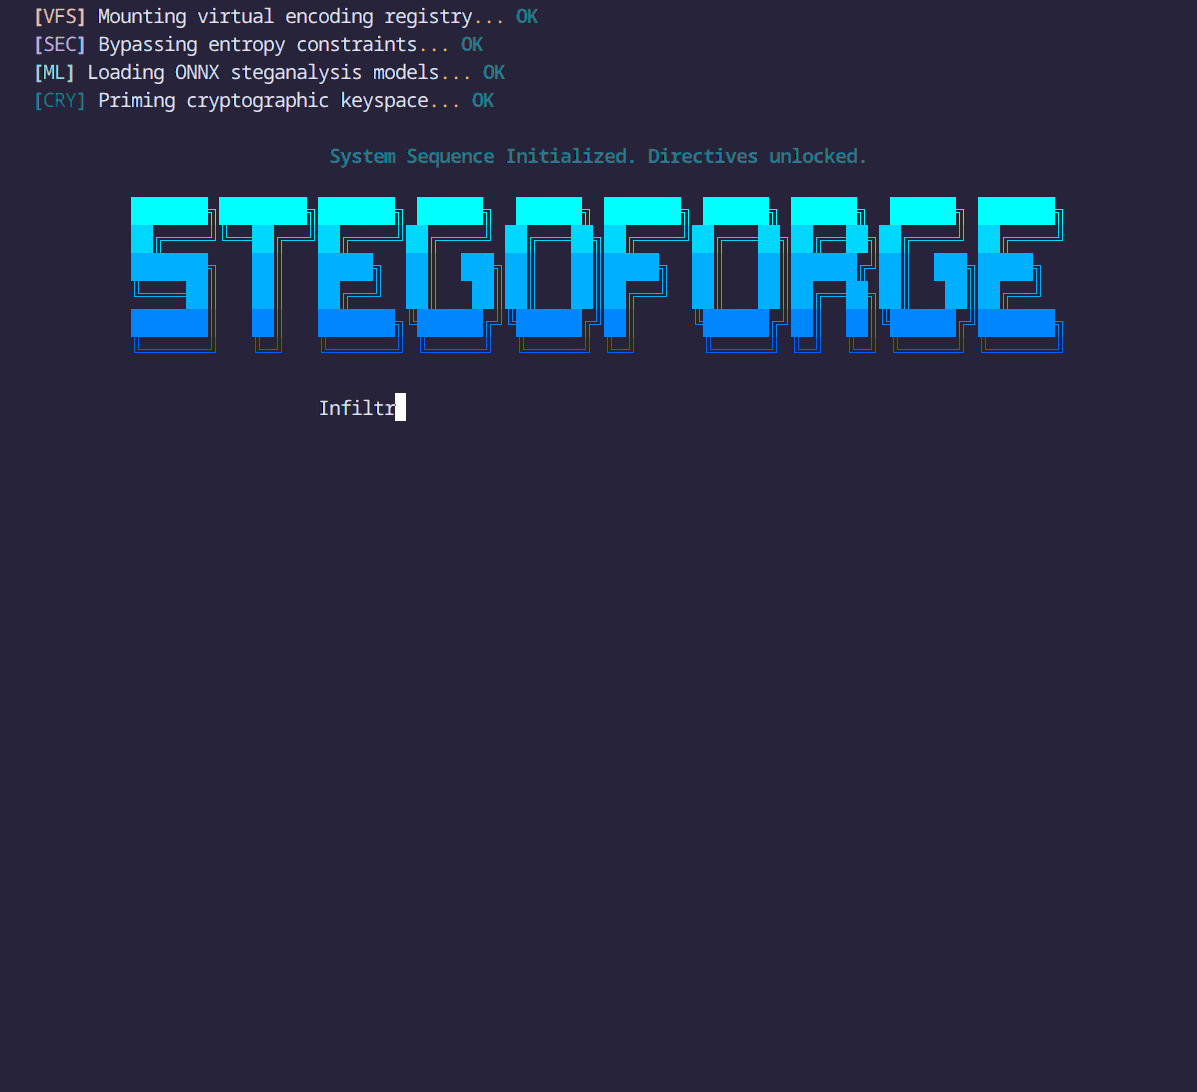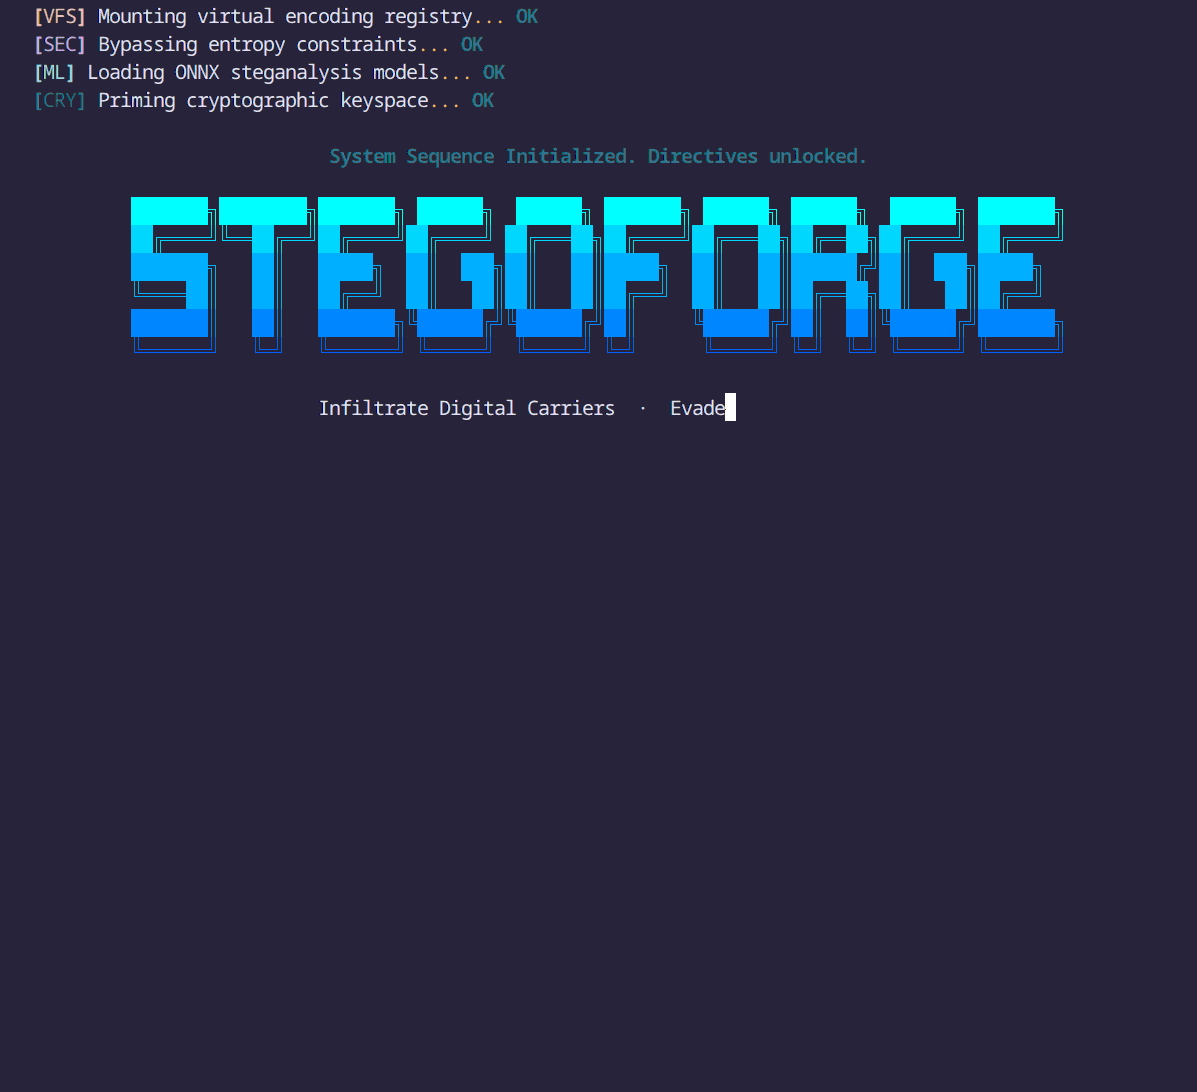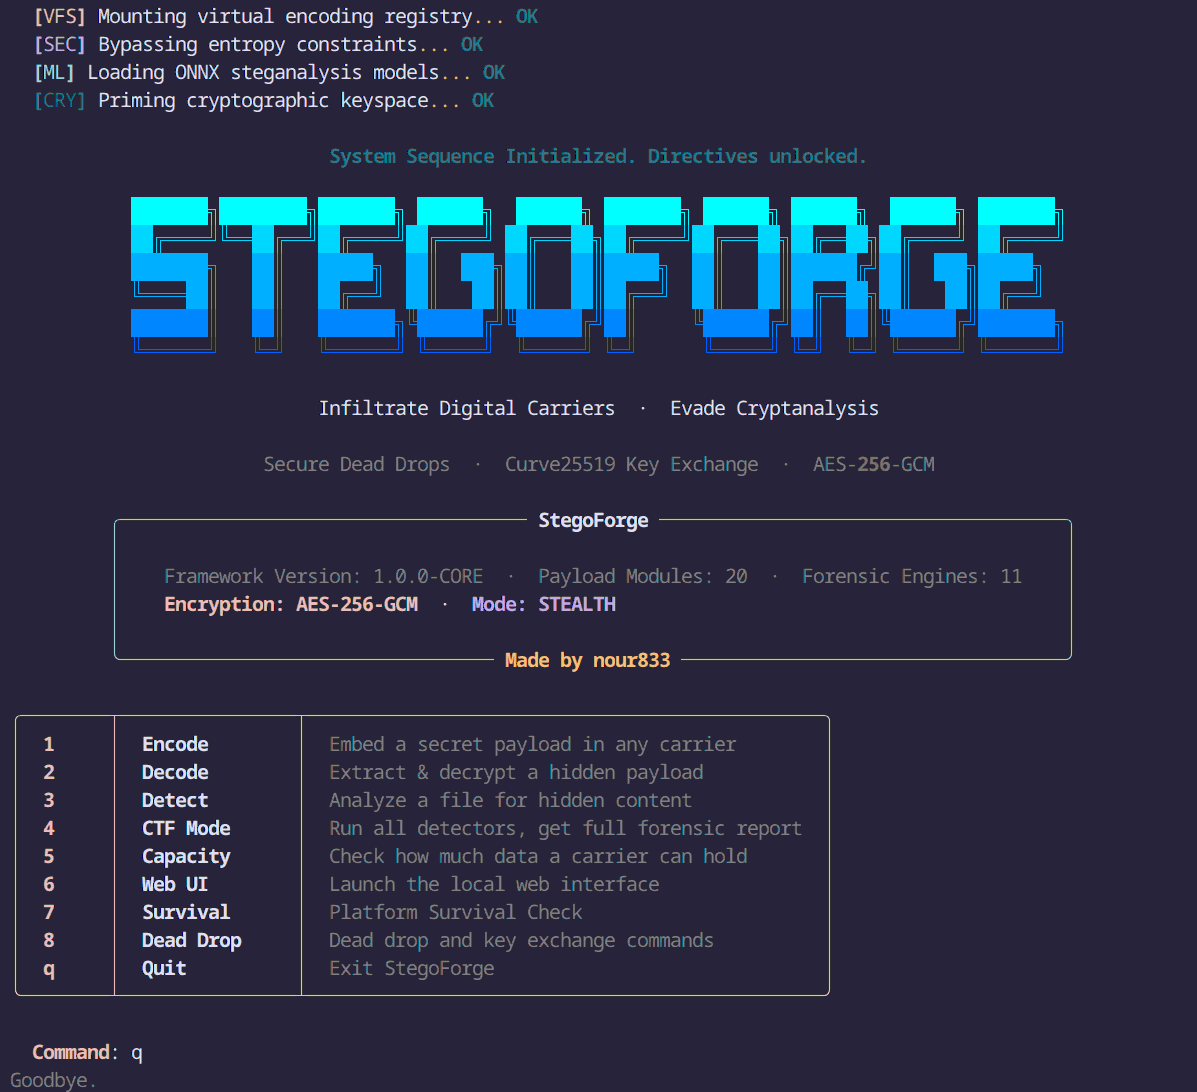 nour833/stegoforge
The ultimate steganography and digital forensics toolkit. Hide and extract data across images, audio, video, documents, and network packets, or run…
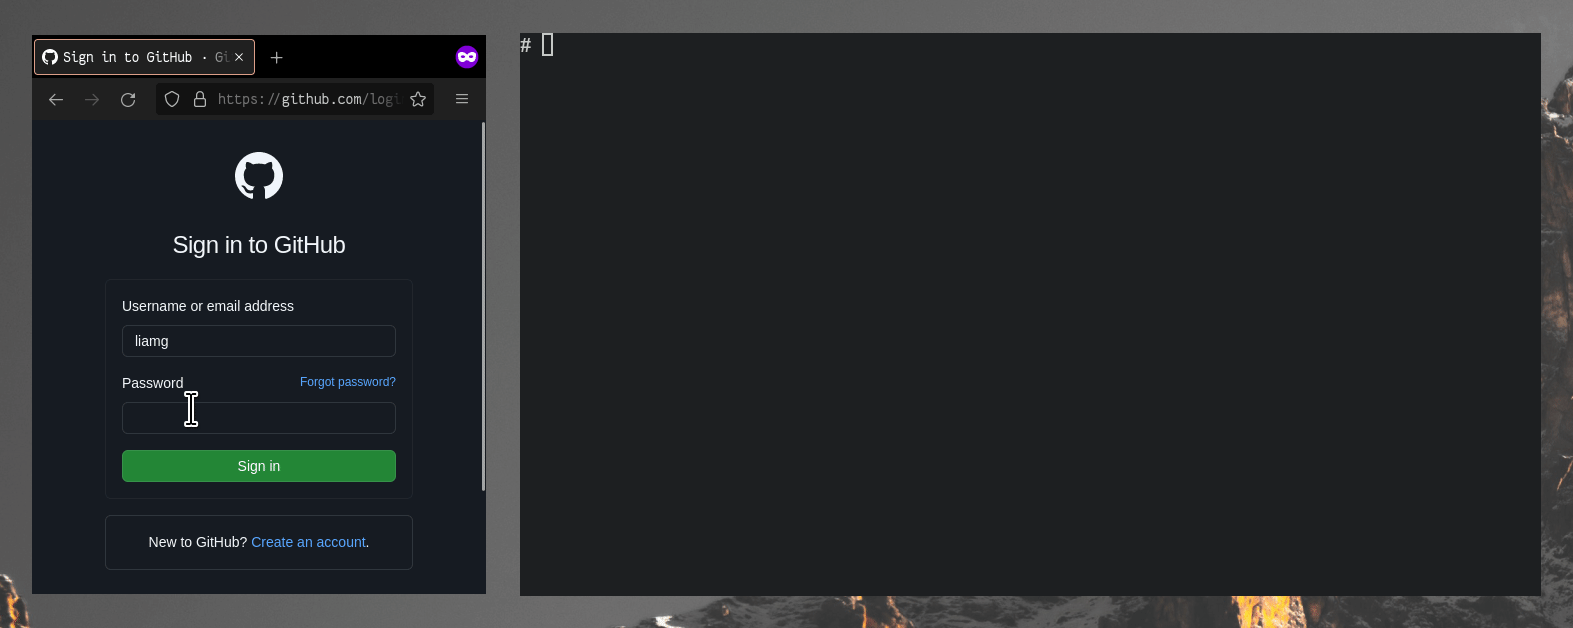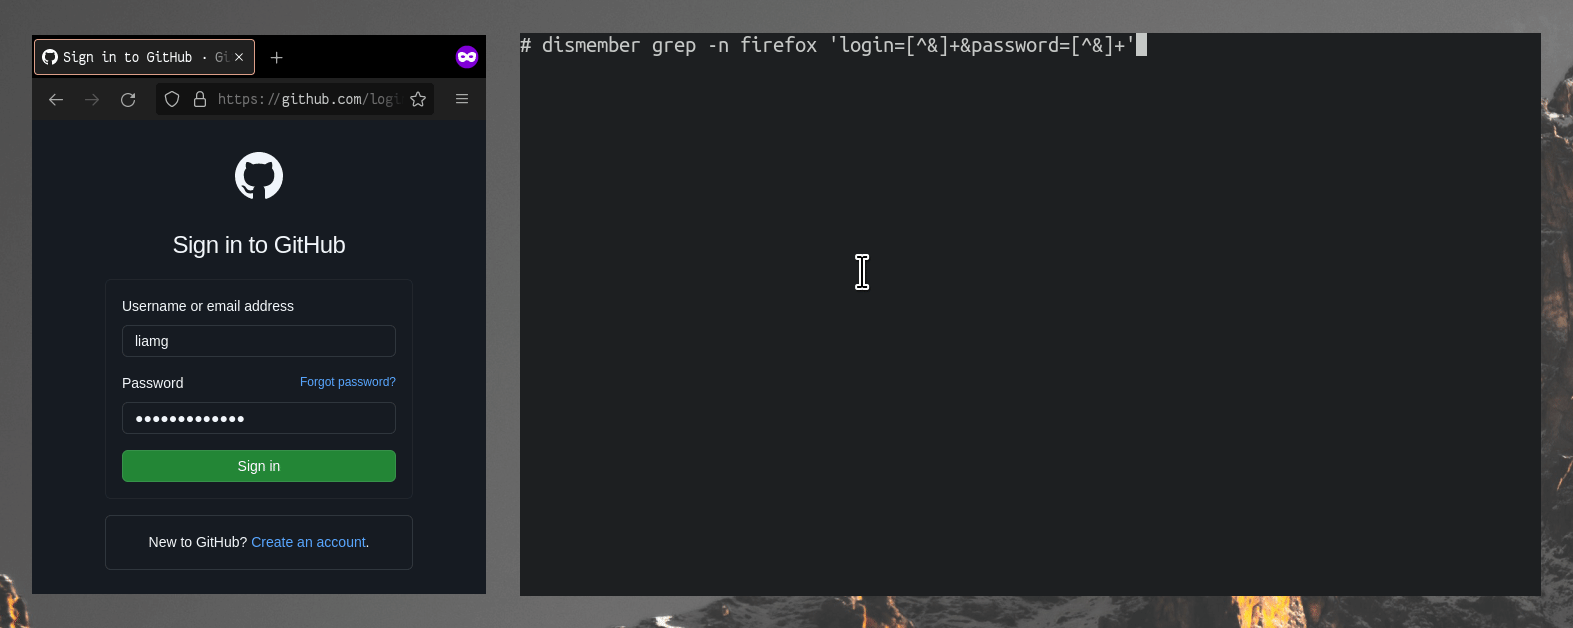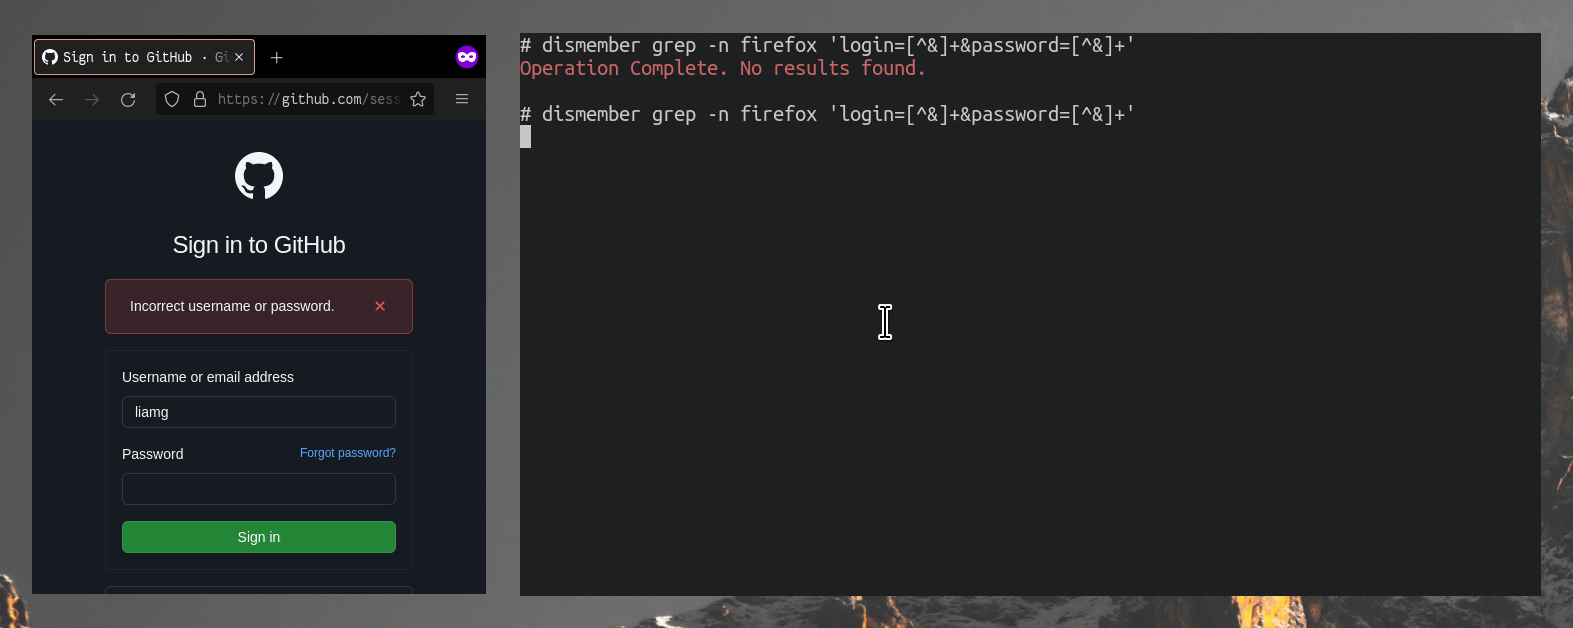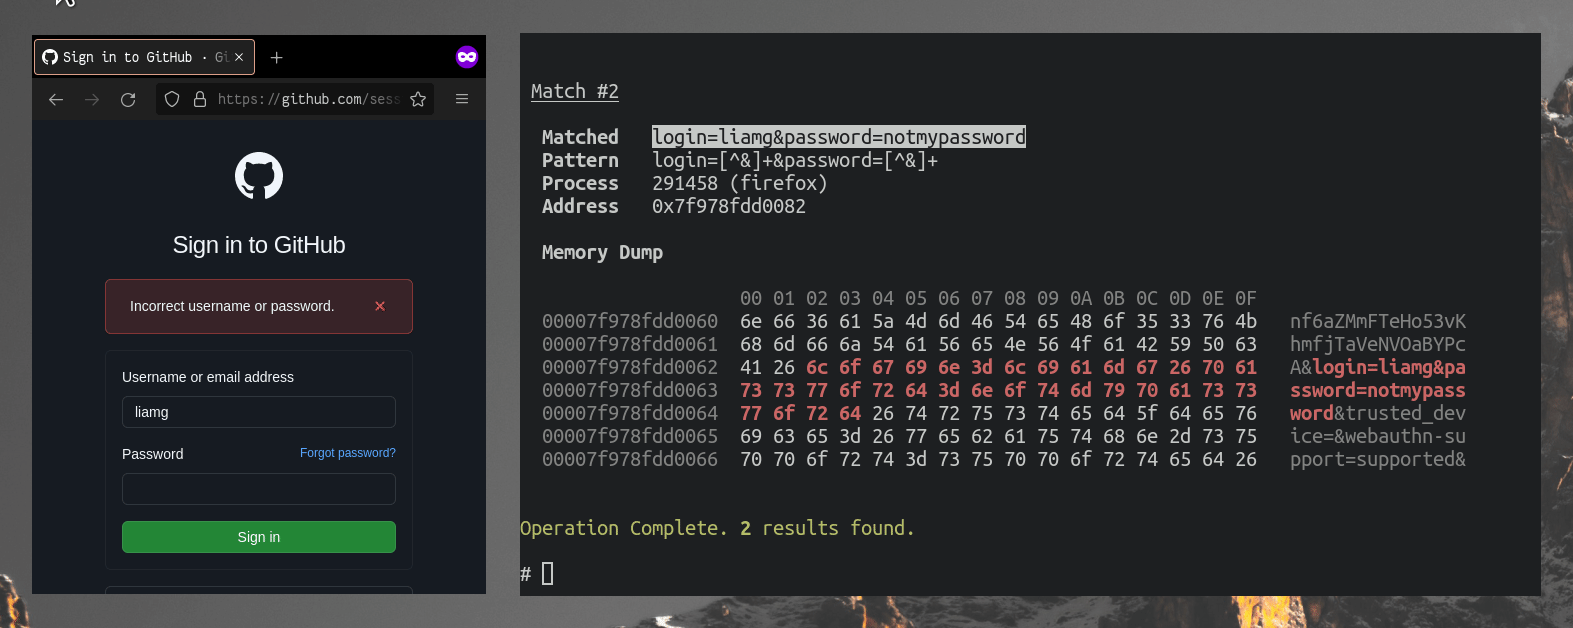 liamg/dismember
:knife: Scan memory for secrets and more. Maybe eventually a full /proc toolkit.