
ulexecve
 anvilsecure/ulexecve
Executes arbitrary ELF binaries directly from memory on Linux without touching disk, enabling stealthy red-teaming and anti-forensic operations via a…
exploitationmemory-forensicspenetration-testing+3
218
anvilsecure/ulexecveExecutes arbitrary ELF binaries directly from memory on Linux without touching disk, enabling stealthy red-teaming and anti-forensic operations via a…
 nightbringer21/fridump
Cross-platform memory dumper using Frida to extract accessible memory from iOS, Android, and Windows applications for forensic analysis and…
 pubglite55/oppo-ghostlock
OPPO Find N2 GhostLock (CVE-2026-43499) exploit adaptation
 thiasap/oppo-pgem10-ghostlock
OPPO Find X6 Pro GhostLock (CVE-2026-43499) exploit adaptation
 woaphone/cve-2021-28664-poc
PoC skeleton for CVE-2021-28664, a Mali kbase GPU driver use-after-free, demonstrating a kernel arbitrary physical memory read/write primitive on…
 huaguiqi/asus-i005-cve-2026-43499
CVE-2026-43499 (GhostLock) adaptation for ASUS ROG Phone 5S — UAF trigger + pselect stack reclaim, KASLR leak blocked
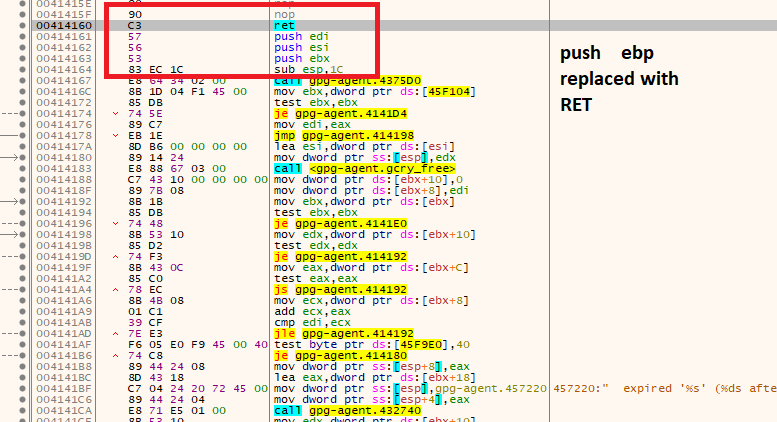 kacperszurek/gpg_reaper
GPG Reaper - Obtain/Steal/Restore GPG Private Keys from gpg-agent cache/memory
 robertmotr/zirconium
DLL-injectable internal game cheat for Plutonium BO2 zombies
 the-maxu/cve-2025-24201-webkit-vulnerability-detector-poc-
CVE-2025-24201 WebKit Vulnerability Detector (PoC)
 rootxsushant/citrix-netscaler-memory-leak-cve-2025-5777
Update the old POC of CVE-2025-5777 Citrix NetScaler Memory leak
 ivan-sincek/invoker
Penetration testing utility and antivirus assessment tool.
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 sensepost/objection
Frida-powered runtime mobile exploration toolkit for assessing iOS and Android app security. Bypass SSL pinning, dump keychains, manipulate heap…
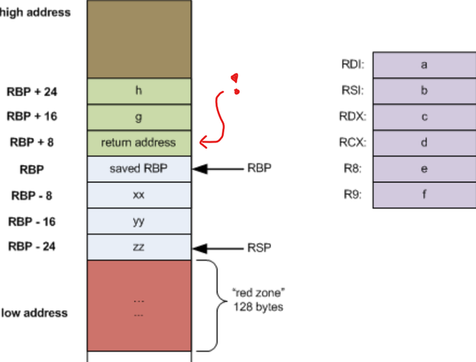 mgeeky/threadstackspoofer
Thread Stack Spoofing - PoC for an advanced In-Memory evasion technique allowing to better hide injected shellcode's memory allocation from scanners…
 kyleavery/aceldr
Cobalt Strike UDRL for memory scanner evasion.
 0x36/pixel_gpu_exploit
Android 14 kernel exploit for Pixel7/8 Pro
 sterrasec/apk-medit
memory search and patch tool on debuggable apk without root & ndk